

Insights from experts shaping secure development
Access expert content on secure coding, AI governance, and software risk management.

SDLC における AI:過度な期待とセキュリティの現実の分離
KnowBe4 との提携による SDLC における AI:Kawin Boonyapredeeto と Pieter Danhieux が AI コードセキュリティリスクを解説します。
ジャーマン OWASP デイ 2026
Secure Code Warrior はジャーマン OWASP デイ 2026 をスポンサーし、セキュアな開発、運用、テストのベストプラクティスを共有します。
アデレードSEC (AdelaideSEC)
Secure Code Warrior は AdelaideSEC でセキュアコーディングトーナメントを開催します。開発者や専門家が実戦形式で競い合います。
Black Hat USA 26
Secure Code Warrior はラスベガスの Black Hat USA 2026 に出展します。CEO Pieter Danhieux、CCO Fatemah Beydoun らが現地にいます。
FS-ISAC APAC サミット
2026年7月14〜15日にシンガポールで開催される FS-ISAC APAC サミットをスポンサーするのが楽しみです!ブース #8 にお立ち寄りください。
Gartner セキュリティ & リスクマネジメント サミット 2026
2026年9月22〜24日にロンドンで開催される Gartner セキュリティ & リスクマネジメント サミットをスポンサーできることに興奮しています!

OWASP グローバル AppSec USA
2026年11月5〜6日にサンフランシスコのハイアットリージェンシーで開催される OWASP Global AppSec USA 2026 のシルバースポンサーを務めることを誇りに思います!

開発者主導のセキュリティの未来:Checkmarx SAST と SCW の統合
この統合は、脆弱性の検出と修復の間のギャップを埋め、必要な瞬間に正確な学習リソースを開発者に提供します。

ソフトウェア開発における DevSecOps の不可欠な役割
SCW Coffee Shop @RSAC24提供:DevSecOps の思想的リーダーや業界専門家とともに、今日の開発における DevSecOps のクリティカルな役割を掘り下げます。
シャドーAIからAIソフトウェアガバナンスへ:コードベース全体での可視性の奪還
Secure Code Warrior の CTO Matias Madou とプロダクトディレクターの Tamim Noorzad から、大規模な AI 支援開発の管理に必要な視点と可視性について学びましょう。

OWASP グローバル AppSec ヨーロッパ
2026年6月22〜26日にウィーンのオーストリアセンターで開催される25周年記念 OWASP Global AppSec EU カンファレンスをスポンサーできるのが待ちきれません!

OWASP BASC
4月11日にマサチューセッツ州ボストンで開催される OWASP BASC をスポンサーできることを嬉しく思います。専門家が集まるプレミア会議です。

OT サミット・マドリード
AI、クラウド、安全な情報管理が新世代のインテリジェント企業をどのように推進しているかを示す OpenText Summit Madrid 2026 にご参加ください。
サイバーセキュリティ サミット
サイバーセキュリティサミットは、トップクラスの専門家、革新者、出展者が集まり、最新トレンドとITレジリエンス戦略を披露する会議です。
開発者のセキュリティ熟達:統合ASTとスキルアップによる脆弱性修正の加速
脆弱性を見つけるだけでなく、根本的に修正しましょう。真の Secure by Design を実現するためのアプローチをご紹介します。

自信を持ってシフト左へ:開発者ワークフローへのセキュリティのネイティブ組み込み
SCW と Checkmarx の専門家を結集し、開発プロセスにセキュリティを円滑に統合するためのベストプラクティスと戦略を共有します。
プロダクトセキュリティ・バーチャルサミット
今年1月28日に開催されるプロダクトセキュリティ・バーチャルサミットで Cycode とパートナーシップを組むことを誇りに思います。AI 時代のソフトウェアの未来を探ります。

フィッシャパルーザ (Phishapalooza)
アメリカがん協会を支援するため、第18回年次 Phishapalooza に参加できることを光栄に思います。アイスフィッシングや資金調達活動を楽しみにしております。
OWASP LASCON
テキサス州オースティンで開催される OWASP LASCON 2026 のゴールドスポンサーであることを誇りに思います!ノーリス・コンファレンス・センターでお待ちしております。

ニューヨーク・セキュアコード・ショーダウン
SCW、OWASP、AWS は、2026年2月19日(木)に開催されるニューヨーク・セキュアコード・ショーダウンに皆様を招待します!

ゴールドコースト BSides
オーストラリアのゴールドコーストで開催されるハンズオンコンペティションで、実際の脆弱性を特定・修復する能力をテストしましょう。
BSides フランクフルト
フランクフルトのゲーテ大学キャンパスで開催されるハンズオンコンペティションに参加し、実際の脆弱性を特定して修正する能力を試してみましょう。
RSA カンファレンス
RSA Conference 2026 に向かっています。開発者が最初からセキュアなコードを書くスキルを支援します。サウスエキスポホールのブース #250 でお会いしましょう。

FS-ISAC FinCyber Today カナダ
FS-ISAC FinCyber Today カナダで開発者リスク管理についてお話する準備ができています。開発者のセキュアコード学習を強化してリスクを軽減します。
Threat Modelling with AI: Turning Every Developer into a Threat Modeler
Threat modeling with AI: how to turn every developer into a threat modeler, straight from their IDE.

開発者の特定
カリキュラムおよびオンボーディングマネージャーの Katelynd Trinidad が、コードコントリビューターを特定してセキュアコードトレーニングを受けさせるための手法を紹介します。

AppSec DevSec DevSecOpsにおけるブランドの力(頭字語の意味とは!?)
AppSecにおいて持続的なプログラムの成果を上げるには、単なる技術以上のもの、つまり強力なブランドが必要です。力強いアイデンティティは、取り組みが共感を呼び、開発者コミュニティ内での持続的な参加を促進します。

Vibe Coding:AI時代に合わせてAppSec戦略を適合させる実践ガイド
実用的なトレーニング優先のアプローチにより、AppSecマネージャーが障害ではなくAI推進者となる方法をオンデマンドでご視聴ください。AIコーディングアシスタント時代において、Secure Code Warrior(SCW)を活用してAppSec戦略を戦略的に更新する方法をご紹介します。

アジャイル学習で開発者リスクを管理するための CISO ガイド
ESG の最近の研究では、回答者の 54% が既知の脆弱性を持つコードを本番環境にリリースしていると述べています。学習プログラムはリスクを減らしていますか?

Secure Code Warrior & GuidePoint Security
Come visit our booth #336 at SecTor 2025 in Toronto at the Metro Toronto Convention Centre! Us along with other security professionals will be sharing our latest research and techniques on underground threats and corporate defenses.

OWASP ニュージーランド・デイ
オークランド大学キャンパスで開催される OWASP ニュージーランド・デイに参加できることを嬉しく思います!堅牢なアーキテクチャに焦点を当てています。

OWASP グローバル AppSec 2025 USA
ワシントンDCの中心部にあるマリオット・マーキスのエキスポスペースでお待ちしております!800人以上の専門家とつながるチャンスです。

OWASP ベネルクス・デイズ
ベルギーで開催される OWASP BeNeLux Days のブースにお越しください!セキュリティ、DevOps、クラウドの専門家による技術トークを提供します。
メルボルン AppSec & DevSecOps サミット
メルボルン AppSec & DevSecOps サミットで、セキュリティや開発リーダーの皆様とアイデアを共有できることを楽しみにしています!
FS-ISAC 秋季サミット
10月7日(火)午前8時より FS-ISAC 秋季アメリカサミットの朝食会ブースにお越しいただき、デザインによるセキュリティについて語り合いましょう。

CISO Inspired サミット アメリカ
CISO Inspired Summit New York 2025 でサイバーセキュリティリーダーとつながり、積極的な防御戦略を掘り下げましょう。

CISO Inspired サミット イギリス
CISO Inspired Summit UK 2025 でサイバーセキュリティリーダーとつながり、デジタル防御を強化し、堅牢な戦略を構築しましょう。

BSides ボーンマス
BSides Bournemouth はコミュニティ主導のサイバーセキュリティ会議です。洞察に満ちた講演やハンズオンアクティビティをお楽しみください。

Black Hat USA
ラスベガスの Mandalay Bay で開催される Black Hat USA で当社役員陣にお会いください!AI/LLM セキュアコードリスクについて話し合えることを楽しみにしています!

OWASP グローバル AppSec ヨーロッパ 2025
OWASP Global AppSec EU のブース #G08 で、デザインによるセキュリティ原則と効果的なリスク管理が次世代サイバーセキュリティをどう形成するかをご覧ください。
FS-ISAC EMEA サミット
5月21日午前8時より FS-ISAC EMEA サミットの朝食会ブースにお越しいただき、デザインによるセキュリティと開発者中心のリスク管理について語り合いましょう。
サイバーセキュリティ・サミット、ハンブルク
予防的セキュアコーディングがセキュリティ体制を向上させながらソフトウェア開発を加速する方法について話し合いましょう。

OpenText サミット・マドリード
Secure Code Warrior は4月10日に開催される OpenText Summit Madrid 2025 を後援することを誇りに思います!リーダーが集まり変革を探ります。
オーストラリア・サイバー・エクスチェンジ (ACE25)
4月3日、CEO の Pieter Danhieux が第1回オーストラリア・サイバー・エクスチェンジ ACE25 で登壇し、オーストラリアのサイバー能力強化について語ります。

セキュリティのシフト左:ソフトウェア開発における DevSecOps の不可欠な役割
このウェビナーでは、DevSecOps の非常に重要な役割と、開発ライフサイクルの初期段階でセキュリティを統合する戦略について掘り下げます。

OWASP SnowFROC
デンバーのプレミアアプリケーションセキュリティ会議 SnowFROC '25 にご参加ください!約400人が集まるこの1日イベントで最高の体験を。

BSides リンブルフ
今年の3月14日に BSides リンブルフでトーナメントを開催します!深い議論、ハンズオンデモ、コラボレーションを促進するイベントです。
第2回 2025年 OWASP メイン州セキュアコーディングトーナメント
OWASP メイン州と Secure Code Warrior が提携し、第2回 OWASP メイン州セキュアコーディングトーナメントを開催します!初心者からシニアレベルまで、すべてのソフトウェア開発者とAppSec専門家を歓迎します。

NDC Security 2025
オスロの中心部で最先端のトピック、ハンズオンワークショップ、ピアネットワーキングに飛び込みましょう。スポット H でお待ちしております!

RSA カンファレンス 2025
RSAC 2025 のブース #2353 にぜひお越しください。革新的なソリューションを探索し、会話に参加してください。

DevSecOps360 ロンドン
2025年1月22日(水)、IBM Innovation Studio ロンドンで開催されるパートナーエコシステム内の DevSecOps 統合ビジョンイベントにご参加ください。

Black Hat Europe
ロンドンの ExCeL で開催される Black Hat Europe にご参加ください

OWASP ベネルクス
SCW は今年のカンファレンスをサポートできることを誇りに思います。ブースにお立ち寄りいただき、OWASP Top 10 を克服する方法をご覧ください。

ジャーマン OWASP デイ 2024
ドイツのライプツィヒで Secure Code Warrior とともに OWASP からの素晴らしい洞察や2025年のソフトウェアセキュリティの方向性を共有しましょう。

DevSecOps 360 トロント
SCW、IBM、Black Duck、Iruis Risk、Contrast に参加して、組織が脆弱性を最小限に抑えながら開発を加速する方法を学びましょう。

クラウド & サイバーセキュリティ エキスポ、パリ
フランスにおけるプレミアサイバーセキュリティイベントのシルバースポンサーを務めることを嬉しく思います。会場でお会いできるのを楽しみにしています。

OpenText World 2024
Secure Code Warrior と OpenText に参加して、世界中の企業が SAST 結果を活用してセキュアコーディングのアジャイルな学習体験を生み出す方法を学びましょう。
DevSecOps 360 ロンドン
SCW、IBM、BlackDuck、IriusRisk に参加して最新の統合を体験し、企業が組織の生産性をいかに実現したかを学びましょう。

AppSecDay ストックホルム
Secure Code Warrior、OpenText、Sonatype とともに、オープンソースのナビゲーション、NIS2への準拠、AIとDevSecOpsに関する議論にご参加ください。
DevSecOps 360 ミラノ
自動化がより迅速で安全な開発を推進する方法をご紹介します。脆弱性を減らすための実践的なソリューションに飛び込みましょう。

チャリティ プロアマ スクランブル
KidSport Québec を支援し、より多くの子供たちがスポーツに参加できるよう、素晴らしい目的のためにゴルフ大会を開催します。
AppSec Day ユトレヒト
アプリケーションセキュリティが進化するにつれ、組織はリアルタイムの脅威検知と予防のために AI ソリューションをますます統合しています。Secure Code Warrior とパートナーにご参加ください!

Secure Code Warrior ユーザーグループ EMEA
他の管理者とつながり、開発者主導のセキュリティプログラムの管理方法を学ぶコミュニティです。ヒントやコツを学びましょう!

SANS Secure ジャパン 2025
SANS が2月17〜22日に東京にやってきます。ブースにお越しいただき、当社の最先端 AppSec ソリューションと学習プラットフォームをご覧ください。

OWASP 2024 グローバル AppSec
Global AppSec US カンファレンスは新しいトレンドで盛り上がります。サンフランシスコのブースで最新製品のデモをご覧ください。

DevSecOps トランスフォーメーション
DevSecOps により、開発ライフサイクルの初期段階でセキュリティ問題を特定し、最も大きな影響を与える開発者に直接提示できます。

サイバーセキュリティ・サミット
ビジネス向けサイバーセキュリティのデジタルソリューションを提供する革新的なプロバイダーと専門家が結集します。

Blackhat USA
27年目を迎える Black Hat USA がラスベガスに戻ってきます。選りすぐりのブリーフィング、オープンソースツールのデモ、ビジネスホールなどが用意されています。

AppSec & DevSecOps サミット
メルボルン AppSec および DevSecOps サミット 2024 でセキュリティ戦略を統合し、強化しましょう。セキュリティスキルを高め、アプリケーションとクラウドセキュリティの革命の最前線に立ちましょう。

SCW Trust Score でセキュリティプログラムの現状をベンチマーク
急速に変化するセキュリティ環境において、セキュリティプログラムの立ち位置を理解することは極めて重要です。CTO Matias Madou とともに SCW Trust Score について話し合いましょう。

ノーディック IT セキュリティ
スカンジナビアで最も評判の高いサイバーセキュリティサミットである Nordic IT Security は、17年間にわたり地域のナビゲーション役を務めています。

ベルギー・コーヒーアワー
ベルギーからの RSAC 参加者のために、3月7日(火)午後3時より特別イベントを開催します。CEO Pieter Danhieux や CTO Matias Madou とともに素晴らしいコーヒーを楽しみましょう。

2026年のセキュリティ・チャンピオン:高め、関与させ、保護する
新規プログラムの立ち上げ、既存プログラムの拡張、あるいは機能の探求を目的としている場合でも、このウェビナーは実践的な洞察を提供します。

SANS ネットワークセキュリティ 2026
9月10〜15日にラスベガスで開催される SANS Network Security 2026 にご参加ください。最新の課題に焦点を当てた実践的なセッションを提供します。

RSA カンファレンス 2024
可能性の芸術がここにあります!ブース 5179 にお立ち寄りいただき、脆弱性を53%削減する方法をご覧ください。

RSAC24 で SCW 経営陣と面談
当社の共同創業者と役員陣が5月6日〜7日にサンフランシスコ最高のコーヒーを楽しみながらミーティングを行います。

開発者と AI を信頼する
SCW Coffee Shop @RSAC24提供:共同創業者兼 CTO Matias Madou と業界の専門家が、開発者内でのセキュリティスキル測定の課題について語ります。

SCW Trust Score でセキュアコーディングプログラムの有効性を定量化する方法
SCW Coffee Shop @RSAC24提供:Patrick Collins と Junie Dinda とともに、セキュアコーディングプログラムの風景を再定義する新しい SCW Trust Score を深掘りします。

Carolina Hurricanes と GuidePoint
GuidePoint のパートナーとともにアイスホッケーの試合と AppSec のトークを楽しみましょう!

ベイエリア・ベンダー・ハッピーアワー
詳細情報はまもなく公開されます。

セキュリティにおける女性リーダー
SCW Coffee Shop @RSAC24提供:共同創業者兼CCOのFatemah Beydounと業界の女性リーダーのパネルに参加し、セキュリティにおけるジェンダーギャップを修正するためのシフト左について話し合います。
コーディングに生成AIを使用することの良さ、悪さ、そして醜さ
このウェビナーでは、Secure Code Warrior CTO 兼共同創業者の Matias Madou とセキュリティ研究者の Jon Helton が力を合わせて生成AIを解読します。
スコシアバンク・アリーナ プライベートスイート
スコシアバンク・アリーナのプライベートスイート体験にご参加ください!排他的な環境で試合を観戦しながら AppSec について語り合いましょう。
アプリケーションセキュリティ・ハンズオンワークショップ
AWS、Contrast Security、Arctiq とのパートナーシップにより、インタラクティブなハンズオン AppSec ワークショップをお届けします。

バーチャルワインテイスティング - オハイオ
GuidePointやその他のパートナーとともに、Silver Oaks Wineryのバーチャルワインテイスティングにご参加ください。
DevSecOps 360 - リヤド
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
DevSecOps 360 - ミュンヘン
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
DevSecOps 360 - ドバイ
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
シフト左テスティング
脆弱性を早期に検出し、修復を加速します。SCW、Cyberark、Checkmarx は一貫したシフト左アプローチで提携しています。
次世代の保護:AIコーディングの脆弱性に正面から立ち向かう
AI の登場はソフトウェア開発の風景を変えました。しかし、これは新たな課題ももたらします。AI は単にコードを書くのではなく、脆弱なコードを書きます。
人工知能時代におけるセキュアコーディング
AI がコード生成を加速する中、堅牢なセキュリティを維持することはかつてないほど重要です。AI 開発の敏捷性とセキュアコーディングのバランスを探る炉辺対談。
Secure Code Warrior ユーザーグループ NA
他の管理者とつながり、開発者主導のセキュリティプログラムの管理方法を学ぶコミュニティです。ヒントやコツを学びましょう!
Secure Code Warrior ユーザーグループ
Secure Code Warrior ユーザーグループへようこそ!製品アップデート、刺激的な顧客の成功事例、インタラクティブなパネルディスカッションをお届けします。
SANS クラウドセキュリティ・トレーニング
SANS クラウドセキュリティ・トレーニングが4月13〜18日にバージニア州アレクサンドリアにやってきます。集中的な実践トレーニングが行われます。
DEVOPS カンファレンスに参加しましょう
3月8〜9日に開催される DEVOPS カンファレンスに参加し、洞察力に満ちた話を聞き、トーナメントに参加するチャンスを手に入れましょう!今すぐ無料チケットを獲得。
セキュリティは開発者の問題か?
テクノロジーが爆発的に増加し、そのすべてを保護する必要があります。しかし、セキュリティチームには急速な進化に対応する人手が不足しています。
包括的な開発者主導のセキュリティでソフトウェアリリースのスピードを向上
AWS + Secure Code Warrior が開発者のコード出力の量と質を高めることの重要性について解説。

包括的な開発者主導のセキュリティでソフトウェアリリースのスピードを向上
悪用可能な脆弱性に起因するセキュリティ侵害が増加する中、組織はリスクを最小限に抑え、リリース速度を高める方法を模索する必要があります。
オープンソースコンプライアンスにおける回避と修復のギャップを埋める方法
このギャップを埋めることは、エンジニアリングチームがオープンソースソフトウェアの影響をよりよく理解するために重要です。

強固な基盤を持った AppSec プログラムの構築方法
AppSec プログラムの戦略開発においてベースラインを設定することの重要性とアプローチ。
Enabler 8: プログラムのブランディング
セキュアコーディングプログラムを成功させるには、優れたコンテンツ以上のものが必要です。イネーブラー8では、ブランディングによって参加をステータスを感じさせる魅力的な体験に変える方法を解説します。
すべての従業員が、今やAIサイバーセキュリティの最前線にいる
エンタープライズテクノロジーの状況は、手遅れになるまでほとんど予測できなかったほどの速度で変化しています。私たちは今、人間が書くコードや基本的なコパイロット支援の時代から、エージェント型開発ライフサイクル(ADLC)の時代へと正式に足を踏み入れました。自律型AIエージェントは、複数の機能にわたってかつてない効率性をもたらす一方で、全く新しい種類のセキュリティリスクや規制リスクも引き起こしています。
イネーブラー7:開発者の表彰
称賛は参加意欲を高めます。イネーブラー7では、開発者の功績を広く称え、セキュアコーディングにおける真の成果に対して報酬や限定グッズを贈呈します。

Gartner® Hype Cycle™ for Application Security 2026に選出
Secure Code Warriorは、「Gartner® Hype Cycle™ for Application Security, 2026」のAgentic Coding SecurityおよびSecure Coding Trainingのカテゴリーで選出されました。その理由を解説します。

LLMによるコード生成のセキュリティとコストにお悩みのCISOやエンジニアリングリーダーの皆様へ
AIモデルを本格導入する前に、当社独自のLLMベンチマークデータである「SCW AI Trust Index」をご確認ください。

イネーブラー6:リーダーシップ層への定期的なレポーティング
経営陣の支持は、放っておいて続くものではありません。成功要因6では、定期的な報告を通じて、いかに経営陣の関心と理解を維持し、プログラムの成功に向けた投資を継続してもらうかを紹介します。

AIソフトウェアガバナンスの未来は、強固なパートナーシップの上に築かれる
Secure Code Warriorがなぜチャネルファースト企業へと舵を切るのか、そして信頼できるパートナーがどのように組織のAIソフトウェアガバナンス導入を安全かつ大規模に支援するのかをご紹介します。

Secure Code WarriorのCitizen AI:AI時代に対応できる人材の育成
Secure Code Warriorによる、非エンジニア従業員向けAIリテラシープログラム。

なぜ多くのCISOは目隠し状態でAI導入を進めているのか(そして、その目隠しを外す方法)
Secure Code Warriorは本日、AI導入に向けた規範的かつ方向性を示すモデルを網羅した新しいホワイトペーパーを発表しました。セキュリティリーダーはこれを利用して、自社の導入段階を特定し、組織内のAIセキュリティリスクを制御下に置くための着実な前進を図ることができます。
イネーブラー 5:認定プログラム
一度きりのトレーニングから脱却しましょう。Enabler 5は多段階の認定プログラムを構築し、開発者に有意義な成長の道筋と確かなスキルを提供します。
NSAが初のMCPセキュリティガイダンスを発表。これが開発者の能力向上に何を意味するのかを解説します。
NSAが初のMCPセキュリティガイダンスを公開しました。SCWのカリキュラムは、指摘された23の課題のうち18をすでにカバーしています。その対応状況をご覧ください。

Gartner®「Hype Cycle™ for Secure Software Engineering 2026」に選出
GartnerがSCWを2部門で選出。AIエージェントが開発業務を担う範囲が広がる中、SCWはAI主導の開発を安全に導入するための能力とガバナンスを提供します。

アダプティブ・ラーニングを発表:AIソフトウェアのセキュリティリスクとスキルギャップに対する解決策
Adaptive Learningは、SCW Trust Agentと当社の学習プラットフォーム全体を連携させ、開発者のリアルタイムな活動に完全に適合したトレーニングを実現します。
実際のAI利用状況を反映したセキュアコーディング学習
セキュアコーディング研修を実際のAI開発アクティビティに適合させ、手動介入なしでAIツールを使用する開発者に自動的にガイダンスを割り当てます。セキュアコーディング研修を実際のAI開発アクティビティに適合させ、手動介入なしでAIツールを使用する開発者に自動的にガイダンスを割り当てます。
人間が書いたコードであれAIが生成したコードであれ、開発者にコード内の真のリスクを教育しましょう
アダプティブラーニングは、実際に脆弱性を生み出している開発者に対して、的を絞ったセキュアコーディングトレーニングを自動的に割り当て、根本的なリスクの再発を防止します。Secure Code Warriorのブログバナー。マルチモニターのデスクでコードを書く開発者の画像に青いオーバーレイを重ね、「開発者にコード内の真のリスクを教育する」という見出しを添えています。
イネーブラー4:ユーザーアクセスの障壁を低く
「イネーブラー4:ユーザーアクセスの障壁低減」で、セキュアコーディングプログラムの摩擦を取り除きましょう。SSO、フロントローディング型のオンボーディング、リレー状態戦略を活用し、開発者がワンクリックでトレーニングを開始できる環境を構築します。

生成AI時代に向けた開発者の育成:AWSとのコラボレーション
Secure Code WarriorがAmazon Web Services(AWS)と戦略的コラボレーション契約を締結したことを発表いたします。脅威の状況が急速に変化する現在、この戦略的提携は、セキュリティリーダーと未来志向の開発者の双方にとって、極めて重要なタイミングで実現しました。
ソフトウェアの未来を守る:SCWとKnowBe4が提携
Secure Code WarriorとKnowBe4の戦略的パートナーシップ締結を発表できることを大変嬉しく思います。KnowBe4は、人間およびAIエージェントに起因するリスク管理において世界をリードする企業であり、世界中の組織へセキュリティ意識の基盤を広めるための最適なパートナーです。

ポスト量子暗号:量子コンピュータは現在の暗号を解読する ― あなたの準備はできていますか?
耐量子計算機暗号(PQC)は、量子コンピューティングの脅威からデータを保護するために不可欠です。「今すぐ収集、後で解読(Harvest Now, Decrypt Later)」という手法がもたらすリスクと、開発者が量子耐性のあるセキュリティに備える方法について解説します。

イネーブラー3:開発者向けコミュニケーションプラン
強力なコミュニケーションプランで、開発者がセキュアコーディングプログラムに意欲的に取り組める環境を維持しましょう。メリットの強調方法、適切なトーンの設定、成果の称え方を学びます。
エージェント時代の到来は予想より早い:不意を突かれないために
Anthropicの「Claude Mythos」は、すべてのセキュリティリーダーがセキュリティプログラム、特にレガシーシステムのパッチ管理に取り組む姿勢を根本から変える、永続的な転換点となります。

Enabler 2: Senior Leadership Sponsorship
Explore Enabler 2: Senior Leadership Sponsorship. Learn why active buy-in from the CIO, CTO, and CISO is vital to drive developer adoption and program credibility.
Observe and Secure the ADLC: A Four-Point Framework for CISOs and Development Teams Using AI
While development teams look to make the most of GenAI’s undeniable benefits, we’d like to propose a four-point foundational framework that will allow security leaders to deploy AI coding tools and agents with a higher, more relevant standard of security best practices. It details exactly what enterprises can do to ensure safe, secure code development right now, and as agentic AI becomes an even bigger factor in the future.
サイバーモンが帰ってきた:ボスを倒すAIミッションがオンデマンドで利用可能になりました
「サイバーモン2025 ビート・ザ・ボス」がSCWで一年中プレイできるようになりました。高度な AI/LLM セキュリティ課題を導入して、安全な AI 開発を大規模に強化しましょう。
AI Can Write and Review Code — But Humans Still Own the Risk
Anthropic’s launch of Claude Code Security marks a defining collision point between AI-assisted software development, and the rapid augmentation of how we approach modern cybersecurity.
サイバー・レジリエンス法の解説:セキュア・バイ・デザイン・ソフトウェア開発にとっての意味
EU サイバー・レジリエンス法 (CRA) が何を要求し、誰に適用されるのか、エンジニアリング・チームがセキュア・バイ・デザイン・プラクティス、脆弱性防止、開発者の能力開発にどのように備えることができるかを学びましょう。

イネーブラー1: 定義済みで測定可能な成功基準
Enabler 1は、10部構成のEnablers of Successシリーズの第1部で、安全なコーディングをリスク削減やスピードなどのビジネス成果に結び付けてプログラムを長期的に成熟させる方法を紹介します。
SCW Turns 11: A Realtime Lesson in Adaptability and Continuous Improvement
2025 was a big year for AI, for cybersecurity, and for SCW. I’m approaching 2026 with quiet confidence, and the optimism that only hard work paying off can bring.

Introducing the 10 Enablers of Success
Secure Code Warrior’s 10 Enablers guide organizations in building lasting secure coding programs by focusing on people, process, and program maturity stages.
OWASP トップ 10 2025: ソフトウェアサプライチェーンの失敗
OWASP Top 10 2025 では、ソフトウェアサプライチェーンの障害が #3 に掲載されています。厳密なSBOM、依存関係の追跡、CI/CD パイプラインの強化により、この影響の大きいリスクを軽減してください。

New Risk Category on the OWASP Top Ten: Expecting the Unexpected
OWASP Top 10 2025 adds Mishandling of Exceptional Conditions at #10. Mitigate risks via "fail closed" logic, global error handlers, and strict input validation.
OWASP トップ 10:2025 — 新機能と、安全なコードウォリアーが連携を維持するのにどのように役立つか
OWASP Top 10:2025で何が変わったのか、そしてSecure Code Warriorがどのようにして移行を容易にしたのか、最新のクエスト、コース、開発者インサイトをご覧ください。
Adopt Agentic AI in Software Development FAST! (Spoiler: You Probably Shouldn't.)
Is the cybersecurity world moving too fast on agentic AI? The future of AI security is here, and it's time for experts to move from reflection to reality.

Solving the Visibility Crisis: How Trust Agent Bridges the Gap Between Learning and Code
Trust Agent by Secure Code Warrior solves the secure coding crisis, validating dev proficiency on every commit. It discovers all contributors & automates governance in your dev workflow.

AI で拡張された安全なソフトウェア開発における批判的思考の回復
AIの議論は、使用に関するものではなく、応用に関するものです。コードを深く理解している開発者に頼って、AI の生産性向上の必要性と堅牢なセキュリティとのバランスを取る方法をご覧ください。
AI Coding Assistants: With Maximum Productivity Comes Amplified Risks
In our latest whitepaper, our co-founders Pieter Danhieux and Dr. Matias Madou, Ph.D., explore the double-edged sword that is AI Coding Assistants and how they can be a welcome addition and a significant security liability at the same time.

サイバーセキュリティリスク評価:定義と手順
効果的なサイバーセキュリティリスク評価を実施するための実践的なガイドを参考に、組織のサイバーセキュリティリスクに対処しましょう。

Why Cybersecurity Awareness Month Must Evolve in the Age of AI
CISOs can’t rely on the same old awareness playbook. In the Age of AI, they must embrace modern approaches to safeguard code, teams, and organizations.

SCW Trust Agent: AI - Visibility and Governance for Your AI-Assisted SDLC
Learn how Trust Agent: AI provides deep visibility and governance over AI-generated code, empowering organizations to innovate faster and more securely.

AI 時代の安全なコーディング:インタラクティブな AI の新しい課題に挑戦
AI支援コーディングは開発を変えています。新しいコパイロットスタイルの AI チャレンジを試して、現実的なワークフローでコードを安全にレビュー、分析、修正してください。

SCW、開発者向け無料の AI/LLM セキュリティビデオシリーズを開始
12 週間の無料の AI/LLM セキュリティビデオシリーズをご紹介します!AI アシストコーディングの基本的なリスクと、より安全なアプリケーションを構築する方法を学びましょう。
AI/LLM Security Video Series: All Episodes, Updated Weekly
Your all-in-one guide to our 12-week AI/LLM security video series. Catch every episode, learn key AI security concepts, and follow along weekly.

セキュア・コーディングとは?テクニック、標準、リソース
セキュア・コーディングの本当の意味と、セキュア・コーディング・プラクティスが企業の脆弱性とセキュリティ関連コストの両方をどのように削減できるかを学びましょう。

10,000,000 頭頭頭頭位上位:10,000 人前海上競走人
10,000個個人、ing・進金金金、新羅大大、相愛愛愛愛愛愛愛護護護護護護護護護護護護護部10大大子子子。
良いツールが悪くなるとき:AI ツールポイズニング、そして AI がダブルエージェントとして振る舞うのを防ぐ方法
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
標準の設定:SCW が GitHub で無料の AI コーディングセキュリティルールをリリース
AI 支援開発はもはや視野に入っていません。それが実現し、ソフトウェアの記述方法が急速に変化しています。GitHub Copilot、Cline、Roo、Cursor、Aider、Windsurf などのツールは、開発者を独自の共同パイロットに変え、より迅速なイテレーションを可能にし、プロトタイピングから大規模なリファクタリングプロジェクトまですべてを加速させています。
Secure Code Warrior Unraveled: Impact of Secure Developers on Software Metrics
When reflecting on our own technology, SCW’s Developer Risk Management platform, I am buoyed by recent metrics from one of our core enterprise clients, and going down the proverbial rabbit hole into this data tells a tale of a high-adoption, potent Secure by Design initiative that has been proven to considerably reduce risk in their organization.

トゥアコ・ウォアー+ハッカーワンで銀皮がらみつき
セキュア・コード・ウォリアーは、「ブリストライダー」と「ハッカーワン」「シューター・ワン」「VISUREND」。、。HackerOne はは、

明らかに:サイバー業界がセキュア・バイ・デザインを定義する方法
最新のホワイトペーパーでは、共同創設者のPieter DanhieuxとMatias Madou博士が、CISO、AppSecリーダー、セキュリティ専門家を含む20人以上のエンタープライズセキュリティリーダーと対談し、このパズルの重要なピースを解き明かし、Secure by Design運動の背後にある現実を明らかにしました。これはセキュリティチーム全体で共通の野望ですが、プレイブックは共有されていません。

Vibe Codingはコードベースをフラットパーティーに変えるのでしょうか?
バイブコーディングは大学のパーティーのようなもので、AIはすべてのフェスティバルの目玉であり、鍵となるのはAIです。リラックスして、創造性を発揮し、想像力を働かせることができるかを見るのはとても楽しいことですが、樽を数本立てた後、適度に飲む(または AI を使用する)方が、長期的に安全な解決策であることは間違いありません。

エージェントコーディングツールのプロンプトインジェクションとセキュリティリスク
コーディングエージェントがだまされて SQL インジェクションを起こしやすいコードを書いたり、シェルツールをインストールしたり、さらにはユーザーをストーキングしたりした経緯

クエストの紹介:安全なコードジャーニーに新たに加わったもの
クエストは、開発者がインタラクティブな学習を通じて安全なコーディングを習得できるようにし、リスクを軽減し、開発を最適化します
ディケイド・オブ・ザ・ディフェンダー:セキュア・コード・ウォリアーが10歳に
Secure Code Warriorの創設チームは、10年間、あらゆる教訓、勝利、挫折を乗り越え、一丸となって船を導いてきました。私たちは規模を拡大しつつあり、開発者リスク管理のリーダーとして、次の章である SCW 2.0 に立ち向かう準備ができています。
10 Key Predictions: Secure Code Warrior on AI & Secure-by-Design’s Influence in 2025
Organizations are facing tough decisions on AI usage to support long-term productivity, sustainability, and security ROI. It’s become clear to us over the last few years that AI will never fully replace the role of the developer. From AI + developer partnerships to the increasing pressures (and confusion) around Secure-by-Design expectations, let’s take a closer look at what we can expect over the next year.
LLMアプリケーションのOWASPトップ10:新機能、変更点、およびセキュリティを維持する方法
OWASP Top 10の最新アップデートで、LLMアプリケーションの保護を先取りしましょう。新機能や変更点、そしてSecure Code WarriorがジェネレーティブAIのリスクを軽減するための最新の学習リソースをどのように提供しているかをご覧ください。

トラストスコアは、セキュリティ・バイ・デザインのスキルアップ・イニシアチブの価値を明らかにする
私たちの調査によると、安全なコードトレーニングは効果があることがわかっています。Trust Score は、600 を超える組織の 25 万人以上の学習者が 2000 万点以上の学習データを利用したアルゴリズムを使用しており、脆弱性を軽減する上での効果と、この取り組みをさらに効果的にする方法が明らかになっています。

Reactive Versus Preventive Security: Prevention Is a Better Cure
The idea of bringing preventive security to legacy code and systems at the same time as newer applications can seem daunting, but a Secure-by-Design approach, enforced by upskilling developers, can apply security best practices to those systems. It’s the best chance many organizations have of improving their security postures.

開発者にとってのセキュリティスキルのベンチマークのメリット
セキュアコードとセキュアバイデザインの原則への注目が高まる中、開発者はSDLCの開始時からサイバーセキュリティに関するトレーニングを受ける必要があり、Secure Code WarriorのTrust Scoreなどのツールが進捗状況の測定と改善に役立ちます。

You’ve got a friend in me: How AI coding tools and security-aware developers can work together safely
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
企業のセキュリティ・バイ・デザイン・イニシアティブの有意義な成功を促す
最新の研究論文「セキュリティスキルのベンチマーキング:企業におけるセキュリティバイデザインの合理化」は、企業レベルでの実際のセキュリティバイデザインの取り組みを詳細に分析し、データ主導の調査結果に基づいてベストプラクティスのアプローチを導き出した結果です。
ディープダイブ:GNU-Linuxシステムにおける重大なCUPSの脆弱性の対処法
Common UNIX 印刷システム (CUPS) における最近の重大度の高い脆弱性を調査しながら、Linux ユーザーが直面している最新のセキュリティ上の課題をご覧ください。これらの問題がどのようにリモートコード実行 (RCE) につながる可能性があるのか、またシステムを保護するためにできることを学びましょう。
How exceptional CISOs are igniting the security fire in their development team
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
コーダーがセキュリティを征服:共有して学ぶ-クロスサイトスクリプティング (XSS)
クロスサイトスクリプティング (XSS) は、ブラウザーの信頼とユーザーの無知を利用して、データを盗んだり、アカウントを乗っ取ったり、ウェブサイトを改ざんしたりします。この脆弱性は、あっという間にひどいものになってしまいます。XSS の仕組み、どのような被害が及ぶ可能性があるか、そしてそれを防ぐ方法を見ていきましょう。

How the best CISOs leverage people and technology to become true superstars
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

DigitalOceanがソフトウェアセキュリティの負債を減らし、生産性の限界を押し広げた方法
Secure Code Warriorは、DigitalOceanが最初から高品質のコードを作成してリリースするのを支援し、セキュリティ意識の高い開発者とともにデジタルイノベーションとモダナイゼーションを推進しました。

Women in Security are Winning: How the AWSN is Setting Up a New Generation of Security Superwomen
Secure-by-Design is the latest initiative on everyone’s lips, and the Australian government, collaborating with CISA at the highest levels of global governance, is guiding a higher standard of software quality and security from vendors.

SCW Trust Agent-開発者主導型セキュリティを拡大するための可視性と制御
Secure Code Warriorによって導入されたSCW Trust Agentは、開発者が主導するセキュリティを組織内で拡大するために必要な可視性と制御をセキュリティリーダーに提供します。コードリポジトリに接続することで、コードコミットのメタデータを評価し、開発者、使用したプログラミング言語、および出荷タイムスタンプを検査して、開発者のセキュリティ知識を判断します。

御社のセキュリティプログラムはCISAのサイバーセキュリティ戦略計画に対応できていますか?
サイバーセキュリティ戦略計画は、ほとんどの組織がサイバーセキュリティに取り組む方法に大きな変化をもたらしますが、開発者はこれらの新しい目標の達成を支援する独自の立場にあります。
Don’t ignore what developers need for a successful software security journey
It's becoming apparent that while cybersecurity platforms and defenses are critical components in defense against modern attacks, what is truly needed is secure code that can be deployed free from vulnerabilities. And that requires security-aware developers with verified security skills.
エンゲージ&エンパワー:デベロッパーエンゲージメントの主要機能を紹介
アジャイル学習手法、Microsoft Teams インテグレーション、および開発エンゲージメントに関するレポートについて詳しく学んでください。
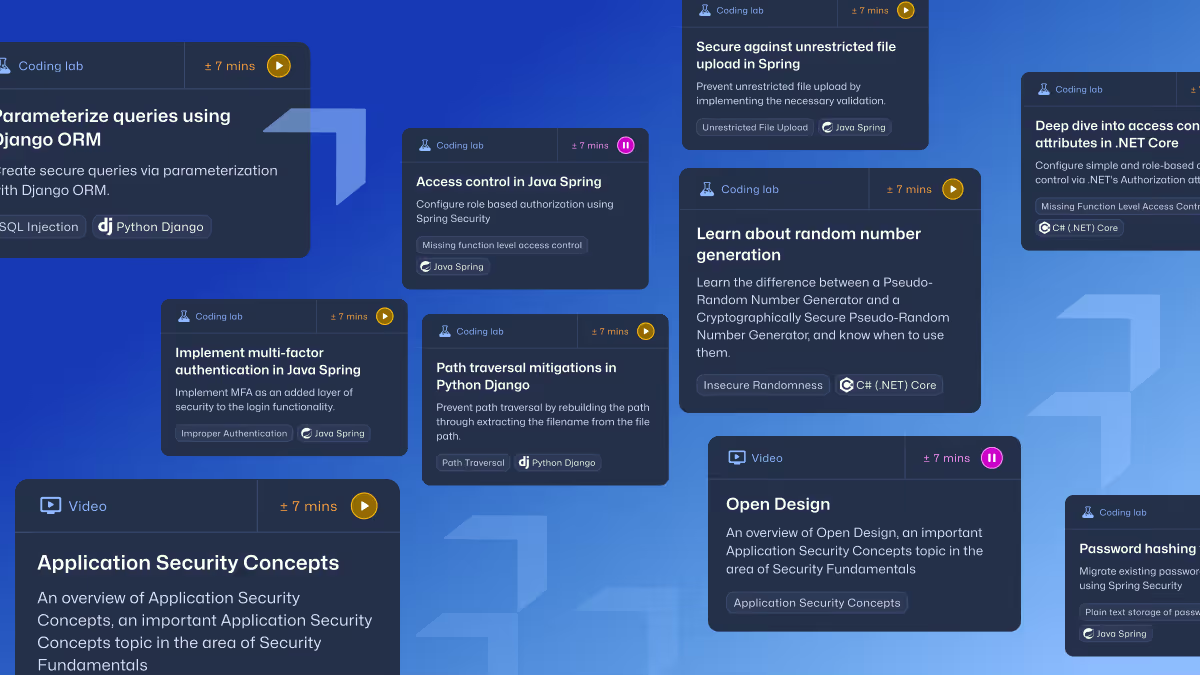
開発者の能力強化:コンテンツをオンデマンドで学習することの重要性
セキュア・コード・ウォリアーでデベロッパーを支援しましょう。当社のプラットフォームは、開発者がオンデマンドでコンテンツを学習できるようにし、支援します。
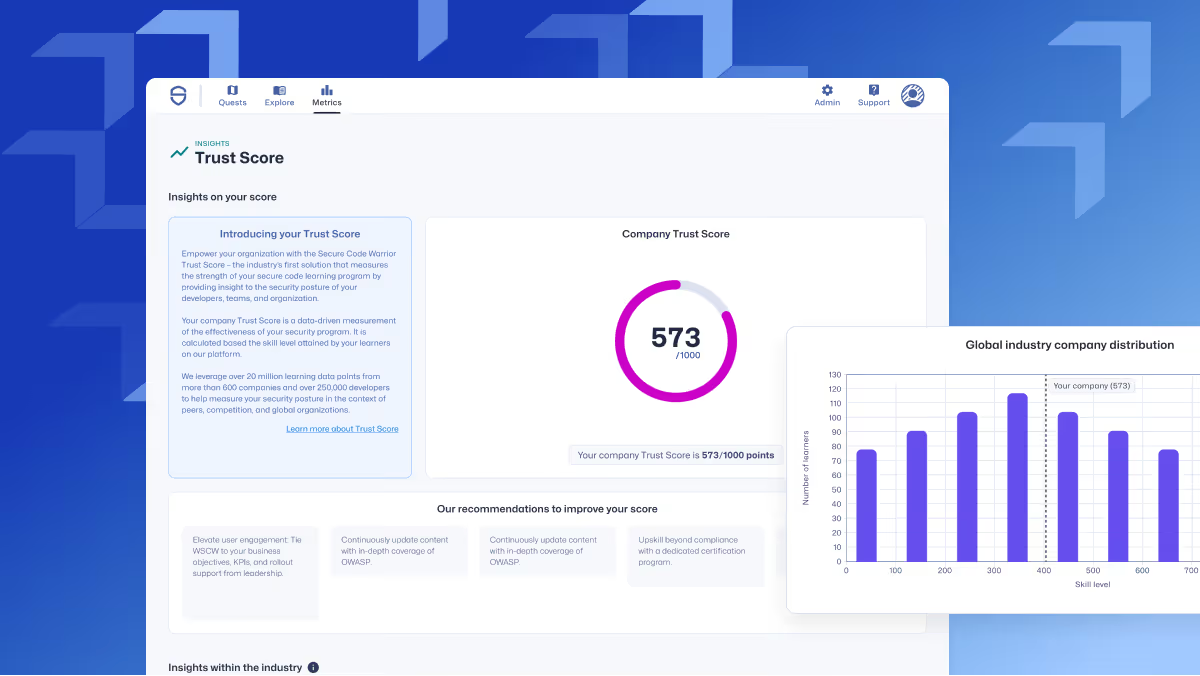
SCW Trust Score: セキュアコーディングプログラムの業界初の指標
組織のセキュリティと開発者の能力に関する深い洞察を提供する SCW Trust Score をご覧ください。

FinServ コンプライアンスはソフトウェアセキュリティに依存
PCI DSSなどの金融サービス業界を統制する規制は、安全なコードの重要性と、セキュリティのベストプラクティスについて開発者を訓練する必要性を強調しています。
LinuxのXZ Utilsバックドアは、より広範なサプライチェーンのセキュリティ問題を示しており、それを食い止めるにはコミュニティ精神以上のものが必要です
主要なLinuxディストリビューションで使用されているXZ Utilsデータ圧縮ライブラリに、脅威アクターによるバックドアを通じて導入された重大な脆弱性CVE-2024-3094が発見されました。この重大度の高い問題により、リモートでコードが実行される可能性があり、ソフトウェアビルドプロセスに重大なリスクをもたらします。この欠陥は Fedora Rawhide の XZ Utils の初期バージョン (5.6.0 と 5.6.1) に影響を及ぼし、組織にパッチを実装するよう緊急に求められています。この事件は、オープンソースソフトウェアの維持におけるコミュニティボランティアの重要な役割を浮き彫りにするとともに、ソフトウェア開発ライフサイクルにおけるセキュリティ対策とアクセス制御の強化の必要性を浮き彫りにしました。
AI イノベーションのメリットを享受できるかどうかは、安全なコードから始めることにかかっています
ジェネレーティブAIは、金融サービス企業に多くの利点をもたらすだけでなく、多くの潜在的なリスクももたらします。セキュリティのベストプラクティスを開発者に教え、それを AI モデルと組み合わせることで、最初から安全なコードを作成できます。

AIとプロアクティブな対策を活用して脆弱性アラートを効果的に管理する
Secure Code WarriorとMend.ioは、AIがセキュリティに与える影響、積極的なセキュリティアプローチ、脆弱性アラートの効果的な管理について話し合っています。
セキュア・コード・ウォリアー第1四半期プロダクトイノベーション
Secure Code Warriorプラットフォームの最新の改善点と、近日公開予定の機能についてご紹介します。
セキュア・コーディングの設計図をナビゲートする:構築上のアナロジー
安全なコーディング手法に従うことで、開発者は攻撃者に悪用される可能性のある脆弱性からアプリケーションを保護することができます。よくできた家が倒壊しにくいのと同じように、適切にコーディングされたアプリケーションはハッキングされる可能性が低くなります。

平均修復時間 (MTTR) 改善のためのアジャイルラーニングの採用
アジャイルラーニングは、継続的な学習によって問題解決を促進し、開発者の効率を高めます。
適切なサポートがあれば、開発者は組織を優れた PCI DSS 4.0 コンプライアンスに導くことができます
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
LLM: 安全なコーディングのための(私の)完全に人間的なアプローチですか?
LLMスタイルのAIテクノロジーが、ソフトウェア開発だけでなく、仕事の多くの側面へのアプローチ方法を変えることは避けられないように見えますが、私たちは一歩下がって、見出しの先にあるリスクを考慮する必要があります。そして、コーディングのお供としては、その欠点はおそらく最も「人間的」な特徴でしょう。

パワー・オブ・ナイン:サイバーセキュリティにとってエキサイティングな時代におけるセキュア・コード・ウォリアーの遺産の成長
今日は私たちの9歳の誕生日です。状況が急速に変化し続ける中、サイバーセキュリティの世界における私たちの業績と永続的な地位を今でも非常に誇りに思い、感謝しています。

セキュリティツールの急増に悩まされている
複雑なセキュリティツールが氾濫していることで、サイバーセキュリティはCISOにとってさらに困難になっています。

API-led data breaches are creating pandamonium for security teams. Why do we make it so easy for threat actors to exploit them?
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

2024年の予測:セキュリティ、AI、開発者の定着率、そして今後の展望
Secure Code Warriorは、2024年以降のサイバーセキュリティ業界に関する予測のトップ10にランクインしています。

Netskopeがセキュアコード教育をどのように再考したか
Netskopeが導入したアジャイル学習環境に焦点を当てたSCWケーススタディブログ。

ディープダイブ:AI コーディングアシスタントによって生成された脆弱性の解決
ソフトウェア開発におけるAIのセキュリティリスクを探り、Secure Code Warriorでこれらの課題に効果的に対処する方法を学びましょう。

eounrccairknrし、burweweを 53% ちくれ3FOOさん
れぶつぎぎし、水分、みみみも、れきにれきついものものものものものものものつみつらい。

Secure Code Warrior 2023: Innovations, achievements, and insights
Explore Secure Code Warrior’s 2023 journey to empower developers, enhance productivity, and mitigate risk in cybersecurity with recent innovations to our agile learning platform.
Attack of the Zombie APIs: Who is leading the security counteroffensive in your organization?
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
組織のセキュリティ成熟度を過大評価していませんか?
世界中のソフトウェアニーズを満たすために大量のコードが開発されていることと相容れないスキル不足が続いているため、多くの企業がサイバーセキュリティ戦略と既存のインフラストラクチャに遅れをとっています。今こそ、サイバーセキュリティ全体の成熟度を正直に見て、目の前にある実行可能な手っ取り早い成果を評価する時です。

セキュリティを強化するための開発者教育の見直し
セキュリティリーダーは、開発者が安全なコード学習体験から得られる価値と、プログラムをより魅力的に、そして最も重要なこととしてよりインパクトのあるものにする方法を再考する必要があります。このブログでは、より多くの実践的な学習とツールとの統合を通じて、開発者が安全なコード教育に興味を持ってもらい、大きな成果をもたらし、導入される脆弱性を最大 53% 削減する方法を探ります。
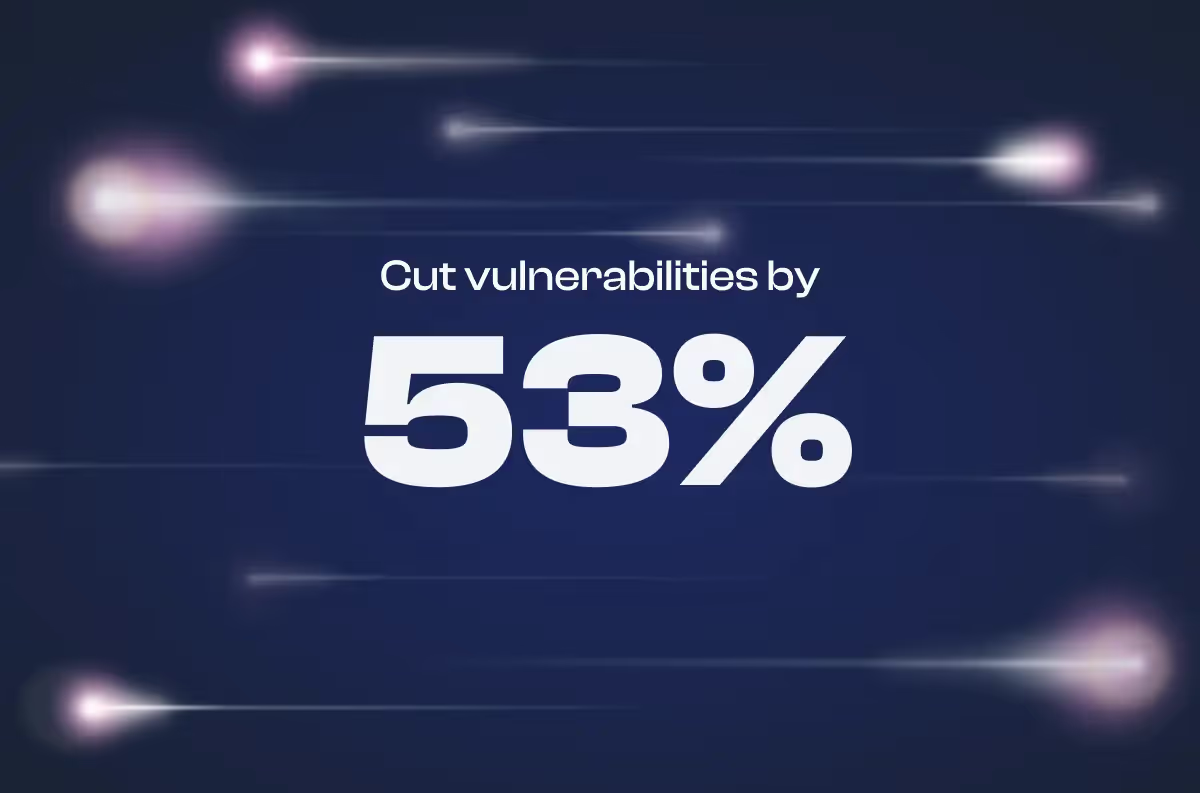
アジャイルラーニングで脆弱性を半減させる
Secure Code Warriorの実践型アジャイルセキュリティトレーニングで、脆弱性とセキュリティ侵害を減らす方法を学びましょう。

ディープダイブ:重大度の高いlibcurl/curlの脆弱性の発見と修正
影響を受けるバージョンの curl ライブラリは、SOCKS5 プロキシプロトコルのレガシー問題に関連する、ヒープベースのバッファオーバーフローの脆弱性の影響を受けます。この種の脆弱性を見つけて修正する方法を、プレイ可能なミッションで学びましょう。
世界クラスのCISOが2023年に予算と取締役会の信頼をどのように獲得しているか
CISOは、より多くの資産を保護し、より多くのコードを発送し、より大きな攻撃対象領域を減らし、それを急速に減少する財源で行うという、ますます困難な状況に陥っています。サイバーセキュリティはコストセンターと見なされていることは避けられない事実です。組織のセキュリティプログラムは、脅威アクターが明日の悲惨な見出しで取り上げるのを妨げるものですが、セキュリティリーダーは、執行機関にとって意味のある言葉で、部門全体のビジネス価値を売り込み、証明するためにより多くのことをしなければなりません。
ディープダイブ:MOVEit のゼロデイ脆弱性を間近で見る
MOVEit のシナリオは、多くの開発者やアプリケーション・セキュリティ・プロフェッショナルがこれまでに経験したことがあるシナリオとは少し異なります。ここでライブ・シミュレーションで SQL を駆使するスキルをテストできます。


Kamer van Koophandelが確立した、大規模な開発者主導型セキュリティのスタンダード
Kamer van Koophandel(オランダ商工会議所)が、役割別の認定制度、Trust Scoreによるベンチマーク、そしてセキュリティを全員で担う文化を通じて、どのようにセキュアコーディングを日常の開発業務に組み込んだかをご紹介します。
ゴールドを目指して:Paysafeで高まるセキュアコーディング基準
PaysafeとSecure Code Warriorのパートナーシップにより、開発者の生産性が45%向上し、コードの脆弱性が大幅に削減された事例をご覧ください。
DigitalOcean Decreases Security Debt with Secure Code Warrior
DigitalOcean's use of Secure Code Warrior training has significantly reduced security debt, allowing teams to focus more on innovation and productivity. The improved security has strengthened their product quality and competitive edge. Looking ahead, the SCW Trust Score will help them further enhance security practices and continue driving innovation.
Devlympics 2023:振り返り
Devlympics 2023のレポートで結果をご覧ください。参加した各業界における開発者のエンゲージメント、技術スタックや言語のトレンド、そしてSecure Code Warriorが主催するこの年次グローバルイベントで取り上げられた主要な脆弱性やCWEについて詳しく解説します。

セキュリティ文化の統一:Sageはいかにしてアジャイルなセキュアコーディング学習でセキュリティチャンピオンプログラムを構築したか
Sageが柔軟かつ関係性を重視したアプローチでセキュリティを強化し、200名以上のセキュリティチャンピオンを育成して、測定可能なリスク低減を実現した事例をご紹介します。

セキュリティチャンピオンへの道:Workdayはいかにしてアジャイル学習で開発者のスキルアップを実現したか
WorkdayがSecure Code Warriorのアジャイル学習を通じて、どのように開発者トレーニングを変革したかをご紹介します。Workdayは、言語別の実践的な教育を開発者に提供することで、SDLCの初期段階における脆弱性を削減しました。セキュアなコード文化を構築するための、彼らの素晴らしい成果と重要なポイントをご覧ください。
タレスはいかにして開発者主導のセキュリティを実現したか
本ケーススタディでは、タレス(Thales)がアジャイルなセキュアコーディング学習プログラムのために、人、プロセス、テクノロジーをどのように統合し、開発者が自発的にセキュリティチャンピオンとして活躍できる環境を構築したかをご紹介します。
コルゲート・パルモリーブはいかにして開発者のセキュリティスキルを向上させ、セキュアコーディングの文化を築いたか
小売大手コルゲート・パルモリーブが、デジタルトランスフォーメーションの過程でどのようにアプリケーションセキュリティを再構築したかをご紹介します。セキュアコーディングの課題に直面していた同社は、開発者のワークフローに短時間で学べるコンテキストに応じた学習を取り入れることで、アプローチを刷新しました。
Security as culture: How Blue Prism cultivates world-class secure developers
Learn how Blue Prism, the global leader in intelligent automation for the enterprise, used Secure Code Warrior's agile learning platform to create a security-first culture with their developers, achieve their business goals, and ship secure code at speed

Supercharged Security Awareness: How Tournaments are Inspiring Developers at Erste Group
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
「Game of Codes」が導く、IAGグループのより安全なコーディングの未来
IAGグループは、アジア太平洋地域をリードする数多くの保険会社を傘下に持ち、数百万人の顧客に対して年間約114億豪ドルの保険料で保険契約を引き受けています。

Driving Actionable Awareness: FINRA's Push For Super-Secure Developers
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

革新的なセキュリティ認定体験の創造
機械学習やサイバーセキュリティなど、多岐にわたる分野で実践的かつ最先端のスキルを数千人の従業員が習得できるよう支援する、社内技術教育イニシアチブの構築事例をご紹介します。

Beyond Compliance: Motorola Solutions Drives Winning Security Culture
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

ASRGによる自動車ソフトウェアセキュリティの推進
この包括的なケーススタディでは、Secure Code Warriorのトーナメントを活用して開発者の関与を促し、自動車ソフトウェアに影響を与える主要な脆弱性への意識を高め、複数の言語やフレームワークにわたる指標を収集した事例を紹介します。

Application Security @ NAB | Gamified Security Training: The Key to Scalable Developer Growth
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
SD Times: Benchmarking AI-assisted developers (and their tools) for superior AI governance
If the tech stack lacks tools that oversee not only developer security proficiency, but also the trustworthiness of approved AI coding companions each developer uses, then it is likely that efforts to uplift the overall security program and the developers working within it will be short of the appropriate data insights to effect change.
ITWire: The Benefits and Risks of Using AI Tools in Software Development
The process of software development is undergoing a period of expedited change. Thanks to massive advances in artificial intelligence (AI) technology, projects can be completed more rapidly and by people with little or no prior experience.

LeadDev: Ethics are being forgotten as the AI race heats up
Is the tech industry capable of the change needed to curb ethical and environmental concerns?
Secure Code Warrior Expands Commitment to Secure by Design Best Practices with Free Secure Code Video Series for Developers
Launch of new 12-week video series on AI/LLM security empowers developers to safely adopt AI coding and mitigate emerging security risks.

CSO Online: When AI nukes your database: The dark side of vibe coding
As developers lean on Copilot and GhostWriter, experts warn of insecure defaults, hallucinated dependencies, and attacks that slip past traditional defenses.

The AI Journal: Resilience and Developer Risk Management: Two Pillars of Success in the Era of Secure by Design and AI Coding
Change is afoot in cybersecurity governance, and it couldn’t come at a more transformative time for security leaders worldwide. The White House issued a recent Executive Order (EO) designed to “reprioritize cybersecurity efforts to protect America”, and with it, reduce friction related to overzealous government oversight to focus on protecting critical digital assets and enhanced secure technology practices. Coupled with significant cuts to CISA, one could be forgiven for being apprehensive of the right approach going forward, especially in the wake of rapid AI technology progression and Secure by Design initiatives.

SecurityWeek: How to Close the AI Governance Gap in Software Development
Widespread adoption of AI coding tools accelerates development—but also introduces critical vulnerabilities that demand stronger governance and oversight.

teiss: When regulations aren’t enough
Pieter Danhieux at Secure Code Warrior explains why “Secure by Design” has emerged as mission critical for software development

Information Age: Vibe coding is a hot skill – and security experts are worried
GenAI tools are building insecure apps faster than ever.

CXFocus Magazine: Going above and beyond in 2026
Today’s customers are an exacting lot with little tolerance for suppliers that fail to meet their ever-increasing expectations. Almost 94 per cent of Australian consumers stopped purchasing from at least one company after a negative experience, according to CPM’s 2025 The State of Customer Experience in Australia Report.

SafetyDetectives: Interview With Matias Madou - CTO and Co-Founder at Secure Code Warrior
SafetyDetectives recently sat down with Matias Madou, CTO and Co-Founder of Secure Code Warrior, to discuss his journey from software developer to cybersecurity leader and entrepreneur. With a background in security research, obfuscation techniques, and nearly a decade at Fortify, Matias has seen firsthand how critical it is to upskill developers if organizations hope to defend against modern threats. In this interview, he shares how Secure Code Warrior is helping organizations foster a security-first development culture, the risks and opportunities of AI-driven coding tools, and why the path to safer software must always begin with better-trained developers.

Dark Reading: Do Claude Code Security Reviews Pass the Vibe Check?
AI-assisted security reviews from Anthropic and others could help level up enterprise application security in the era of vibe coding.

GovTech Review: The global challenge of achieving cyber resilience
Concerningly, 2030 is only five years away, and cybersecurity efforts — whether national, international or specific to organisations — still face many of the same barriers that have always hampered comprehensive security. For this reason there remains a question mark over whether countries will be able to meet their 2030 goals.

KBI Media: AI Coding Assistants Boost Productivity … But At What Cost to Security?
As the pressure mounts to ship faster and innovate more aggressively, development teams must remember that code security is no longer optional but a business-critical necessity.
Forbes: Beware Of Agentic AI’s Heel Turn As Corporate Security Villain
Enterprises need to assert AI governance and ensure that developers are equipped to maintain oversight, with the security skills to safely prompt and review AI-assisted code and commits.
Techradar Pro: Why continuous security improvement for developers is the key to renewed resilience
While change can be challenging to navigate, the current security climate feels like the perfect time to embrace measures that will improve software quality and reduce risk for years to come.
DevOps Digest: From Helper to Hacker: How AI Tools Can Be Turned Against You
A recent finding by InvariantLabs uncovered a critical vulnerability in the Model Context Protocol (MCP), an API-like framework allowing powerful AI tools to autonomously interact with other software and databases, that allows for what has been dubbed "Tool Poisoning Attacks," a new vulnerability category that could prove especially damaging in the enterprise.

Technology Decisions: Secure by Design: Vital in an evolving threat landscape
In the evolving world of software development, a familiar term is gaining renewed urgency: Secure by Design.

Information Week: Will Any Countries Meet the Cyber Resilience Challenge?
One of the key hurdles facing nations and enterprises in achieving cyber resilience goals is the lack of security personnel and advanced security skills.

SecurityBrief Australia: The risks of using AI in the software development pipeline
AI coding assistants are not going away, and the upgrade in code velocity cannot be ignored. However, security leaders must act now to manage their use safely.

ITWire: AI Appreciation Day
Artificial Intelligence Appreciation Day celebrates the way AI has changed our lives for the better. This year, we speak to AI leaders to analyse what the next wave of innovations has in store for us and their transformative impact on various industries worldwide.

Dynamic Business: AI Appreciation Day: What business leaders really think about AI right now
On AI Appreciation Day, industry experts reveal how smart, responsible AI use is transforming business, empowering people, and driving meaningful innovation.

In AI Today: How to keep AI-assisted software development under control
Faced with large workloads and relentless deadlines, developers are understandably inclined to turn to third-party AI tools, sometimes without vetting them or getting approval from supervisors. It’s creating a trend dubbed ‘Shadow AI’. This should be of concern for all senior executives as unmanaged AI decreases overall enterprise visibility of development processes while increasing the potential for new vulnerabilities that are not adequately captured or managed.

Help Net Security: Cybersecurity essentials for the future: From hype to what works
Cybersecurity never stands still. One week it’s AI-powered attacks, the next it’s a new data breach, regulation, or budget cut. With all that noise, it’s easy to get distracted. But at the end of the day, the goal stays the same: protect the business.

Cyber Daily: Bad practices are increasing security risks within software development projects
A recent CISA discussion paper details some exceptionally risky software development activities that are in all-too-common use.

Techstrong.tv: [VIDEO] Secure Code Warrior CTO Matias Madou on Empowering Developers with AI-Driven Security Tools
Matias Madou, CTO and Co-Founder of Secure Code Warrior, shares his journey in app security and how AI is helping developers write secure code. He introduces new AI security rules, available free on GitHub, and discusses the future of development tools and AI solutions.
DevOps.com: Secure Code Warrior Defines Security Rules for AI Coding
Secure Code Warrior has made available a set of security rules for application developers using artificial intelligence (AI) tools to generate code.

SecurityBrief Australia: Secure Code Warrior unveils free AI security rules for developers
Secure Code Warrior has released AI Security Rules on GitHub, offering developers a free resource aimed at improving code security when working with AI coding tools.
KBI Media: Overcoming The Complexity And Security Issues Posed By AI Coding Tools
The current software environment has grown out of control security-wise and this trend shows no signs of slowing. However there is hope for slaying the twin challenges of complexity and insecurity.
Secure Code Warrior Unveils Industry-First AI Coding Rulesets to Guide Safer AI Code Deployment
Secure Code Warrior, the leading developer risk management company, today announced the availability of AI Security Rules on GitHub – a first-of-its-kind, free resource to help developers generate more secure code when working with AI coding tools like GitHub Copilot, Cline, Roo, Cursor, Aider and Windsurf.
Help Net Security: Free AI coding security rules now available on GitHub
Developers are turning to AI coding assistants to save time and speed up their work. But these tools can also introduce security risks if they suggest flawed or unsafe code. To help address that, Secure Code Warrior has released a new set of free AI Security Rules on GitHub.

DevPro Journal: Secure Code Warrior unveils AI coding rulesets to guide safer AI code deployment
Community-driven resource empowers developer teams of all sizes to integrate AI safely into critical workflows.

SD Times: Managing the growing risk profile of agentic AI and MCP in the enterprise
Security leaders need to take a hard look at how these risks affect their business, being sure they understand the potential vulnerabilities that result from using agentic AI and MCP, and take the necessary steps to minimize those risks.

HackerOne Launches Technology Alliance Program to Advance AI-Powered Security Ecosystem and Customer Innovation
HackerOne, a global leader in offensive security solutions, today announced the launch of its PartnerOne Technology Alliance Program. The initiative is designed to accelerate secure innovation by connecting leading technology providers with HackerOne’s AI-powered platform that seamlessly scales human security expertise through AI agents to not just find but remediate vulnerabilities.
Dark Reading: Next-Gen Developers Are a Cybersecurity Powder Keg
AI coding tools promise productivity but deliver security problems, too. As developers embrace "vibe coding," enterprises face mounting risks from insecure code generation that security teams can't keep pace with.

Conversational AI News: Training Developers to Build Defensively with AI
Today we're meeting Pieter Danhieux, CEO & Co-Founder at Secure Code Warrior. They specialise in secure coding practices and developer risk management.
ITWire: The Importance Of Security Benchmarking When Using AI Development Tools
If it was possible to have an experienced chef in the kitchen to help prepare a sophisticated dish, most people would happily accept the assistance. The same holds true for a qualified contractor to work on a home-improvement project, or an office aide to handle tedious, repetitive tasks.
DevOps Digest: Fix It or Face the Consequences: CISA's Memory-Safe Muster
While CISA's efforts can help companies navigate the "need for speed" in a fast-moving DevOps environment, IT and security leaders across the private sector must do their part to prepare their companies for the necessary changes.

SC Magazine UK: Secure-by-Design Is Hard, but Our Online Future Depends on It
Secure software hinges on introducing security at the beginning of the SDLC.
ITWire: Experts Confirm DeepSeek Too Insecure for Enterprise Deployment
While DeepSeek’s capabilities seem to be extensive, experts have identified significant failings – particularly from a security perspective.
Cyber Daily: Secure-by-design principles struggle to find unified enterprise adoption
While awareness of the concept of ‘Secure by Design’ is growing within many organisations, its usage remains fragmented and inconsistent.

Built In: How to Tame ‘Unleashed’ AI-Assisted Software Development
The rise of AI coding assistants in software development has introduced new vulnerabilities. Our expert, Dr Matias Madou, offers advice for stemming the tide.

Cybersecurity Tribe: Experts Reveal How Agentic AI Is Shaping Cybersecurity in 2025
We were lucky enough at RSAC 2025 to interview a series of industry experts to explore this issue, "Where exactly are we with Agentic AI in cybersecurity in 2025?"

DevOps.com: How Benchmarking Can Help Software Development Teams Achieve CISA’s “Secure by Design”
Organizations can more readily achieve CISA’s Secure by Design through benchmarking by implementing the following developer-centric best practices.

Bank Info Security: Secure by Design: Moving Beyond Checkbox Compliance
Secure Code Warrior CEO Danhieux Urges Clarity Around Secure-by-Design Practices.

SecurityWeek: Developers Must Slay the Complexity and Security Issues of AI Coding Tools
The advantages AI tools deliver in speed and efficiency are impossible for developers to resist. But the complexity and risk created by AI-generated code can’t be ignored.

The AI Journal: Why Security Benchmarking Has Emerged as Critical for AI in Software Development Tools
In the last five years, nearly two-thirds of IT executives and administrators say their organisation has incorporated AI tools into the software development lifecycle (SDLC), according to research from KPMG and OutSystems, which makes available a low-code, AI-supported platform to build applications.
KBI Media: How Adopting Maturity Models Can Improve Enterprise IT Security
With risk assessments becoming a higher priority, organisations need to take an approach with developer-driven security that actively targets developer risk management, skills enhancement and strategic repository “gatekeeping”. Initiatives that can help them stay on course while assessing their current security levels and creating an action plan that aligns with BSIMM or OWASP SAMM.
Forbes: How Companies Can Chart The Way Along The Secure-By-Design Path
From our own observations, we've found that organizations generally need three to five years to fully integrate SBD into their software development practices as part of a developer risk management commitment. But we've also seen that it’s well worth the time and effort: Within the context of the software development life cycle (SDLC), SBD promotes a “security first” enterprise culture and mindset in eliminating vulnerabilities as early as possible in the process.

TechRadar Pro: Secure by design: what we can learn from the financial services sector
Secure by design in software development, inspired by financial services.

Dynamic Business: 26 Aussie startups to unleash cyber fixes at ACE 25
The Australian Cyber Exchange 2025 (ACE 25), in collaboration with the Tech Council of Australia (TCA), rolled out in Sydney and is aimed at building up Australia’s own cyber capabilities.
iTWire: The Tech Council of Australia Bolsters Collaboration To Building Sovereign Capability To Keep Australians Safe
The Tech Council of Australia (TCA) is collaborating with industry and government leaders to advocate for the national approach across the cyber ecosystem and is reinforcing its position on building sovereign cyber security capability.

Intelligent CIO: The Tech Council of Australia bolsters collaboration to building sovereign capability
Collaboration pitched as a critical step to ensure industry and government are taking a coordinated approach to building Australia’s cyber security and resilience.
KBI Media: How Organisations Can Achieve Secure-By-Design By 2030
Governments worldwide, from the UK to Australia, have set ambitious goals to enhance software security by 2030, particularly within critical infrastructure. However, achieving a secure-by-design (SBD) approach is not merely a matter of deploying advanced security tools or implementing stringent policies. Rather, it necessitates a fundamental shift in organisational culture, prioritising security at every level of software development.
Cyber Daily: Paving a pathway to better Australian cyber security preparedness
Australia’s goal of seeding a zero-trust culture across all organisations can be significantly achieved by focusing on the first line of defence against threat actors: software developers.
SecurityWeek: Security Maturity Models: Leveraging Executive Risk Appetite for Your Secure Development Evolution
Organizations can align their processes with one of two global industry standards for self-assessment and security maturity—BSIMM and OWASP SAMM.

SD Times: DeepSeek is unsafe for enterprise use, tests reveal
The birth of China’s DeepSeek AI technology clearly sent shockwaves throughout the industry, with many lauding it as a faster, smarter and cheaper alternative to well-established LLMs. However, similar to the hype train we saw (and continue to see) for the likes of OpenAI and ChatGPT’s current and future capabilities, the reality of its prowess lies somewhere between the dazzling controlled demonstrations and significant dysfunction, especially from a security perspective.

Energy Source & Distribution: How to boost security of Australia’s critical infrastructure
Increasing technical complexity and a widening attack surface are making life tough for IT security professionals. Faced with an evolving threat landscape, the pressure is on to deploy and maintain effective protection for critical infrastructure.

KBI Media: A Supercharged Security Culture is Needed to Navigate Australia’s Cybersecurity Rules
A success marker in cybersecurity has traditionally been for an organisation to have an uneventful year – but this has become much harder to pull off. Even if an organisation manages to navigate the threat landscape without incident, it must still meet an ever-growing list of requirements just to maintain its license to operate. Australian CISOs have never had to deal with a greater number of legislative and regulatory requirements being imposed to drive secure behaviours and uplift collective cybersecurity postures.

Intelligent CISO: Q&A: How organizations can achieve Secure-by-Design by 2030
Matias Madou, Co-founder and CTO, Secure Code Warrior, says Secure-by-Design (SBD) requires a cultural shift in how developers approach security.
Cyber Daily: Finalists revealed for the Australian Cyber Awards 2025
Cyber Daily has unveiled that more than 220 finalists have been selected out of over 300 submissions for the annual Australian Cyber Awards.

Manufacturing.net: Rethinking Critical Infrastructure: A Secure Path for High-Risk Connectivity
Digital frontiers are highly prized targets, and this will ramp up in the coming years.
KBI Media: Understanding The Risks Associated With ‘Shadow AI’ In Software Development
According to research by the Australian Government’s Department of Industry, Science and Resources[1], 35% of small and mid-sized businesses are already using AI tools and usage is expected to continue to increase. Applications include everything from marketing automation and fraud detection to data and document processing.
Cyber Daily: The Industry Speaks: Data Privacy Day 2025
January 28 is International Data Privacy Day, and this year’s theme is ‘Taking Control of Your Data’ – here’s some expert advice and perspectives on how to do just that.

DevOps.com: How to Prove That Your Security-Aware Developers are a Cut Above the Rest
Companies that need to respond by upskilling their developers should take a three-tiered approach that includes implementing a measured program to deliver education and competency, providing right-fit tools that suit the organization’s tech stack, and overhauling the processes that have led to cut corners and insecure coding patterns running rampant.

DevOps.com: Navigating the Next Wave of Cybersecurity Legislation With a Supercharged Security Culture
CISA’s Secure-by-Design guidelines are gaining traction as a higher standard for software vendors to achieve, while updates from NIST, PCI and the EU-wide NIS2 Directive are having a global impact on many enterprise companies. Smart CISOs are utilizing their full team potential through role-based upskilling and especially enabling the development cohort to take pressure off the AppSec team by honing their security prowess on an ongoing basis.

teiss: Balancing AI innovation and security
LLMs struggle to generate consistently secure code. Security-skilled developers can help ensure secure AI-generated code while optimising performance. Pieter Danhieux at Secure Code Warrior explores a CISO’s role in AI-powered coding.

Dark Reading: OWASP's New LLM Top 10 Shows Emerging AI Threats
Ultimately, there is no replacement for an intuitive, security-focused developer working with the critical thinking required to drive down the risk of both AI and human error.
KBI Media: Cybersecurity’s Evolution And The Shift Toward Secure-By-Design Principles
In the ever-changing landscape of cybersecurity, experts are increasingly advocating for Secure-by-Design principles to address the accelerating challenges of today’s digital world. The concept emphasises embedding security into software from the beginning of the development process in a shift that reflects a significant maturation of the cybersecurity industry.
SecurityWeek: How to Eliminate “Shadow AI” in Software Development
With a security-first culture fully in play, developers will view the protected deployment of AI as a marketable skill, and respond accordingly.
SecurityBrief Australia: How AI and software development will continue to shape the developer community in 2025
Organisations are facing tough decisions on AI usage to support long-term productivity, sustainability, and security ROI.It's become clear to us over the last few years that AI will never fully replace the role of the developer. From AI + developer partnerships to the increasing pressures (and confusion) around Secure-by-Design expectations, here's what we can expect over the next year.
ITWire: Why Software Developers Need a Security ‘Rewards Program’
Frequent flyer and other points-based programs reward people who remain loyal to particular brands or organisations. The programs issue points to participants who can use them for discounts or purchases in the future. Some airline programs also reward loyal customers with perks such as priority boarding and lounge access. It’s becoming clear that the software development industry could use something similar, especially when it comes to ensuring a ‘security first’ mindset among developers.

In AI Today: Achieving effective security in an AI-assisted software development world
It’s highly likely that AI-assisted development will become even more of a norm in the near future. Organisations will, therefore, have to establish policies and best practices to effectively manage it, just as they’ve done with cloud deployments, Bring Your Own Device (BYOD), and other tech-in-the-workplace trends.
DevOps Digest: 2025 DevSecOps Predictions
As part of DEVOPSdigest's annual list of DevOps predictions, DevSecOps experts — from analysts and consultants to the top vendors — offer thoughtful, insightful, and often controversial predictions on how DevSecOps and related risks and tools will evolve in 2025.
SecurityWeek: How to Implement Impactful Security Benchmarks for Software Development Teams
Benchmarking is all about taking back control – you’re measuring to gain complete awareness of your development teams’ security skills and practices.
KBi Media: Secure-By-Design Is A Significant Exercise, But The Rewards Are Significant, Too
Concerted multilateral efforts are underway to influence and change developer behaviour when it comes to secure software creation.

The Peter Carr Blog: Gary Kasparov and the New Code Generation
Man vs. Machine in the Era of AI and Secure Coding.

VMBlog: OpenText Partners with Secure Code Warrior to Deliver Comprehensive Application Security and Customized Developer Risk Management
OpenText announced a strategic partnership with Secure Code Warrior to integrate its dynamic learning platform into the OpenText Fortify application security product suite. This partnership will help developers improve their secure coding skills through real-time training to reduce risks, quickly identify and resolve vulnerabilities, and ultimately build greater trust with customers.

SecurityInfoWatch: OpenText partners with Secure Code Warrior to deliver comprehensive app security
The new agreement empowers development teams with continuous upskilling to turn security into a strategic advantage, reduce risks, and elevate customer trust.
SecurityBrief Australia: OpenText partners with Secure Code Warrior to boost security
OpenText and Secure Code Warrior have announced a strategic partnership to integrate Secure Code Warrior's dynamic learning platform into the OpenText Fortify application security product suite.
ITWire: OpenText Partners with Secure Code Warrior to Deliver Comprehensive Application Security and Customised Developer Risk Management
The new agreement empowers development teams with continuous upskilling to turn security into a strategic advantage, reduce risks, and elevate customer trust.

Cyber Magazine: OpenText Partnership Targets Software Supply Chain Fears
OpenText partners with Secure Code Warrior to address rise in supply chain attacks through enhanced security training for coders and adoption of DevSecOps.
OpenText Partners with Secure Code Warrior to Deliver Comprehensive Application Security and Customized Developer Risk Management
The new agreement empowers development teams with continuous upskilling to turn security into a strategic advantage, reduce risks, and elevate customer trust.

[PODCAST] Information Week: Have We Gone Too Far With AI in Software Development?
Has the promise of improved efficiency through AI been realized in software development? Is there still a place for citizen developers with AI in the development cycle?
DevOps Digest: How Organizations Can Create Successful Secure-by-Design Programs
Our latest research paper, Benchmarking Security Skills: Streamlining Secure-by-Design in the Enterprise is the result of deep analysis of real Secure-by-Design initiatives at the enterprise level, and deriving the best practices for implementation based on data-driven findings.

Cybersecurity Insiders: Building a Security “Loyalty Program” for Software Developers is a Winning Formula in 2025
The software development industry could use something like a “frequent flyer status” system – especially when it comes to fostering a “security-first” mindset among developers. Without any incentive program, it’s nearly impossible for organisations and their developer teams to evaluate their security proficiency and compare their competencies alongside peers.

Authority Magazine: Matias Madou Of Secure Code Warrior On Embedding Security in Product Design and Development
CISOs need to lead a transition from the uncertainty of shadow AI to a more known, controlled and well-managed ‘Bring Your Own AI’ (BYOAI) environment. This will require full executive buy-in, careful implementation of AI into the existing tech stack and adoption of secure-by-design principles as part of a security-first culture that doesn’t slow down a product rollout.

Dynamic Business: New Cyber rules: Are experts pumped or pessimistic?
On November 25, 2024, the Australian Parliament passed significant reforms to bolster the nation’s cyber security posture, forming part of a strategic effort to position Australia as a global leader in cyber security by 2030.
Cyber Daily: Industry responds to passing of Australia’s Cyber Security Act
Opinions are mixed on the nation’s new cyber security legislation, which has been deployed as part of the 2023–2030 Australian Cyber Security Strategy.
Forbes: Strategic Secure-By-Design Initiatives: Best Practices For Meaningful Outcomes
It is possible to realize a meaningful secure-by-design initiative and lead the charge in transforming the current status quo around security culture. Let’s discuss the challenges ahead and techniques to overcome them in enterprise security and development teams.
KBI Media: Overcoming Common Security Vulnerabilities In The Banking Sector
While the physical security measures in place within many banks today are impressive – large vaults, bullet-proof glass, silent holdup alarms – it can be a very different story when it comes to cybersecurity.
DevOps Digest: Exploring the Power of AI in Software Development
DEVOPSdigest invited experts across the industry — consultants, analysts and vendors — to comment on how AI can support the software development life cycle (SDLC). Part 3 of this series covers advantages gained by leveraging AI tools in software development.
SecurityWeek: How to Improve the Security of AI-Assisted Software Development
CISOs need an AI visibility and KPI plan that supports a “just right” balance to enable optimal security and productivity outcomes.
DevOps.com: 6 Essential Components of a Successful Security ‘Rewards Program’ for Software Developers
Whether teams opt for on-the-job collaborative training opportunities or interactive, agile learning sessions, they would substantially benefit from standardized developer benchmarking for success. Such benchmarking could lead to a ‘trust score’ that, much like rewards programs, would provide incentives to developers for their security achievements and offer clear pathways for improvement.

SecurityInfoWatch: Critical infrastructure industries making progress on Secure-by-Design developer readiness
Secure Code Warrior's analysis highlights the critical need for developer upskilling to properly measure Secure-by-Design progress.

ITWire: Secure Code Warrior Research: Critical Infrastructure Industries Making Progress on Secure-by-Design Developer Readiness
New analysis collaborated on with Paladin Global Institute highlights the critical need for developer upskilling to properly measure Secure-by-Design progress
Secure Code Warrior Research: Critical Infrastructure Industries Making Progress on Secure-by-Design Developer Readiness
New analysis collaborated on with Paladin Global Institute highlights the critical need for developer upskilling to properly measure Secure-by-Design progress.

Politico: Cyber is getting schooled
Less than 4 percent of developers globally are involved in Secure-by-Design upskilling initiatives, according to new research out this morning by Secure Code Warrior.

NextGov: Few software developers employ secure by design training, research finds
The analysis, conducted by Secure Code Warrior, is supported by former White House cybersecurity officials Kemba Walden and Chris Inglis.

Cyberscoop: Organizations can substantially lower vulnerabilities with secure-by-design practices, report finds
Ex-National Cyber Director Inglis says “quantitative data” in Secure Code Warrior’s report shows the importance of the cybersecurity practice.