

Insights from experts shaping secure development
Access expert content on secure coding, AI governance, and software risk management.

SDLC 中的 AI:去伪存真与安全现实
与 KnowBe4 联合呈现的 SDLC 中的 AI:Kawin Boonyapredeeto (KnowBe4 CISO 顾问) 和 Pieter Danhieux (SCW CEO) 剖析 AI 代码安全风险。
2026 年德国 OWASP 日
Secure Code Warrior 正在赞助 2026 年德国 OWASP 日,汇聚 AppSec 从业人员共同探讨安全开发、运营和测试的最佳实践。
阿德莱德SEC (AdelaideSEC)
Secure Code Warrior 正在 AdelaideSEC 举办安全编码锦标赛。开发人员和安全专业人员将通过实操比赛识别并修复漏洞。
Black Hat USA 26
Secure Code Warrior 正参展 2026 年拉斯维加斯 Black Hat USA。CEO Pieter Danhieux、CCO Fatemah Beydoun 和 CPTO Alex Bullen 将在现场——欢迎预约会面!
FS-ISAC APAC 峰会
迫不及待赞助 2026 年 7 月 14 日至 15 日在新加坡举行的 FS-ISAC APAC 峰会!欢迎光临 #8 展位,并于 7 月 14 日下午 1:15 聆听 Pieter Danhieux 揭示 AI 编码模型与 10,000 名人类开发人员对比的研究。
Gartner 2026 年安全与风险管理峰会
很高兴赞助 2026 年 9 月 22 日至 24 日在伦敦举行的 Gartner 安全与风险管理峰会!欢迎与我们的团队建立联系,了解 Secure Code Warrior 如何帮助企业治理 AI 生成的代码。

OWASP 全球 AppSec 美国
很荣幸成为 OWASP Global AppSec USA 2026 的银牌赞助商,该大会将于 2026 年 11 月 5 日至 6 日在旧金山凯悦酒店迎来 25 周年!与 800+ 专业人士一起参加研讨会和 CTF 竞赛!

开发人员驱动安全的未来:集成 Checkmarx SAST 和 SCW
这种集成缩小了漏洞检测和修复之间的差距,为开发人员在需要时提供确切的学习资源。通过将强大的静态分析与敏捷实操学习相结合,企业可以更有效地左移。

DevSecOps 在软件开发中的关键作用
SCW Coffee Shop @RSAC24 呈现:加入 DevSecOps 思想领袖和行业专家小组,深入探讨 DevSecOps 在塑造当今和未来软件开发中的关键作用。
从影子 AI 到 AI 软件治理:重获对代码库的可见性
加入 Secure Code Warrior CTO Matias Madou 和产品总监 Tamim Noorzad,了解 AI 软件治理如何提供大规模管理 AI 辅助开发所需的可见性和洞察力。

OWASP 全球 AppSec 欧洲
迫不及待地想赞助 OWASP Global AppSec EU 大会,该大会将于 2026 年 6 月 22 日至 26 日在维也纳奥地利中心迎来其 25 周年纪念。欢迎光临我们的展位!

OWASP BASC
我们很高兴赞助 4 月 11 日在马萨诸塞州波士顿举行的 OWASP BASC。这是汇聚安全专业人士、开发人员和研究人员的首屈一指的应用安全大会。

OT 马德里峰会
加入我们的 OpenText Summit Madrid 2026 线下活动,旨在展示 AI、云和安全信息管理如何赋能新一代智能企业。
网络安全峰会
网络安全峰会于 4 月 28 日和 29 日举行,汇集了顶尖专家、创新者和参展商,展示最新趋势和最佳实践。不要错过参观我们展位的位置!
开发人员安全精通:通过集成 AST 和开发人员技能提升加速漏洞修复
停止仅仅寻找漏洞,开始彻底修复漏洞。检测到 Bug 只是成功的一半。要实现真正的 Secure by Design,安全见解必须转化为快速有效的修复。加入专家讨论。

充满自信地左移:让安全原生融入开发人员工作流
我们汇集了来自 SCW 和 Checkmarx 的行业专家,分享将安全无缝集成到您的开发流程中的最佳实践和策略。
产品安全虚拟峰会
Secure Code Warrior 荣幸与 Cycode 合作举办今年的产品安全虚拟峰会。我们将深入探讨 AI 时代安全软件的未来,展示如何将安全警报转化为开发人员的超能力。

网络钓鱼嘉年华 (Phishapalooza)
SCW 很荣幸能参加第 18 届 Phishapalooza 年会,以支持美国癌症协会。我们期待与当地网络安全社区联系,在双城开展冰钓和筹款活动。
OWASP LASCON
我们很荣幸成为德克萨斯州奥斯汀 OWASP LASCON 2026 的金牌赞助商!与 400 多名 Web 开发人员和安全专业人员一起分享应用安全的切削前沿思想。

纽约安全编码对决
SCW、OWASP 和 AWS 邀请您参加 2026 年 2 月 19 日星期四举行的纽约安全编码对决。在您选择的主要语言中挑战识别和修复漏洞!

黄金海岸 BSides
我们很高兴在 BSides Goldie 举办安全编码锦标赛!加入我们在澳大利亚黄金海岸举办的实操比赛,测试您识别和修复真实漏洞的能力。
BSides 法兰克福
我们很高兴在 BSides 法兰克福举办安全编码锦标赛!加入我们在法兰克福歌德大学校园举行的实操比赛。
RSA 大会
我们正前往旧金山参加 RSA Conference 2026。我们帮助企业赋予开发人员从一开始就编写安全代码的技能。欢迎访问我们在 South Expo Hall 的 #250 展位!

FS-ISAC FinCyber Today 加拿大
我们准备在 FS-ISAC FinCyber Today 加拿大峰会上讨论开发人员风险管理。我们通过赋予开发人员安全代码学习能力来帮助金融机构缓解应用风险。
Threat Modelling with AI: Turning Every Developer into a Threat Modeler
Threat modeling with AI: how to turn every developer into a threat modeler, straight from their IDE.

寻找您的开发人员
课程与入职培训经理 Katelynd Trinidad 介绍了定位组织内代码贡献者的不同方法,以确保他们接受安全代码培训。

品牌在 AppSec DevSec DevSecOps 中的力量(首字母缩写词代表什么!?)
在 AppSec 中,持久的计划影响力需要的不仅仅是技术——它需要一个强大的品牌。强大的身份确保您的举措能够产生共鸣并推动开发人员社区内的持续参与。

Vibe Coding:针对 AI 时代更新 AppSec 策略的实用指南
按需观看,了解如何通过实用的培训优先方法,使 AppSec 管理员成为 AI 推动者而非阻碍者。我们将展示如何利用 Secure Code Warrior (SCW) 在 AI 编码助手时代战略性地更新您的 AppSec 策略。

CISO 通过敏捷学习管理开发人员风险的指南
在 ESG 最近的一项研究中,54% 的受访者表示他们将带有已知漏洞的代码发布到生产环境中。由于现代软件生态系统中存在如此多的漏洞,您的安全代码学习计划是否降低了风险?

Secure Code Warrior 与 GuidePoint Security
Come visit our booth #336 at SecTor 2025 in Toronto at the Metro Toronto Convention Centre! Us along with other security professionals will be sharing our latest research and techniques on underground threats and corporate defenses.

OWASP 新西兰日
我们很高兴能在奥克兰大学校园参加 OWASP 新西兰日!该会议旨在通过关注强健的架构和开发技术来帮助开发人员构建更安全的应用。

OWASP 全球 AppSec 2025 美国
欢迎来到我们在华盛顿特区市中心万豪侯爵酒店的展区!您将有机会与我们以及 800 多位热爱安全的专家建立联系。

OWASP 荷比卢日
欢迎访问我们在比利时梅赫伦举行的 OWASP BeNeLux Days 展位!本次活动为您带来来自安全、DevOps 和云专家的技术演讲以及实操培训。
墨尔本 AppSec & DevSecOps 峰会
准备好在墨尔本 AppSec & DevSecOps 峰会上度过充满见解和社交的一天!我们迫不及待地想与您这样的安全和开发领导者联系。
FS-ISAC 秋季峰会
欢迎于 10 月 7 日星期二上午 8:00 访问我们在 FS-ISAC 秋季美洲峰会上的早餐会,探讨原生安全策略和以开发人员为中心的风险管理。

CISO Inspired 美国峰会
加入我们在 2025 年纽约 CISO Inspired 峰会!这是您与网络安全领导者建立联系、深入探讨主动防御策略的机会。

CISO Inspired 英国峰会
今年 11 月,加入我们的 2025 年 CISO Inspired 英国峰会!与网络安全领导者联系,应对上升的威胁并建立强大的防御策略。

BSides 伯恩茅斯
BSides Bournemouth 是一个社区驱动的网络安全会议。欢迎加入我们和其他优秀赞助商,共度充实的一天。

Black Hat USA
在拉斯维加斯 Mandalay Bay 举行的 Black Hat USA 上加入我们的高管团队!他们非常高兴能讨论 AI/LLM 安全代码风险!

OWASP 全球 AppSec 欧洲 2025
访问我们在 OWASP Global AppSec EU 的 #G08 展位,了解原生安全原则和有效的开发人员风险管理如何塑造下一代网络安全。
FS-ISAC EMEA 峰会
欢迎于 5 月 21 日上午 8:00 访问我们在 FS-ISAC EMEA 峰会上的早餐会,探讨原生安全 (secure by design) 策略和以开发人员为中心的风险管理如何变革网络安全。
网络安全峰会,汉堡
我们很高兴在网络安全峰会上与决策者和创新者建立联系,探讨主动安全编码如何在提升安全姿态的同时加速软件开发。

OpenText 马德里峰会
Secure Code Warrior 荣幸赞助 4 月 10 日举行的 OpenText Summit Madrid 2025!这一专属活动汇集了各界领导者,探索云、安全和 AI 如何改变信息管理。
澳大利亚网络网络交流会 (ACE25)
4月3日,我们的首席执行官 Pieter Danhieux 将在首届澳大利亚网络交流会 ACE25 上发表演讲,联合政府、私营部门和学术界以加强澳大利亚的网络能力。

安全左移:DevSecOps 在软件开发中的关键作用
在本次研讨会中,我们将深入探讨 DevSecOps 的至关重要性以及在软件开发生命周期早期集成安全的策略。随着网络威胁日益复杂,安全左移是必由之路。

OWASP SnowFROC
加入丹佛首屈一指的应用安全大会 SnowFROC '25!这项为期一天的活动吸引了约 400 名参会者,包含实操培训和出色的网络交流机会。

BSides 林堡
Secure Code Warrior 将于今年 3 月 14 日在 BSides 林堡举办一场锦标赛!深入讨论、实操演示并展开协作。
2025 年第二届 OWASP 缅因州安全编码锦标赛
OWASP 缅因州与 Secure Code Warrior 合作举办第二届 OWASP 缅因州安全编码锦标赛!这是一次线下聚会,我们欢迎从初级到资深的所有软件开发人员和 AppSec 专业人员。带上您的笔记本电脑,与同行一较高下!

NDC Security 2025
在奥斯陆市中心深入研究前沿主题、实操工作坊并与同行建立联系。访问我们的 H 展位,了解我们如何助力开发人员提升代码安全!

RSA 大会 2025
欢迎光临 RSAC 2025 的 #2353 展位,探索创新解决方案并参与塑造网络安全未来的对话。

DevSecOps360 伦敦
欢迎参加 2025 年 1 月 22 日星期三在 IBM Innovation Studio 伦敦举行的活动,展示我们在合作伙伴生态系统中针对 DevSecOps 的最新集成愿景。

Black Hat Europe
在伦敦 ExCeL 举行的 Black Hat Europe 上加入我们

OWASP 荷比卢
SCW 很荣幸赞助今年的大会。欢迎光临我们的展位,了解 SCW 如何帮助欧洲各地的公司掌握 OWASP Top 10 并降低安全风险。

2024 年德国 OWASP 日
在德国莱比锡加入 Secure Code Warrior,获取来自 OWASP 的深刻洞察、对 2025 年软件安全方向的展望以及有趣的社交活动。

DevSecOps 360 多伦多
加入 SCW、IBM、Black Duck、Iruis Risk 和 Contrast,了解您的组织如何在减少漏洞的同时加速开发,为业务和安全团队带来明确的收益。

巴黎云与网络安全博览会
Secure Code Warrior 非常高兴能成为法国首屈一指的网络安全活动的银牌赞助商。期待与您相见。

OpenText World 2024
加入 Secure Code Warrior 和 OpenText,了解世界各地的公司如何利用 SAST 结果为安全编码创造敏捷的学习体验。
DevSecOps 360 伦敦
加入 SCW、IBM、BlackDuck 和 IriusRisk,参加一场富有见地的活动,展示我们最新的集成,并了解企业如何为其组织实现真正的业务和生产力提升。

AppSecDay 斯德哥尔摩
加入 Secure Code Warrior、OpenText 和 Sonatype,共同讨论应对开源、遵循 NIS2 法规、AI 与 DevSecOps
DevSecOps 360 米兰
与我们一起展示自动化如何推动更快、更安全的开发。与我们的合作伙伴 IBM、Synopsys 和 IriusRisk 一起,我们将深入探讨减少漏洞的实用解决方案。

慈善职业-业余混合配对赛 (Charity Pro-Am Scramble)
加入 Secure Code Warrior 和我们的合作伙伴 Arctiq,参加在 Golf Le Diable 举行的慈善配对赛。我们将为了慈善事业挥杆,支持 KidSport Québec。
AppSec Day 乌得勒支
随着应用安全的发展,各组织正在越来越多地集成 AI 解决方案,以实现实时威胁检测和预防。加入 Secure Code Warrior 和我们的合作伙伴!

Secure Code Warrior 用户组 EMEA
欢迎来到 SCW 用户组,这是一个与其他 SCW 管理员和用户建立联系的社区,以详细了解他们如何管理开发人员驱动的安全计划。学习使用平台的技巧和诀窍!

SANS Secure 日本 2025
SANS 将于 2 月 17 日至 22 日来到日本东京。我们很高兴在这个顶尖培训活动中与来自世界各地的网络安全专业人士建立联系。顺道拜访我们的展位吧!

OWASP 2024 全球 AppSec
Global AppSec US 大会充满了新趋势和热点话题。欢迎光临我们在旧金山的展位,观看我们最新产品阵容的演示。

DevSecOps 转型
DevSecOps 能够在开发生命周期早期识别安全问题——直接呈现给能够产生最大影响的开发人员。

网络安全峰会
来自中大型企业的顶尖专家将与商业网络安全数字解决方案的创新供应商会面。从我们舞台上的专家那里学习,并在展区与领先的供应商会面。

Blackhat USA
Black Hat USA 迎来第 27 个年头,重返拉斯维加斯 Mandalay Bay 会展中心。主会议将包含 100 多场精选简报会和数十个开源工具演示。

AppSec & DevSecOps 峰会
在 2024 年墨尔本 AppSec 和 DevSecOps 峰会上梳理、团结并提升您的安全策略。提高您的安全技能,站在应用和云安全革命的最前沿。

使用 SCW Trust Score 评估您安全计划的当前状态
在当今快速演变的安全局势中,了解安全计划所处的位置至关重要。与 Secure Code Warrior 联合创始人兼 CTO Matias Madou 一起讨论 SCW Trust Score。

北欧 IT 安全大会
Nordic IT Security 是斯堪的纳维亚半岛最负盛名的网络安全峰会,17 年来一直是指导北欧网络安全导航的“方向盘”。

比利时咖啡时光
对于来自比利时的 RSAC 与会者,我们将在3月7日星期二下午3:00举办特别的“一日之末咖啡”活动。与 CEO Pieter Danhieux 和 CTO Matias Madou 一起品尝咖啡。

2026 年的安全倡导者:提升、参与和保护
无论您是想启动新计划、扩展现有计划,还是只是想探索该计划的工作原理;本次研讨会旨在为具有影响力的安全倡导者计划提供可操作的见解。

SANS 网络安全 2026
9 月 10 日至 15 日在拉斯维加斯加入我们的 SANS Network Security 2026。活动汇集网络安全专业人士,进行深入的实操培训与互动。

RSA 大会 2024
可能性的艺术就在这里!欢迎光临 5179 展位,了解如何将漏洞减少 53%

在 RSAC24 与 SCW 领导层会面
我们的联合创始人及高管将于 5 月 6 日至 7 日在 Bluestone Lane 联合广场咖啡馆品尝旧金山最好的咖啡并开展会谈。

我们信任开发人员和 AI
SCW Coffee Shop @RSAC24 呈现:联合创始人兼 CTO Matias Madou 与行业专家一起探讨评估开发人员群体内安全技能的挑战与策略。

如何使用 SCW Trust Score 量化安全编码计划的有效性
SCW Coffee Shop @RSAC24 呈现:加入 CTPO Patrick Collins 和 CMO Junie Dinda,深入了解全新的 SCW Trust Score。

Carolina Hurricanes 与 GuidePoint
加入我们和 GuidePoint 的合作伙伴,在冰球场观赏精彩的比赛并交流 AppSec!

湾区厂商欢乐时光
更多信息即将推出。

安全领域的技术女性领导者
SCW Coffee Shop @RSAC24 呈现:联合创始人兼 CCO Fatemah Beydoun 与行业女性领导者小组一起讨论如何左移以纠正安全领域的性别差距。由我们自己的 Channel Partners 副总裁 Holly Whalen 主持。
使用生成式 AI 进行编码的好处、坏处与隐患
在本次研讨会中,Secure Code Warrior CTO 兼联合创始人 Matias Madou 与安全研究员 Jon Helton 强强联手,揭示生成式 AI 的能力,同时去伪存真。
丰业银行体育馆私人包厢
在丰业银行体育馆的私人包厢中加入 Secure Code Warrior 和 GuidePoint!在专属环境中观看比赛的同时与同行交流,讨论应用安全的最新动态。
应用安全实操工作坊
与 AWS、Contrast Security 和 Arctiq 合作,为您带来互动式 AppSec 实操工作坊

线上品酒会 - 俄亥俄州
加入我们、GuidePoint 和其他合作伙伴,参加 Silver Oaks 酒庄线上品酒会。
DevSecOps 360 - 利雅得
与 IBM、Synopsys 和 IriusRisk 合作,我们将分享合作伙伴生态系统内 DevSecOps 的最新集成愿景
DevSecOps 360 - 慕尼黑
与 IBM、Synopsys 和 IriusRisk 合作,我们将分享合作伙伴生态系统内 DevSecOps 的最新集成愿景
DevSecOps 360 - 迪拜
与 IBM、Synopsys 和 IriusRisk 合作,我们将分享合作伙伴生态系统内 DevSecOps 的最新集成愿景
Shift-Left 测试
早期发现漏洞并加速修复。SCW、Cyberark 和 Checkmarx 合作打造一致的左移安全方法。
保障下一代安全:正面解决 AI 编码漏洞
人工智能的出现改变了软件开发的格局,带来了前所未有的效率。然而,这也带来了挑战,尤其是在应用安全领域。AI 不仅编写代码,它还编写存在漏洞的代码。
人工智能时代的安全编码
随着 AI 加速代码生成,保持强大的安全性比以往任何时候都更加重要。观看我们的独家炉边谈话,探索 AI 驱动开发的敏捷性与安全编码的必要性之间的微妙平衡。
Secure Code Warrior 用户组 NA
欢迎来到 SCW 用户组,这是一个与其他 SCW 管理员和用户建立联系的社区,以详细了解他们如何管理开发人员驱动的安全计划。学习使用平台的技巧和诀窍!
Secure Code Warrior 用户组
欢迎来到 Secure Code Warrior 用户组!本节包含产品更新、鼓舞人心的客户成功故事和互动面板讨论。了解同行如何克服应用安全挑战。
SANS 云安全培训
SANS 云安全培训将于 4 月 13 日至 18 日在弗吉尼亚州亚历山德里亚举行。本次活动汇集了顶尖的网络安全专业人员,进行密集的实战培训。请务必光临我们的展位!
加入我们的 DEVOPS 大会
欢迎在今年 3 月 8 日至 9 日加入我们的 DEVOPS 大会,聆听见解深刻的演讲并有机会参加安全编码锦标赛。立即获取免费门票!
安全是开发人员的问题吗?
技术爆发式增长,一切都需要被保障安全。然而,在技术快速增长和网络威胁演变的时代,安全团队没有足够的人力覆盖所有方面。
通过全方位的开发人员驱动安全提高软件发布速度
AWS + Secure Code Warrior 论提升开发人员代码输出数量和质量的重要性。

通过全方位的开发人员驱动安全提高软件发布速度
随着可利用软件漏洞引发的安全泄露事件上升,企业必须寻求最大程度减少漏洞并提高软件发布速度的方法。
如何缩小开源合规中的规避与修复差距。
缩小这一差距对于帮助工程团队及其领导者更好地了解开源软件对组织交付无风险解决方案能力的影响至关重要。

如何构建具有坚实基础的 AppSec 计划
在制定 AppSec 计划策略时,设定基线的重要性及关键方法。
推动者 8:打造您的项目品牌
安全编码项目若想取得成功,仅有优质内容是不够的。赋能要素 8 将展示如何通过品牌塑造,将参与过程转化为一种令人向往且具有身份象征的体验。
每一位员工现在都站在 AI 网络安全的最前线
企业技术格局正以一种鲜有人预料到的速度发生剧变。我们已正式跨越了从人工编写代码和基础辅助编程,迈向“智能体开发生命周期”(ADLC)的时代。虽然自主 AI 智能体在多项职能中展现出前所未有的效率,但也带来了全新的安全与合规风险。
赋能 7:开发者表彰
认可激发参与。赋能要素 7 旨在通过奖励和专属礼品大张旗鼓地庆祝开发者的成就,以此彰显真正且来之不易的安全编码成果。

入选 2026 年 Gartner® 应用安全技术成熟度曲线™ (Hype Cycle™)
Secure Code Warrior 入选 2026 年 Gartner® 应用安全技术成熟度曲线(Hype Cycle™),涵盖“代理式编码安全”与“安全编码培训”类别。原因如下。

您是否是一位担心 LLM 代码生成安全性和成本的 CISO 或工程负责人?
在全面采用某款 AI 模型之前,请先查阅我们专有的 LLM 基准测试数据——SCW AI 信任指数。

赋能要素 6:定期向领导层汇报
高管支持并非一劳永逸。第 6 项赋能要素将展示如何通过定期汇报,让领导层持续关注、了解并投入到项目的成功中。

AI 软件治理的未来建立在稳固的合作伙伴关系之上
了解 Secure Code Warrior 为何转型为渠道优先型公司,以及值得信赖的合作伙伴如何帮助企业安全、大规模地采用 AI 软件治理。

Secure Code Warrior 推出的 Citizen AI:打造具备 AI 竞争力的员工队伍
Secure Code Warrior 专为非开发人员打造的 AI 素养计划。

为什么大多数 CISO 在采用 AI 时如盲人摸象(以及如何摘下眼罩)
Secure Code Warrior 今日发布了一份全新的白皮书,其中涵盖了一种指导性的 AI 采用模型。安全领导者可以利用该模型识别自身所处的采用阶段,并切实有效地管控组织内部的 AI 安全风险。
赋能 5:认证计划
告别“一劳永逸”的培训模式。Enabler 5 可构建多级认证计划,为开发人员提供明确的进阶路径并验证其专业技能。
NSA 刚刚发布了首份 MCP 安全指南。这对开发者能力意味着什么?
NSA 发布了首份 MCP 安全指南。SCW 的课程体系已覆盖其中 23 个问题中的 18 个——以下是具体的映射情况。

入选 2026 年 Gartner® 安全软件工程技术成熟度曲线™ (Hype Cycle™)
Gartner 两度点名 SCW。随着 AI 智能体在开发工作中发挥越来越大的作用,SCW 为您提供安全采用 AI 驱动开发所需的各项能力与治理手段。

发布自适应学习:应对 AI 软件安全风险与技能差距的良方
Adaptive Learning 将 SCW Trust Agent 与我们的整个学习平台无缝连接,确保培训内容与开发者的实时工作保持高度同步。
契合真实 AI 使用场景的安全编码学习
将安全编码培训与实际的 AI 开发活动相结合——无需人工干预,即可自动为使用 AI 工具的开发人员分配指导。将安全编码培训与实际的 AI 开发活动相结合——无需人工干预,即可自动为使用 AI 工具的开发人员分配指导。
针对代码中的实际风险对开发者进行培训,无论是人工编写还是 AI 生成的代码
自适应学习会自动为引入实际漏洞的开发人员分配针对性的安全编码培训,从源头上降低重复风险。Secure Code Warrior 博客横幅,背景为一名开发人员在多显示器工作台前编写代码,上方覆盖蓝色图层,标题为“针对开发人员代码中的实际风险进行培训”。
赋能点 4:低门槛用户访问
通过“赋能要素 4:低门槛用户访问”消除安全编码计划中的阻力。探索 SSO、预置式入职引导和中继状态策略,让开发人员只需点击一下即可开始培训。

为生成式 AI 时代武装开发者:与 AWS 的合作
我非常自豪地宣布,Secure Code Warrior 已与亚马逊云科技(AWS)签署了战略合作协议。鉴于威胁形势的迅速演变,对于安全领导者和着眼未来的开发者而言,此次战略合作正当其时,意义重大。
保障软件的未来:SCW 与 KnowBe4 强强联手
我非常高兴地宣布,Secure Code Warrior 与 KnowBe4 即将达成战略合作伙伴关系。KnowBe4 是全球领先的综合性人力与智能体 AI 风险管理专家,是协助我们将基础安全意识推广至全球各地的理想合作伙伴。

后量子密码学:量子计算机将破解当今的加密技术——您准备好了吗?
后量子密码学(PQC)对于保护数据免受量子计算威胁至关重要。了解“先截获,后解密”策略如何带来风险,以及开发人员应如何为量子安全做好准备。

赋能要素 3:开发者沟通计划
利用强有力的沟通计划,让开发者持续参与您的安全编码项目。学习如何突出项目优势、把握沟通基调并庆祝取得的成果。
智能体时代提前到来:切勿措手不及
Anthropic 的 Claude Mythos 标志着每位安全领导者在规划安全项目时必须进行根本性的永久转变,尤其是在处理遗留系统的补丁管理方面。

Enabler 2: Senior Leadership Sponsorship
Explore Enabler 2: Senior Leadership Sponsorship. Learn why active buy-in from the CIO, CTO, and CISO is vital to drive developer adoption and program credibility.
Observe and Secure the ADLC: A Four-Point Framework for CISOs and Development Teams Using AI
While development teams look to make the most of GenAI’s undeniable benefits, we’d like to propose a four-point foundational framework that will allow security leaders to deploy AI coding tools and agents with a higher, more relevant standard of security best practices. It details exactly what enterprises can do to ensure safe, secure code development right now, and as agentic AI becomes an even bigger factor in the future.
Cybermon 回来了:打败老板 AI 任务现已按需提供
Cybermon 2025 打败老板现已在 SCW 中全年开幕。部落高级 AI/LLM 安全战,大规格模加强安全 AI 开发。
AI Can Write and Review Code — But Humans Still Own the Risk
Anthropic’s launch of Claude Code Security marks a defining collision point between AI-assisted software development, and the rapid augmentation of how we approach modern cybersecurity.
《网络弹性法》解读:通过设计软件开发实现安全意味着什么
了解《欧盟网络弹性法案》(CRA) 的要求、适用于谁以及工程团队如何通过设计实践、漏洞预防和开发人员能力建设做好准备。

推动因素 1:明确且可衡量的成功标准
Enabler 1 是我们由 10 部分组成的成功推动者系列的序幕,它展示了如何将安全编码与业务成果(例如降低风险和提高长期计划成熟度的速度)联系起来。
SCW Turns 11: A Realtime Lesson in Adaptability and Continuous Improvement
2025 was a big year for AI, for cybersecurity, and for SCW. I’m approaching 2026 with quiet confidence, and the optimism that only hard work paying off can bring.

Introducing the 10 Enablers of Success
Secure Code Warrior’s 10 Enablers guide organizations in building lasting secure coding programs by focusing on people, process, and program maturity stages.
OWASP 2025 年前 10 名:软件供应链故障
OWASP 2025 年前 10 名将软件供应链故障列为 #3。通过严格的 SBOM、依赖关系跟踪和 CI/CD 管道强化来缓解这种高影响风险。

New Risk Category on the OWASP Top Ten: Expecting the Unexpected
OWASP Top 10 2025 adds Mishandling of Exceptional Conditions at #10. Mitigate risks via "fail closed" logic, global error handlers, and strict input validation.
OWASP 前 10 名:2025 年 — 新增内容以及安全代码勇士如何帮助您保持一致
了解 OWASP Top 10:2025 中发生了哪些变化,以及 Secure Code Warrior 如何通过更新的任务、课程和开发者见解轻松过渡。
Adopt Agentic AI in Software Development FAST! (Spoiler: You Probably Shouldn't.)
Is the cybersecurity world moving too fast on agentic AI? The future of AI security is here, and it's time for experts to move from reflection to reality.

Solving the Visibility Crisis: How Trust Agent Bridges the Gap Between Learning and Code
Trust Agent by Secure Code Warrior solves the secure coding crisis, validating dev proficiency on every commit. It discovers all contributors & automates governance in your dev workflow.

在 AI 增强型安全软件开发中重拾批判性思维
人工智能的争论不在于使用,而是应用。了解如何依靠深入了解其代码的开发人员,在提高 AI 生产力的需求与强大的安全性之间取得平衡。
AI Coding Assistants: With Maximum Productivity Comes Amplified Risks
In our latest whitepaper, our co-founders Pieter Danhieux and Dr. Matias Madou, Ph.D., explore the double-edged sword that is AI Coding Assistants and how they can be a welcome addition and a significant security liability at the same time.


Why Cybersecurity Awareness Month Must Evolve in the Age of AI
CISOs can’t rely on the same old awareness playbook. In the Age of AI, they must embrace modern approaches to safeguard code, teams, and organizations.

SCW Trust Agent: AI - Visibility and Governance for Your AI-Assisted SDLC
Learn how Trust Agent: AI provides deep visibility and governance over AI-generated code, empowering organizations to innovate faster and more securely.

人工智能时代的安全编码:试试我们的全新交互式 AI 挑战
人工智能辅助编码正在改变开发。试试我们全新的 Copilot 风格的人工智能挑战赛,在现实的工作流程中安全地审查、分析和修复代码。

SCW 为开发人员推出免费 AI/LLM 安全视频系列
介绍我们为期 12 周的免费 AI/LLM 安全视频系列!了解人工智能辅助编码的基本风险以及如何构建更安全的应用程序。
AI/LLM Security Video Series: All Episodes, Updated Weekly
Your all-in-one guide to our 12-week AI/LLM security video series. Catch every episode, learn key AI security concepts, and follow along weekly.


10,000 多项安全代码学习活动:开发人员员工风险管理十年
庆祝 10,000 多场安全代码学习活动,以及十年来帮助开发人员降低低风险风险、提高高代码质量并自信地处理 AI 辅助 AI 辅助助开开发。
当好工具变坏时:AI 工具中毒,以及如何阻止你的 AI 充当双重间谍
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
制定标准:SCW 在 GitHub 上发布免费的 AI 编码安全规则
人工智能辅助开发已不在眼前——它就在这里,它正在迅速重塑软件的编写方式。GitHub Copilot、Cline、Roo、Cursor、Aider和Windsurf等工具正在将开发人员转变为自己的副驾驶,从而加快迭代速度,加速从原型设计到重大重构项目的所有工作。
Secure Code Warrior Unraveled: Impact of Secure Developers on Software Metrics
When reflecting on our own technology, SCW’s Developer Risk Management platform, I am buoyed by recent metrics from one of our core enterprise clients, and going down the proverbial rabbit hole into this data tells a tale of a high-adoption, potent Secure by Design initiative that has been proven to considerably reduce risk in their organization.

使用 Secure Code Warrior + HackerOne 闭环漏洞
Secure Code Warrior很高兴地宣布我们与进攻性安全解决方案领导者HackerOne进行了新的整合。我们正在共同建立一个强大的综合生态系统。HackerOne 查明了现实环境中漏洞实际发生的位置,暴露了安全问题的 “内容” 和 “在哪里”。

揭晓:网络行业如何通过设计定义安全
在我们最新的白皮书中,我们的联合创始人彼得·丹希厄和马蒂亚斯·马杜博士与包括首席信息安全官、AppSec领导人和安全专业人员在内的二十多位企业安全领导者进行了座谈,找出了这个难题的关键部分,并揭示了安全由设计运动背后的现实。这是安全团队的共同抱负,但没有共同的策略。

Vibe Coding 会把你的代码库变成兄弟会派对吗?
Vibe 编程就像大学兄弟会派对,而人工智能是所有庆祝活动的核心,小桶。放松身心,发挥创造力,看看你的想象力可以带你走向何方,这很有趣,但是在喝了几个小桶之后,适量饮酒(或者使用人工智能)无疑是更安全的长期解决方案。


捍卫者十年:安全代码勇士十岁了
Secure Code Warrior 的创始团队一直团结在一起,在整整十年中指导飞船度过每一次教训、胜利和挫折。作为开发者风险管理领域的领导者,我们正在扩大规模,准备迎接我们的下一个篇章——SCW 2.0。
十大关键预测:2025年安全代码勇士对人工智能的影响以及安全设计的影响
组织在使用人工智能来支持长期生产力、可持续性和安全投资回报率方面面临着艰难的决定。在过去的几年中,我们很清楚,人工智能永远不会完全取代开发者的角色。从 AI + 开发人员合作伙伴关系到围绕 Secure-by-Design 期望的日益增加的压力(和困惑),让我们仔细看看明年的预期。
OWASP LLM 应用程序前 10 名:新增内容、变化以及如何保持安全
利用最新的 OWASP 十大更新,在保护 LLM 应用程序方面保持领先地位。了解新增内容、变化以及 Secure Code Warrior 如何为您提供最新的学习资源,以降低生成式 AI 中的风险。

信使评分演示了安全设计提示升技能 “计划” 的价钱值
我们的研究表明,安全代码培训是有效的。Trust Score使用了一种算法,该算法利利用了来自600多个组织的25万多名学者从工作中获得的超额超过2000万个学习数据点,展示了其在低速降低漏洞的有效性以及如何使该计划更有效。

Reactive Versus Preventive Security: Prevention Is a Better Cure
The idea of bringing preventive security to legacy code and systems at the same time as newer applications can seem daunting, but a Secure-by-Design approach, enforced by upskilling developers, can apply security best practices to those systems. It’s the best chance many organizations have of improving their security postures.

对开发人员进行安全技能基准测试的好处
人们越来越关注安全代码和安全设计原则,这要求开发人员从SDLC一开始就接受网络安全培训,Secure Code Warrior的信任评分等工具可以帮助衡量和改善他们的进度。

You’ve got a friend in me: How AI coding tools and security-aware developers can work together safely
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
推动企业安全设计计划取得有意义的成功
我们最新的研究论文《基准安全技能:简化企业中的安全设计》是对企业层面真正的安全设计计划进行深入分析的结果,并根据数据驱动的发现得出最佳实践方法。
深度探索:探索 GNU-Linux 系统中的关键 CUPS 漏洞
在我们探索通用 UNIX 打印系统 (CUPS) 中最近出现的高严重性漏洞时,了解 Linux 用户面临的最新安全挑战。了解这些问题如何可能导致潜在的远程代码执行 (RCE),以及您可以采取哪些措施来保护系统。
How exceptional CISOs are igniting the security fire in their development team
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
程序员服装安全:分享与学习-跨站点脚本 (XSS)
跨站脚本 (XSS) 利用 BROWSER 的信使和用户的无知来取走数据、接管帐户和破坏者网站;这个漏洞很快,会变得非常快。让我们来看看 XSS 是如何工作的,可以造成什么伤害以及如何防止。

介绍我们的新参与度洞察报告
了解我们新的参与度洞察报告,该报告提供了深入的分析,可帮助您衡量安全代码学习成果。
How the best CISOs leverage people and technology to become true superstars
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

DigitalOcean 如何减少软件安全债务并突破生产力界限
Secure Code Warrior从一开始就帮助DigitalOcean构建和发布高质量的代码,与具有安全意识的开发人员一起推动数字创新和现代化。

Women in Security are Winning: How the AWSN is Setting Up a New Generation of Security Superwomen
Secure-by-Design is the latest initiative on everyone’s lips, and the Australian government, collaborating with CISA at the highest levels of global governance, is guiding a higher standard of software quality and security from vendors.

SCW Trust Agent-可视性和控制力以扩展开发人员驱动的安全性
由 Secure Code Warrior 推出的 SCW Trust Agent 为安全领导者提供了在组织内扩展开发人员驱动的安全性所需的可见性和控制力。通过连接到代码存储库,它可以评估代码提交元数据,检查开发人员、使用的编程语言和交付时间戳,以确定开发人员的安全知识。

你的安全计划是 CISA 的网络安全战略计划做好准备了吗?
网络安全战略计划推出了大多数人组织网络安全方程式的重量大变化,开发人处的工作人员帮助实现了这些新目标的独家地位。
Don’t ignore what developers need for a successful software security journey
It's becoming apparent that while cybersecurity platforms and defenses are critical components in defense against modern attacks, what is truly needed is secure code that can be deployed free from vulnerabilities. And that requires security-aware developers with verified security skills.
Engage & Empower:重点介绍开发者参与的关键功能
全面了解我们的敏捷学习方法、Microsoft 团队集成以及我们的开发参与报告。
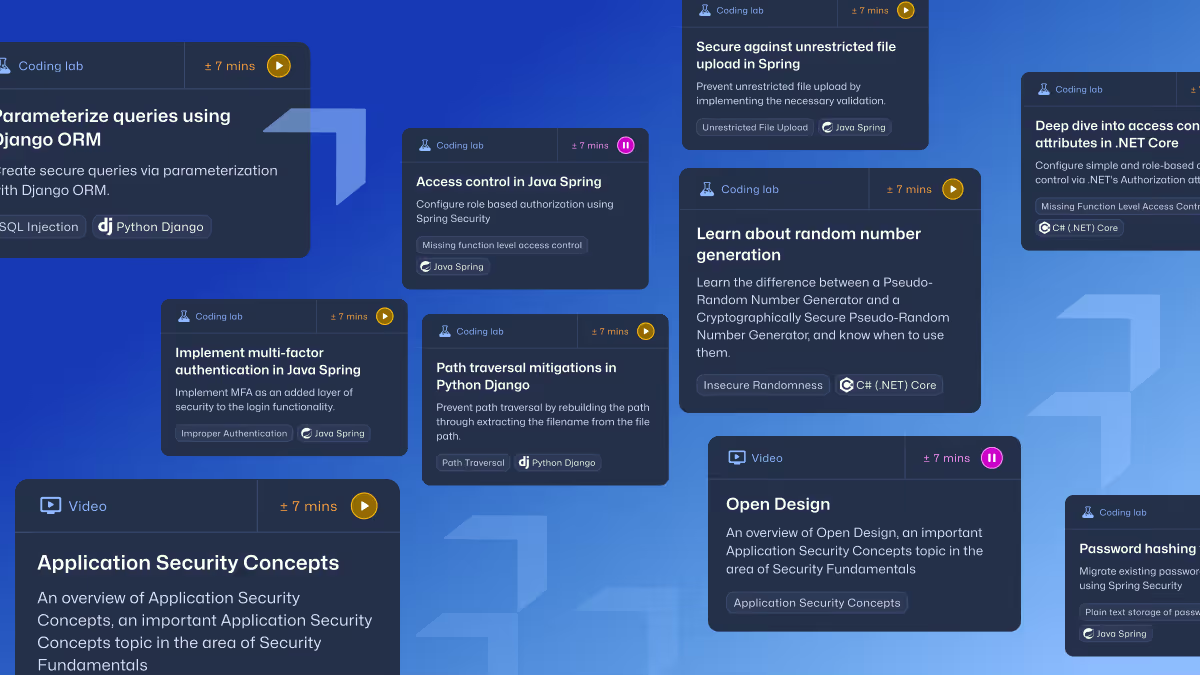
赋予开发者权力:按需学习内容的重要性
使用安全代码勇士为您的开发人员提供支持。我们的平台为开发人员提供按需学习内容并赋予其权力。
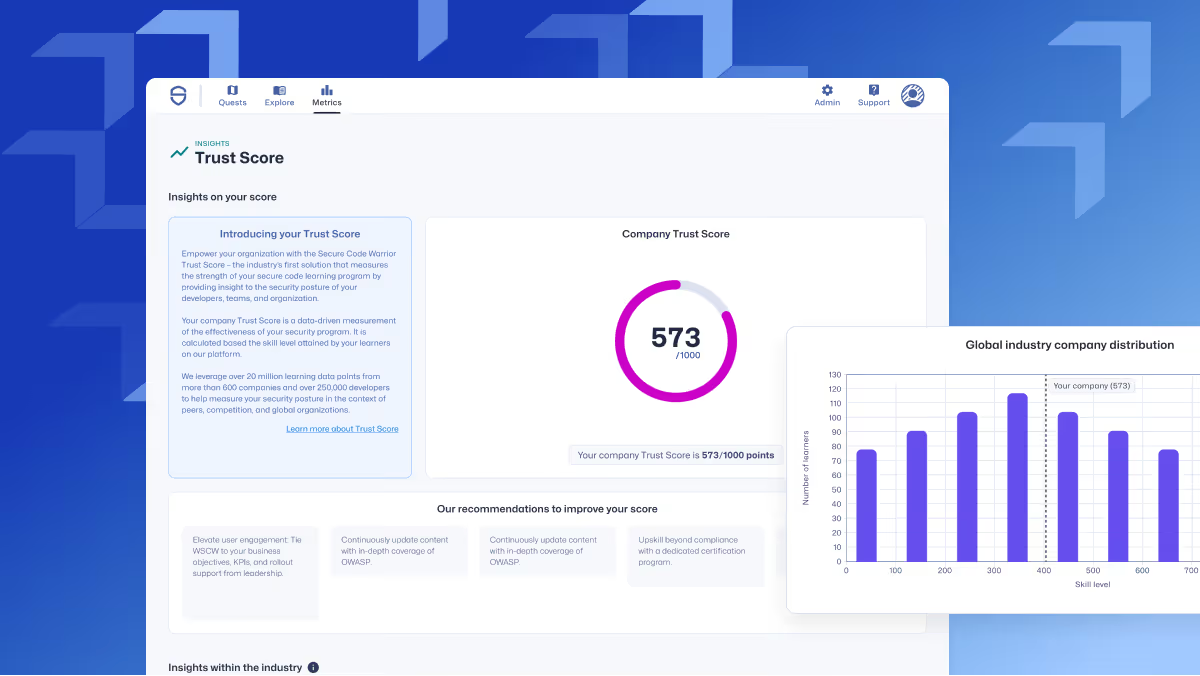

FinServ 合规性取决于软件安全性
管理金融服务行业的法规,例如PCI DSS,强调了安全代码的重要性以及对开发人员进行安全最佳实践培训的必要性。
Linux 中的 XZ Utils 后门程序指出了更广泛的供应链安全问题,要将其阻止,我们需要的不仅仅是社区精神
在主要 Linux 发行版使用的 XZ Utils 数据压缩库中发现了一个名为 CVE-2024-3094 的严重漏洞,该漏洞是由威胁行为者通过后门程序引入的。这种高严重性问题允许潜在的远程代码执行,对软件构建过程构成重大风险。该漏洞影响了Fedora Rawhide中XZ Utils的早期版本(5.6.0和5.6.1),并紧急呼吁各组织实施补丁。该事件凸显了社区志愿者在维护开源软件方面的关键作用,并凸显了在软件开发生命周期内加强安全措施和访问控制的必要性。
收获人工智能创新的好处取决于从安全代码开始
生成式人工智能为金融服务公司提供了很多优势,但也带来了很多潜在风险。培训开发人员掌握安全最佳实践并将其与 AI 模型配对,有助于从一开始就创建安全代码。

利用 AI 和主动措施有效管理漏洞警报
Secure Code Warrior和Mend.io讨论了人工智能对安全性的影响、主动安全方法以及漏洞警报的有效管理。
将 “边做边学” 提升到一个新的水平——查看我们与 Apiiro 的新集成
了解 Secure Code Warrior 与 Apiiro 的最新集成。
浏览安全编码蓝图:构造类比
通过遵循安全编码惯例,开发人员可以帮助保护其应用程序免受攻击者利用的漏洞的侵害。正如精心建造的房屋不太可能倒塌一样,编码良好的应用程序也不太可能被黑客入侵。

有了适当的支持,开发人员可以引导您的组织实现卓越的 PCI DSS 4.0 合规性
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
LLMs:一种(im)完全人性化的安全编码方法?
尽管LLM式的人工智能技术似乎不可避免地会改变我们处理许多方面的工作方式,而不仅仅是软件开发,但我们必须退后一步,考虑头条新闻之外的风险。作为编程伙伴,它的缺陷可能是它最为 “人性化” 的属性。

九之力:在激动人心的网络安全时刻发展安全代码勇士的遗产
今天是我们的九岁生日,随着形势的持续快速变化,我对我们在网络安全领域取得的成就和持久的地位感到非常自豪和感激。


API-led data breaches are creating pandamonium for security teams. Why do we make it so easy for threat actors to exploit them?
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

2024 年预测:安全、人工智能、开发者留存率和未来之路
安全代码勇士对2024年及以后网络安全行业的十大预测。

Netskope 如何重新构想安全代码教育
SCW 案例研究博客,重点介绍了 Netskope 部署的敏捷学习环境。

深度探索:探索 AI 编程助手生成的漏洞
探索 AI 在软件开发中的安全风险,并学习如何使用 Secure Code Warrior 有效应对这些挑战。

加强开发人员安全教育并将漏洞减少 53% 的 3 个步骤
为开发人员提供分层方法,以减少漏洞、增进关系并对反复出现的问题进行优先排序。

Secure Code Warrior 2023: Innovations, achievements, and insights
Explore Secure Code Warrior’s 2023 journey to empower developers, enhance productivity, and mitigate risk in cybersecurity with recent innovations to our agile learning platform.
Attack of the Zombie APIs: Who is leading the security counteroffensive in your organization?
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
您是否高估了组织的安全成熟度?
由于持续的技能短缺与为满足世界软件需求而编写的大量代码背道而驰,许多企业的网络安全战略和现有基础设施都落在了后面。现在是我们诚实地审视我们的整体网络安全成熟度,并评估摆在我们面前的可行速赢的时候了。

重新思考开发者教育以增强安全性
安全领导者需要重新考虑开发人员从安全代码学习体验中获得的价值,以及如何使该计划更具吸引力,最重要的是,更具影响力。在本博客中,我们将探讨如何通过更多的实践学习和与工具的集成,让开发人员对安全代码教育感到兴奋,从而取得重大成果,并将引入的漏洞减少多达 53%。
通过敏捷学习将漏洞减少一半
通过 Secure Code Warrior 的动手敏捷安全培训,了解如何减少漏洞和安全漏洞。

深入研究:查找和修复高严重性的 libcurl/curl 漏洞
受影响的 curl 库版本容易受到基于堆的缓冲区溢出漏洞的影响,该漏洞与 SOCKS5 代理协议的传统问题有关。学习如何通过可玩的任务来查找和修复这种漏洞类型。
世界一流的首席信息安全官如何在 2023 年赢得更多预算和董事会信任
首席信息安全官发现自己处于越来越紧张的境地:保护更多资产,发布更多代码,减少更大的攻击面,并利用迅速减少的财务资源来做到这一点。网络安全被视为成本中心是不可避免的事实,尽管组织的安全计划阻碍了威胁行为者成为明天的灾难性头条,但安全领导者必须采取更多措施,用对执行机构来说合理的语言进行推销和证明该部门的整体商业价值。
深入探讨:近距离接触MoveIT未修补漏洞
MoveIT场景与许多开发人员和AppSec专业人员以前可能经历的场景略有不同,你可以在这里的实时模拟中测试你的SQLI-slaying技能。


荷兰商会:树立大规模开发人员主导安全的新标杆
荷兰商会(Kamer van Koophandel)分享了他们如何通过基于角色的认证、信任评分基准测试以及共享安全责任的文化,将安全编码融入日常开发工作。
勇夺金牌:Paysafe 安全代码标准再攀高峰
了解 Paysafe 如何通过与 Secure Code Warrior 的合作,将开发人员生产力提升 45%,并大幅减少代码漏洞。
DigitalOcean Decreases Security Debt with Secure Code Warrior
DigitalOcean's use of Secure Code Warrior training has significantly reduced security debt, allowing teams to focus more on innovation and productivity. The improved security has strengthened their product quality and competitive edge. Looking ahead, the SCW Trust Score will help them further enhance security practices and continue driving innovation.
Devlympics 2023:回顾
请通过本报告探索 2023 年 Devlympics 的比赛结果。深入了解各参赛行业的开发者参与度、技术栈与编程语言趋势,以及本次由 Secure Code Warrior 主办的年度全球赛事中所涵盖的关键漏洞与 CWE。

统一的安全文化:Sage 如何通过敏捷安全编码学习构建其安全倡导者计划
了解 Sage 如何通过灵活且以关系为导向的方法增强安全性,成功培养了 200 多名安全倡导者,并实现了可衡量的风险降低。

通往安全专家的路径:Workday 如何利用敏捷学习提升开发人员技能
了解 Workday 如何通过 Secure Code Warrior 的敏捷学习模式革新开发者培训。通过为开发者提供实操性的语言专属课程,Workday 在软件开发生命周期(SDLC)的早期阶段就有效降低了漏洞风险。查看他们的显著成果与核心经验,助力构建安全编码文化。
泰雷兹如何实现开发人员驱动的安全模式
在本案例研究中,了解泰雷兹(Thales)如何通过人员、流程和技术方法构建敏捷的安全代码学习计划,从而激励开发人员成为积极的安全倡导者。
高露洁棕榄如何提升开发人员安全技能并打造安全编码文化
了解零售巨头高露洁棕榄(Colgate-Palmolive)如何在数字化转型过程中重塑其应用安全。面对安全编码方面的挑战,他们通过将碎片化、情境化的学习融入开发人员的工作流程,实现了创新。
Security as culture: How Blue Prism cultivates world-class secure developers
Learn how Blue Prism, the global leader in intelligent automation for the enterprise, used Secure Code Warrior's agile learning platform to create a security-first culture with their developers, achieve their business goals, and ship secure code at speed

Supercharged Security Awareness: How Tournaments are Inspiring Developers at Erste Group
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
“代码游戏”如何引领 IAG 集团迈向更安全的编码未来
IAG 集团是亚太地区多家领先保险公司的幕后推手,每年为数百万客户承保的保费总额约达 114 亿澳元。

Driving Actionable Awareness: FINRA's Push For Super-Secure Developers
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

打造革命性的安全认证体验
了解他们如何创建了一项内部技术教育计划,旨在支持数千名员工学习包括机器学习和网络安全在内的多个学科中实用且前沿的技能。

Beyond Compliance: Motorola Solutions Drives Winning Security Culture
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

ASRG 对汽车软件安全的推动
请阅读这份详尽的案例研究,了解他们如何利用 Secure Code Warrior 的竞赛功能来提升开发人员的参与度,增强对汽车软件关键漏洞的认知,并获取跨多种语言和框架的衡量指标。

Application Security @ NAB | Gamified Security Training: The Key to Scalable Developer Growth
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
SD Times: Benchmarking AI-assisted developers (and their tools) for superior AI governance
If the tech stack lacks tools that oversee not only developer security proficiency, but also the trustworthiness of approved AI coding companions each developer uses, then it is likely that efforts to uplift the overall security program and the developers working within it will be short of the appropriate data insights to effect change.
ITWire: The Benefits and Risks of Using AI Tools in Software Development
The process of software development is undergoing a period of expedited change. Thanks to massive advances in artificial intelligence (AI) technology, projects can be completed more rapidly and by people with little or no prior experience.

LeadDev: Ethics are being forgotten as the AI race heats up
Is the tech industry capable of the change needed to curb ethical and environmental concerns?
Secure Code Warrior Expands Commitment to Secure by Design Best Practices with Free Secure Code Video Series for Developers
Launch of new 12-week video series on AI/LLM security empowers developers to safely adopt AI coding and mitigate emerging security risks.

CSO Online: When AI nukes your database: The dark side of vibe coding
As developers lean on Copilot and GhostWriter, experts warn of insecure defaults, hallucinated dependencies, and attacks that slip past traditional defenses.

The AI Journal: Resilience and Developer Risk Management: Two Pillars of Success in the Era of Secure by Design and AI Coding
Change is afoot in cybersecurity governance, and it couldn’t come at a more transformative time for security leaders worldwide. The White House issued a recent Executive Order (EO) designed to “reprioritize cybersecurity efforts to protect America”, and with it, reduce friction related to overzealous government oversight to focus on protecting critical digital assets and enhanced secure technology practices. Coupled with significant cuts to CISA, one could be forgiven for being apprehensive of the right approach going forward, especially in the wake of rapid AI technology progression and Secure by Design initiatives.

SecurityWeek: How to Close the AI Governance Gap in Software Development
Widespread adoption of AI coding tools accelerates development—but also introduces critical vulnerabilities that demand stronger governance and oversight.

teiss: When regulations aren’t enough
Pieter Danhieux at Secure Code Warrior explains why “Secure by Design” has emerged as mission critical for software development

Information Age: Vibe coding is a hot skill – and security experts are worried
GenAI tools are building insecure apps faster than ever.

CXFocus Magazine: Going above and beyond in 2026
Today’s customers are an exacting lot with little tolerance for suppliers that fail to meet their ever-increasing expectations. Almost 94 per cent of Australian consumers stopped purchasing from at least one company after a negative experience, according to CPM’s 2025 The State of Customer Experience in Australia Report.

SafetyDetectives: Interview With Matias Madou - CTO and Co-Founder at Secure Code Warrior
SafetyDetectives recently sat down with Matias Madou, CTO and Co-Founder of Secure Code Warrior, to discuss his journey from software developer to cybersecurity leader and entrepreneur. With a background in security research, obfuscation techniques, and nearly a decade at Fortify, Matias has seen firsthand how critical it is to upskill developers if organizations hope to defend against modern threats. In this interview, he shares how Secure Code Warrior is helping organizations foster a security-first development culture, the risks and opportunities of AI-driven coding tools, and why the path to safer software must always begin with better-trained developers.

Dark Reading: Do Claude Code Security Reviews Pass the Vibe Check?
AI-assisted security reviews from Anthropic and others could help level up enterprise application security in the era of vibe coding.

GovTech Review: The global challenge of achieving cyber resilience
Concerningly, 2030 is only five years away, and cybersecurity efforts — whether national, international or specific to organisations — still face many of the same barriers that have always hampered comprehensive security. For this reason there remains a question mark over whether countries will be able to meet their 2030 goals.

KBI Media: AI Coding Assistants Boost Productivity … But At What Cost to Security?
As the pressure mounts to ship faster and innovate more aggressively, development teams must remember that code security is no longer optional but a business-critical necessity.
Forbes: Beware Of Agentic AI’s Heel Turn As Corporate Security Villain
Enterprises need to assert AI governance and ensure that developers are equipped to maintain oversight, with the security skills to safely prompt and review AI-assisted code and commits.
Techradar Pro: Why continuous security improvement for developers is the key to renewed resilience
While change can be challenging to navigate, the current security climate feels like the perfect time to embrace measures that will improve software quality and reduce risk for years to come.
DevOps Digest: From Helper to Hacker: How AI Tools Can Be Turned Against You
A recent finding by InvariantLabs uncovered a critical vulnerability in the Model Context Protocol (MCP), an API-like framework allowing powerful AI tools to autonomously interact with other software and databases, that allows for what has been dubbed "Tool Poisoning Attacks," a new vulnerability category that could prove especially damaging in the enterprise.

Technology Decisions: Secure by Design: Vital in an evolving threat landscape
In the evolving world of software development, a familiar term is gaining renewed urgency: Secure by Design.

Information Week: Will Any Countries Meet the Cyber Resilience Challenge?
One of the key hurdles facing nations and enterprises in achieving cyber resilience goals is the lack of security personnel and advanced security skills.

SecurityBrief Australia: The risks of using AI in the software development pipeline
AI coding assistants are not going away, and the upgrade in code velocity cannot be ignored. However, security leaders must act now to manage their use safely.

ITWire: AI Appreciation Day
Artificial Intelligence Appreciation Day celebrates the way AI has changed our lives for the better. This year, we speak to AI leaders to analyse what the next wave of innovations has in store for us and their transformative impact on various industries worldwide.

Dynamic Business: AI Appreciation Day: What business leaders really think about AI right now
On AI Appreciation Day, industry experts reveal how smart, responsible AI use is transforming business, empowering people, and driving meaningful innovation.

In AI Today: How to keep AI-assisted software development under control
Faced with large workloads and relentless deadlines, developers are understandably inclined to turn to third-party AI tools, sometimes without vetting them or getting approval from supervisors. It’s creating a trend dubbed ‘Shadow AI’. This should be of concern for all senior executives as unmanaged AI decreases overall enterprise visibility of development processes while increasing the potential for new vulnerabilities that are not adequately captured or managed.

Help Net Security: Cybersecurity essentials for the future: From hype to what works
Cybersecurity never stands still. One week it’s AI-powered attacks, the next it’s a new data breach, regulation, or budget cut. With all that noise, it’s easy to get distracted. But at the end of the day, the goal stays the same: protect the business.

Cyber Daily: Bad practices are increasing security risks within software development projects
A recent CISA discussion paper details some exceptionally risky software development activities that are in all-too-common use.

Techstrong.tv: [VIDEO] Secure Code Warrior CTO Matias Madou on Empowering Developers with AI-Driven Security Tools
Matias Madou, CTO and Co-Founder of Secure Code Warrior, shares his journey in app security and how AI is helping developers write secure code. He introduces new AI security rules, available free on GitHub, and discusses the future of development tools and AI solutions.
DevOps.com: Secure Code Warrior Defines Security Rules for AI Coding
Secure Code Warrior has made available a set of security rules for application developers using artificial intelligence (AI) tools to generate code.

SecurityBrief Australia: Secure Code Warrior unveils free AI security rules for developers
Secure Code Warrior has released AI Security Rules on GitHub, offering developers a free resource aimed at improving code security when working with AI coding tools.
KBI Media: Overcoming The Complexity And Security Issues Posed By AI Coding Tools
The current software environment has grown out of control security-wise and this trend shows no signs of slowing. However there is hope for slaying the twin challenges of complexity and insecurity.
Secure Code Warrior Unveils Industry-First AI Coding Rulesets to Guide Safer AI Code Deployment
Secure Code Warrior, the leading developer risk management company, today announced the availability of AI Security Rules on GitHub – a first-of-its-kind, free resource to help developers generate more secure code when working with AI coding tools like GitHub Copilot, Cline, Roo, Cursor, Aider and Windsurf.
Help Net Security: Free AI coding security rules now available on GitHub
Developers are turning to AI coding assistants to save time and speed up their work. But these tools can also introduce security risks if they suggest flawed or unsafe code. To help address that, Secure Code Warrior has released a new set of free AI Security Rules on GitHub.

DevPro Journal: Secure Code Warrior unveils AI coding rulesets to guide safer AI code deployment
Community-driven resource empowers developer teams of all sizes to integrate AI safely into critical workflows.

SD Times: Managing the growing risk profile of agentic AI and MCP in the enterprise
Security leaders need to take a hard look at how these risks affect their business, being sure they understand the potential vulnerabilities that result from using agentic AI and MCP, and take the necessary steps to minimize those risks.

HackerOne Launches Technology Alliance Program to Advance AI-Powered Security Ecosystem and Customer Innovation
HackerOne, a global leader in offensive security solutions, today announced the launch of its PartnerOne Technology Alliance Program. The initiative is designed to accelerate secure innovation by connecting leading technology providers with HackerOne’s AI-powered platform that seamlessly scales human security expertise through AI agents to not just find but remediate vulnerabilities.
Dark Reading: Next-Gen Developers Are a Cybersecurity Powder Keg
AI coding tools promise productivity but deliver security problems, too. As developers embrace "vibe coding," enterprises face mounting risks from insecure code generation that security teams can't keep pace with.

Conversational AI News: Training Developers to Build Defensively with AI
Today we're meeting Pieter Danhieux, CEO & Co-Founder at Secure Code Warrior. They specialise in secure coding practices and developer risk management.
ITWire: The Importance Of Security Benchmarking When Using AI Development Tools
If it was possible to have an experienced chef in the kitchen to help prepare a sophisticated dish, most people would happily accept the assistance. The same holds true for a qualified contractor to work on a home-improvement project, or an office aide to handle tedious, repetitive tasks.
DevOps Digest: Fix It or Face the Consequences: CISA's Memory-Safe Muster
While CISA's efforts can help companies navigate the "need for speed" in a fast-moving DevOps environment, IT and security leaders across the private sector must do their part to prepare their companies for the necessary changes.

SC Magazine UK: Secure-by-Design Is Hard, but Our Online Future Depends on It
Secure software hinges on introducing security at the beginning of the SDLC.
ITWire: Experts Confirm DeepSeek Too Insecure for Enterprise Deployment
While DeepSeek’s capabilities seem to be extensive, experts have identified significant failings – particularly from a security perspective.
Cyber Daily: Secure-by-design principles struggle to find unified enterprise adoption
While awareness of the concept of ‘Secure by Design’ is growing within many organisations, its usage remains fragmented and inconsistent.

Built In: How to Tame ‘Unleashed’ AI-Assisted Software Development
The rise of AI coding assistants in software development has introduced new vulnerabilities. Our expert, Dr Matias Madou, offers advice for stemming the tide.

Cybersecurity Tribe: Experts Reveal How Agentic AI Is Shaping Cybersecurity in 2025
We were lucky enough at RSAC 2025 to interview a series of industry experts to explore this issue, "Where exactly are we with Agentic AI in cybersecurity in 2025?"

DevOps.com: How Benchmarking Can Help Software Development Teams Achieve CISA’s “Secure by Design”
Organizations can more readily achieve CISA’s Secure by Design through benchmarking by implementing the following developer-centric best practices.

Bank Info Security: Secure by Design: Moving Beyond Checkbox Compliance
Secure Code Warrior CEO Danhieux Urges Clarity Around Secure-by-Design Practices.

SecurityWeek: Developers Must Slay the Complexity and Security Issues of AI Coding Tools
The advantages AI tools deliver in speed and efficiency are impossible for developers to resist. But the complexity and risk created by AI-generated code can’t be ignored.

The AI Journal: Why Security Benchmarking Has Emerged as Critical for AI in Software Development Tools
In the last five years, nearly two-thirds of IT executives and administrators say their organisation has incorporated AI tools into the software development lifecycle (SDLC), according to research from KPMG and OutSystems, which makes available a low-code, AI-supported platform to build applications.
KBI Media: How Adopting Maturity Models Can Improve Enterprise IT Security
With risk assessments becoming a higher priority, organisations need to take an approach with developer-driven security that actively targets developer risk management, skills enhancement and strategic repository “gatekeeping”. Initiatives that can help them stay on course while assessing their current security levels and creating an action plan that aligns with BSIMM or OWASP SAMM.
Forbes: How Companies Can Chart The Way Along The Secure-By-Design Path
From our own observations, we've found that organizations generally need three to five years to fully integrate SBD into their software development practices as part of a developer risk management commitment. But we've also seen that it’s well worth the time and effort: Within the context of the software development life cycle (SDLC), SBD promotes a “security first” enterprise culture and mindset in eliminating vulnerabilities as early as possible in the process.

TechRadar Pro: Secure by design: what we can learn from the financial services sector
Secure by design in software development, inspired by financial services.

Dynamic Business: 26 Aussie startups to unleash cyber fixes at ACE 25
The Australian Cyber Exchange 2025 (ACE 25), in collaboration with the Tech Council of Australia (TCA), rolled out in Sydney and is aimed at building up Australia’s own cyber capabilities.
iTWire: The Tech Council of Australia Bolsters Collaboration To Building Sovereign Capability To Keep Australians Safe
The Tech Council of Australia (TCA) is collaborating with industry and government leaders to advocate for the national approach across the cyber ecosystem and is reinforcing its position on building sovereign cyber security capability.

Intelligent CIO: The Tech Council of Australia bolsters collaboration to building sovereign capability
Collaboration pitched as a critical step to ensure industry and government are taking a coordinated approach to building Australia’s cyber security and resilience.
KBI Media: How Organisations Can Achieve Secure-By-Design By 2030
Governments worldwide, from the UK to Australia, have set ambitious goals to enhance software security by 2030, particularly within critical infrastructure. However, achieving a secure-by-design (SBD) approach is not merely a matter of deploying advanced security tools or implementing stringent policies. Rather, it necessitates a fundamental shift in organisational culture, prioritising security at every level of software development.
Cyber Daily: Paving a pathway to better Australian cyber security preparedness
Australia’s goal of seeding a zero-trust culture across all organisations can be significantly achieved by focusing on the first line of defence against threat actors: software developers.
SecurityWeek: Security Maturity Models: Leveraging Executive Risk Appetite for Your Secure Development Evolution
Organizations can align their processes with one of two global industry standards for self-assessment and security maturity—BSIMM and OWASP SAMM.

SD Times: DeepSeek is unsafe for enterprise use, tests reveal
The birth of China’s DeepSeek AI technology clearly sent shockwaves throughout the industry, with many lauding it as a faster, smarter and cheaper alternative to well-established LLMs. However, similar to the hype train we saw (and continue to see) for the likes of OpenAI and ChatGPT’s current and future capabilities, the reality of its prowess lies somewhere between the dazzling controlled demonstrations and significant dysfunction, especially from a security perspective.

Energy Source & Distribution: How to boost security of Australia’s critical infrastructure
Increasing technical complexity and a widening attack surface are making life tough for IT security professionals. Faced with an evolving threat landscape, the pressure is on to deploy and maintain effective protection for critical infrastructure.

KBI Media: A Supercharged Security Culture is Needed to Navigate Australia’s Cybersecurity Rules
A success marker in cybersecurity has traditionally been for an organisation to have an uneventful year – but this has become much harder to pull off. Even if an organisation manages to navigate the threat landscape without incident, it must still meet an ever-growing list of requirements just to maintain its license to operate. Australian CISOs have never had to deal with a greater number of legislative and regulatory requirements being imposed to drive secure behaviours and uplift collective cybersecurity postures.

Intelligent CISO: Q&A: How organizations can achieve Secure-by-Design by 2030
Matias Madou, Co-founder and CTO, Secure Code Warrior, says Secure-by-Design (SBD) requires a cultural shift in how developers approach security.
Cyber Daily: Finalists revealed for the Australian Cyber Awards 2025
Cyber Daily has unveiled that more than 220 finalists have been selected out of over 300 submissions for the annual Australian Cyber Awards.

Manufacturing.net: Rethinking Critical Infrastructure: A Secure Path for High-Risk Connectivity
Digital frontiers are highly prized targets, and this will ramp up in the coming years.
KBI Media: Understanding The Risks Associated With ‘Shadow AI’ In Software Development
According to research by the Australian Government’s Department of Industry, Science and Resources[1], 35% of small and mid-sized businesses are already using AI tools and usage is expected to continue to increase. Applications include everything from marketing automation and fraud detection to data and document processing.
Cyber Daily: The Industry Speaks: Data Privacy Day 2025
January 28 is International Data Privacy Day, and this year’s theme is ‘Taking Control of Your Data’ – here’s some expert advice and perspectives on how to do just that.

DevOps.com: How to Prove That Your Security-Aware Developers are a Cut Above the Rest
Companies that need to respond by upskilling their developers should take a three-tiered approach that includes implementing a measured program to deliver education and competency, providing right-fit tools that suit the organization’s tech stack, and overhauling the processes that have led to cut corners and insecure coding patterns running rampant.

DevOps.com: Navigating the Next Wave of Cybersecurity Legislation With a Supercharged Security Culture
CISA’s Secure-by-Design guidelines are gaining traction as a higher standard for software vendors to achieve, while updates from NIST, PCI and the EU-wide NIS2 Directive are having a global impact on many enterprise companies. Smart CISOs are utilizing their full team potential through role-based upskilling and especially enabling the development cohort to take pressure off the AppSec team by honing their security prowess on an ongoing basis.

teiss: Balancing AI innovation and security
LLMs struggle to generate consistently secure code. Security-skilled developers can help ensure secure AI-generated code while optimising performance. Pieter Danhieux at Secure Code Warrior explores a CISO’s role in AI-powered coding.

Dark Reading: OWASP's New LLM Top 10 Shows Emerging AI Threats
Ultimately, there is no replacement for an intuitive, security-focused developer working with the critical thinking required to drive down the risk of both AI and human error.
KBI Media: Cybersecurity’s Evolution And The Shift Toward Secure-By-Design Principles
In the ever-changing landscape of cybersecurity, experts are increasingly advocating for Secure-by-Design principles to address the accelerating challenges of today’s digital world. The concept emphasises embedding security into software from the beginning of the development process in a shift that reflects a significant maturation of the cybersecurity industry.
SecurityWeek: How to Eliminate “Shadow AI” in Software Development
With a security-first culture fully in play, developers will view the protected deployment of AI as a marketable skill, and respond accordingly.
SecurityBrief Australia: How AI and software development will continue to shape the developer community in 2025
Organisations are facing tough decisions on AI usage to support long-term productivity, sustainability, and security ROI.It's become clear to us over the last few years that AI will never fully replace the role of the developer. From AI + developer partnerships to the increasing pressures (and confusion) around Secure-by-Design expectations, here's what we can expect over the next year.
ITWire: Why Software Developers Need a Security ‘Rewards Program’
Frequent flyer and other points-based programs reward people who remain loyal to particular brands or organisations. The programs issue points to participants who can use them for discounts or purchases in the future. Some airline programs also reward loyal customers with perks such as priority boarding and lounge access. It’s becoming clear that the software development industry could use something similar, especially when it comes to ensuring a ‘security first’ mindset among developers.

In AI Today: Achieving effective security in an AI-assisted software development world
It’s highly likely that AI-assisted development will become even more of a norm in the near future. Organisations will, therefore, have to establish policies and best practices to effectively manage it, just as they’ve done with cloud deployments, Bring Your Own Device (BYOD), and other tech-in-the-workplace trends.
DevOps Digest: 2025 DevSecOps Predictions
As part of DEVOPSdigest's annual list of DevOps predictions, DevSecOps experts — from analysts and consultants to the top vendors — offer thoughtful, insightful, and often controversial predictions on how DevSecOps and related risks and tools will evolve in 2025.
SecurityWeek: How to Implement Impactful Security Benchmarks for Software Development Teams
Benchmarking is all about taking back control – you’re measuring to gain complete awareness of your development teams’ security skills and practices.
KBi Media: Secure-By-Design Is A Significant Exercise, But The Rewards Are Significant, Too
Concerted multilateral efforts are underway to influence and change developer behaviour when it comes to secure software creation.

The Peter Carr Blog: Gary Kasparov and the New Code Generation
Man vs. Machine in the Era of AI and Secure Coding.

VMBlog: OpenText Partners with Secure Code Warrior to Deliver Comprehensive Application Security and Customized Developer Risk Management
OpenText announced a strategic partnership with Secure Code Warrior to integrate its dynamic learning platform into the OpenText Fortify application security product suite. This partnership will help developers improve their secure coding skills through real-time training to reduce risks, quickly identify and resolve vulnerabilities, and ultimately build greater trust with customers.

SecurityInfoWatch: OpenText partners with Secure Code Warrior to deliver comprehensive app security
The new agreement empowers development teams with continuous upskilling to turn security into a strategic advantage, reduce risks, and elevate customer trust.
SecurityBrief Australia: OpenText partners with Secure Code Warrior to boost security
OpenText and Secure Code Warrior have announced a strategic partnership to integrate Secure Code Warrior's dynamic learning platform into the OpenText Fortify application security product suite.
ITWire: OpenText Partners with Secure Code Warrior to Deliver Comprehensive Application Security and Customised Developer Risk Management
The new agreement empowers development teams with continuous upskilling to turn security into a strategic advantage, reduce risks, and elevate customer trust.

Cyber Magazine: OpenText Partnership Targets Software Supply Chain Fears
OpenText partners with Secure Code Warrior to address rise in supply chain attacks through enhanced security training for coders and adoption of DevSecOps.
OpenText Partners with Secure Code Warrior to Deliver Comprehensive Application Security and Customized Developer Risk Management
The new agreement empowers development teams with continuous upskilling to turn security into a strategic advantage, reduce risks, and elevate customer trust.

[PODCAST] Information Week: Have We Gone Too Far With AI in Software Development?
Has the promise of improved efficiency through AI been realized in software development? Is there still a place for citizen developers with AI in the development cycle?
DevOps Digest: How Organizations Can Create Successful Secure-by-Design Programs
Our latest research paper, Benchmarking Security Skills: Streamlining Secure-by-Design in the Enterprise is the result of deep analysis of real Secure-by-Design initiatives at the enterprise level, and deriving the best practices for implementation based on data-driven findings.

Cybersecurity Insiders: Building a Security “Loyalty Program” for Software Developers is a Winning Formula in 2025
The software development industry could use something like a “frequent flyer status” system – especially when it comes to fostering a “security-first” mindset among developers. Without any incentive program, it’s nearly impossible for organisations and their developer teams to evaluate their security proficiency and compare their competencies alongside peers.

Authority Magazine: Matias Madou Of Secure Code Warrior On Embedding Security in Product Design and Development
CISOs need to lead a transition from the uncertainty of shadow AI to a more known, controlled and well-managed ‘Bring Your Own AI’ (BYOAI) environment. This will require full executive buy-in, careful implementation of AI into the existing tech stack and adoption of secure-by-design principles as part of a security-first culture that doesn’t slow down a product rollout.

Dynamic Business: New Cyber rules: Are experts pumped or pessimistic?
On November 25, 2024, the Australian Parliament passed significant reforms to bolster the nation’s cyber security posture, forming part of a strategic effort to position Australia as a global leader in cyber security by 2030.
Cyber Daily: Industry responds to passing of Australia’s Cyber Security Act
Opinions are mixed on the nation’s new cyber security legislation, which has been deployed as part of the 2023–2030 Australian Cyber Security Strategy.
Forbes: Strategic Secure-By-Design Initiatives: Best Practices For Meaningful Outcomes
It is possible to realize a meaningful secure-by-design initiative and lead the charge in transforming the current status quo around security culture. Let’s discuss the challenges ahead and techniques to overcome them in enterprise security and development teams.
KBI Media: Overcoming Common Security Vulnerabilities In The Banking Sector
While the physical security measures in place within many banks today are impressive – large vaults, bullet-proof glass, silent holdup alarms – it can be a very different story when it comes to cybersecurity.
DevOps Digest: Exploring the Power of AI in Software Development
DEVOPSdigest invited experts across the industry — consultants, analysts and vendors — to comment on how AI can support the software development life cycle (SDLC). Part 3 of this series covers advantages gained by leveraging AI tools in software development.
SecurityWeek: How to Improve the Security of AI-Assisted Software Development
CISOs need an AI visibility and KPI plan that supports a “just right” balance to enable optimal security and productivity outcomes.
DevOps.com: 6 Essential Components of a Successful Security ‘Rewards Program’ for Software Developers
Whether teams opt for on-the-job collaborative training opportunities or interactive, agile learning sessions, they would substantially benefit from standardized developer benchmarking for success. Such benchmarking could lead to a ‘trust score’ that, much like rewards programs, would provide incentives to developers for their security achievements and offer clear pathways for improvement.

SecurityInfoWatch: Critical infrastructure industries making progress on Secure-by-Design developer readiness
Secure Code Warrior's analysis highlights the critical need for developer upskilling to properly measure Secure-by-Design progress.

ITWire: Secure Code Warrior Research: Critical Infrastructure Industries Making Progress on Secure-by-Design Developer Readiness
New analysis collaborated on with Paladin Global Institute highlights the critical need for developer upskilling to properly measure Secure-by-Design progress
Secure Code Warrior Research: Critical Infrastructure Industries Making Progress on Secure-by-Design Developer Readiness
New analysis collaborated on with Paladin Global Institute highlights the critical need for developer upskilling to properly measure Secure-by-Design progress.

Politico: Cyber is getting schooled
Less than 4 percent of developers globally are involved in Secure-by-Design upskilling initiatives, according to new research out this morning by Secure Code Warrior.

NextGov: Few software developers employ secure by design training, research finds
The analysis, conducted by Secure Code Warrior, is supported by former White House cybersecurity officials Kemba Walden and Chris Inglis.

Cyberscoop: Organizations can substantially lower vulnerabilities with secure-by-design practices, report finds
Ex-National Cyber Director Inglis says “quantitative data” in Secure Code Warrior’s report shows the importance of the cybersecurity practice.