Linux 中的 XZ Utils 后门指向了更广泛的供应链安全问题,我们需要的不只是社区精神,更需要切实有效的防御措施。
随着一起隐蔽的软件供应链攻击被曝光,网络安全行业再次拉响了警报。该漏洞存在于随主流 Linux 发行版发布的 XZ Utils 数据压缩库中,编号为 CVE-2024-3094,其本质是一个由曾经受信任的志愿者维护者蓄意植入的后门。如果被成功利用,在某些情况下它允许远程代码执行(RCE),这是一个高危漏洞,能够对既定的软件构建流程造成严重破坏。
幸运的是,另一位维护者在恶意代码进入 Linux 稳定版本之前发现了这一威胁,但它仍然对那些已开始在 Fedora Rawhide 中运行 XZ Utils 5.6.0 和 5.6.1 版本的用户构成了问题,相关组织被敦促紧急修补该漏洞。如果此次发现不够及时,其风险程度可能使其成为有史以来最具破坏性的供应链攻击之一,甚至可能超过 SolarWinds 事件。
对社区志愿者维护关键系统的依赖已是众所周知,但除非像此次事件这样产生重大影响,否则很少被讨论。虽然他们的辛勤工作对于开源软件的维护至关重要,但这凸显了在开发者层面加强安全技能和意识的必要性,更不用说围绕软件仓库加强访问控制了。
什么是 XZ Utils 后门,以及如何进行缓解?
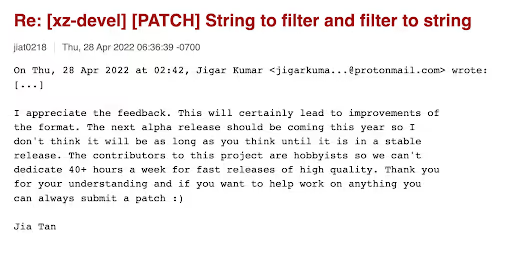
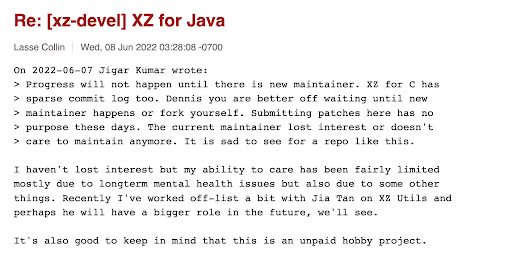
3 月 29 日,红帽公司发布了紧急安全警报,通知 Fedora Linux 40 和 Fedora Rawhide 的用户,最新版本的“XZ”压缩工具和库包含恶意代码,这些代码似乎是专门为促进未经授权的第三方访问而构建的。这些恶意代码是如何被注入的,未来可能会成为深入研究的主题,但它归结为攻击者(一个化名为“Jia Tan”的威胁行为者)进行的一场复杂、耐心且长达数年的社会工程学演练。此人花费了无数时间赢取其他维护者的信任,在两年多的时间里为 XZ Utils 项目和社区做出了合法贡献,在多个马甲账号削弱了对项目所有者 Lasse Collin 的信任后,最终获得了“受信任维护者”的身份:
这种不同寻常的情况是一个典型的例子,说明即使是高技术人员也可能成为通常针对技术水平较低者所使用的策略的受害者,这表明需要进行精确的、基于角色的安全意识培训。正是因为微软软件工程师兼 PostgreSQL 维护者Andres Freund的好奇心和敏捷思维,该后门才得以被发现并回滚了版本,从而阻止了可能成为近期记忆中最具破坏性的供应链攻击。
The backdoor itself is officially being tracked as a vulnerability of the highest possible severity in NIST’s registry. Initially thought to allow SSH authentication bypassing, further investigation revealed that it enabled unauthenticated remote code execution on vulnerable Linux systems, including Fedora Rawhide, Fedora 41, Kali Linux, openSUSE MicroOS, openSUSE Tumbleweed, and some versions of Debian.
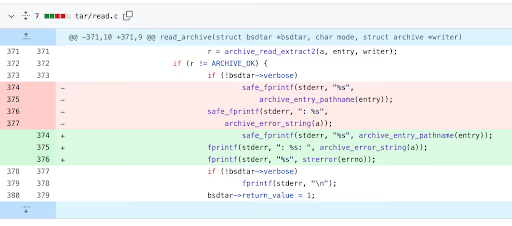
Jia Tan appears to have gone to great lengths to obfuscate the malicious package, which, when triggered to construct itself during the build process, hampers authentication in SSHd via systemd. As Red Hat detailed, in the right circumstances, this interference could potentially allow an attacker to break SSHd authentication and gain remote unauthorized access to the entire system.
Microsoft, among others, has published comprehensive guidance on scanning systems for instances of the exploit and mitigating its effect, and the immediate action recommended by CISA is that affected developers and users should downgrade XZ Utils to an uncompromised version, like XZ Utils 5.4.6 Stable.
Preventing this attack type is incredibly difficult - especially when utilizing open-source components in software - as there is precious little assurance and transparency over the security of the supply chain. We've already combatted accidental flaws in the software supply chain, but this risk has elevated to include security bugs deliberately planted with malice to compromise open-source security.
Most developers will not be able to stop an attack of this nature unless they have a strong sense of security awareness, healthy security knowledge, and a sprinkling of paranoia. It’s almost a case of requiring a threat actor mindset. However, a chief consideration should always center around source code repos that are controlled internally (i.e. not open-source). These should only be accessible to people who have verified, relevant security skills. AppSec professionals might consider a setup like branch-level security controls, only allowing security-skilled developers to commit changes to the final master branch.
志愿者维护者是英雄,但维护安全软件需要全社会的共同努力
对于软件工程领域之外的人来说,一个充满激情的志愿者社区在业余时间辛苦维护关键系统的想法很难理解,但这正是开源开发的本质,也是保护供应链的安全专业人员面临的关键风险领域。
开源软件几乎是每个企业数字生态系统中至关重要的一部分,受信任的维护者(其中大多数是出于善意)在无私追求技术进步和完整性方面确实是英雄,但让他们孤军奋战是荒谬的。在当今以 DevSecOps 为中心的时代,安全是共同的责任,每位开发者都必须掌握知识和合适的工具,以应对工作中可能遇到的安全问题。安全意识和实践技能在软件开发过程中应是不可妥协的,安全领导者有责任在企业层面推动变革。
立即通过 Secure Code Warrior 的深度课程,在您的组织中建立蓬勃发展的安全文化。
在 AI 驱动的开发成果发布前实现有效治理
评估 AI 辅助风险,在提交代码时强制执行安全编码策略,并加速整个软件开发生命周期的安全交付。
探索更多博客
获取有关安全编码、人工智能治理和软件风险管理的专家内容。

Supercharged Security Awareness: How Tournaments are Inspiring Developers at Erste Group
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

Security as culture: How Blue Prism cultivates world-class secure developers
Learn how Blue Prism, the global leader in intelligent automation for the enterprise, used Secure Code Warrior's agile learning platform to create a security-first culture with their developers, achieve their business goals, and ship secure code at speed




在产品发布前确保 AI 驱动的开发安全
洞察开发风险,执行安全策略,并在整个软件开发生命周期中预防漏洞。
