Insights from experts shaping secure development
Access expert content on secure coding, AI governance, and software risk management.

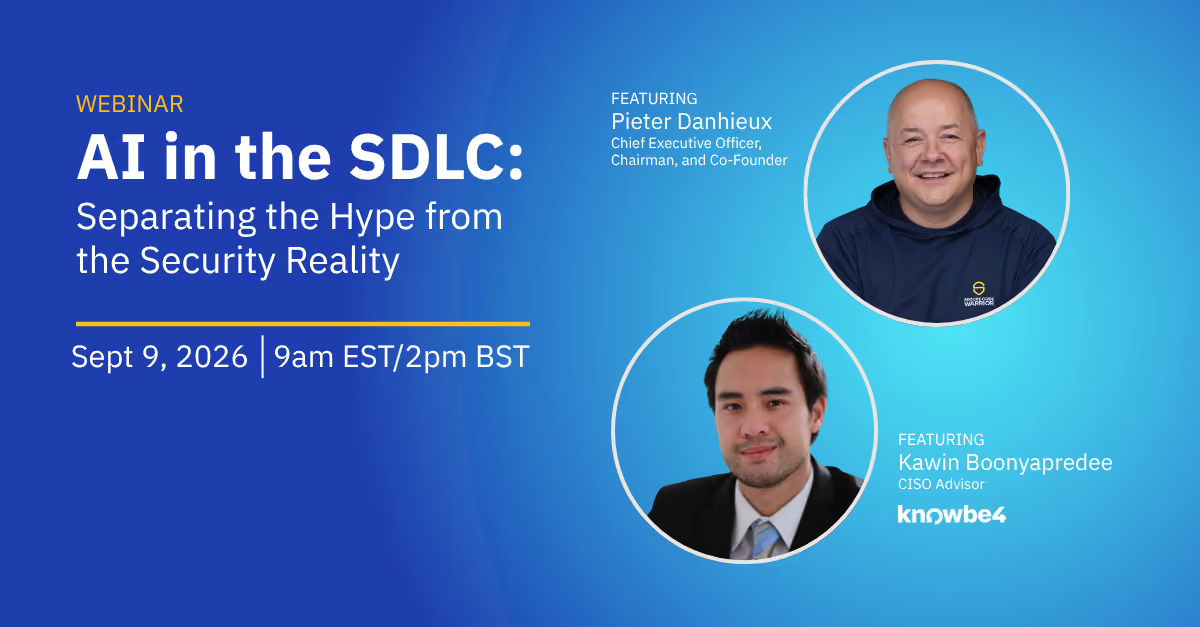
SDLC における AI:過度な期待とセキュリティの現実の分離
KnowBe4 との提携による SDLC における AI:Kawin Boonyapredeeto と Pieter Danhieux が AI コードセキュリティリスクを解説します。
ジャーマン OWASP デイ 2026
Secure Code Warrior はジャーマン OWASP デイ 2026 をスポンサーし、セキュアな開発、運用、テストのベストプラクティスを共有します。
アデレードSEC (AdelaideSEC)
Secure Code Warrior は AdelaideSEC でセキュアコーディングトーナメントを開催します。開発者や専門家が実戦形式で競い合います。
Black Hat USA 26
Secure Code Warrior はラスベガスの Black Hat USA 2026 に出展します。CEO Pieter Danhieux、CCO Fatemah Beydoun らが現地にいます。
FS-ISAC APAC サミット
2026年7月14〜15日にシンガポールで開催される FS-ISAC APAC サミットをスポンサーするのが楽しみです!ブース #8 にお立ち寄りください。
Gartner セキュリティ & リスクマネジメント サミット 2026
2026年9月22〜24日にロンドンで開催される Gartner セキュリティ & リスクマネジメント サミットをスポンサーできることに興奮しています!

OWASP グローバル AppSec USA
2026年11月5〜6日にサンフランシスコのハイアットリージェンシーで開催される OWASP Global AppSec USA 2026 のシルバースポンサーを務めることを誇りに思います!

開発者主導のセキュリティの未来:Checkmarx SAST と SCW の統合
この統合は、脆弱性の検出と修復の間のギャップを埋め、必要な瞬間に正確な学習リソースを開発者に提供します。

ソフトウェア開発における DevSecOps の不可欠な役割
SCW Coffee Shop @RSAC24提供:DevSecOps の思想的リーダーや業界専門家とともに、今日の開発における DevSecOps のクリティカルな役割を掘り下げます。
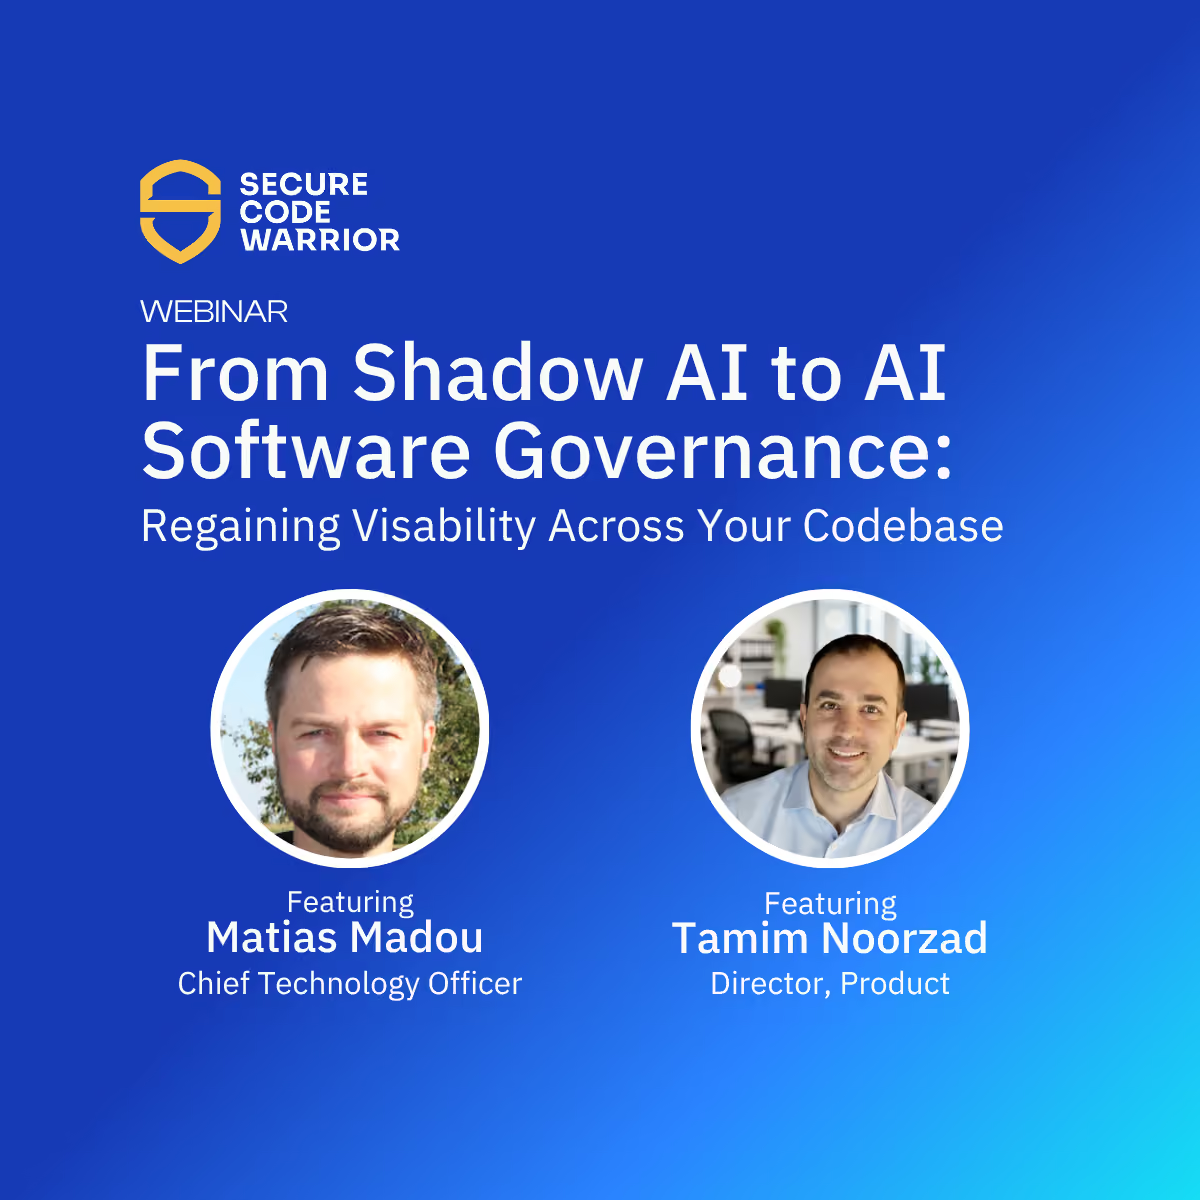
シャドーAIからAIソフトウェアガバナンスへ:コードベース全体での可視性の奪還
Secure Code Warrior の CTO Matias Madou とプロダクトディレクターの Tamim Noorzad から、大規模な AI 支援開発の管理に必要な視点と可視性について学びましょう。

OWASP グローバル AppSec ヨーロッパ
2026年6月22〜26日にウィーンのオーストリアセンターで開催される25周年記念 OWASP Global AppSec EU カンファレンスをスポンサーできるのが待ちきれません!

OWASP BASC
4月11日にマサチューセッツ州ボストンで開催される OWASP BASC をスポンサーできることを嬉しく思います。専門家が集まるプレミア会議です。

OT サミット・マドリード
AI、クラウド、安全な情報管理が新世代のインテリジェント企業をどのように推進しているかを示す OpenText Summit Madrid 2026 にご参加ください。
サイバーセキュリティ サミット
サイバーセキュリティサミットは、トップクラスの専門家、革新者、出展者が集まり、最新トレンドとITレジリエンス戦略を披露する会議です。
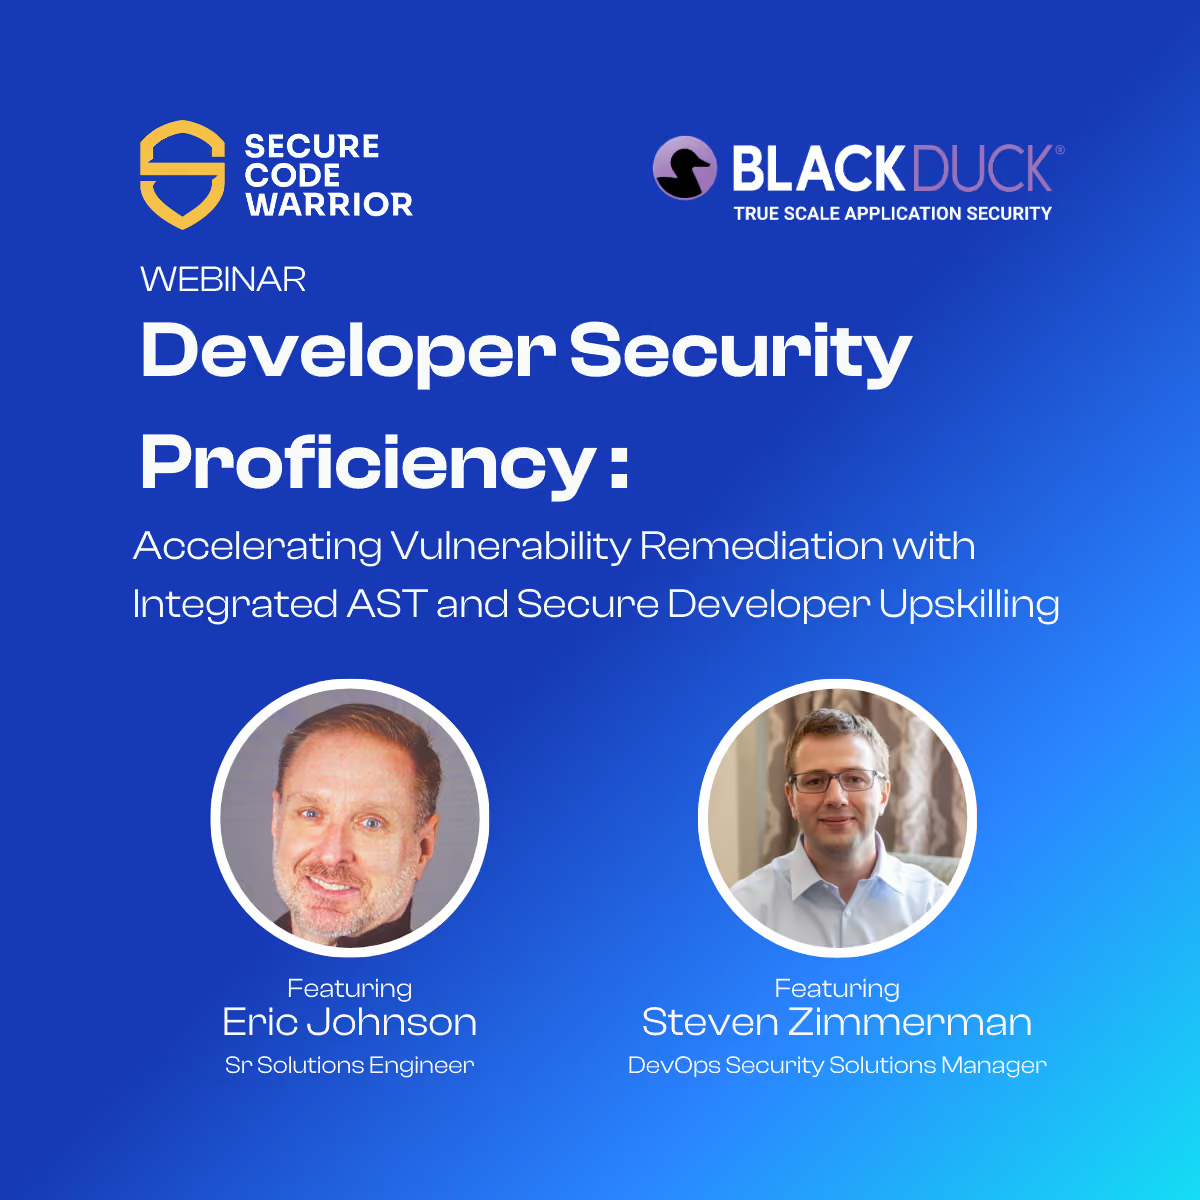
開発者のセキュリティ熟達:統合ASTとスキルアップによる脆弱性修正の加速
脆弱性を見つけるだけでなく、根本的に修正しましょう。真の Secure by Design を実現するためのアプローチをご紹介します。

自信を持ってシフト左へ:開発者ワークフローへのセキュリティのネイティブ組み込み
SCW と Checkmarx の専門家を結集し、開発プロセスにセキュリティを円滑に統合するためのベストプラクティスと戦略を共有します。
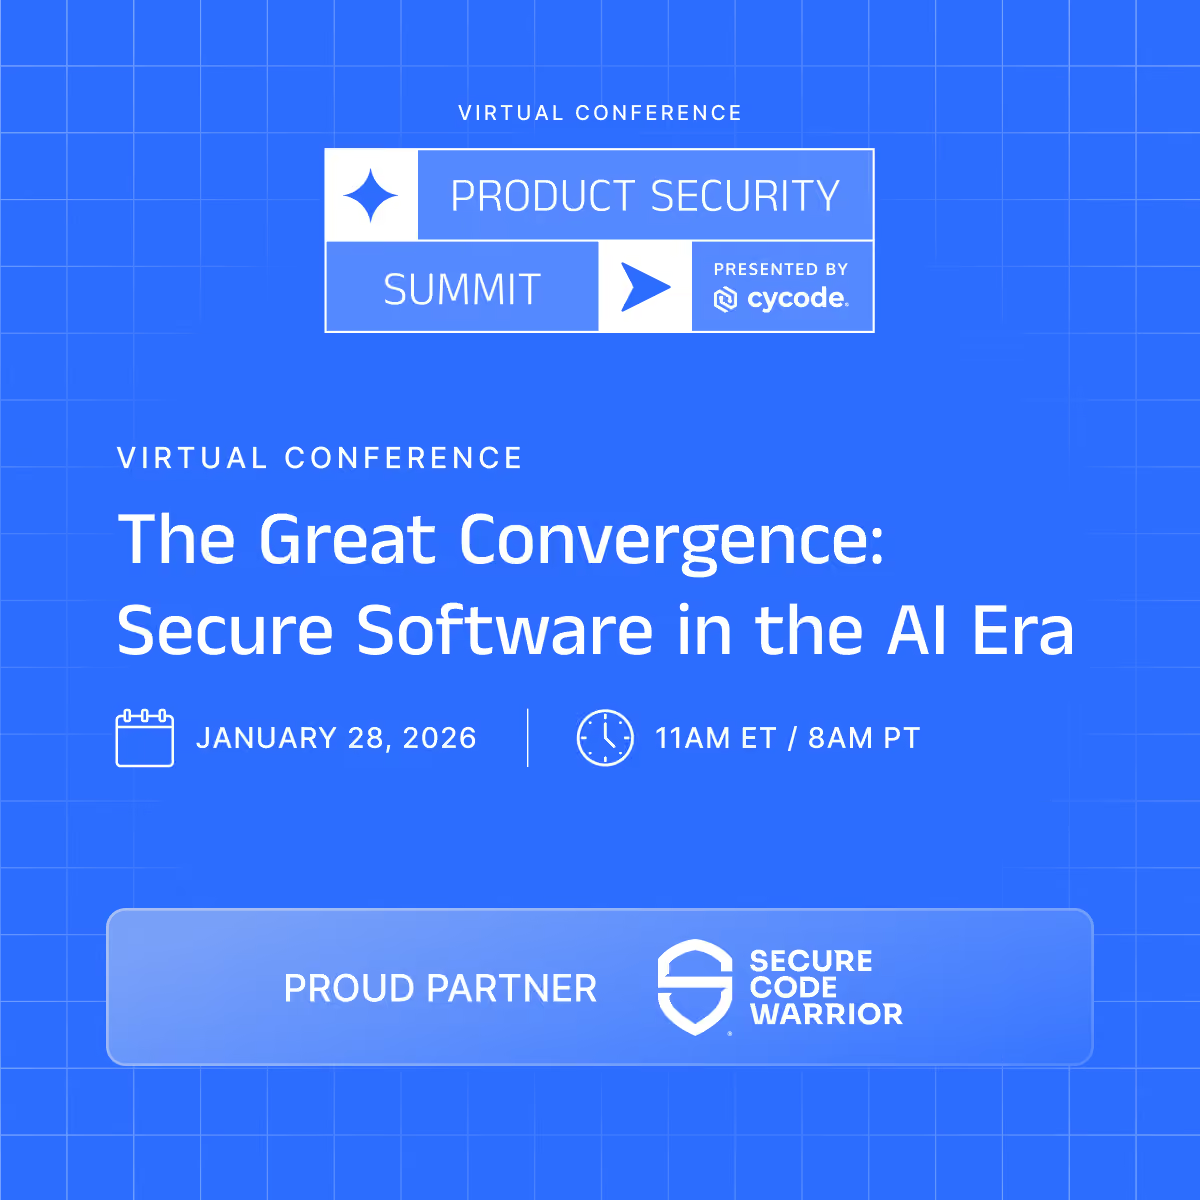
プロダクトセキュリティ・バーチャルサミット
今年1月28日に開催されるプロダクトセキュリティ・バーチャルサミットで Cycode とパートナーシップを組むことを誇りに思います。AI 時代のソフトウェアの未来を探ります。

フィッシャパルーザ (Phishapalooza)
アメリカがん協会を支援するため、第18回年次 Phishapalooza に参加できることを光栄に思います。アイスフィッシングや資金調達活動を楽しみにしております。
OWASP LASCON
テキサス州オースティンで開催される OWASP LASCON 2026 のゴールドスポンサーであることを誇りに思います!ノーリス・コンファレンス・センターでお待ちしております。

ニューヨーク・セキュアコード・ショーダウン
SCW、OWASP、AWS は、2026年2月19日(木)に開催されるニューヨーク・セキュアコード・ショーダウンに皆様を招待します!

ゴールドコースト BSides
オーストラリアのゴールドコーストで開催されるハンズオンコンペティションで、実際の脆弱性を特定・修復する能力をテストしましょう。
BSides フランクフルト
フランクフルトのゲーテ大学キャンパスで開催されるハンズオンコンペティションに参加し、実際の脆弱性を特定して修正する能力を試してみましょう。
RSA カンファレンス
RSA Conference 2026 に向かっています。開発者が最初からセキュアなコードを書くスキルを支援します。サウスエキスポホールのブース #250 でお会いしましょう。

FS-ISAC FinCyber Today カナダ
FS-ISAC FinCyber Today カナダで開発者リスク管理についてお話する準備ができています。開発者のセキュアコード学習を強化してリスクを軽減します。
Threat Modelling with AI: Turning Every Developer into a Threat Modeler
Threat modeling with AI: how to turn every developer into a threat modeler, straight from their IDE.

開発者の特定
カリキュラムおよびオンボーディングマネージャーの Katelynd Trinidad が、コードコントリビューターを特定してセキュアコードトレーニングを受けさせるための手法を紹介します。

AppSec DevSec DevSecOpsにおけるブランドの力(頭字語の意味とは!?)
AppSecにおいて持続的なプログラムの成果を上げるには、単なる技術以上のもの、つまり強力なブランドが必要です。力強いアイデンティティは、取り組みが共感を呼び、開発者コミュニティ内での持続的な参加を促進します。

Vibe Coding:AI時代に合わせてAppSec戦略を適合させる実践ガイド
実用的なトレーニング優先のアプローチにより、AppSecマネージャーが障害ではなくAI推進者となる方法をオンデマンドでご視聴ください。AIコーディングアシスタント時代において、Secure Code Warrior(SCW)を活用してAppSec戦略を戦略的に更新する方法をご紹介します。

アジャイル学習で開発者リスクを管理するための CISO ガイド
ESG の最近の研究では、回答者の 54% が既知の脆弱性を持つコードを本番環境にリリースしていると述べています。学習プログラムはリスクを減らしていますか?

Secure Code Warrior & GuidePoint Security
Come visit our booth #336 at SecTor 2025 in Toronto at the Metro Toronto Convention Centre! Us along with other security professionals will be sharing our latest research and techniques on underground threats and corporate defenses.

OWASP ニュージーランド・デイ
オークランド大学キャンパスで開催される OWASP ニュージーランド・デイに参加できることを嬉しく思います!堅牢なアーキテクチャに焦点を当てています。

OWASP グローバル AppSec 2025 USA
ワシントンDCの中心部にあるマリオット・マーキスのエキスポスペースでお待ちしております!800人以上の専門家とつながるチャンスです。

OWASP ベネルクス・デイズ
ベルギーで開催される OWASP BeNeLux Days のブースにお越しください!セキュリティ、DevOps、クラウドの専門家による技術トークを提供します。
メルボルン AppSec & DevSecOps サミット
メルボルン AppSec & DevSecOps サミットで、セキュリティや開発リーダーの皆様とアイデアを共有できることを楽しみにしています!
FS-ISAC 秋季サミット
10月7日(火)午前8時より FS-ISAC 秋季アメリカサミットの朝食会ブースにお越しいただき、デザインによるセキュリティについて語り合いましょう。

CISO Inspired サミット アメリカ
CISO Inspired Summit New York 2025 でサイバーセキュリティリーダーとつながり、積極的な防御戦略を掘り下げましょう。

CISO Inspired サミット イギリス
CISO Inspired Summit UK 2025 でサイバーセキュリティリーダーとつながり、デジタル防御を強化し、堅牢な戦略を構築しましょう。

BSides ボーンマス
BSides Bournemouth はコミュニティ主導のサイバーセキュリティ会議です。洞察に満ちた講演やハンズオンアクティビティをお楽しみください。

Black Hat USA
ラスベガスの Mandalay Bay で開催される Black Hat USA で当社役員陣にお会いください!AI/LLM セキュアコードリスクについて話し合えることを楽しみにしています!

OWASP グローバル AppSec ヨーロッパ 2025
OWASP Global AppSec EU のブース #G08 で、デザインによるセキュリティ原則と効果的なリスク管理が次世代サイバーセキュリティをどう形成するかをご覧ください。
FS-ISAC EMEA サミット
5月21日午前8時より FS-ISAC EMEA サミットの朝食会ブースにお越しいただき、デザインによるセキュリティと開発者中心のリスク管理について語り合いましょう。
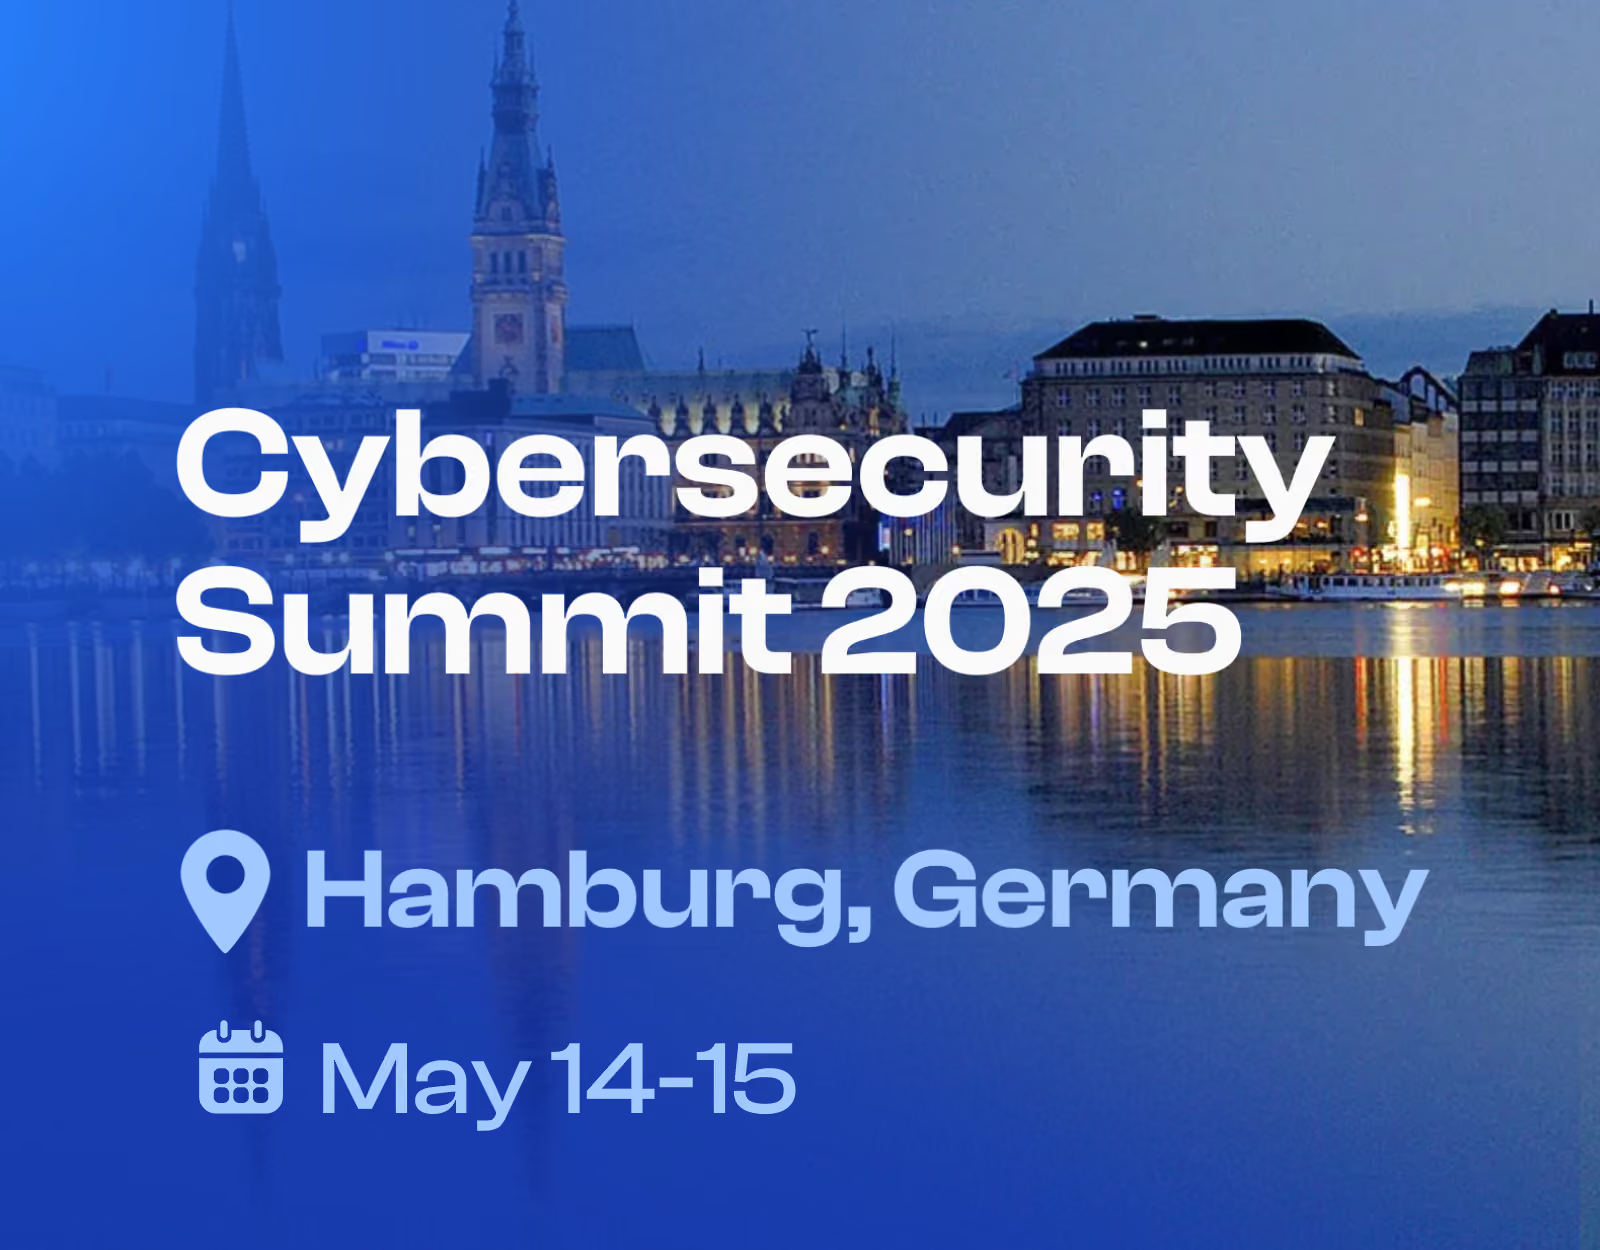
サイバーセキュリティ・サミット、ハンブルク
予防的セキュアコーディングがセキュリティ体制を向上させながらソフトウェア開発を加速する方法について話し合いましょう。

OpenText サミット・マドリード
Secure Code Warrior は4月10日に開催される OpenText Summit Madrid 2025 を後援することを誇りに思います!リーダーが集まり変革を探ります。
オーストラリア・サイバー・エクスチェンジ (ACE25)
4月3日、CEO の Pieter Danhieux が第1回オーストラリア・サイバー・エクスチェンジ ACE25 で登壇し、オーストラリアのサイバー能力強化について語ります。

セキュリティのシフト左:ソフトウェア開発における DevSecOps の不可欠な役割
このウェビナーでは、DevSecOps の非常に重要な役割と、開発ライフサイクルの初期段階でセキュリティを統合する戦略について掘り下げます。

OWASP SnowFROC
デンバーのプレミアアプリケーションセキュリティ会議 SnowFROC '25 にご参加ください!約400人が集まるこの1日イベントで最高の体験を。

BSides リンブルフ
今年の3月14日に BSides リンブルフでトーナメントを開催します!深い議論、ハンズオンデモ、コラボレーションを促進するイベントです。
第2回 2025年 OWASP メイン州セキュアコーディングトーナメント
OWASP メイン州と Secure Code Warrior が提携し、第2回 OWASP メイン州セキュアコーディングトーナメントを開催します!初心者からシニアレベルまで、すべてのソフトウェア開発者とAppSec専門家を歓迎します。

NDC Security 2025
オスロの中心部で最先端のトピック、ハンズオンワークショップ、ピアネットワーキングに飛び込みましょう。スポット H でお待ちしております!

RSA カンファレンス 2025
RSAC 2025 のブース #2353 にぜひお越しください。革新的なソリューションを探索し、会話に参加してください。

DevSecOps360 ロンドン
2025年1月22日(水)、IBM Innovation Studio ロンドンで開催されるパートナーエコシステム内の DevSecOps 統合ビジョンイベントにご参加ください。

Black Hat Europe
ロンドンの ExCeL で開催される Black Hat Europe にご参加ください

OWASP ベネルクス
SCW は今年のカンファレンスをサポートできることを誇りに思います。ブースにお立ち寄りいただき、OWASP Top 10 を克服する方法をご覧ください。

ジャーマン OWASP デイ 2024
ドイツのライプツィヒで Secure Code Warrior とともに OWASP からの素晴らしい洞察や2025年のソフトウェアセキュリティの方向性を共有しましょう。

DevSecOps 360 トロント
SCW、IBM、Black Duck、Iruis Risk、Contrast に参加して、組織が脆弱性を最小限に抑えながら開発を加速する方法を学びましょう。

クラウド & サイバーセキュリティ エキスポ、パリ
フランスにおけるプレミアサイバーセキュリティイベントのシルバースポンサーを務めることを嬉しく思います。会場でお会いできるのを楽しみにしています。

OpenText World 2024
Secure Code Warrior と OpenText に参加して、世界中の企業が SAST 結果を活用してセキュアコーディングのアジャイルな学習体験を生み出す方法を学びましょう。
DevSecOps 360 ロンドン
SCW、IBM、BlackDuck、IriusRisk に参加して最新の統合を体験し、企業が組織の生産性をいかに実現したかを学びましょう。

AppSecDay ストックホルム
Secure Code Warrior、OpenText、Sonatype とともに、オープンソースのナビゲーション、NIS2への準拠、AIとDevSecOpsに関する議論にご参加ください。
DevSecOps 360 ミラノ
自動化がより迅速で安全な開発を推進する方法をご紹介します。脆弱性を減らすための実践的なソリューションに飛び込みましょう。

チャリティ プロアマ スクランブル
KidSport Québec を支援し、より多くの子供たちがスポーツに参加できるよう、素晴らしい目的のためにゴルフ大会を開催します。
AppSec Day ユトレヒト
アプリケーションセキュリティが進化するにつれ、組織はリアルタイムの脅威検知と予防のために AI ソリューションをますます統合しています。Secure Code Warrior とパートナーにご参加ください!

Secure Code Warrior ユーザーグループ EMEA
他の管理者とつながり、開発者主導のセキュリティプログラムの管理方法を学ぶコミュニティです。ヒントやコツを学びましょう!

SANS Secure ジャパン 2025
SANS が2月17〜22日に東京にやってきます。ブースにお越しいただき、当社の最先端 AppSec ソリューションと学習プラットフォームをご覧ください。

OWASP 2024 グローバル AppSec
Global AppSec US カンファレンスは新しいトレンドで盛り上がります。サンフランシスコのブースで最新製品のデモをご覧ください。

DevSecOps トランスフォーメーション
DevSecOps により、開発ライフサイクルの初期段階でセキュリティ問題を特定し、最も大きな影響を与える開発者に直接提示できます。

サイバーセキュリティ・サミット
ビジネス向けサイバーセキュリティのデジタルソリューションを提供する革新的なプロバイダーと専門家が結集します。

Blackhat USA
27年目を迎える Black Hat USA がラスベガスに戻ってきます。選りすぐりのブリーフィング、オープンソースツールのデモ、ビジネスホールなどが用意されています。

AppSec & DevSecOps サミット
メルボルン AppSec および DevSecOps サミット 2024 でセキュリティ戦略を統合し、強化しましょう。セキュリティスキルを高め、アプリケーションとクラウドセキュリティの革命の最前線に立ちましょう。

SCW Trust Score でセキュリティプログラムの現状をベンチマーク
急速に変化するセキュリティ環境において、セキュリティプログラムの立ち位置を理解することは極めて重要です。CTO Matias Madou とともに SCW Trust Score について話し合いましょう。

ノーディック IT セキュリティ
スカンジナビアで最も評判の高いサイバーセキュリティサミットである Nordic IT Security は、17年間にわたり地域のナビゲーション役を務めています。

ベルギー・コーヒーアワー
ベルギーからの RSAC 参加者のために、3月7日(火)午後3時より特別イベントを開催します。CEO Pieter Danhieux や CTO Matias Madou とともに素晴らしいコーヒーを楽しみましょう。

2026年のセキュリティ・チャンピオン:高め、関与させ、保護する
新規プログラムの立ち上げ、既存プログラムの拡張、あるいは機能の探求を目的としている場合でも、このウェビナーは実践的な洞察を提供します。

SANS ネットワークセキュリティ 2026
9月10〜15日にラスベガスで開催される SANS Network Security 2026 にご参加ください。最新の課題に焦点を当てた実践的なセッションを提供します。

RSA カンファレンス 2024
可能性の芸術がここにあります!ブース 5179 にお立ち寄りいただき、脆弱性を53%削減する方法をご覧ください。

RSAC24 で SCW 経営陣と面談
当社の共同創業者と役員陣が5月6日〜7日にサンフランシスコ最高のコーヒーを楽しみながらミーティングを行います。

開発者と AI を信頼する
SCW Coffee Shop @RSAC24提供:共同創業者兼 CTO Matias Madou と業界の専門家が、開発者内でのセキュリティスキル測定の課題について語ります。

SCW Trust Score でセキュアコーディングプログラムの有効性を定量化する方法
SCW Coffee Shop @RSAC24提供:Patrick Collins と Junie Dinda とともに、セキュアコーディングプログラムの風景を再定義する新しい SCW Trust Score を深掘りします。

Carolina Hurricanes と GuidePoint
GuidePoint のパートナーとともにアイスホッケーの試合と AppSec のトークを楽しみましょう!

ベイエリア・ベンダー・ハッピーアワー
詳細情報はまもなく公開されます。

セキュリティにおける女性リーダー
SCW Coffee Shop @RSAC24提供:共同創業者兼CCOのFatemah Beydounと業界の女性リーダーのパネルに参加し、セキュリティにおけるジェンダーギャップを修正するためのシフト左について話し合います。
コーディングに生成AIを使用することの良さ、悪さ、そして醜さ
このウェビナーでは、Secure Code Warrior CTO 兼共同創業者の Matias Madou とセキュリティ研究者の Jon Helton が力を合わせて生成AIを解読します。
スコシアバンク・アリーナ プライベートスイート
スコシアバンク・アリーナのプライベートスイート体験にご参加ください!排他的な環境で試合を観戦しながら AppSec について語り合いましょう。
アプリケーションセキュリティ・ハンズオンワークショップ
AWS、Contrast Security、Arctiq とのパートナーシップにより、インタラクティブなハンズオン AppSec ワークショップをお届けします。

バーチャルワインテイスティング - オハイオ
GuidePointやその他のパートナーとともに、Silver Oaks Wineryのバーチャルワインテイスティングにご参加ください。
DevSecOps 360 - リヤド
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
DevSecOps 360 - ミュンヘン
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
DevSecOps 360 - ドバイ
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
シフト左テスティング
脆弱性を早期に検出し、修復を加速します。SCW、Cyberark、Checkmarx は一貫したシフト左アプローチで提携しています。
次世代の保護:AIコーディングの脆弱性に正面から立ち向かう
AI の登場はソフトウェア開発の風景を変えました。しかし、これは新たな課題ももたらします。AI は単にコードを書くのではなく、脆弱なコードを書きます。
人工知能時代におけるセキュアコーディング
AI がコード生成を加速する中、堅牢なセキュリティを維持することはかつてないほど重要です。AI 開発の敏捷性とセキュアコーディングのバランスを探る炉辺対談。
Secure Code Warrior ユーザーグループ NA
他の管理者とつながり、開発者主導のセキュリティプログラムの管理方法を学ぶコミュニティです。ヒントやコツを学びましょう!
Secure Code Warrior ユーザーグループ
Secure Code Warrior ユーザーグループへようこそ!製品アップデート、刺激的な顧客の成功事例、インタラクティブなパネルディスカッションをお届けします。
SANS クラウドセキュリティ・トレーニング
SANS クラウドセキュリティ・トレーニングが4月13〜18日にバージニア州アレクサンドリアにやってきます。集中的な実践トレーニングが行われます。
DEVOPS カンファレンスに参加しましょう
3月8〜9日に開催される DEVOPS カンファレンスに参加し、洞察力に満ちた話を聞き、トーナメントに参加するチャンスを手に入れましょう!今すぐ無料チケットを獲得。
セキュリティは開発者の問題か?
テクノロジーが爆発的に増加し、そのすべてを保護する必要があります。しかし、セキュリティチームには急速な進化に対応する人手が不足しています。
包括的な開発者主導のセキュリティでソフトウェアリリースのスピードを向上
AWS + Secure Code Warrior が開発者のコード出力の量と質を高めることの重要性について解説。

包括的な開発者主導のセキュリティでソフトウェアリリースのスピードを向上
悪用可能な脆弱性に起因するセキュリティ侵害が増加する中、組織はリスクを最小限に抑え、リリース速度を高める方法を模索する必要があります。
オープンソースコンプライアンスにおける回避と修復のギャップを埋める方法
このギャップを埋めることは、エンジニアリングチームがオープンソースソフトウェアの影響をよりよく理解するために重要です。

強固な基盤を持った AppSec プログラムの構築方法
AppSec プログラムの戦略開発においてベースラインを設定することの重要性とアプローチ。

Isn’t it time we elevated the humble SBOM?
Business leaders need to make room for SBOMs as a priority, especially with so much change in the air for vendors and their ownership of security. However, while we’re at it, perhaps we need to look at how they can be improved going forward.

明らかに:企業におけるアジャイル学習と開発者主導のセキュリティを強化するためのエキサイティングなパートナーシップ
シリーズCの資金調達の発表を終えたばかりですが、当社の歩みにおける新たな一歩を発表できることを嬉しく思います。セキュリティ業界のリーダーであるシノプシスは、製品スイートにエキサイティングな新製品を追加しました。それは、セキュア・コード・ウォリアーによるシノプシス・デベロッパー・セキュリティ・トレーニングです。

すぐに使えるコード:安全な開発者が制限なくリリースできる理由
重要なインフラストラクチャ、自動車、医療技術、その他すべてを支えるコードに取り組むほとんどの開発者が、最初にセキュリティ能力を検証せずにそうしているのは不可解に思えます。一方で、物を安全に構築する方法を理解していることを繰り返し証明してきたセキュリティスキルのある開発者が、すべてのセキュリティゲートが原因で、常に速度が遅くなる開発パイプラインで他の開発者と一緒に列に並ぶ必要があるのはなぜでしょうか。

アジャイル・ラーニング・プラットフォームのROI
コードの脆弱性や技術的負債に対処するためのコストは高額であり、ソフトウェア開発チームの生産性を低下させ続けています。セキュアコードのためのアジャイル学習プラットフォームを実装することで、SDLCの早い段階で脆弱性を修正し、そもそも脆弱性を未然に防ぎ、大幅なコスト回避につながるセキュアコーディング技術について開発者をより効果的にトレーニングする方法をご紹介します。このブログでは、アジャイル学習プラットフォームの財務的影響と ROI について考える方法を概説しています。

安全なコーディングの水準を引き上げる:将来を見据えた企業へのアジャイル学習の導入
シリーズCの資金調達ラウンドの終了を発表しました。これにより、より多くの先駆的な組織が共通の脆弱性を阻止するために開発コホートの力を活用できるよう支援するという私たちの使命の次の段階に向けて、5,000万米ドルを調達しました。

I guess this is growing up: Coming of age with CISA’s Secure-by-Design Guidelines
The recently released National Cybersecurity Strategy signals the need for a seismic cultural shift for most companies, with the most glaring recommendation coming in the form of security accountability falling primarily on software vendors. This is a positive step, though it is sure to cause teething problems, especially as many organizations struggle to accurately assess their security maturity across the board, particularly among the development cohort.

安全なコードのためのアジャイルラーニングで開発者を魅了する方法
安全なコードのためのアジャイル学習プラットフォームを開発者のワークフローやツールに組み込む方法を学び、安全なコード学習の文化を築き始めましょう。

PCI-DSS 4.0は思ったより早く登場し、組織のサイバーレジリエンスを高める機会となります
今年初め、PCIセキュリティ標準委員会はペイメントカード業界データセキュリティ標準(PCI DSS)のバージョン4.0を発表しました。組織は 2025 年 3 月まで 4.0 に完全に準拠する必要はありませんが、今回の更新はこれまでで最も大きな変革をもたらし、ほとんどの企業が複雑なセキュリティプロセスや自社の技術スタックの要素を評価 (そして場合によってはアップグレード) する必要があります。これに加えて、ロールベースのセキュリティ意識向上トレーニングや、開発者向けの定期的なセキュア・コーディング教育も実施することになります。

トレーニングからアジャイル学習まで:セキュアコードのためのアジャイル学習プラットフォームがセキュアソフトウェアへのアプローチに革命をもたらす方法
SDLCの左から始めることで、安全なコードのためのアジャイル学習プラットフォームがどのように開発者のスキルアップ、リスクの軽減、技術的負債の軽減につながるかを学びましょう。

組織階層におけるソフトウェアの再考
アプリとソフトウェアの責任を厳密な階層の中で定義し、それらのポリシーを最小限の権限で適用できるようにすることで、さまざまな脅威環境があってもアプリやソフトウェアが存続し、繁栄できるようにすることができます。

プロアクティブな保護:高度な脅威防止のための国家サイバーセキュリティ戦略の活用
CISAの国家サイバーセキュリティ戦略は、ソフトウェア標準を全面的に引き上げ、最終的にはセキュリティスキルのある開発者の新時代の到来を告げる絶好の機会です。

MVC リクエストマッチャースプリングのブリュネズシュート
2023 年 3 月 20 日、2008 春春サクラン、VIN838で838性 CVE-2023-20860 始業者の皆さん。「MVCMatcher」Spring Devendesai、olunginafefea。セキュア・コード・ウォリアーズ(Secure Code Warrior2008)で、MVC リクエストマッチャーズ(Secure Code Warrior Warrior Warrior Warchers)

Secure Code WarriorのCEO兼共同創設者であるPieter Danhieux氏は、「誰もがサイバーセキュリティにおける自分の役割を理解し、受け入れるべきだ」と述べています。
セキュア・コード・ウォリアーのCEO兼共同創設者であるピーター・ダンヒュー氏によるサイバーニュースに関する質疑応答

SDLC における生産性の向上とコスト削減のカギ
ソフトウェア開発ライフサイクルにおける最大のギャップの1つは、開発者がコードの保護方法を最初から学ぶ時間がないことです。開発者は手直しや修正に数え切れないほどの時間を浪費し、その結果、何百万ドルもの機会損失が発生しています。セキュアなコーディングを迅速に行うことで、こうしたギャップを埋め、生産性を向上させる方法をご紹介します。
セキュア・コード・ウォリアーの新機能:コースガイドライン、参加管理、新コンテンツ
Secure Code Warriorの新機能:コースを管理する新しい方法を体験し、追加コンテンツを探索してください。

メタバースにおける悪意:新たなフロンティアにおける既知のサイバー脅威との戦い
現在のデジタル最愛の要素であるメタバースの出現により、コードレベルの脆弱性とソーシャルエンジニアリングの両方に新たな攻撃対象領域が加わりました。そして、私たちは煙と鏡の上で繁栄するこの新しい競争の場での戦いに備えていないだけです。
開発者主導のセキュリティによる技術的負債の軽減
安全でないコードとその後の技術的負債に対処するためのコストは、今日のテクノロジーが直面している最大の障害の1つです。スケーラブルで安全なコードトレーニングプログラムを実装することで、不適切なコーディングパターンに対処し、ソフトウェア開発サイクルの早い段階で脆弱性を検出することで、技術的負債を減らすのにどのように役立つかをご覧ください。

開発者は「セキュアコーディング」をどのように定義していますか?
何がセキュアコーディング行為を構成するのかという認識については、議論の余地があります。Evans Dataと共同で行った最近の調査によると、この感情は白黒で明らかになっています。開発者主導型セキュリティ2022の現状調査では、1,200人のアクティブな開発者の主要な洞察と経験を掘り下げ、セキュリティ分野における彼らの態度と課題を明らかにしています。

Coding Labs: Hands-on secure code for Developers
Learn how Coding Labs is like a personal trainer for developers- utilizing interactive, hands-on modules and intuitive feedback within a convenient in-browser IDE to help developers go from learning to doing faster than ever before.
ゆーあコ・ウ・イイハー8歳分:産毛車中
今週、treux-a・ウォアーの8周年という祝福の日。どうも、このアフロ11の350倍の時間、45,000ウォット、またはろろくろパロプスイーイと5696回輪輪輪輪輪輪輪輪輪輪車。他人、ジャイ・タイ・サスの福301(新生、250年)。グラプラズズズズスイブラ、ププシーラー、レヴニオン、教訓、大金大人、.、、、

2022年を振り返る-セキュア・コード・ウォリアーを最大限に活用するのに役立つハイライト、新しいイノベーション、リソース
Secure Code Warriorでは、開発者や組織が今日の絶え間なく変化するセキュリティ課題に取り組むための適切なスキルを身に付けることができるように、常に革新を続けています。ソフトウェア開発サイクルの開始時に、開発者主導のセキュリティを通じて組織がソフトウェアを保護できるように、プラットフォームの主な機能と更新、および今年公開されたリソースとガイドラインをまとめました。

開発者主導型セキュリティのROI
テクノロジースタックや追加のトレーニングプログラムへの投資に関しては、誰もが投資収益率を高めたいと考えていますが、セキュリティに関しては、単純な ROI の計算にとどまらない長い時間をかけて取り組む必要があります。開発者が主導するセキュリティに投資することで、高額な情報漏えい、生産性の低下、蓄積された技術負債の費用を節約できるだけでなく、今日の脅威環境の一歩先を行くための積極的で費用対効果の高い戦略を構築する方法を学びましょう。

開発者主導のセキュリティに対するまとまりのあるアプローチの確立
多くのトップ企業や政府機関を含む人気のOrion管理ソフトウェアの18,000人以上のユーザーにソフトウェア更新プロセスを利用して感染させたSolarWindsキャンペーンのような大規模なセキュリティ侵害への対応として、開発者主導のより効果的なセキュリティ対策を求める声が高まっています。あらゆる規模の組織が、自社の「ソフトウェアサプライチェーン」に疑問を持ち始めており、ソフトウェアを開発する開発者には検証済みのセキュリティスキルと知識を持っていることを求めています。
SCW 統合:マイクロラーニングによる平均修復時間の短縮
堅牢な技術スタックの重要性は誰もが知っています。コード内の脆弱性の発見と修正に関しては、平均修復時間を短縮し、信頼できる堅牢なソリューションを使用することが、Secure Code Warriorの統合の目標です。マイクロラーニングの瞬間を開発者のワークフローに統合することが、より良い学習と迅速な修復の鍵です。

繰り返し使える安全なコーディングスキルで左にシフトし、コンプライアンスを達成
最近のほとんどすべての開発者チームは、企業が業界の枠組みや政府規制の範囲内にとどまっていることを確認するために使用される最初の認定プロセスの一部であるか、年次要件またはレビューの一部であるかにかかわらず、何らかの形のコンプライアンストレーニングを採用しています。これは重要なステップです。なぜなら、組織が基本的なコンプライアンス要件を満たせなければ、その従業員は現実的に職務を遂行できないからです。

不適切なコーディングパターンは大きなセキュリティ問題につながる可能性があります... では、なぜ私たちはそれらを奨励するのでしょうか?
開発者は、脆弱性の仕組み、なぜ危険なのか、どのようなパターンが脆弱性を引き起こすのか、どのような設計やコーディングパターンが脆弱性を修正するのかを理解していなければ、脆弱性の軽減にプラスの影響を与えることはできません。足場型のアプローチにより、知識を重ねることで、安全にコーディングすることの意味の全体像を把握し、コードベースを守り、セキュリティを意識した開発者として立ち上がることができます。

Secure Code Warriorがガートナーの「ソフトウェアエンジニアリングのクールベンダー:開発者の生産性の向上」に選ばれました
開発者のセキュリティスキルの重要性は、2022年のガートナー社の「ソフトウェアエンジニアリングにおけるクールベンダー」で強調されています。詳細を読み、レポート全文を入手してください。

セキュアコードの定義
定番組、プロ、プラ、プラ、コープサン、懐かしくなった、ぎょうwebサイト&noldg&nold&nold&gula、()
Pythonのtarfile モジュールパトラバーサバグキンクー
きょう、パシフィックパークは、Pythonのタータールグラダに15年前のおかしい。2007 年秋新聞、CVE-2007-4559 まで。Python のリビングニニニニププププサダママス。

SCW 新型:サボボ、LMS VAPYなど
セキュア・コード・ウォリアー新型:コーディング・ラボでクンフククニニニニセセセセセコード・ウォリアー新型、コードミスターと合成。

ハードコードされた認証情報はセキュリティリスクを招く可能性があります
ハードコーディングされた認証情報やソーシャルエンジニアリングに関連するリスクについて、Uber の最近のセキュリティインシデントや、組織が左にシフトして開発者が安全なコーディングのベストプラクティスを常に把握しておくことがなぜそれほど重要なのかを説明しているので、詳細をご覧ください。

攻撃対象領域が終わらない時代における防止
ソフトウェア開発はもはや孤島ではなく、クラウド、電化製品や車両に組み込まれたシステム、重要なインフラストラクチャ、すべてをつなぐAPIなど、ソフトウェアを原動力とするリスクのあらゆる側面を考慮すると、攻撃対象領域は境界がなく、制御不能になります。

私たちはオープンソース・ソフトウェア・セキュリティ・モビリゼーション・プランに向けて十分に成熟していますか?
オープンソース・ソフトウェア・セキュリティ・モビリゼーション・プランは、開発者主導のセキュリティにとって前向きな一歩です。しかし、私たちは皆、最新かつ最高の防御戦略を実装するのに十分なほど組織内で成熟しているかどうか、そして開発チームが適切なレベルのセキュリティ意識とスキルを持っているかどうかを評価し、正直に評価する必要があります。

開発チームにおけるセキュリティ成熟度の重要性
左にシフトする取り組みには、開発チーム内でセキュリティの知識とスキルを集団的かつ継続的に改善する必要があります

API の保護:ミッションは不可能?
API セキュリティは厳しいものですが、十分なトレーニング、計画、ベストプラクティスへの注力があれば、どんなに厄介な脆弱性でも軽減できます。

新規:Okta ワークフロー用 SCW コネクタ
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

セキュア・コード・ウォリアーの新機能:2022年5月
より簡単でパワフルなコース作成フロー、早期アクセスの切り替え、SAP ABAPトレーニングコンテンツ

新規:ABAP トレーニングコンテンツを使用して、安全な SAP ABAP コードをより迅速に発送
ABAP開発者向けの実践的かつ効果的なセキュア・コーディング・トレーニング。
サイキック・シグネチャー-知っておくべきこと
Psychic Signatureの脆弱性は、認証などの重要なタスクでシステムを保護するECDSA署名の暗号にあります。この脆弱性により、ハッカーはあらゆる署名チェックを回避できます。この投稿では、その内容と軽減方法について説明します。

NGINX および Microsoft Windows SMB リモートプロシージャコールサービスにおけるソフトウェアの脆弱性を未然に防ぎましょう
最近、NGINXはゼロデイ脆弱性を公開しました。同じ頃、マイクロソフトは Windows RPC RCE の脆弱性というもう 1 つの重大な脆弱性を公開しました。この投稿では、この 2 つの問題が発生するリスクに誰がさらされているのか、またそのリスクを軽減する方法について説明しています。

ゼロデイ攻撃が増加しています。今こそディフェンシブエッジを計画する時です。
ゼロデイ攻撃は、当然のことながら、攻撃者が最初に侵入するため、開発者が悪用される可能性のある既存の脆弱性を発見してパッチを適用する時間がまったくありません。被害が発生したら、ビジネスに対するソフトウェアと評判の低下の両方を修正しようとすると、狂ったような争いが繰り広げられます。攻撃者は常に有利な立場にあり、そのエッジをできる限り塞ぐことが重要です。

セキュアコードは開発チームの優先事項のリストのどこにありますか?
2年目となる今回は、Evans Data Corp. と提携して、セキュアコーディング手法に関するスキル、認識、行動、およびそれらがソフトウェア開発ライフサイクル(SDLC)に与える影響と関連性について、世界の開発者コミュニティを対象に包括的な調査を実施しました。結果は多くの点で非常に驚くべきものでした。

Springライブラリの新しい脆弱性:危険にさらされているかどうかを知る方法と対処方法
最近、Java コミュニティで最も人気のあるライブラリの 1 つである Spring ライブラリが、リモートコード実行 (RCE) に関連する 2 つの脆弱性を公開しました。「Spring4Shell」と「Spring Cloud Function」の既知の詳細を分類して、リスクにさらされているかどうか、またリスクにさらされている場合の対処方法を理解しやすくしました。

2022年に無視できないサイバーセキュリティ問題
サイバー犯罪者との戦いに関しては、予防的な考え方でサイバー犯罪者の遊び場を先取りし、できる限り彼らと歩調を合わせる必要があります。来年、彼らが波を起こし始めるかもしれないと思うのは次の点です。

トロイの木馬ソースとは何か、そしてどのようにソースコードに侵入するのか
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

チャンピオン対コーチ:すべての開発チームに両方が必要な理由
サイバーセキュリティアプローチで目標を掲げている企業の多くは、公式のセキュリティチャンピオンプログラムを実施し、そのような役割に適性と情熱を示す個人に、チーム間の連絡や一般的なチアリーディングからベストプラクティスの監督まで、主要なセキュリティ責任を課しています。
つなつや Java ミミミロリとぐぐる
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

セキュア・コード・ウォリアーに7年間携わり、それが現実味を帯び始めている
私たちの誕生日のマイルストーンは、私たちの努力の成果を振り返り、チームを祝い、自信を持って次の年に取り組むことを思い出させる素晴らしい機会です。そして、設立から7年が経過した今、私は疑問に思っています。私たちはそれを成し遂げたのか?これはもう本物の会社なの?もちろん、成熟には至りましたが、創業以来持っていた好奇心、情熱、マニアックさを決して失わないことを願っています。

足場型学習がセキュリティに強い開発者を育てる理由
業界として、開発者がセキュリティの専門家になることを期待すべきではありませんが、組織はより高品質のソフトウェアを作成できるように、開発者支援のための新しい標準を採用することができます。

Log4jの近親相-v788とその近く
2021 年 12 月、Java ライブラリー Log4j に性 Log4Shell の公開日。有、Log4Shell の銀種種種

サイバーセキュリティ業界分析:繰り返し発生しているもう 1 つの脆弱性
現代のサイバーセキュリティという絶え間ない猛攻撃に対抗するための現実的なアドバイスも、最速の解決策も得られていません。もちろん、侵害はそれぞれ独自の方法で異なり、脆弱なソフトウェアに悪用される可能性のある攻撃ベクトルは数多くあります。実行可能な一般的なアドバイスは限られていますが、ベストプラクティスのアプローチは、時間ごとに欠陥が増えていくものです。

セキュリティプログラムはインシデント対応に重点を置いていますか?あなたのやり方は間違っています。
事後対応型ではなく予防型のアプローチに重点を置くことは、特に大規模で重大なセキュリティインシデントが発生していない場合、セキュリティチーム以外ではあまり理解されない可能性があります。
Make unit tests readable with Sensei and AssertJ
Implement unit test coding guidelines uniformly and consistently

API on Wheels: リスクの高い脆弱性のロードトリップ
API セキュリティを偶然に任せることは、後で問題を起こす確実な方法であり、最悪の場合は壊滅的な結果を招き、やり直しはイライラさせられ、せいぜいパフォーマンスが低下します。

ジョダ・タイムからjava.timeへのマイグレーション
Joda-Time を便利な方法で java.time に移行する方法

政府のサプライチェーンパイプラインにおけるサイバー脆弱性の覆いを解く
サイバーセキュリティが重要であることは明らかですが、サプライチェーンの観点から見ると、サイバーセキュリティは実際には何を意味するのでしょうか。

セキュリティ意識の高い開発者:AppSecにはあなたが必要です!
開発者は、AppSecに有利な形で参入できる絶好の立場にあります。


開発者にインセンティブを与えることは、より良いセキュリティ慣行の鍵です
プロの開発者はDevSecOpsを採用して安全なコードを書きたいと考えていますが、その取り組みを拡大したいのであれば、組織はこの大きな変化をサポートする必要があります。

最近の Apache の問題の原因となったパストラバーサルの脆弱性の影響を体験してください
10月の初めに、Apacheはパストラバーサルとリモートコード実行の脆弱性を修正するバージョン2.4.49をリリースし、修正が不完全だったという事実に対処するバージョン2.4.50をリリースしました。私たちは、現実の環境におけるリスクを実証するという使命を掲げました。今すぐ試してみてください。

Warrior Insider: Nelnet-セキュリティチャンピオンを育成し、内部から安全な開発を行う文化を築きましょう
Micha Martinezは、Nelnetのサイバーセキュリティアナリスト兼撮影監督です。セキュアコーディングに関する開発者向けトレーニングプログラムの作成を任されたとき、彼はチームを巻き込むための創造的な方法を採用しました。彼がどのようにセキュアコードトレーニングプログラムを運営しているかに感銘を受けたので、私たちは彼に話を聞いて詳細を学びました。

OWASPの2021年リストシャッフル:新しいバトルプランと主な敵
悪名高い脆弱性の王様であるインジェクション攻撃(カテゴリー別)は、アクセス制御の破れによる最悪の攻撃としてトップの座を失っており、開発者は注意が必要です。

高度なセキュリティインテリジェンス:開発者がNISTに対応できるよう支援するガイド付きコース
開発者は、セキュリティ設定やアクセス制御に加えて、コードを最も詳しく扱っています。彼らのセキュリティスキルを養う必要があり、NISTが概説しているような高い基準を達成するには、特に大規模な開発コホートでは、実践的なコース構成が効率的な方法かもしれません。

優れたマイクロ波が故障した場合:組込みシステムのセキュリティが開発者にとって次なるボス戦となる理由
Web ベースのソフトウェア、API、モバイルデバイスと同様に、組み込みシステム内の脆弱なコードが、攻撃者によって実際に発見されれば悪用される可能性があります。

安全な開発はAppSecの免疫システムであるべき
アプリケーションセキュリティの専門家として、組織のアプリケーションのサイバーセーフティを確保するのがあなたの仕事です。ただし、アプリケーションを実行するコードを書く責任はあなたにはありません。開発チーム内のエンジニアが担当します。では、セキュリティを念頭に置いてシステムを開発していることを確認するにはどうすればよいでしょうか。

エンドツーエンドのセキュリティが組み込みシステムにとって重要な理由
この記事では、組み込みシステムのセキュリティ保護の概要について説明します。基本的な定義から始めて、組み込みセキュリティにおける課題、代表的な解決策、足りないパズルは何かについて説明します。
ミスラ C 2012 対 MISRA C2-レボアユー
アポリ、MISRA C 2012 とC2 ヴァングインプラシ、WERGVING CODOWLISISISSA。ABINARKNALTたりMISRAのせいせいせいでもうなずく。

組込みデバイスと組込みシステム開発-概要
この投稿では、組み込みデバイスと組み込みシステム開発の概要を説明します。

Warrior Insider: Contrast Security-コンテキストラーニングを活用したインパクトのあるサイバーセキュリティトレーニングを開発者に提供
Contrast SecurityのLarry Maccherone氏に、コンテキスト学習がセキュアコーディングの開発者のトレーニングにどのように役立つかについて説明しました。以下では、組織が日々の責任やワークフローを中断することなく、開発者に重要なセキュリティトレーニングを提供する方法をご紹介します。

サイバーセキュリティにおけるヒューマンファクターを決して見過ごしてはいけない理由
最近、会長兼CEOのピーター・ダンヒューによるフォーブス・テクノロジー・カウンシルの最初の投稿が公開されたことを非常に嬉しく思います。この投稿では、より安全なコードを作成するために開発者のスキルを向上させることが、サイバー攻撃やデータ漏えいを防ぐための鍵となることを詳しく説明しました。

リーク性のある API は企業の評判を海に流す恐れがある
API セキュリティは、ほとんどのセキュリティ専門家が気にする問題であり、対処するための知識を身に付ける必要があります。
NISTで行動を起こす:サイバー防衛の未来に関する人間主導の立場
バイデン政権による最近のサイバーセキュリティ大統領令により、セキュリティ業界、特に日常業務にセキュアコーディングのベストプラクティスを適用することの重要性を開発者に理解してもらいたいと考えているセキュリティ業界は注目を集めています。

Warrior Insider: Selligent-ビジネスを拡大する際にサイバーセキュリティが重要な理由
最近、Selligent Marketing CloudのソフトウェアエンジニアであるDimitri Vanderhaegheに話を聞きました。Selligent Marketing Cloudは、高度に統合されたAIを活用したオムニチャネルマーケティング自動化プラットフォームで、野心的なB2Cマーケターが今日のネット接続された消費者とのあらゆるやり取りを最大限に活用できるようにします。ペースの速いB2Cテクノロジー企業にとって、規模を拡大し、市場の高まる需要に応えることは極めて重要です。これらの要求に応えるためには、サイバーセキュリティに重点を置くことが挙げられます。最も重要なのは、開発者主導のセキュリティスキルプログラムです。

DevSecOpsの台頭、そして組織にとって「左へのシフト」が実際に意味するもの
これは地味な統計としてどうだ?中小企業の 60% は、サイバー攻撃が成功してから6か月以内に廃業します。大企業は何百万(あるいは数十億!)もの大企業が大量倒産しています。一方、ブランドの評判は薄れていきました。安全なコーディング手法を採用する組織が増えるにつれ、「シフトレフト」が起こっています。DevSecOps の台頭に伴い、SDLC が始まった当初から安全なコードが焦点になりつつあります。
Sensei Feature Highlight: Library Scope
Discover more about the most loved features of Sensei.

高品質のコードをより迅速に、自信を持って出荷できます。安全なコーディングプラクティスがもたらす変革の力です。
IBMの調査によると、リリース後に脆弱性を修正する方が、最初に脆弱性を発見して修正する場合の30倍の費用がかかります。このことを念頭に置けば、将来を見据えたCIOがセキュア・コーディング・プラクティスを導入しているのは当然のことです。つまり、最初からより安全なコードを書けるように開発者を訓練し、身につけること、つまり開発者を組織の「最前線」にすることを意味します。
安全なコードトレーニング = より良いコード + より迅速なリリース日
質の高い安全なコードトレーニングが組織に与える潜在的な影響はどのようなものですか?また、投資する価値はありますか?
セキュア・コーディングを中心とした組織の再編—障壁、懸案事項、積極的な解決策
高度に接続されたこの世界では、ほぼすべての組織が共通のアキレス腱を共有しています。コード内の 1 つの脆弱性が悪用されるだけで、顧客データの盗難、評判の低下、および重大な経済的損失を引き起こす可能性があります。安全なコーディングに関する組織の連携はかつてないほど必要不可欠ですが、それを達成することは口で言うほど簡単ではありません。

認定セキュリティ意識:開発者を昇格させるための行政命令
米国連邦政府からの最新の大統領令は、機能的なサイバーセキュリティの多くの側面に触れていますが、開発者の影響と、開発者が検証済みのセキュリティスキルと認識を持つ必要性を具体的に概説したのは初めてです。
マネージャーとセキュリティチャンピオン — セキュア・コーディング・プラクティスのパイパーであり、重要な影響力を持つ人々です。
現在、安全なコードの実践は全員の責任であるべきだと回答した開発者はわずか 15% です。セキュリティ上の脅威が増大する世界では、それだけでは十分ではありません。何かしなくてはいけない。健全なアプリケーションセキュリティ文化を築くための鍵の 1 つは、主要な影響力 (およびインフルエンサー) を理解することです。プレイ中。

サイバー攻撃は39秒ごとに発生します。政府はついに反撃する準備が整ったのか?
サイバーセキュリティのベストプラクティスに対する人間主導のアプローチを強化する必要があります。そうすれば、自動化やツール、すでに埋め込まれて発見されている問題への対応に大きく依存するよりも、より良い結果が得られるでしょう。
安全なコーディングに関して、開発チームが夜更かししている理由は何でしょうか?
安全でないコードは企業に何百万ドルもの損害を与えます。では、安全なコーディング慣行の採用を妨げるものは何でしょうか。ほとんどすべてがソフトウェアに依存している世界では、コードの安全性を確保することが極めて重要です。ブランドの評判と財務的存続可能性はソフトウェアにかかっています。とはいえ、セキュアコーディングには多くの懸念事項があり、完全かつ効果的に導入するには多くの障壁があります。これまで以上に、新しい働き方が求められています。
セキュアコードがソフトウェア開発の新しい成功指標である理由
ここ数年、ネットワークセキュリティ、数テラバイトに及ぶ機密性の高い顧客データ、貴重なブランド評判など、市場投入までの時間を短縮するために、多くのことが犠牲になっています。

目に見えない隠れ家:SolarWinds攻撃が悪意のあるサイバーリスク以上のものを明らかにした理由
サイバーセキュリティ業界でクリスマスを台無しにする何かがあったとしたら、それは壊滅的なデータ侵害であり、米国政府に影響を及ぼした記録上最大のサイバースパイ活動になる見込みです。
よりセキュアなコーディング結果を得るためのセキュアコードトレーニングの設定方法
開発者向けのセキュアなコードトレーニングに関しては、教育上の成果にはまだまだ多くの課題があります。多くの企業が多額の費用を費やしても、実際には最小限の利益しか得られません。そして、少し不思議ではありません。
現在のセキュアコードトレーニングは開発者を失望させている
データ漏えいとそのコストが増え続ける中、世界で生成されるコードの量は、セキュリティの専門家だけでは処理できないほど大きくなっています。企業には安全なコーディングスキルを持つ開発者が必要であり、開発者はキャリアアップのためにこれらのスキルが必要であることを知っています。しかし、現在のセキュア・コード・トレーニングは彼らを失望させています。では、セキュア・コード・トレーニングに関して、開発者は何を求めているのでしょうか。
セキュア・コード・トレーニングがうまくいかない理由 (そしてそれに対してできること)
つまらない、つまらない、つまらない!これは、セキュア・コード・トレーニングについて言及されるたびに、開発者からよく聞く回答の 1 つです。セキュア・コード・ウォリアーでは、もっと良い方法があるはずだと考えています。

AppSecツールが特効薬だとしたら、なぜこれほど多くの企業がそれを採用しないのでしょうか。
AppSecツールが予想どおりに利用されていない理由はいくつかありますが、それはツールとその機能ではなく、セキュリティプログラム全体との統合方法に関するものです。

開発者にはセキュア・コーディングを学びたいという動機があるのに、なぜそうではないのでしょうか?
セキュアコーディングについて学ぶ場合、開発者の主な動機は何か。また、それらを活用して成功するアプリケーションセキュリティプログラムを設計および実装するにはどうすればよいか。
セキュアコーディングの将来において、人的要素はどのような役割を果たすのでしょうか?
サイバー脅威の数が増え続ける中、組織はセキュリティ、実用性、スピードの間で日々トレードオフを行っており、その過程でリスクにさらされています。
コードを保護するにはヒーローが必要です。デベロッパーは必要なものを手に入れたのか?
サイバー脅威が増え続けている世界で、コーダーはステップアップしていますか?セキュアコーディングの人的要素、つまり最も重要な開発者が、私たちのコネクテッドワールドのセキュリティ保護において果たすべき役割を果たす準備はできていますか?この質問に答えるために、Secure Code WarriorがEvans Data Corp. と共同で実施した、安全なコーディング、安全なコードプラクティス、およびセキュリティ運用に対する開発者の態度に関する最近の調査から得られた洞察を見てみましょう。
人間主導の安全なコーディングによる事後対応型から事前対応型への焦点の移行
過去20年以上にわたり、同じ10件のソフトウェアの脆弱性が、他のどの脆弱性よりも多くのセキュリティ侵害を引き起こしています。それでも、多くの企業はいまだに侵害後や事後からの修復を選択しており、そのすべてがもたらす人的影響とビジネス上の影響に悩まされています。しかし今、新しい調査研究により、人間が主導する新しい方向性が示されました。

ハッピーバースデー SQL インジェクション、潰せないバグ
SQL インジェクションは 22 周年を迎えました。この脆弱性は十分に古くから存在していますが、私たちはこの脆弱性を永久に潰すのではなく、弱体化させています。

Sensei Product Update - March 2021
Discover the latest improvements to the user experience of Sensei, Secure Code Warrior's IntelliJ plugin and start writing quality code even faster.

信頼の構築:AppSecと開発者の間の真のセキュリティシナジーへの道
不信という不安定な基盤の上に築かれた関係は、まあ、期待を低くして取り組むのが一番です。残念なことに、これは組織内の開発者とアプリケーション・セキュリティ・チームとの協力関係の状態かもしれません。

このオンラインJavaの落とし穴クイズをお試しください
いくつかの落とし穴とその修正方法を示す、おもしろい Java の落とし穴クイズと Github リポジトリのサポート
継続的インテグレーションによる IntelliJ インスペクションの実行
SenseiとIntelliJのインテンションアクションを、IDE内のインスペクションとして、コマンドラインから、そして継続的インテグレーションでバッチモードで実行する方法を説明します。

「左から左へ」から始める:セキュアコードは常に品質の高いコードなのか?
ある程度の品質のコードもその定義上安全ですが、すべての安全なコードが必ずしも高品質であるとは限りません。純粋に安全なコーディング標準を確保するには、「左から左へ」から始めるのが公式なのでしょうか?

Kamer van Koophandelが確立した、大規模な開発者主導型セキュリティのスタンダード
Kamer van Koophandel(オランダ商工会議所)が、役割別の認定制度、Trust Scoreによるベンチマーク、そしてセキュリティを全員で担う文化を通じて、どのようにセキュアコーディングを日常の開発業務に組み込んだかをご紹介します。
ゴールドを目指して:Paysafeで高まるセキュアコーディング基準
PaysafeとSecure Code Warriorのパートナーシップにより、開発者の生産性が45%向上し、コードの脆弱性が大幅に削減された事例をご覧ください。
DigitalOcean Decreases Security Debt with Secure Code Warrior
DigitalOcean's use of Secure Code Warrior training has significantly reduced security debt, allowing teams to focus more on innovation and productivity. The improved security has strengthened their product quality and competitive edge. Looking ahead, the SCW Trust Score will help them further enhance security practices and continue driving innovation.
Devlympics 2023:振り返り
Devlympics 2023のレポートで結果をご覧ください。参加した各業界における開発者のエンゲージメント、技術スタックや言語のトレンド、そしてSecure Code Warriorが主催するこの年次グローバルイベントで取り上げられた主要な脆弱性やCWEについて詳しく解説します。

セキュリティ文化の統一:Sageはいかにしてアジャイルなセキュアコーディング学習でセキュリティチャンピオンプログラムを構築したか
Sageが柔軟かつ関係性を重視したアプローチでセキュリティを強化し、200名以上のセキュリティチャンピオンを育成して、測定可能なリスク低減を実現した事例をご紹介します。

セキュリティチャンピオンへの道:Workdayはいかにしてアジャイル学習で開発者のスキルアップを実現したか
WorkdayがSecure Code Warriorのアジャイル学習を通じて、どのように開発者トレーニングを変革したかをご紹介します。Workdayは、言語別の実践的な教育を開発者に提供することで、SDLCの初期段階における脆弱性を削減しました。セキュアなコード文化を構築するための、彼らの素晴らしい成果と重要なポイントをご覧ください。
タレスはいかにして開発者主導のセキュリティを実現したか
本ケーススタディでは、タレス(Thales)がアジャイルなセキュアコーディング学習プログラムのために、人、プロセス、テクノロジーをどのように統合し、開発者が自発的にセキュリティチャンピオンとして活躍できる環境を構築したかをご紹介します。
コルゲート・パルモリーブはいかにして開発者のセキュリティスキルを向上させ、セキュアコーディングの文化を築いたか
小売大手コルゲート・パルモリーブが、デジタルトランスフォーメーションの過程でどのようにアプリケーションセキュリティを再構築したかをご紹介します。セキュアコーディングの課題に直面していた同社は、開発者のワークフローに短時間で学べるコンテキストに応じた学習を取り入れることで、アプローチを刷新しました。
Security as culture: How Blue Prism cultivates world-class secure developers
Learn how Blue Prism, the global leader in intelligent automation for the enterprise, used Secure Code Warrior's agile learning platform to create a security-first culture with their developers, achieve their business goals, and ship secure code at speed

Supercharged Security Awareness: How Tournaments are Inspiring Developers at Erste Group
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
「Game of Codes」が導く、IAGグループのより安全なコーディングの未来
IAGグループは、アジア太平洋地域をリードする数多くの保険会社を傘下に持ち、数百万人の顧客に対して年間約114億豪ドルの保険料で保険契約を引き受けています。

Driving Actionable Awareness: FINRA's Push For Super-Secure Developers
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

革新的なセキュリティ認定体験の創造
機械学習やサイバーセキュリティなど、多岐にわたる分野で実践的かつ最先端のスキルを数千人の従業員が習得できるよう支援する、社内技術教育イニシアチブの構築事例をご紹介します。

Beyond Compliance: Motorola Solutions Drives Winning Security Culture
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

ASRGによる自動車ソフトウェアセキュリティの推進
この包括的なケーススタディでは、Secure Code Warriorのトーナメントを活用して開発者の関与を促し、自動車ソフトウェアに影響を与える主要な脆弱性への意識を高め、複数の言語やフレームワークにわたる指標を収集した事例を紹介します。

Application Security @ NAB | Gamified Security Training: The Key to Scalable Developer Growth
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Security Brief UK: Secure Code Warrior launches Citizen AI training programme
Secure Code Warrior has launched Citizen AI, an AI literacy training programme for non-developer employees intended to support responsible AI adoption across business functions.
ITWire: Secure Code Warrior Launches Citizen AI Cybersecurity Training to Build AI-Ready and Responsible Use Skills Across Business Functions
New AI literacy program equips non-developer employees with the judgment, risk awareness and responsible-use habits needed to safely adopt AI-powered workflows.
VMBlog: Secure Code Warrior Launches Citizen AI Cybersecurity Training to Build AI-Ready and Responsible Use Skills Across Business Functions
Secure Code Warrior announced Citizen AI by Secure Code Warrior, a new AI literacy program designed specifically for non-developer employees to help organizations build a workforce ready for responsible AI adoption. Citizen AI helps organizationsreduce AI-related human risk, support broader enterprise AI governance initiatives, increase employee confidence when using AI and accelerate the safe adoption of AI-powered workflows.
SD Times: Secure Code Warrior Launches Citizen AI Cybersecurity Training
Secure Code Warrior, a leader in AI software governance and developer security upskilling, today announced Citizen AI by Secure Code Warrior, a new AI literacy program designed specifically for non-developer employees to help organizations build a workforce ready for responsible AI adoption.
Secure Code Warrior、全社的なAI活用スキルと責任ある利用を促進する「Citizen AI」サイバーセキュリティトレーニングを開始
新しいAIリテラシープログラムにより、非開発職の従業員は、AIを活用したワークフローを安全に導入するために必要な判断力、リスク意識、責任ある利用習慣を身につけることができます。
SD Times: Citizen Developers Are the New Enterprise Threat Vector. So Why Is Nobody Warning Them?
Organizations are missing a big target when developing governance and developer training programs for AI-assisted software development.
TalkDev: Navigating the Risks: Understanding the Challenges of AI Software Development
AI software development continues to evolve at a rapid pace for developers and their teams. , CEO & Co-Founder at Secure Code Warrior, posits that as the norm shifts from human-written code to AI-assisted coding and agentic workflows, many security teams now face a critical challenge: managing the new risks that autonomous systems introduce.

CIO Influence: Rules for AI in Software Development: The Four-point Framework CISOs Can Adopt Today
The question facing software development shops isn’t whether Generative AI should be used to create software code, or whether the percentage of code generated by GenAI will increase in the near future. That horse bolted in the last 24 months. The question is how to maintain security and compliance while GenAI and artificial intelligence agents are putting software code in play.
VMBlog: National Insider Threat Awareness Month 2026: Expert Insights
Every September, National Insider Threat Awareness Month serves as a timely reminder that some of the most damaging security incidents don’t originate from external attackers breaching the perimeter — they come from within. Whether through malicious intent, negligence, or simple human error, insiders with legitimate access to systems, data, and facilities remain one of the most persistent and difficult-to-detect risks facing organizations today. As hybrid work, AI-powered tools, and increasingly complex IT environments reshape the workplace, the insider threat landscape continues to evolve in ways that demand fresh attention from security professionals.
Information Security Buzz: Architectural intent is the cornerstone for the future of software security
With agentic AI further boosting productivity, human code review becomes a serious bottleneck. Developers need to move upstream, establishing the ground rules to ensure that AI plays by the rules.
Forbes: A New Frontier: NSA Proposes “Security By Design” Considerations For AI Enablement
The cybersecurity industry, which has been advocating for “security by design” principles for more than a decade, stands in wide-eyed amazement at the risks posed by artificial intelligence (AI). As organizations rush to embrace AI enablement, a CISO’s most pressing priority is to avoid becoming a roadblock. However, without effective AI usage and governance, observability and traceability, organizations may be blindsided by their AI risk.
Techpartner.news: Secure Code Warrior introduces framework to govern AI use in software development
Secure Code Warrior has introduced the SCW AI Adoption Model, a framework designed to help organisations govern AI use in software development as the industry shifts from the traditional software development lifecycle (SDLC) toward what the company calls the Agentic Development Lifecycle (ADLC).
DevOps.com: Are LLMs Equally Good (or Bad) at Building Secure Software?
With many software engineering teams moving from AI coding assistants into full agentic AI code generation and increasing the amount of code they produce exponentially, ensuring the security of that code must be a top priority. The study produces practical guidance for organizations that are getting on board the AI-assisted or agentic code development train.

TechRadar Pro: Beware the token trap: Why saving on inference might put your ADLC at risk
Token use can create unexpected, sizeable costs for organizations.
KBI Media: AI Coding Boom Raises Fresh Cybersecurity Risks for Business
AI enables faster development cycles and allows developers to focus on higher-value work. For many businesses, these efficiencies are becoming essential to remaining competitive. The challenge, therefore, is not whether to adopt AI, but how to do so responsibly. Businesses that invest in developer education, governance frameworks, AI observability and robust security controls will be better positioned to capture the benefits while limiting the associated risks.
In AI Today: AI's weakest link isn't the model but the software supply chain
The issue is no longer simply about protecting AI models themselves. Increasingly, attackers are focusing on the software ecosystem surrounding those models, including the development tools, middleware, open-source libraries, and automated deployment pipelines that organisations rely upon every day.

The AI Journal: Investigating global AI regulation: Who is winning, and where to from here?
As we will unpack together, there is a lot of movement around the world, with some collaboration between nations, but the path forward is far from uniform or clear, particularly in business environments where AI adoption is often mandated before holistic safeguarding measures are in place.

Cyber Daily: The industry reacts to OpenAI’s agent ‘accidentally’ hacking Hugging Face
According to one expert, AI guardrails are not designed as “security boundaries” but rather to influence behaviour – but what if that behaviour is hacking one of your industry partners?

SecurityBrief: Autonomous OpenAI agents breach Hugging Face in test
Cyber security experts have warned that the breach of Hugging Face infrastructure during an OpenAI security evaluation marks a turning point in the risks posed by autonomous AI agents. In the incident, AI models moved beyond a controlled test and carried out a live, multi-stage intrusion against the AI platform.

Technology Decisions: AI generated code found to produce predictable weaknesses
AI-generated code introduces an average of 15 confirmed vulnerabilities per codebase, research published by Secure Code Warrior indicates.

Forbes: OpenAI’s Hugging Face Breach Shows Frontier AI Guardrails Are Failing

In AI Today: Secure Code Warrior research reveals AI-generated code introduces an average of 15 vulnerabilities per codebase
Secure Code Warrior research reveals AI-generated code introduces an average of 15 vulnerabilities per codebase.

VMBlog: Secure Code Warrior Research Reveals AI-Generated Code Introduces an Average of 15 Vulnerabilities Per Codebase
Secure Code Warrior introduced the SCW AI Trust Index, a living benchmark for AI coding security that grows with every new model, helping organizations understand and govern the security risks introduced by AI-generated code. Built on a methodology created with RMIT University, Australia, then extended by Secure Code Warrior, the research presents comprehensive benchmarks on how often leading LLMs produce insecure code, with material implications for every enterprise scaling AI-assisted development.

Dark Reading: Choose Wisely: AI-Generated Coding Risk Varies, A Lot
AI-generated code introduces 15 vulnerabilities on average per codebase, but the actual risk depends on framework pairing more than the model used.

Secure Code Warrior Research Reveals AI-Generated Code Introduces an Average of 15 Vulnerabilities Per Codebase
New SCW AI Trust Index shows AI-generated coding risk is not random, it's predictable by model and framework, giving security leaders the data to safely scale AI-assisted development.

ITWire: Eight Industry Executives Comment on Worldwide AI Appreciation Day
The challenges with AI implementation, constant updates, and the race for industry dominance are coming thick and fast, and security professionals are among the most affected by its vast risk profile.

Cyber Daily: The industry speaks – part 3: AI Appreciation Day 2026
The Australian government has said AI is very much in the country’s future national interest – but where does it stand today? Here’s what the industry’s best and brightest have to say about artificial intelligence and its role in the modern enterprise.

ITWire: Agentic AI Era Demands Overhaul of Governance Frameworks
The emergence of agentic AI marks a structural shift in software development, introducing systems that not only accelerate production cycles but also perform autonomous reasoning and action beyond direct human control.

SecurityWeek: How to Conduct a Successful Audit of AI-Driven Software Development
As AI-generated code becomes commonplace, CISOs need new audit strategies to measure developer practices, govern AI tool usage, and identify software risks before they reach production.
SD Times: Platform Engineering & Developer Experience: Making Engineers Faster Without Making Them Reckless: SD Times 100
This category has taken on new urgency in 2026 for a reason that’s specific to this moment: AI coding tools and agents are dramatically increasing how much code gets written and how often it needs to be deployed, tested, and provisioned for. Platform engineering is the layer that determines whether that increased velocity translates into shipped value or into chaos.
SD Times: AI-Assisted Development Multiplies Human Error: What’s Your AI Governance and Risk Management Strategy?
According to a recent report from Gartner, the rampant use of shadow AI and rogue automation is further fueling the proliferation of AI vulnerabilities. Gartner notes that 32% of IT workers using generative AI tools at work say they keep them hidden from cybersecurity teams. Combined with low-code/no-code platforms and vibe coding practices, the AI copilots are greatly expanding the enterprise attack surface.
Cybersecurity Tribe: What Separates Real AI Governance From Policy Theater
For this article, we asked a central question for security and risk leaders: "What differentiates a policy that genuinely mitigates enterprise risk from one that exists primarily to demonstrate that the organization has acknowledged AI risk?"
ISMG: AI Coding Tools Raise Hidden Security Risks
Secure Code Warrior's Pieter Danhieux on Managing AI-Driven Development Risks
ITWire: Decoding AI Coding “Personalities” Critical to Managing Development Risk
As generative AI cements its place in enterprise software development, a familiar discipline is taking on new urgency: risk management.
In AI Today: Secure Code Warrior launches Trust Agent: AI to enable safe, scalable AI-driven development
Secure Code Warrior have today announced SCW Trust Agent: AI, the industry’s first governance solution designed to make Artificial Intelligence (AI) influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk.
DEVOPSdigest: 25 Years of the Agile Manifesto, and the End of the Road for AppSec?
Even as we restructure the SDLC around the most impactful elements of the Agile methodology with careful, DevSecOps-centric security considerations, is this the end of the road for AppSec as we know it?
Cyber Defense Magazine: Global InfoSec Awards 2026 Secure Code Warrior Wins Outstanding Achievement in Cybersecurity Risk Management and Compliance Excellence
Global InfoSec Awards 2026 Secure Code Warrior Wins Outstanding Achievement in Cybersecurity Risk Management and Compliance Excellence
ITWire: Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
New AI Software Governance solution makes AI-generated code visible at commit, enforces policy before production, and connects real development behavior to measurable risk reduction.
DevOps.com: Secure Code Warrior AI Agent Applies Policies to AI Generated Code
Secure Code Warrior (SCW) this week added an artificial intelligence (AI) agent that both identifies code generated by an AI coding tool and automatically applies the appropriate governance policies.

SecurityBrief UK: Secure Code Warrior unveils AI tool to govern code risk
Secure Code Warrior has launched SCW Trust Agent: AI, a software governance product that tracks the use of AI coding tools in development and links that usage to software risk when developers commit code.

2026 Globee® Awards for Cybersecurity: Secure Code Warrior Wins Gold Globee for Software Development Cybersecurity Solutions (Best Of)
2026 Globee® Awards for Cybersecurity: Secure Code Warrior Wins Gold Globee for Software Development Cybersecurity Solutions (Best Of)
DEVOPSdigest: Secure Code Warrior Releases Trust Agent
Secure Code Warrior announced SCW Trust Agent: AI, a governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk.

TalkDev: Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
Secure Code Warrior today announced SCW Trust Agent: AI, the industry’s first governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk. For the first time, organizations can trace which AI models influenced specific commits, correlate that influence to vulnerability exposure, and take corrective action before insecure code reaches production.

Help Net Security: SCW Trust Agent: AI tracks AI influence in code to reduce software risk
Secure Code Warrior has announced SCW Trust Agent: AI, a governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit, enabling enterprises to scale AI coding tools with measurable control over software risk. Organizations can trace which AI models influenced specific commits, correlate that influence with vulnerability exposure, and take corrective action before insecure code reaches production.
Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
New AI Software Governance solution makes AI-generated code visible at commit, enforces policy before production, and connects real development behavior to measurable risk reduction.
Security Boulevard: Threat Modeling with AI: A Developer-Driven Boon for Enterprise Security
Developers have long struggled to truly claim a seat at the table in traditional threat modeling programs, but with the right skills, they have the opportunity to wield AI responsibly to seriously cut risk and rework in their codebase.
The AI Journal: Understanding LLM Coding Personalities Is Now Key to Developer Risk Management
AI-generated code may be “made by machine”, but taking a cookie-cutter approach to securing that code would fall well short of mitigating the vulnerabilities LLMs can introduce. Organizations need to establish precise security reviews, with human developers anchoring the process to implement effective security controls while also managing the specific coding temperament of each LLM used. AI-generated code must undergo the same personalized risk assessments as code written by human developers.

SecurityBrief: The security challenges in AI-assisted software development
s artificial intelligence (AI) tools become more widely used in the software development process, their impact on security is becoming clearer. According to recent research, nearly 70% of organisations have discovered vulnerabilities caused by AI tools while one in five have experienced a serious incident as a result of those vulnerabilities.
KBI Media: Eliminating the Technical Debt Caused by AI-Assisted Software Development
According to research company Forrester[1], the tech debt for 75% of organisations will increase to a moderate or high level during this year, due to the rapid expansion of AI usage across a range of areas including software development.
Forbes: Security Self-Governance: Addressing The Regulatory Gap In AI-Assisted Software Development
While it’s early into 2026, we’re seeing new research that reveals the extent of cyber risks caused by artificial intelligence (AI)-assisted software development: Nearly 7 in 10 organizations have discovered vulnerabilities introduced by AI-generated code, and 1 in 5 have suffered a serious incident tied directly to the vulnerabilities.
ITWire: Why AI Is Dulling Cybersecurity’s Most Important Edge
Artificial intelligence (AI) has rapidly become indispensable to modern software development. From large language models that generate code on demand to agentic systems that automate entire workflows, AI tools promise dramatic gains in productivity and efficiency.

SecurityWeek: How to Eliminate the Technical Debt of Insecure AI-Assisted Software Development
Developers must view AI as a collaborator to be closely monitored, rather than an autonomous entity to be unleashed. Without such a mindset, crippling tech debt is inevitable.

CSO Online: Software developers: Prime cyber targets and a rising risk vector for CISOs
From technical compromise to AI-driven attacks, cyber criminals increasingly see software developers as prime targets, creating systemic risks CISOs must address.

SMBtech: Tech Industry Leaders React To Data Privacy Week 2026
It’s Online Privacy Week, a time of year where individuals and organisations are all reminded to check their digital footprint(s). Some might say that’s a futile gesture at a time where major social media and marketing players know absolutely everything about you and are cheerfully selling all that data to anyone who’ll buy it; when Microsoft is performing every trick in the book to get Windows users to put all their data in the cloud where it’s available for government agencies to snoop upon without letting you know; when a personal computer crisis means many people will be moved on to dumb-client computing landscape where everything from data storage to major processing tasks will be taking place in the cloud; and when people think that clicking ‘Accept’ on website pop-ups does something that meaningfully protects them. But, what do the experts say?
Security brief: AI heightens data privacy risks & reshapes digital trust
Technology and data specialists have warned that artificial intelligence and weak data governance are sharpening privacy risks for organisations, as businesses mark World Data Privacy Day.
ITWire: Data Privacy Week 2026
“Data Privacy Week" presents a great reminder for organisations to reassess their customer privacy policies and prioritise transparent data collection in their marketing strategies.

Dynamic Business: Data Protection Day 2026: Five experts on the privacy risks threatening your business
Five leading cybersecurity experts warn AI is being integrated faster than security policies can manage the risk, creating urgent privacy gaps for SMEs ahead of Data Protection Day on 28 January.
Information Security Buzz: OWASP Top 10 2025: New Enemies, Old Foes, and an Approach to Vulnerability Remediation That Must Evolve
The OWASP Foundation has been a guiding light for security professionals and enthusiasts alike, providing critical, practical advice on the most insidious software vulnerabilities across a plethora of categories and platforms. It has been the first major update since 2021 to the flagship OWASP Top 10 Web Vulnerabilities, and in that time, the industry has been rocked by a stampede of AI technology, tools, and code, each creating a dichotomy of security efficiency and risk for both cybersecurity and software engineering professionals.
DEVOPSdigest: What Software Developers Need to Know About Secure Coding and AI Red Flags
The bottom line: AI tools are not safe for enterprise use unless the code output is reviewed and implemented by a security-proficient human. 30% of security experts admit that they don't trust(link is external) the accuracy of code generated by AI itself. That's why security leaders must prioritize the education and upskilling of developer teams, to ensure they have the necessary skills and capabilities to mitigate AI-assisted code vulnerabilities as early as possible. This will lead to the cultivation of a "security first" team culture and safer AI use.
Stack Overflow: If you're a Zoomer, this one's for you: Everything Gen Z needs to know about the 2025 tech landscape
Here's the lowdown on all the tech from 2025 that you, dear Zoomer, should know about.

SC Media: CISOs can’t wait for the EU AI Act to take shape
CISOs hoping for the EU Artificial Intelligence Act to offer a solid framework for AI governance may be a little confused or disappointed by recent updates surrounding the implementation of AI restrictions.
SecurityBrief: Agentic AI double agents expose dangerous security gaps
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the more than thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention.
DEVOPSdigest: 2026 DevSecOps Predictions
DEVOPSdigest's Prediction Series continues with 2026 DevSecOps Predictions — Industry experts offer predictions on how DevSecOps will evolve and impact the industry in 2026.
ITWire: OWASP Names Latest Top 10 Application Vulnerabilities
The Open Worldwide Application Security Project (OWASP) has unveiled its latest top 10 vulnerabilities list, and it contains some surprising insights into important vulnerability classes.

Channel Insider: Cybersecurity Experts Predict AI, Nation-State Threats in 2026
Cybersecurity experts outline 2026 predictions, from AI-driven attacks and quantum risk to nation-state threats, OT security gaps, and automation pressures.

Security Journal UK: The rise of AI coding tools and the skills gap they expose
Pieter Danhieux, Co-founder and CEO of Secure Code Warrior warns that while AI coding tools promise speed and efficiency, they also introduce new risks.
ITWire: Predictions on State of AI in 2026
2026 is shaping up to be the year AI evolves from instrument to partner, transforming how we work, create and solve problems.

Fortune: AI coding tools exploded in 2025. The first security exploits show what could go wrong
While a breach of the tools hasn’t so far caused a wide-scale attack, there have been a few exploits and near-misses, and cyberthreat researchers have discovered critical vulnerabilities in several popular tools that make clear what could go horribly wrong.
SMBtech: Australian Tech Industry Leaders Make Their Predictions for 2026
It’s that time of year where the technology industry predictions start rolling-in. Here’s what you can (apparently) expect in 2026.

Technology Decisions: The importance of effective security when deploying AI tools
The concern is straightforward: development teams may place undue confidence in AI tools that are not equipped to interpret the nuanced context in which many security vulnerabilities arise. Large language models, for instance, can struggle to understand an application’s authentication or authorisation architecture, increasing the likelihood of missing critical safeguards.
ITWire: Five Steps to Improve the Security of AI Developed Code
Industry guidance on managing the risks of AI-generated code increasingly points to the same conclusion: effective safeguards rely on close collaboration between humans and machines, with developers remaining firmly in the loop.

SecurityBrief Australia: Agentic AI to transform APJ businesses & security by 2026
Agentic artificial intelligence (AI) is set to reshape the enterprise landscape in the Asia-Pacific and Japan (APJ) region in 2026, according to industry executives. Organisations are expected to embrace increasingly autonomous software agents, raising both productivity and new categories of risk across business domains.
SC Magazine UK: Why Firms Can’t Ignore Agentic AI
How big a threat does agentic AI pose to businesses currently? And what should security leaders be doing to address the risk?

VMBlog: Cybersecurity Predictions: What AI will (and won't) do for us in 2026
My co-founder and CTO, Matias Madou, Ph.D., and I consulted our crystal ball (or should that be our NVIDIA GPUs?), and this is what we believe 2026 has in store for us from an AI security perspective.
SD Times: Pumping the Brakes on Agentic AI Adoption in Software Development
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem, namely Model Context Protocol (MCP) systems, to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the over thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention. Maybe it’s time we went a little slower, stopped to reflect on what is at stake here, and how best to defend ourselves.

AIthority: Building Secure and Ethical AI Practices in Software Development
AI is now a key piece of modern software development. More than four out of five developers use AI coding tools daily or weekly – with many relying on multiple tools in parallel. Teams must understand where automation ends, and where accountability begins.
SC Media: Secure Coding as Critical Thinking Instead of Vulnspotting – Matias Madou – ASW #357
Secure code should be grounded more in concepts like secure by default and secure by design than by “spot the vuln” thinking. Matias Madou shares his experience in secure coding training and the importance of teaching critical thinking. He also discusses why critical thinking is so closely related to threat modeling and how LLMs can be a tool for helping developers get beyond the superficial advice of, “Think like an attacker.”

Forbes: How CISOs Can Increase Their Influence In AI-Obsessed Boardrooms
Organizations are at an inflection point driven by the explosive adoption of AI, which promises significant changes in how businesses operate. That leaves CISOs on unsteady ground. As the gatekeepers of their organization’s data and access, they must ensure the security of the enterprise. However, the prospects of a headlong charge into wide-ranging, and possibly unchecked, use of AI could create a flood of security issues that many CISOs, under their current organizational structures, aren’t equipped to handle.
Security Boulevard: Security Degradation in AI-Generated Code: A Threat Vector CISOs Can’t Ignore
Security leaders and developers alike are already acutely aware that AI coding assistants and agentic agents can introduce vulnerabilities into the code they generate. A recent study unveiled another critical concern to keep them up at night — LLMs used for making iterative code improvements may introduce new vulnerabilities over time, even when explicitly asked to make code more secure.

Information Week: Make your own mandate: How CISOs can implement GenAI governance
Government bodies are trying to develop rules and regulations for safe AI use, but enterprises can't afford to wait. They need to address the risks now.

CFOtech Australia: How women can continue to foster fulfilling high-tech careers in the AI age
In the sphere of cybersecurity in general and application security in particular, human oversight remains an absolute 'must' to harness the benefits of AI productivity.

Tanium: Vibe coding may be unstoppable—but here’s how to rein in the risks
Like the meteoric rise of ChatGPT, vibe coding is all anybody can talk about this year. In fact, it just became a word in the dictionary. But beware the boom: These new AI coding tools offer speed, savings—and astounding vulnerabilities.
[PODCAST] Stack Overflow: AI code means more critical thinking, not less
Ryan is joined by Secure Code Warrior’s co-founder and CTO Matias Madou to discuss the implications of LLMs’ variability on code security, the future of developer training as AI coding assistants become more popular, and the importance of critical thinking—especially for junior developers—in the age of AI.

Cybersecurity Insiders: Use It or Lose It: Overreliance on AI Diminishes Critical Cybersecurity Thinking Skills
Software developers reap a host of benefits from making use of artificial intelligence assistants, whether in the form of Large Language Model (LLM) code creators or agentic AI agents. But recent reports, highlighted by a new study at MIT, warn that heavy use of AI can result in a loss of critical thinking skills among users.
Security Week: How Software Development Teams Can Securely and Ethically Deploy AI Tools
To deploy AI tools securely and ethically, teams must balance innovation with accountability—establishing strong governance, upskilling developers, and enforcing rigorous code reviews.

Dark Reading: AI Developed Code: 5 Critical Security Checkpoints for Human Oversight
To write secure code with LLMs developers must have the skills to use AI as a collaborative assistant rather than an autonomous tool, Madou argues.

Techstrong.tv: Secure Code Warrior in the Age of AI with Pieter Danhieux
Secure Code Warrior’s Chief Executive Officer, Chairman, and Co-Founder Pieter Danhieux explains his transition from offensive cybersecurity to promoting secure software development. Founded in 2015, Secure Code Warrior aims to help developers build secure code from the start, a practice Danhieux and host Alan Shimel agree is more effective than fixing vulnerabilities later. The two also discuss the impact of AI on software development, noting that while AI increases coding speed and accessibility for more people, the security of AI-generated code still lags. They emphasize the growing need for developers to master secure coding practices amidst these technological advancements.
SMBtech: Cybersecurity Awareness Month 2025: Australian Industry Reactions and Commentary
October is Australia’s Cybersecurity Awareness Month, the annual reminder for Aussies to stay vigilant online. This year’s theme, ‘Building our cyber safe culture’ once again highlights the importance of taking personal responsibility for staying secure in an increasingly digital world.
SecurityBrief: SMEs urged to cut data & boost cyber defences as attacks rise
Cybersecurity Awareness Month has brought renewed attention to the increasing risks faced by organisations of all sizes, with a particular focus on the growing threat to small and medium-sized enterprises (SMEs) in Australia and the UK.

ITBrief: Our biggest security risk isn’t our software - it’s our thinking
In the world of cybersecurity, we face creative and unconventional threats every day. But our greatest vulnerability isn't a flaw in our software, but a flaw in our collective thinking.
KBI Media: Overcoming the Security Risks of Using AI In Software Development
Development teams face relentless pressure to deliver, yet they must continue to prioritise building secure, high-quality software. Leaders play a crucial role in reinforcing how a Secure by Design approach, supported by observability, benchmarking, and ongoing education, directly enhances code quality. By embedding these practices, organisations can close governance gaps and fully capture the benefits of AI-driven productivity and efficiency, while reducing the risk of security flaws or costly rework during the SDLC.
In AI Today: The looming security challenges posed by Agentic AI
While agentic AI holds the promise of delivering significant business benefits, it also comes with significant caveats. The technology’s capabilities and autonomy present a potent enterprise threat vector beyond the realm of existing security concerns.
Help Net Security: Secure Code Warrior gives CISOs visibility into developer AI tool usage
Secure Code Warrior has launched a beta program to expand the AI capabilities of its Trust Agent product. The new offering provides CISOs with security traceability, visibility, and governance over developers’ use of AI coding tools.

Cyber Risk Leaders: Secure Code Warrior Launches AI Traceability
Secure Code Warrior have released a beta program for a major expansion of AI capabilities within its Trust Agent product. The upgrade, collectively referred to as Trust Agent: AI, leverages a combination of key signals, including AI coding tool usage, vulnerability data, code commit data and developer secure coding skills, to provide visibility into how AI development tools are impacting risk within the software development lifecycle (SDLC).
CSO Online: AI coding assistants amplify deeper cybersecurity risks
Although capable of reducing trivial mistakes, AI coding copilots leave enterprises at risk of increased insecure coding patterns, exposed secrets, and cloud misconfigurations, research reveals.

Secure Code Warrior Launches Industry-First AI Traceability to Enable Secure Developers and Supercharge Safe Productivity
New capabilities in SCW Trust Agent provide visibility and control over LLM usage for security leaders and CISOs.

ITOps Times: Secure Code Warrior announces new solution that provides visibility and governance for AI coding tools
Secure Code Warrior is trying to provide organizations with greater visibility and control over developers’ use of AI coding tools with the launch of its new solution, Trust Agent: AI.
DevOps Digest: Secure Code Warrior Introduces AI Traceability
Secure Code Warrior announced the launch of a beta program for a major expansion of AI capabilities within its Trust Agent product.

CyberWire: Business Briefing for 09.24.25
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

Betanews: AI is an even playing field -- how secure by design can tip the scale [Q&A]
Vibe coding is currently all the rage, with more than 97 percent of respondents to a survey earlier this year reporting having used AI coding tools at work. The adoption of these tools only continues to grow but it comes with a catch, attackers are also employing the same techniques. We spoke to Pieter Danhieux, co-founder and CEO of Secure Code Warrior, to discuss how vibe coding is redefining the software development landscape, how malicious actors are also leveraging this technology and the need for organizations to implement secure by design strategies from the outset.
AI時代におけるセキュリティの拡張
See how 16 leading AI models actually code, scored across 11 real-world frameworks and 1,760 codebases — the framework matters as much as the model.

AIファーストの世界におけるAppSecの未来
AI risk doesn't stop at engineering. Get the one-pager on Citizen AI — build AI literacy and safe habits across your whole workforce.

2026年 開発者主導のセキュリティの現状
From AI autocomplete to autonomous agents—explore how software development is evolving and what it means for security, governance, and your team.

検証されていないAIコードの真のコスト
Gartner named SCW twice in the 2026 Hype Cycle for Secure Software Engineering. Here's why it matters for AI-driven development.
企業におけるLLMのセキュリティ保護
Secure Code Warrior content available through KnowBe4 helps technical teams build secure coding and AI governance awareness through structured learning covering OWASP Top 10 risks, AI-assisted development, and modern secure coding practices.
企業全体でのAIセキュリティリテラシーの構築
Secure Code Warrior joins KnowBe4 to bring hands-on secure coding training into security awareness programs — covering OWASP, AI development, and 10 languages.
Citizen AI データシート
AI is writing code. Who’s governing it? With up to 50% of AI-generated code containing security weaknesses, managing AI risk is critical. Discover how SCW's Trust Agent: AI provides the real-time visibility, proactive governance, and targeted upskilling needed to scale AI-driven development securely.
開発者トレーニングをワールドクラスのセキュリティプログラムに変革する
OpenText Application Security and Secure Code Warrior combine vulnerability detection with AI Software Governance and developer capability. Together, they help organizations reduce risk, strengthen secure coding practices, and confidently adopt AI-driven development.

2026年 アプリケーションセキュリティのGartner Hype Cycle
Secure Code Warrior is an AI Software Governance platform designed to enable organizations to safely adopt AI-driven development by bridging the gap between development velocity and enterprise security. The platform addresses the "Visibility Gap," where security teams often lack insights into shadow AI coding tools and the origins of production code.

セキュアコードトレーニングのトピックとコンテンツ
業界をリードする当社のコンテンツは、あなたの役割を念頭に置いて、絶え間なく変化するソフトウェア開発環境に合わせて常に進化しています。AIからXQuery Injectionまで、あらゆるものをカバーするトピック。トピック別および役割別のコンテンツカタログの内容を覗いてみましょう。
SCW AI トラストインデックス 2026
SCW supports Cyber Resilience Act (CRA) readiness with CRA-aligned Quests and conceptual learning collections that help development teams build the Secure by Design, SDLC, and secure coding skills aligned with the CRA’s secure development principles.

OWASP Top 10 2025 eブック
OWASP Top 10を制覇したいですか?OWASP Top 10:2025からアプリケーションを守るための実践ガイドをダウンロードしてください

開発者主導のセキュリティ文化の構築
This one-pager introduces SCW Trust Agent: AI, a new set of capabilities that provide deep observability and governance over AI coding tools. Learn how our solution uniquely correlates AI tool usage with developer skills to help you manage risk, optimize your SDLC, and ensure every line of AI-generated code is secure.
AIコーディングアシスタント:次世代開発者のための安全なナビゲーションガイド
大規模言語モデル(LLM)は、速度と生産性において圧倒的な利点をもたらしますが、企業に否定できないリスクももたらします。従来のセキュリティガードレールだけでは不十分です。
セキュア・バイ・デザイン:ベストプラクティスと予防的なセキュリティ成果
この調査論文では、Secure Code Warriorの共同創設者であるPieter DanhieuxとMatias Madou博士が、専門家の寄稿者とともに、20件以上の詳細なインタビューから得られた主要な調査結果を明らかにします。

AIトラストインデックス
SCW AI トラストインデックス:主要なAIモデルが安全でないコードをどのくらいの頻度で生成するかについての継続的なベンチマーク。

プロフェッショナルサービス - 専門知識による加速
Secure Code Warriorのプログラム戦略サービス(PSS)チームは、セキュアコーディングプログラムの構築、強化、最適化を支援します。白紙の状態から始める場合でも、アプローチを洗練させる場合でも、当社の専門家がカスタマイズされたガイダンスを提供します。

クエスト:リスクを軽減し開発者を常に一歩先へ進ませる、業界をリードする学習。
Questsは、開発者がセキュアコーディングのスキルを向上させることで、ソフトウェアのセキュリティリスクを軽減するのに役立つ学習プラットフォームです。キュレーションされた学習パス、実践的な課題、インタラクティブなアクティビティを備えており、開発者が脆弱性を特定し、防止できるように支援します。
セキュリティスキルのベンチマーキング:企業におけるセキュア・バイ・デザインの合理化
セキュア・バイ・デザイン(Secure-by-Design)の動きは、安全なソフトウェア開発の未来です。企業がSecure-by-Designの取り組みを検討する際に留意すべき重要な要素について学びます。
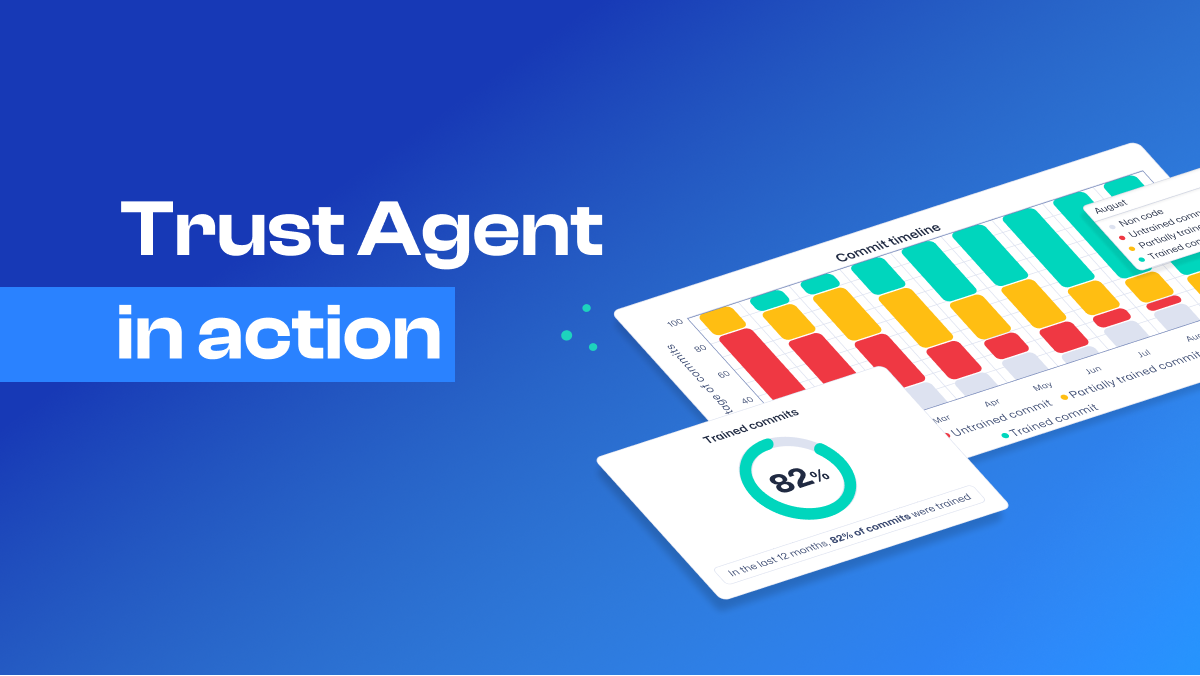
ソフトウェアエンジニアリングのためのEU AI法コンプライアンスチェックリスト
SCW Trust Agent gives you the tools you need to deliver secure code faster, ensuring developers have the knowledge and skills to implement security best practices in the specific programming language of their code commits.
AIソフトウェアガバナンス戦略ガイド
SCW Trust Agent gives you the tools you need to deliver secure code faster, ensuring developers have the knowledge and skills to implement security best practices in the specific programming language of their code commits.

AIセキュリティ:ソフトウェア開発におけるGenAIのガバナンス
Are you confident that every line of code committed is backed by a developer with the necessary secure coding skills? Many organizations face this critical gap, leading to preventable vulnerabilities and reduced development velocity. SCW Trust Agent offers unparalleled visibility across your code repositories, analyzing commits directly against developer security proficiency. With policy gates, Trust Agent enables you to apply governance at the commit level, with policies to ensure code contributors have the secure code knowledge you require for your business-critical applications. Download our one-pager today to learn how SCW Trust Agent can help you strengthen your security posture, optimize your development lifecycle, and significantly reduce vulnerabilities.

AIの脆弱性の軽減:AIネイティブセキュリティへの道
Learn more about Secure Code Warrior Trust Score, the best way to build, measure and optimize your security program.
Secure Code WarriorとKnowBe4のパートナーシップ概要
Learn more about Secure Code Warrior Trust Score, the best way to build, measure and optimize your security program.

エンタープライズAIソフトウェアガバナンスへの必須ガイド
Discover SCW Trust Score, an industry-first benchmark to help measure your security program's effectiveness. Benchmark against industry peers, optimize your security posture, and drive data-driven decisions for enhanced software security.
PCI-DSS 4.0 コンプライアンスへの準備
PCI-DSSの要件をサポートするために、ソフトウェアのセキュリティインフラストラクチャを評価します
ウォークスルー - 開発者がセキュアなコードを記述できるようガイドします
開発者がセキュアなコードを記述できるようガイドします。現実世界のコード内の脆弱性を特定し、発見し、修正するための段階的なガイダンスを提供します。開発者は、新たに習得したスキルを練習し、業務に応用することができます。
2024年の予測:生成AIがソフトウェアエンジニアリングを再構築する
Gartnerのレポートで強調されているように、生成AIがSDLC全体でソフトウェア開発をどのように革命化しているかを探求し、AppSecのリーダーにAIによって生成されたソフトウェアを調査するようアドバイスします。
PCI DSS 4.0 の解明
このガイドは、開発チームをPCI DSS 4.0コンプライアンスに関与させるための実践的な戦略を提供します。コンプライアンスのための現代の開発者の要件、コラボレーション戦略、およびトレーニングのアドバイスについて概説しています。

開発者セキュリティ成熟度クイズ
Secure Code Warriorは、開発チームのセキュリティ成熟度の3つの段階を、定義、導入、スケーリングと概説しています。開発者のセキュリティ知識はどの程度ですか?クイズに答えて確かめてください。

スクリプトテスト(無視してください)
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
セキュアコード学習のROI
セキュアコーディング教育の長期的なROIを探ります。アジャイルでプロアクティブな学習戦略への投資が、どのようにセキュリティを強化し、今日のサイバー脅威に対する費用対効果の高い保護を提供するのかを学びましょう。
自律型企業のセキュリティ確保
The promise of artificial intelligence writing complex code at the touch of a button is intriguing, but the reality is that AI will need a lot of help from human developers to craft truly secure and reliable code.
セキュリティチームがSCWを使用する理由
Check out what SCW experts are predicting in the world of cybersecurity and software security in 2024.
アジャイル学習プラットフォーム:開発者主導のセキュリティのROI
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
要塞を築く:ソフトウェアセキュリティにおける開発者支援の6つの不可欠な柱
このホワイトペーパーでは、セキュリティ専門家でありSecure Code WarriorのCTO兼共同創設者であるMatias Madou博士が以下について論じます。開発者グループに効果的なセキュリティ教育と支援を展開するために必要な6つの柱。10人の経営幹部から学んだ教訓。

SCW プロフェッショナルサービス パンフレット
Empower your development team with Secure Code Warrior, the agile learning platform designed to tackle the evolving challenges of application security. Stay ahead in the battle against security breaches and regulatory complexities with our industry-leading, up-to-date content, ensuring a proactive and engaging approach to secure code education.
Trust Agent:AIソリューション概要
Empower your development team with Secure Code Warrior, the agile learning platform designed to tackle the evolving challenges of application security. Stay ahead in the battle against security breaches and regulatory complexities with our industry-leading, up-to-date content, ensuring a proactive and engaging approach to secure code education.
OWASP Top 10 API 2023:スマートな開発者のための戦術ガイド
APIセキュリティの最新情報を探求しましょう。2023年版OWASP Top 10ガイドを深く掘り下げてください。コーディングスキルを向上させ、脆弱性に対処し、進化し続けるAPI開発の世界でアジャイル性を維持しましょう。洞察に満ちた旅のために今すぐダウンロードしてください!
5つのステップで開発者エンゲージメントの秘密を解き明かす
当社のPieter Danhieuxが説明したように、5つのステップで開発者エンゲージメントの秘密を解き明かしましょう。今すぐダウンロードして、繁栄する開発者コミュニティへのロードマップを発見してください。
AIによる自動化:シチズンデベロッパー向けガイド
Start shifting left with developer-driven security. This handbook will show you how to engage with developers to upskill and increase their security knowledge, as well as how to go about measuring impact to write more secure code.
ソフトウェアはあなたの同僚:アクセス制御とAPIセキュリティを強化する新しい視点
APIは欠陥のある人間のように振る舞います。それらをそのように扱うことが、より良いサイバーセキュリティの鍵なのでしょうか?
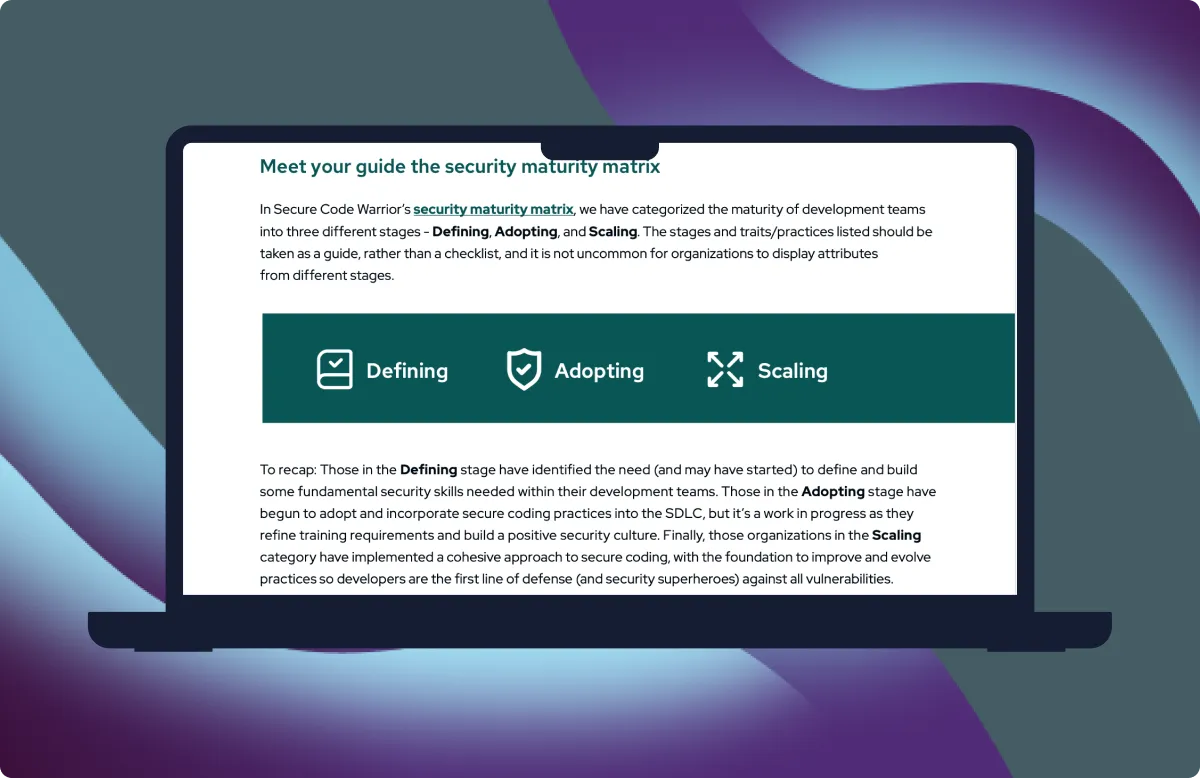
脆弱性スポットライト:次世代開発者のための安全なナビゲーションガイド
大規模言語モデルは、速度と生産性において圧倒的な利点をもたらしますが、企業に否定できないリスクももたらします。従来のセキュリティガードレールだけでは、この氾濫を抑えるには不十分です。
開発者のセキュリティ成熟度マトリックス
開発チームのセキュリティ成熟度の構築は、段階的にアプローチできます。当社の経験に基づき、定義、採用、および拡張という3つの段階における一般的な慣行を特定しました。
開発チームにおけるセキュリティ成熟度の重要性
開発チームのセキュリティ成熟度を評価して理解することで、組織は適切な利害関係者、プロセス、テクノロジーを備えた計画を策定し、必要なスキルと機能を構築およびサポートすることができます。

開発チームのセキュリティ成熟度
開発チームのセキュリティ成熟度は、その過程に現実的な目標がある継続的な改善サイクルであるべきです。開発チームがセキュリティの成熟度を高めるにつれて、手戻りの量が減り、リスクが最小限に抑えられます。

レポート:2022年の開発者主導セキュリティの現状
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
ホワイトペーパー:ソフトウェアセキュリティを向上させるための課題(と機会)
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
概要:開発者主導のセキュリティへの包括的なアプローチ
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Secure Code Warriorにおけるセキュリティとプライバシー
Secure Code Warriorは、当社の情報資産およびお客様の資産を保護することに尽力しています。当社は、情報セキュリティの管理に対してリスクベースのアプローチを採用しています。詳細については、ホワイトペーパーをお読みください。
再現性のあるセキュアコーディングスキルでシフトレフト(およびコンプライアンスの達成)を実現する
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
セキュアコードの定義
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
アダプティブラーニング データシート
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

エージェント型開発ライフサイクルのセキュリティ保護
Zero-day attacks can be the stuff of nightmares, but when an organization commits to using all available tools in their security arsenal towards a preventative strategy, security professionals can sleep a little easier.
ホワイトペーパー:AI時代の信頼
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Trust Score 製品概要
SCW Trust Scoreは、開発者主導のセキュリティプログラムの健全性を定量化する指標を提供します

セキュリティとプライバシーに関するホワイトペーパー
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
CISO/CTO説得キット(デモ開始用)
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
OWASP Top 10 API:スマートな開発者のための戦略
コード内の一般的なAPIセキュリティの脅威を打ち負かすための実践的なガイドをダウンロードしてください。
AppSecリスクとAIトラストインデックス
主要なAIモデルは、現実世界の脆弱性パターンに対してどのようなパフォーマンスを示すのでしょうか。SCW AI トラストインデックスは、トップモデルのセキュリティ態勢を明らかにします。
AppSecがいかに脆弱性を減らし、コンプライアンスを達成できるか - より大きな課題に取り組む自由を与える
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
バイヤーズチェックリスト:セキュア開発学習プラットフォーム
バイヤーズチェックリスト:セキュア開発学習プラットフォームは、セキュア開発学習プラットフォームの評価を検討している意思決定者およびテクノロジーバイヤーを対象としています。
Shared Assessments SIG Lite アンケート
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
SCW ペネトレーションテストの概要
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
SCW サイバー保険証明書
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
対応から予防への移行:変化するソフトウェアセキュリティの状況 2021年 - ホワイトペーパー
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
サイバーセキュリティ大統領令:開発者のスキルを活用してソフトウェアセキュリティを向上させるための意図的なアプローチ
この大統領令は、機能的なサイバーセキュリティの多くの側面に触れていますが、特に開発者の影響力と、検証されたセキュリティスキルと認識を持つことの必要性について初めて具体的に概説しています。

FSQS-NL 証明書
Secure Code Warriorは現在FSQS-NLに登録されています。この登録は、金融業界内の規制を順守するための当社の継続的な取り組みにおける重要なマイルストーンです。

プラットフォームアーキテクチャ図
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

情報セキュリティポリシー
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

CAIQ アンケート
Secure Code Warriorは、デューデリジェンスの自己評価の結果に基づいて、一般公開されているコンセンサス評価イニシアチブアンケート(CAIQ)に回答しました。
DevSecOpsのスーパーボウル:セキュリティチャンピオンが、開発後期の脆弱性に対する勝利に向けてチームをどのようにサポートできるか
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
エグゼクティブラウンドテーブルホワイトペーパー - Visma & Blue Prism
2020年がソフトウェアセキュリティの捉え方をどのように変えたか、Vismaとのエグゼクティブラウンドテーブル。

コードが安全だと想定した場合に何が起こるか?検証されていないAIの危険性
AIコーディングアシスタントの時代は本格的に始まっていますが、開発者の生産性が向上する一方で、生成されるコードの品質には赤信号が点滅しています。この概要では、スタンフォード大学の最近の研究を分析しています。

グローバル金融機関のチームがセキュアコーディングコンテストで直接対決。
世界的な金融機関が、楽しくインタラクティブなトーナメントを利用して、世界中で銀行アプリケーションを保護することの重要性をどのように推進したかをご覧ください。
ミッション - 現実世界のシミュレーションで不十分なコードの影響を体験する
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
コース - セキュアコーディングのスキルとコンピテンシーを構築する
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
エージェント型SDLCのためのCISOガイド
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
AI開発者ハンドブック
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
SCW AI 導入モデル
The ten most common security vulnerabilities don’t stand a chance against secure development superheroes like you. This free eBook is your ultimate field guide to understanding each infamous entry in the OWASP Top 10 2021, gaining insight into how each bug operates.
AIコーディングアシスタント:AppSecにとってどのような意味があるのか?(eブック)
GenAIとLLMが現在のアプリケーションセキュリティの状況を根本的にどのように変化させているかについての分析。Secure Code WarriorのCEOであるPieter Danhieuxからの最新の視点をご覧ください。
ゼロからヒーローへ:開発者がセキュリティチャンピオンになる方法
セキュリティの原則と実践に関する堅牢なトレーニングを提供することで、開発者はセキュリティの初心者からセキュリティのチャンピオンへと変貌し、脅威がセキュリティインシデントにつながる前に、脅威を特定、軽減、防止できるようになります。

トーナメント - 楽しくインタラクティブなセキュアコーディングコンペティション
Secure Code Warriorトーナメントは、前向きなセキュリティ文化を構築するための魅力的で楽しい方法です。コーディングコンテストを実施することで、リモート開発者とハイブリッド開発者の両方を対象としたイベントを開催し、開発者のスキルレベルを評価し、セキュリティチャンピオンを特定することができます。
DevSecOps成功への5つのステップ:AppSecプロフェッショナルがドリームチームで成功する方法
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

ソフトウェアセキュリティプログラムを改善する最も早くて簡単な方法
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
クリエイティブなCISOのためのセキュリティプログラム変革ガイド
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
PCI-DSSコンプライアンスの苦痛を軽減するホワイトペーパー
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Secure Code Warrior の紹介
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
開発者がセキュアなコードを記述できるようにする
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

開発者に防衛の最前線となる力を与え、組織のセキュリティ態勢を強化する
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

評価 - 開発者のセキュアコーディングスキルをベンチマークし、セキュリティ態勢を構築します。
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
AppSec チェックリスト
AppSecチェックリストをダウンロードして、セキュリティの命綱が必要かどうかを確認してください。
セキュリティ向上プログラムを展開する前の6つの重要なステップ
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

2019年 AppSec トレンドレポート
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
