

Insights from experts shaping secure development
Access expert content on secure coding, AI governance, and software risk management.

SDLC における AI:過度な期待とセキュリティの現実の分離
KnowBe4 との提携による SDLC における AI:Kawin Boonyapredeeto と Pieter Danhieux が AI コードセキュリティリスクを解説します。
ジャーマン OWASP デイ 2026
Secure Code Warrior はジャーマン OWASP デイ 2026 をスポンサーし、セキュアな開発、運用、テストのベストプラクティスを共有します。
アデレードSEC (AdelaideSEC)
Secure Code Warrior は AdelaideSEC でセキュアコーディングトーナメントを開催します。開発者や専門家が実戦形式で競い合います。
Black Hat USA 26
Secure Code Warrior はラスベガスの Black Hat USA 2026 に出展します。CEO Pieter Danhieux、CCO Fatemah Beydoun らが現地にいます。
FS-ISAC APAC サミット
2026年7月14〜15日にシンガポールで開催される FS-ISAC APAC サミットをスポンサーするのが楽しみです!ブース #8 にお立ち寄りください。
Gartner セキュリティ & リスクマネジメント サミット 2026
2026年9月22〜24日にロンドンで開催される Gartner セキュリティ & リスクマネジメント サミットをスポンサーできることに興奮しています!

OWASP グローバル AppSec USA
2026年11月5〜6日にサンフランシスコのハイアットリージェンシーで開催される OWASP Global AppSec USA 2026 のシルバースポンサーを務めることを誇りに思います!

開発者主導のセキュリティの未来:Checkmarx SAST と SCW の統合
この統合は、脆弱性の検出と修復の間のギャップを埋め、必要な瞬間に正確な学習リソースを開発者に提供します。

ソフトウェア開発における DevSecOps の不可欠な役割
SCW Coffee Shop @RSAC24提供:DevSecOps の思想的リーダーや業界専門家とともに、今日の開発における DevSecOps のクリティカルな役割を掘り下げます。
シャドーAIからAIソフトウェアガバナンスへ:コードベース全体での可視性の奪還
Secure Code Warrior の CTO Matias Madou とプロダクトディレクターの Tamim Noorzad から、大規模な AI 支援開発の管理に必要な視点と可視性について学びましょう。

OWASP グローバル AppSec ヨーロッパ
2026年6月22〜26日にウィーンのオーストリアセンターで開催される25周年記念 OWASP Global AppSec EU カンファレンスをスポンサーできるのが待ちきれません!

OWASP BASC
4月11日にマサチューセッツ州ボストンで開催される OWASP BASC をスポンサーできることを嬉しく思います。専門家が集まるプレミア会議です。

OT サミット・マドリード
AI、クラウド、安全な情報管理が新世代のインテリジェント企業をどのように推進しているかを示す OpenText Summit Madrid 2026 にご参加ください。
サイバーセキュリティ サミット
サイバーセキュリティサミットは、トップクラスの専門家、革新者、出展者が集まり、最新トレンドとITレジリエンス戦略を披露する会議です。
開発者のセキュリティ熟達:統合ASTとスキルアップによる脆弱性修正の加速
脆弱性を見つけるだけでなく、根本的に修正しましょう。真の Secure by Design を実現するためのアプローチをご紹介します。

自信を持ってシフト左へ:開発者ワークフローへのセキュリティのネイティブ組み込み
SCW と Checkmarx の専門家を結集し、開発プロセスにセキュリティを円滑に統合するためのベストプラクティスと戦略を共有します。
プロダクトセキュリティ・バーチャルサミット
今年1月28日に開催されるプロダクトセキュリティ・バーチャルサミットで Cycode とパートナーシップを組むことを誇りに思います。AI 時代のソフトウェアの未来を探ります。

フィッシャパルーザ (Phishapalooza)
アメリカがん協会を支援するため、第18回年次 Phishapalooza に参加できることを光栄に思います。アイスフィッシングや資金調達活動を楽しみにしております。
OWASP LASCON
テキサス州オースティンで開催される OWASP LASCON 2026 のゴールドスポンサーであることを誇りに思います!ノーリス・コンファレンス・センターでお待ちしております。

ニューヨーク・セキュアコード・ショーダウン
SCW、OWASP、AWS は、2026年2月19日(木)に開催されるニューヨーク・セキュアコード・ショーダウンに皆様を招待します!

ゴールドコースト BSides
オーストラリアのゴールドコーストで開催されるハンズオンコンペティションで、実際の脆弱性を特定・修復する能力をテストしましょう。
BSides フランクフルト
フランクフルトのゲーテ大学キャンパスで開催されるハンズオンコンペティションに参加し、実際の脆弱性を特定して修正する能力を試してみましょう。
RSA カンファレンス
RSA Conference 2026 に向かっています。開発者が最初からセキュアなコードを書くスキルを支援します。サウスエキスポホールのブース #250 でお会いしましょう。

FS-ISAC FinCyber Today カナダ
FS-ISAC FinCyber Today カナダで開発者リスク管理についてお話する準備ができています。開発者のセキュアコード学習を強化してリスクを軽減します。
Threat Modelling with AI: Turning Every Developer into a Threat Modeler
Threat modeling with AI: how to turn every developer into a threat modeler, straight from their IDE.

開発者の特定
カリキュラムおよびオンボーディングマネージャーの Katelynd Trinidad が、コードコントリビューターを特定してセキュアコードトレーニングを受けさせるための手法を紹介します。

AppSec DevSec DevSecOpsにおけるブランドの力(頭字語の意味とは!?)
AppSecにおいて持続的なプログラムの成果を上げるには、単なる技術以上のもの、つまり強力なブランドが必要です。力強いアイデンティティは、取り組みが共感を呼び、開発者コミュニティ内での持続的な参加を促進します。

Vibe Coding:AI時代に合わせてAppSec戦略を適合させる実践ガイド
実用的なトレーニング優先のアプローチにより、AppSecマネージャーが障害ではなくAI推進者となる方法をオンデマンドでご視聴ください。AIコーディングアシスタント時代において、Secure Code Warrior(SCW)を活用してAppSec戦略を戦略的に更新する方法をご紹介します。

アジャイル学習で開発者リスクを管理するための CISO ガイド
ESG の最近の研究では、回答者の 54% が既知の脆弱性を持つコードを本番環境にリリースしていると述べています。学習プログラムはリスクを減らしていますか?

Secure Code Warrior & GuidePoint Security
Come visit our booth #336 at SecTor 2025 in Toronto at the Metro Toronto Convention Centre! Us along with other security professionals will be sharing our latest research and techniques on underground threats and corporate defenses.

OWASP ニュージーランド・デイ
オークランド大学キャンパスで開催される OWASP ニュージーランド・デイに参加できることを嬉しく思います!堅牢なアーキテクチャに焦点を当てています。

OWASP グローバル AppSec 2025 USA
ワシントンDCの中心部にあるマリオット・マーキスのエキスポスペースでお待ちしております!800人以上の専門家とつながるチャンスです。

OWASP ベネルクス・デイズ
ベルギーで開催される OWASP BeNeLux Days のブースにお越しください!セキュリティ、DevOps、クラウドの専門家による技術トークを提供します。
メルボルン AppSec & DevSecOps サミット
メルボルン AppSec & DevSecOps サミットで、セキュリティや開発リーダーの皆様とアイデアを共有できることを楽しみにしています!
FS-ISAC 秋季サミット
10月7日(火)午前8時より FS-ISAC 秋季アメリカサミットの朝食会ブースにお越しいただき、デザインによるセキュリティについて語り合いましょう。

CISO Inspired サミット アメリカ
CISO Inspired Summit New York 2025 でサイバーセキュリティリーダーとつながり、積極的な防御戦略を掘り下げましょう。

CISO Inspired サミット イギリス
CISO Inspired Summit UK 2025 でサイバーセキュリティリーダーとつながり、デジタル防御を強化し、堅牢な戦略を構築しましょう。

BSides ボーンマス
BSides Bournemouth はコミュニティ主導のサイバーセキュリティ会議です。洞察に満ちた講演やハンズオンアクティビティをお楽しみください。

Black Hat USA
ラスベガスの Mandalay Bay で開催される Black Hat USA で当社役員陣にお会いください!AI/LLM セキュアコードリスクについて話し合えることを楽しみにしています!

OWASP グローバル AppSec ヨーロッパ 2025
OWASP Global AppSec EU のブース #G08 で、デザインによるセキュリティ原則と効果的なリスク管理が次世代サイバーセキュリティをどう形成するかをご覧ください。
FS-ISAC EMEA サミット
5月21日午前8時より FS-ISAC EMEA サミットの朝食会ブースにお越しいただき、デザインによるセキュリティと開発者中心のリスク管理について語り合いましょう。
サイバーセキュリティ・サミット、ハンブルク
予防的セキュアコーディングがセキュリティ体制を向上させながらソフトウェア開発を加速する方法について話し合いましょう。

OpenText サミット・マドリード
Secure Code Warrior は4月10日に開催される OpenText Summit Madrid 2025 を後援することを誇りに思います!リーダーが集まり変革を探ります。
オーストラリア・サイバー・エクスチェンジ (ACE25)
4月3日、CEO の Pieter Danhieux が第1回オーストラリア・サイバー・エクスチェンジ ACE25 で登壇し、オーストラリアのサイバー能力強化について語ります。

セキュリティのシフト左:ソフトウェア開発における DevSecOps の不可欠な役割
このウェビナーでは、DevSecOps の非常に重要な役割と、開発ライフサイクルの初期段階でセキュリティを統合する戦略について掘り下げます。

OWASP SnowFROC
デンバーのプレミアアプリケーションセキュリティ会議 SnowFROC '25 にご参加ください!約400人が集まるこの1日イベントで最高の体験を。

BSides リンブルフ
今年の3月14日に BSides リンブルフでトーナメントを開催します!深い議論、ハンズオンデモ、コラボレーションを促進するイベントです。
第2回 2025年 OWASP メイン州セキュアコーディングトーナメント
OWASP メイン州と Secure Code Warrior が提携し、第2回 OWASP メイン州セキュアコーディングトーナメントを開催します!初心者からシニアレベルまで、すべてのソフトウェア開発者とAppSec専門家を歓迎します。

NDC Security 2025
オスロの中心部で最先端のトピック、ハンズオンワークショップ、ピアネットワーキングに飛び込みましょう。スポット H でお待ちしております!

RSA カンファレンス 2025
RSAC 2025 のブース #2353 にぜひお越しください。革新的なソリューションを探索し、会話に参加してください。

DevSecOps360 ロンドン
2025年1月22日(水)、IBM Innovation Studio ロンドンで開催されるパートナーエコシステム内の DevSecOps 統合ビジョンイベントにご参加ください。

Black Hat Europe
ロンドンの ExCeL で開催される Black Hat Europe にご参加ください

OWASP ベネルクス
SCW は今年のカンファレンスをサポートできることを誇りに思います。ブースにお立ち寄りいただき、OWASP Top 10 を克服する方法をご覧ください。

ジャーマン OWASP デイ 2024
ドイツのライプツィヒで Secure Code Warrior とともに OWASP からの素晴らしい洞察や2025年のソフトウェアセキュリティの方向性を共有しましょう。

DevSecOps 360 トロント
SCW、IBM、Black Duck、Iruis Risk、Contrast に参加して、組織が脆弱性を最小限に抑えながら開発を加速する方法を学びましょう。

クラウド & サイバーセキュリティ エキスポ、パリ
フランスにおけるプレミアサイバーセキュリティイベントのシルバースポンサーを務めることを嬉しく思います。会場でお会いできるのを楽しみにしています。

OpenText World 2024
Secure Code Warrior と OpenText に参加して、世界中の企業が SAST 結果を活用してセキュアコーディングのアジャイルな学習体験を生み出す方法を学びましょう。
DevSecOps 360 ロンドン
SCW、IBM、BlackDuck、IriusRisk に参加して最新の統合を体験し、企業が組織の生産性をいかに実現したかを学びましょう。

AppSecDay ストックホルム
Secure Code Warrior、OpenText、Sonatype とともに、オープンソースのナビゲーション、NIS2への準拠、AIとDevSecOpsに関する議論にご参加ください。
DevSecOps 360 ミラノ
自動化がより迅速で安全な開発を推進する方法をご紹介します。脆弱性を減らすための実践的なソリューションに飛び込みましょう。

チャリティ プロアマ スクランブル
KidSport Québec を支援し、より多くの子供たちがスポーツに参加できるよう、素晴らしい目的のためにゴルフ大会を開催します。
AppSec Day ユトレヒト
アプリケーションセキュリティが進化するにつれ、組織はリアルタイムの脅威検知と予防のために AI ソリューションをますます統合しています。Secure Code Warrior とパートナーにご参加ください!

Secure Code Warrior ユーザーグループ EMEA
他の管理者とつながり、開発者主導のセキュリティプログラムの管理方法を学ぶコミュニティです。ヒントやコツを学びましょう!

SANS Secure ジャパン 2025
SANS が2月17〜22日に東京にやってきます。ブースにお越しいただき、当社の最先端 AppSec ソリューションと学習プラットフォームをご覧ください。

OWASP 2024 グローバル AppSec
Global AppSec US カンファレンスは新しいトレンドで盛り上がります。サンフランシスコのブースで最新製品のデモをご覧ください。

DevSecOps トランスフォーメーション
DevSecOps により、開発ライフサイクルの初期段階でセキュリティ問題を特定し、最も大きな影響を与える開発者に直接提示できます。

サイバーセキュリティ・サミット
ビジネス向けサイバーセキュリティのデジタルソリューションを提供する革新的なプロバイダーと専門家が結集します。

Blackhat USA
27年目を迎える Black Hat USA がラスベガスに戻ってきます。選りすぐりのブリーフィング、オープンソースツールのデモ、ビジネスホールなどが用意されています。

AppSec & DevSecOps サミット
メルボルン AppSec および DevSecOps サミット 2024 でセキュリティ戦略を統合し、強化しましょう。セキュリティスキルを高め、アプリケーションとクラウドセキュリティの革命の最前線に立ちましょう。

SCW Trust Score でセキュリティプログラムの現状をベンチマーク
急速に変化するセキュリティ環境において、セキュリティプログラムの立ち位置を理解することは極めて重要です。CTO Matias Madou とともに SCW Trust Score について話し合いましょう。

ノーディック IT セキュリティ
スカンジナビアで最も評判の高いサイバーセキュリティサミットである Nordic IT Security は、17年間にわたり地域のナビゲーション役を務めています。

ベルギー・コーヒーアワー
ベルギーからの RSAC 参加者のために、3月7日(火)午後3時より特別イベントを開催します。CEO Pieter Danhieux や CTO Matias Madou とともに素晴らしいコーヒーを楽しみましょう。

2026年のセキュリティ・チャンピオン:高め、関与させ、保護する
新規プログラムの立ち上げ、既存プログラムの拡張、あるいは機能の探求を目的としている場合でも、このウェビナーは実践的な洞察を提供します。

SANS ネットワークセキュリティ 2026
9月10〜15日にラスベガスで開催される SANS Network Security 2026 にご参加ください。最新の課題に焦点を当てた実践的なセッションを提供します。

RSA カンファレンス 2024
可能性の芸術がここにあります!ブース 5179 にお立ち寄りいただき、脆弱性を53%削減する方法をご覧ください。

RSAC24 で SCW 経営陣と面談
当社の共同創業者と役員陣が5月6日〜7日にサンフランシスコ最高のコーヒーを楽しみながらミーティングを行います。

開発者と AI を信頼する
SCW Coffee Shop @RSAC24提供:共同創業者兼 CTO Matias Madou と業界の専門家が、開発者内でのセキュリティスキル測定の課題について語ります。

SCW Trust Score でセキュアコーディングプログラムの有効性を定量化する方法
SCW Coffee Shop @RSAC24提供:Patrick Collins と Junie Dinda とともに、セキュアコーディングプログラムの風景を再定義する新しい SCW Trust Score を深掘りします。

Carolina Hurricanes と GuidePoint
GuidePoint のパートナーとともにアイスホッケーの試合と AppSec のトークを楽しみましょう!

ベイエリア・ベンダー・ハッピーアワー
詳細情報はまもなく公開されます。

セキュリティにおける女性リーダー
SCW Coffee Shop @RSAC24提供:共同創業者兼CCOのFatemah Beydounと業界の女性リーダーのパネルに参加し、セキュリティにおけるジェンダーギャップを修正するためのシフト左について話し合います。
コーディングに生成AIを使用することの良さ、悪さ、そして醜さ
このウェビナーでは、Secure Code Warrior CTO 兼共同創業者の Matias Madou とセキュリティ研究者の Jon Helton が力を合わせて生成AIを解読します。
スコシアバンク・アリーナ プライベートスイート
スコシアバンク・アリーナのプライベートスイート体験にご参加ください!排他的な環境で試合を観戦しながら AppSec について語り合いましょう。
アプリケーションセキュリティ・ハンズオンワークショップ
AWS、Contrast Security、Arctiq とのパートナーシップにより、インタラクティブなハンズオン AppSec ワークショップをお届けします。

バーチャルワインテイスティング - オハイオ
GuidePointやその他のパートナーとともに、Silver Oaks Wineryのバーチャルワインテイスティングにご参加ください。
DevSecOps 360 - リヤド
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
DevSecOps 360 - ミュンヘン
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
DevSecOps 360 - ドバイ
IBM、Synopsys、IriusRisk とのパートナーシップにより、パートナーエコシステム内での DevSecOps 統合ビジョンを共有します。
シフト左テスティング
脆弱性を早期に検出し、修復を加速します。SCW、Cyberark、Checkmarx は一貫したシフト左アプローチで提携しています。
次世代の保護:AIコーディングの脆弱性に正面から立ち向かう
AI の登場はソフトウェア開発の風景を変えました。しかし、これは新たな課題ももたらします。AI は単にコードを書くのではなく、脆弱なコードを書きます。
人工知能時代におけるセキュアコーディング
AI がコード生成を加速する中、堅牢なセキュリティを維持することはかつてないほど重要です。AI 開発の敏捷性とセキュアコーディングのバランスを探る炉辺対談。
Secure Code Warrior ユーザーグループ NA
他の管理者とつながり、開発者主導のセキュリティプログラムの管理方法を学ぶコミュニティです。ヒントやコツを学びましょう!
Secure Code Warrior ユーザーグループ
Secure Code Warrior ユーザーグループへようこそ!製品アップデート、刺激的な顧客の成功事例、インタラクティブなパネルディスカッションをお届けします。
SANS クラウドセキュリティ・トレーニング
SANS クラウドセキュリティ・トレーニングが4月13〜18日にバージニア州アレクサンドリアにやってきます。集中的な実践トレーニングが行われます。
DEVOPS カンファレンスに参加しましょう
3月8〜9日に開催される DEVOPS カンファレンスに参加し、洞察力に満ちた話を聞き、トーナメントに参加するチャンスを手に入れましょう!今すぐ無料チケットを獲得。
セキュリティは開発者の問題か?
テクノロジーが爆発的に増加し、そのすべてを保護する必要があります。しかし、セキュリティチームには急速な進化に対応する人手が不足しています。
包括的な開発者主導のセキュリティでソフトウェアリリースのスピードを向上
AWS + Secure Code Warrior が開発者のコード出力の量と質を高めることの重要性について解説。

包括的な開発者主導のセキュリティでソフトウェアリリースのスピードを向上
悪用可能な脆弱性に起因するセキュリティ侵害が増加する中、組織はリスクを最小限に抑え、リリース速度を高める方法を模索する必要があります。
オープンソースコンプライアンスにおける回避と修復のギャップを埋める方法
このギャップを埋めることは、エンジニアリングチームがオープンソースソフトウェアの影響をよりよく理解するために重要です。

強固な基盤を持った AppSec プログラムの構築方法
AppSec プログラムの戦略開発においてベースラインを設定することの重要性とアプローチ。

4歳の誕生日おめでとう、セキュア・コード・ウォリアー、ユー・チーキー・リトル・トドラー
娘と会社が年をとるほど、スタートアップの旅と「初めて」の親の旅との間には、非常に多くの類似点があることに気づきます。私は今、どちらも4年目です。.pi
コーダーがセキュリティを征服する:シェア&ラーニングシリーズ-クリックジャッキング
それでは、クリックジャッキングのしくみ、なぜ危険なのか、そしてあなたのような開発者がクリックジャッキングを防止するためにできることについて見ていきましょう。
コーダーズ・コンカー・コンカー・セキュリティ:シェア&ラーニング・シリーズ-OS コマンド・インジェクション
OS コマンドインジェクション攻撃は、初級レベルの熟練度の低いハッカーが実行する可能性があり、セキュリティチームが経験する最も一般的な弱点の 1 つとなっています。ありがたいことに、攻撃を阻止するための非常に効果的な方法は数多くあります。
コーダーがセキュリティを征服:共有して学ぶシリーズ-セッション管理の弱点
セッションは、Web を使用する際の優れたユーザーエクスペリエンスの鍵です。ただし、セッションを誤って管理すると、攻撃者が悪用できるセキュリティホールが発生する可能性があります。

開発者トーナメント:セキュリティ文化とエンゲージメントを向上させるためのAppSecの秘密兵器
そろそろ警備のイメージチェンジをする時だと思わない?会話を変えて、すべてがもう少しポジティブになるのと同じくらい簡単です (楽しいことは言うまでもありません!)双方にとって、特に開発チームにとって。
コーダーズ・コンカーズ・コンカー・セキュリティ:シェア&ラーニング・シリーズ-パディング・オラクル
Padding Oracleは、オルタナティブ・ロック・バンドとしては非常に悪い名前のように聞こえますが、実際には攻撃者が暗号鍵を知らなくても情報を復号化するために悪用できる脆弱性です。
コーダーがセキュリティを征服する:共有して学ぶシリーズ-LDAP インジェクション
悪意のあるユーザーが LDAP クエリを操作できると、問題が発生する可能性があります。これを行うと、受信側のサーバーを騙して、通常は許可されないような無効なクエリを実行させたり、パスワードなしで無効なユーザーやセキュリティレベルの低いユーザーに高レベルまたは管理者アクセスを許可したりする可能性があります。

アプリケーション・セキュリティ・バッドランドで必要な変化:私の 2019 年の予測
私たちが直面している本当の戦いは、スクリプト小僧や危険な組織化されたサイバー犯罪シンジケートに対するものではありません。データ侵害が起こっていることを、より多くの人々に気にかけてもらうことです。
コーダーズ・コンカーズ・コンカー・セキュリティ:シェア&ラーニング・シリーズ-無制限のファイルアップロード
サイバーセキュリティでは、攻撃者は無制限のファイルアップロードをサポートすることが許可されているアプリケーションやプログラムをすぐに悪用できます。そして、その結果は壊滅的なものになる可能性があります。
コーダーがセキュリティを征服する:共有して学ぶシリーズ-NoSQL インジェクション
NoSQL データベースはますます人気が高まっています。そのスピードと非構造化データの扱いやすさは否定できませんが、利用が広まるにつれ、より多くの脆弱性が表面に出てくることは避けられません。
コーダーがセキュリティを征服する:共有して学ぶシリーズ-クロスサイトリクエストフォージェリ
CSRF 攻撃はかなり複雑で、成功するには複数のレイヤーが必要です。言い換えると、攻撃者に有利に働かせるためには、多くのことを突破しなければならないということです。それにもかかわらず、これらは非常に人気があり、収益性の高い攻撃ベクトルです。
セキュリティを克服するコーダー:共有と学習-SQL インジェクション
攻撃者はSQLインジェクションを使用しています。SQLインジェクションは最も古いものの1つです(1998年以降!)そして、最も厄介なデータ脆弱性は、世界中の何百万ものデータベースにある機密情報を盗み、改ざんすることです。

プライバシーとセキュリティを混同する:致命的な間違い
オンラインプライバシーがセキュリティなしで存在しようとすると、混乱が支配します。ロス・ウルブリヒトに聞いてみてください。

金融機関がセキュアコーディングにおける開発者のスキルアップを主導している理由
Wox: requéén

SQLインジェクションがアプリケーションセキュリティ界のゴキブリである理由(およびCISOがSQLインジェクションを完全に根絶する方法)
ゴキブリは基本的に何にでも生き残ることができるというよく知られた理論があります。核爆発でさえも。

DevSecOpsの明るい未来とは?思っているよりも近い
コードの脆弱性を発見するソリューションは数多くありますが、セキュリティでは、そもそもミスを防ぐためのセキュリティガイドラインに従うよう開発者に教えることに重点を置く必要があります。

ゲーミフィケーションがソフトウェアセキュリティのレベルアップの鍵となる理由
私たちは話題を変え、セキュリティをすべての開発者の仕事に欠かせないものにするよう努めなければなりません。そのための最善の方法の 1 つは、ゲーミフィケーションなどを通じて開発者にセキュリティに関する権限を与え、関与させることだと思います。

侵害が増え、問題が増える:サードパーティーアプリへの信頼の代償
セキュリティを企業のイノベーションの道における苛立たしい障害と考えるのはやめなければなりません。


一部のCISOは、セキュリティスキルの不足をチャンスに変えています
開発者が最初から安全なコードを書けるようにすることは、CISOにとってセキュリティの苦境からある程度プロアクティブなコントロールをつかむ機会であり、セキュリティチームと開発チームの両方にとって、迅速、簡単、かつ測定可能な改善の機会でもあります。
石油・ガス業界の「爆発的な」サイバー攻撃は生命を脅かす
捜査官によると、爆発を防いだのは攻撃者のコンピューターコードの間違いだけだという。

Web アプリケーションのセキュリティ上の欠陥の原因となる、忘れ去られた人的要因
安全なコードがなぜ重要なのか、安全でないコードがもたらす影響、そして最も重要なのは、そもそもこれらの脆弱性をそれぞれのプログラミングフレームワークに書き込まないようにする方法について、誰も教えてくれなかったら、開発者はどのようにして安全なコードを書くべきなのでしょうか。
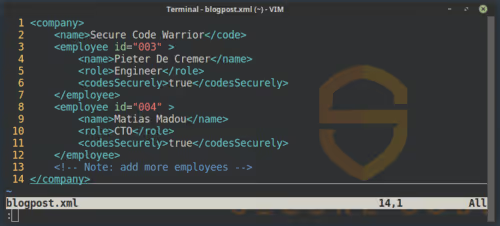
セキュア・コーディング技法:XML データの処理、第 1 部
XML および XML スキーマの仕様には、複数のセキュリティ上の欠陥があります。同時に、これらの仕様は XML アプリケーションを保護するために必要なツールも提供します。XML スキーマは XML 文書のセキュリティを定義するのに使用しますが、さまざまな攻撃に利用される可能性があります。

安全なコーディング手法:Zipライブラリのデフォルトの動作がリモートコード実行につながる可能性がある
名前の先頭に「」が付いた zip にファイルを挿入できます。
1 行のコード、100 万ドル
航空電子機器のコード1行を変更するコストは100万ドルで、実装には1年かかります。ボーイング737をベースとした機材を保有するサウスウエスト航空にとっては「破産」することになります。

学術研究から産業界への移行は簡単ではありません
Show 139: Matias Madouがセキュア開発トレーニングとソフトウェアセキュリティテストの研究について語る
Android フルデバイス暗号化技術 | セキュア・コード・ウォリアー
Android のフルデバイス暗号化はすべてのデータを保護してストレージに書き込み、デバイスのロックが解除された後にのみ表示されます。セキュア・コード・ウォリアーから学びましょう。
安全なコーディング手法:タップジャックについて話そう
場合によっては、ユーザーの十分な知識と同意を得てアクションが実行されていることをアプリケーションで検証できることが不可欠です。

採用プロセスを改善するビデオゲーム
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

安全なコーディング手法:カスタム権限の問題
カスタム権限を定義することで、アプリはそのリソースと機能を他のアプリと共有できます。
30万人の開発者が実際に行っているセキュリティ対策とは?
約95,000のアプリケーションにまたがる約30万人の開発者が、ソフトウェア・セキュリティ・イニシアチブ(SSI)の計画、実行、測定にBSIMM8を使用しています。
ユーザー名の列挙を回避する方法 | セキュア・コード・ウォリアー
ユーザー名の列挙とは、ハッカーがブルートフォース攻撃を利用してユーザー名とパスワードの情報を取得することです。セキュア・コード・ウォリアーでユーザー名の列挙を回避する方法を学びましょう。

開発者向けセキュリティトレーニングを効果的に展開する方法:5 つの重要な教訓
効果的な開発者セキュリティトレーニングを展開する方法に関する5つの重要な教訓

コピー/貼り付けは危険なコーディング手法です
この研究の意義は、これまで報告されていなかった、多くの憂慮すべきセキュアコーディングの問題について、経験的証拠を提供したことです。

反対側からこんにちは。バグバウンティハンターへのインタビュー。
バグはまだ残っています。これはすぐに直せるものではない。過去数か月にわたって、バグ報奨金プログラムの一環として、何十もの企業や影響を受けたベンダーに連絡を取り、セットアップを修正してもらいました。

開発者はリスクの第一線なのか、それとも防御の最前線なのか?当社のセキュア・コーディング・チェックリストに照らして御社を評価してください
CIOが企業のアジャイル能力を積極的に構築するにつれて、安全なコーディングスキルはイノベーションの武器となり、持たないことは破壊の手段となるでしょう。

このマインドリーダーから教訓を得て、セキュリティをもう一度楽しくしましょう!
サイバーセキュリティについて経営幹部のトレーニングを行う場合でも、JAVA や C# の開発者がコーディングスキルを確保できるよう支援する場合でも、創造性、ゲーミフィケーション、そして楽しみの場があります。
左へのシフト
開発者がJavaScriptでコーディングしているときにクロスサイトスクリプティングエラーを記述し、その欠陥を作成してから数分以内にそれを検出できる場合

すべての開発者が将来の雇用主に尋ねるべき100万ドルの質問
卒業生であろうとベテランであろうと、すべての開発者が尋ねるべき質問があります。そして、その答えは重要です。

サイバーセキュリティトレーニングと積極的な強化
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
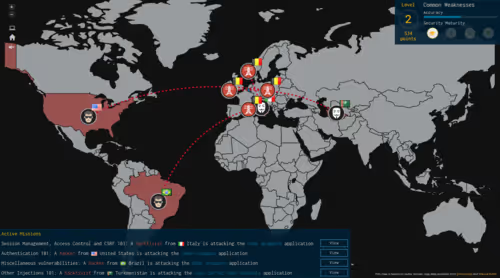
セキュア・コーディング・ガイドラインはどのように進化するか
先週、セキュア・コーディング・ガイドラインを最新のものにするために、Java Springの脆弱性を調査していました。
2016年に明らかになったEquifaxのセキュリティ問題
x0rzという名前の研究者のツイートによると、2016年に話を進めると、セキュリティ研究者がEquifaxのメインWebサイトでクロスサイトスクリプティング(XSS)と呼ばれる一般的な脆弱性を発見しました。
デシリアライゼーションの脆弱性にパッチを適用することの難しさ
この脆弱性は、Strutsがそのようなデータを解析して、Javaプログラミング言語で解釈できる情報に変換する方法に関係しています。
安全なコーディング手法:ファイルを安全に削除する
データ残留とは、何らかの方法で消去されたデータが物理的に残っている状態のことです。
Equifaxのハッキングの根本原因はウェブアプリの脆弱性です
繰り返しになりますが、Equifaxのハッキングの根本原因はWebアプリの脆弱性です。この種の脆弱性は10年以上前から存在していますが、今日でもなお重大な問題です。
What does it take to be a security champion? Lessons from three tech professionals
Recently we interviewed some of the future leaders in the secure development or “DevSec” world and found their individual career paths into cybersecurity fascinating. For those of you out there wishing to become a security champion, jump into the elusive AppSec realm, or even just learn more about secure coding, here are the stories from three security professionals with a background in development, about how they got interested in security and the security lessons they wish every organization would follow.
Kamer van Koophandelが確立した、大規模な開発者主導型セキュリティのスタンダード
Kamer van Koophandel(オランダ商工会議所)が、役割別の認定制度、Trust Scoreによるベンチマーク、そしてセキュリティを全員で担う文化を通じて、どのようにセキュアコーディングを日常の開発業務に組み込んだかをご紹介します。
ゴールドを目指して:Paysafeで高まるセキュアコーディング基準
PaysafeとSecure Code Warriorのパートナーシップにより、開発者の生産性が45%向上し、コードの脆弱性が大幅に削減された事例をご覧ください。
DigitalOcean Decreases Security Debt with Secure Code Warrior
DigitalOcean's use of Secure Code Warrior training has significantly reduced security debt, allowing teams to focus more on innovation and productivity. The improved security has strengthened their product quality and competitive edge. Looking ahead, the SCW Trust Score will help them further enhance security practices and continue driving innovation.
Devlympics 2023:振り返り
Devlympics 2023のレポートで結果をご覧ください。参加した各業界における開発者のエンゲージメント、技術スタックや言語のトレンド、そしてSecure Code Warriorが主催するこの年次グローバルイベントで取り上げられた主要な脆弱性やCWEについて詳しく解説します。

セキュリティ文化の統一:Sageはいかにしてアジャイルなセキュアコーディング学習でセキュリティチャンピオンプログラムを構築したか
Sageが柔軟かつ関係性を重視したアプローチでセキュリティを強化し、200名以上のセキュリティチャンピオンを育成して、測定可能なリスク低減を実現した事例をご紹介します。

セキュリティチャンピオンへの道:Workdayはいかにしてアジャイル学習で開発者のスキルアップを実現したか
WorkdayがSecure Code Warriorのアジャイル学習を通じて、どのように開発者トレーニングを変革したかをご紹介します。Workdayは、言語別の実践的な教育を開発者に提供することで、SDLCの初期段階における脆弱性を削減しました。セキュアなコード文化を構築するための、彼らの素晴らしい成果と重要なポイントをご覧ください。
タレスはいかにして開発者主導のセキュリティを実現したか
本ケーススタディでは、タレス(Thales)がアジャイルなセキュアコーディング学習プログラムのために、人、プロセス、テクノロジーをどのように統合し、開発者が自発的にセキュリティチャンピオンとして活躍できる環境を構築したかをご紹介します。
コルゲート・パルモリーブはいかにして開発者のセキュリティスキルを向上させ、セキュアコーディングの文化を築いたか
小売大手コルゲート・パルモリーブが、デジタルトランスフォーメーションの過程でどのようにアプリケーションセキュリティを再構築したかをご紹介します。セキュアコーディングの課題に直面していた同社は、開発者のワークフローに短時間で学べるコンテキストに応じた学習を取り入れることで、アプローチを刷新しました。
Security as culture: How Blue Prism cultivates world-class secure developers
Learn how Blue Prism, the global leader in intelligent automation for the enterprise, used Secure Code Warrior's agile learning platform to create a security-first culture with their developers, achieve their business goals, and ship secure code at speed

Supercharged Security Awareness: How Tournaments are Inspiring Developers at Erste Group
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
「Game of Codes」が導く、IAGグループのより安全なコーディングの未来
IAGグループは、アジア太平洋地域をリードする数多くの保険会社を傘下に持ち、数百万人の顧客に対して年間約114億豪ドルの保険料で保険契約を引き受けています。

Driving Actionable Awareness: FINRA's Push For Super-Secure Developers
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

革新的なセキュリティ認定体験の創造
機械学習やサイバーセキュリティなど、多岐にわたる分野で実践的かつ最先端のスキルを数千人の従業員が習得できるよう支援する、社内技術教育イニシアチブの構築事例をご紹介します。

Beyond Compliance: Motorola Solutions Drives Winning Security Culture
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

ASRGによる自動車ソフトウェアセキュリティの推進
この包括的なケーススタディでは、Secure Code Warriorのトーナメントを活用して開発者の関与を促し、自動車ソフトウェアに影響を与える主要な脆弱性への意識を高め、複数の言語やフレームワークにわたる指標を収集した事例を紹介します。

Application Security @ NAB | Gamified Security Training: The Key to Scalable Developer Growth
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Security Brief UK: Secure Code Warrior launches Citizen AI training programme
Secure Code Warrior has launched Citizen AI, an AI literacy training programme for non-developer employees intended to support responsible AI adoption across business functions.
ITWire: Secure Code Warrior Launches Citizen AI Cybersecurity Training to Build AI-Ready and Responsible Use Skills Across Business Functions
New AI literacy program equips non-developer employees with the judgment, risk awareness and responsible-use habits needed to safely adopt AI-powered workflows.
VMBlog: Secure Code Warrior Launches Citizen AI Cybersecurity Training to Build AI-Ready and Responsible Use Skills Across Business Functions
Secure Code Warrior announced Citizen AI by Secure Code Warrior, a new AI literacy program designed specifically for non-developer employees to help organizations build a workforce ready for responsible AI adoption. Citizen AI helps organizationsreduce AI-related human risk, support broader enterprise AI governance initiatives, increase employee confidence when using AI and accelerate the safe adoption of AI-powered workflows.
SD Times: Secure Code Warrior Launches Citizen AI Cybersecurity Training
Secure Code Warrior, a leader in AI software governance and developer security upskilling, today announced Citizen AI by Secure Code Warrior, a new AI literacy program designed specifically for non-developer employees to help organizations build a workforce ready for responsible AI adoption.
Secure Code Warrior、全社的なAI活用スキルと責任ある利用を促進する「Citizen AI」サイバーセキュリティトレーニングを開始
新しいAIリテラシープログラムにより、非開発職の従業員は、AIを活用したワークフローを安全に導入するために必要な判断力、リスク意識、責任ある利用習慣を身につけることができます。
SD Times: Citizen Developers Are the New Enterprise Threat Vector. So Why Is Nobody Warning Them?
Organizations are missing a big target when developing governance and developer training programs for AI-assisted software development.
TalkDev: Navigating the Risks: Understanding the Challenges of AI Software Development
AI software development continues to evolve at a rapid pace for developers and their teams. , CEO & Co-Founder at Secure Code Warrior, posits that as the norm shifts from human-written code to AI-assisted coding and agentic workflows, many security teams now face a critical challenge: managing the new risks that autonomous systems introduce.

CIO Influence: Rules for AI in Software Development: The Four-point Framework CISOs Can Adopt Today
The question facing software development shops isn’t whether Generative AI should be used to create software code, or whether the percentage of code generated by GenAI will increase in the near future. That horse bolted in the last 24 months. The question is how to maintain security and compliance while GenAI and artificial intelligence agents are putting software code in play.
VMBlog: National Insider Threat Awareness Month 2026: Expert Insights
Every September, National Insider Threat Awareness Month serves as a timely reminder that some of the most damaging security incidents don’t originate from external attackers breaching the perimeter — they come from within. Whether through malicious intent, negligence, or simple human error, insiders with legitimate access to systems, data, and facilities remain one of the most persistent and difficult-to-detect risks facing organizations today. As hybrid work, AI-powered tools, and increasingly complex IT environments reshape the workplace, the insider threat landscape continues to evolve in ways that demand fresh attention from security professionals.
Information Security Buzz: Architectural intent is the cornerstone for the future of software security
With agentic AI further boosting productivity, human code review becomes a serious bottleneck. Developers need to move upstream, establishing the ground rules to ensure that AI plays by the rules.
Forbes: A New Frontier: NSA Proposes “Security By Design” Considerations For AI Enablement
The cybersecurity industry, which has been advocating for “security by design” principles for more than a decade, stands in wide-eyed amazement at the risks posed by artificial intelligence (AI). As organizations rush to embrace AI enablement, a CISO’s most pressing priority is to avoid becoming a roadblock. However, without effective AI usage and governance, observability and traceability, organizations may be blindsided by their AI risk.
Techpartner.news: Secure Code Warrior introduces framework to govern AI use in software development
Secure Code Warrior has introduced the SCW AI Adoption Model, a framework designed to help organisations govern AI use in software development as the industry shifts from the traditional software development lifecycle (SDLC) toward what the company calls the Agentic Development Lifecycle (ADLC).
DevOps.com: Are LLMs Equally Good (or Bad) at Building Secure Software?
With many software engineering teams moving from AI coding assistants into full agentic AI code generation and increasing the amount of code they produce exponentially, ensuring the security of that code must be a top priority. The study produces practical guidance for organizations that are getting on board the AI-assisted or agentic code development train.

TechRadar Pro: Beware the token trap: Why saving on inference might put your ADLC at risk
Token use can create unexpected, sizeable costs for organizations.
KBI Media: AI Coding Boom Raises Fresh Cybersecurity Risks for Business
AI enables faster development cycles and allows developers to focus on higher-value work. For many businesses, these efficiencies are becoming essential to remaining competitive. The challenge, therefore, is not whether to adopt AI, but how to do so responsibly. Businesses that invest in developer education, governance frameworks, AI observability and robust security controls will be better positioned to capture the benefits while limiting the associated risks.
In AI Today: AI's weakest link isn't the model but the software supply chain
The issue is no longer simply about protecting AI models themselves. Increasingly, attackers are focusing on the software ecosystem surrounding those models, including the development tools, middleware, open-source libraries, and automated deployment pipelines that organisations rely upon every day.

The AI Journal: Investigating global AI regulation: Who is winning, and where to from here?
As we will unpack together, there is a lot of movement around the world, with some collaboration between nations, but the path forward is far from uniform or clear, particularly in business environments where AI adoption is often mandated before holistic safeguarding measures are in place.

Cyber Daily: The industry reacts to OpenAI’s agent ‘accidentally’ hacking Hugging Face
According to one expert, AI guardrails are not designed as “security boundaries” but rather to influence behaviour – but what if that behaviour is hacking one of your industry partners?

SecurityBrief: Autonomous OpenAI agents breach Hugging Face in test
Cyber security experts have warned that the breach of Hugging Face infrastructure during an OpenAI security evaluation marks a turning point in the risks posed by autonomous AI agents. In the incident, AI models moved beyond a controlled test and carried out a live, multi-stage intrusion against the AI platform.

Technology Decisions: AI generated code found to produce predictable weaknesses
AI-generated code introduces an average of 15 confirmed vulnerabilities per codebase, research published by Secure Code Warrior indicates.

Forbes: OpenAI’s Hugging Face Breach Shows Frontier AI Guardrails Are Failing

In AI Today: Secure Code Warrior research reveals AI-generated code introduces an average of 15 vulnerabilities per codebase
Secure Code Warrior research reveals AI-generated code introduces an average of 15 vulnerabilities per codebase.

VMBlog: Secure Code Warrior Research Reveals AI-Generated Code Introduces an Average of 15 Vulnerabilities Per Codebase
Secure Code Warrior introduced the SCW AI Trust Index, a living benchmark for AI coding security that grows with every new model, helping organizations understand and govern the security risks introduced by AI-generated code. Built on a methodology created with RMIT University, Australia, then extended by Secure Code Warrior, the research presents comprehensive benchmarks on how often leading LLMs produce insecure code, with material implications for every enterprise scaling AI-assisted development.

Dark Reading: Choose Wisely: AI-Generated Coding Risk Varies, A Lot
AI-generated code introduces 15 vulnerabilities on average per codebase, but the actual risk depends on framework pairing more than the model used.

Secure Code Warrior Research Reveals AI-Generated Code Introduces an Average of 15 Vulnerabilities Per Codebase
New SCW AI Trust Index shows AI-generated coding risk is not random, it's predictable by model and framework, giving security leaders the data to safely scale AI-assisted development.

ITWire: Eight Industry Executives Comment on Worldwide AI Appreciation Day
The challenges with AI implementation, constant updates, and the race for industry dominance are coming thick and fast, and security professionals are among the most affected by its vast risk profile.

Cyber Daily: The industry speaks – part 3: AI Appreciation Day 2026
The Australian government has said AI is very much in the country’s future national interest – but where does it stand today? Here’s what the industry’s best and brightest have to say about artificial intelligence and its role in the modern enterprise.

ITWire: Agentic AI Era Demands Overhaul of Governance Frameworks
The emergence of agentic AI marks a structural shift in software development, introducing systems that not only accelerate production cycles but also perform autonomous reasoning and action beyond direct human control.

SecurityWeek: How to Conduct a Successful Audit of AI-Driven Software Development
As AI-generated code becomes commonplace, CISOs need new audit strategies to measure developer practices, govern AI tool usage, and identify software risks before they reach production.
SD Times: Platform Engineering & Developer Experience: Making Engineers Faster Without Making Them Reckless: SD Times 100
This category has taken on new urgency in 2026 for a reason that’s specific to this moment: AI coding tools and agents are dramatically increasing how much code gets written and how often it needs to be deployed, tested, and provisioned for. Platform engineering is the layer that determines whether that increased velocity translates into shipped value or into chaos.
SD Times: AI-Assisted Development Multiplies Human Error: What’s Your AI Governance and Risk Management Strategy?
According to a recent report from Gartner, the rampant use of shadow AI and rogue automation is further fueling the proliferation of AI vulnerabilities. Gartner notes that 32% of IT workers using generative AI tools at work say they keep them hidden from cybersecurity teams. Combined with low-code/no-code platforms and vibe coding practices, the AI copilots are greatly expanding the enterprise attack surface.
Cybersecurity Tribe: What Separates Real AI Governance From Policy Theater
For this article, we asked a central question for security and risk leaders: "What differentiates a policy that genuinely mitigates enterprise risk from one that exists primarily to demonstrate that the organization has acknowledged AI risk?"
ISMG: AI Coding Tools Raise Hidden Security Risks
Secure Code Warrior's Pieter Danhieux on Managing AI-Driven Development Risks
ITWire: Decoding AI Coding “Personalities” Critical to Managing Development Risk
As generative AI cements its place in enterprise software development, a familiar discipline is taking on new urgency: risk management.
In AI Today: Secure Code Warrior launches Trust Agent: AI to enable safe, scalable AI-driven development
Secure Code Warrior have today announced SCW Trust Agent: AI, the industry’s first governance solution designed to make Artificial Intelligence (AI) influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk.
DEVOPSdigest: 25 Years of the Agile Manifesto, and the End of the Road for AppSec?
Even as we restructure the SDLC around the most impactful elements of the Agile methodology with careful, DevSecOps-centric security considerations, is this the end of the road for AppSec as we know it?
Cyber Defense Magazine: Global InfoSec Awards 2026 Secure Code Warrior Wins Outstanding Achievement in Cybersecurity Risk Management and Compliance Excellence
Global InfoSec Awards 2026 Secure Code Warrior Wins Outstanding Achievement in Cybersecurity Risk Management and Compliance Excellence
ITWire: Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
New AI Software Governance solution makes AI-generated code visible at commit, enforces policy before production, and connects real development behavior to measurable risk reduction.
DevOps.com: Secure Code Warrior AI Agent Applies Policies to AI Generated Code
Secure Code Warrior (SCW) this week added an artificial intelligence (AI) agent that both identifies code generated by an AI coding tool and automatically applies the appropriate governance policies.

SecurityBrief UK: Secure Code Warrior unveils AI tool to govern code risk
Secure Code Warrior has launched SCW Trust Agent: AI, a software governance product that tracks the use of AI coding tools in development and links that usage to software risk when developers commit code.

2026 Globee® Awards for Cybersecurity: Secure Code Warrior Wins Gold Globee for Software Development Cybersecurity Solutions (Best Of)
2026 Globee® Awards for Cybersecurity: Secure Code Warrior Wins Gold Globee for Software Development Cybersecurity Solutions (Best Of)
DEVOPSdigest: Secure Code Warrior Releases Trust Agent
Secure Code Warrior announced SCW Trust Agent: AI, a governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk.

TalkDev: Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
Secure Code Warrior today announced SCW Trust Agent: AI, the industry’s first governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk. For the first time, organizations can trace which AI models influenced specific commits, correlate that influence to vulnerability exposure, and take corrective action before insecure code reaches production.

Help Net Security: SCW Trust Agent: AI tracks AI influence in code to reduce software risk
Secure Code Warrior has announced SCW Trust Agent: AI, a governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit, enabling enterprises to scale AI coding tools with measurable control over software risk. Organizations can trace which AI models influenced specific commits, correlate that influence with vulnerability exposure, and take corrective action before insecure code reaches production.
Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
New AI Software Governance solution makes AI-generated code visible at commit, enforces policy before production, and connects real development behavior to measurable risk reduction.
Security Boulevard: Threat Modeling with AI: A Developer-Driven Boon for Enterprise Security
Developers have long struggled to truly claim a seat at the table in traditional threat modeling programs, but with the right skills, they have the opportunity to wield AI responsibly to seriously cut risk and rework in their codebase.
The AI Journal: Understanding LLM Coding Personalities Is Now Key to Developer Risk Management
AI-generated code may be “made by machine”, but taking a cookie-cutter approach to securing that code would fall well short of mitigating the vulnerabilities LLMs can introduce. Organizations need to establish precise security reviews, with human developers anchoring the process to implement effective security controls while also managing the specific coding temperament of each LLM used. AI-generated code must undergo the same personalized risk assessments as code written by human developers.

SecurityBrief: The security challenges in AI-assisted software development
s artificial intelligence (AI) tools become more widely used in the software development process, their impact on security is becoming clearer. According to recent research, nearly 70% of organisations have discovered vulnerabilities caused by AI tools while one in five have experienced a serious incident as a result of those vulnerabilities.
KBI Media: Eliminating the Technical Debt Caused by AI-Assisted Software Development
According to research company Forrester[1], the tech debt for 75% of organisations will increase to a moderate or high level during this year, due to the rapid expansion of AI usage across a range of areas including software development.
Forbes: Security Self-Governance: Addressing The Regulatory Gap In AI-Assisted Software Development
While it’s early into 2026, we’re seeing new research that reveals the extent of cyber risks caused by artificial intelligence (AI)-assisted software development: Nearly 7 in 10 organizations have discovered vulnerabilities introduced by AI-generated code, and 1 in 5 have suffered a serious incident tied directly to the vulnerabilities.
ITWire: Why AI Is Dulling Cybersecurity’s Most Important Edge
Artificial intelligence (AI) has rapidly become indispensable to modern software development. From large language models that generate code on demand to agentic systems that automate entire workflows, AI tools promise dramatic gains in productivity and efficiency.

SecurityWeek: How to Eliminate the Technical Debt of Insecure AI-Assisted Software Development
Developers must view AI as a collaborator to be closely monitored, rather than an autonomous entity to be unleashed. Without such a mindset, crippling tech debt is inevitable.

CSO Online: Software developers: Prime cyber targets and a rising risk vector for CISOs
From technical compromise to AI-driven attacks, cyber criminals increasingly see software developers as prime targets, creating systemic risks CISOs must address.

SMBtech: Tech Industry Leaders React To Data Privacy Week 2026
It’s Online Privacy Week, a time of year where individuals and organisations are all reminded to check their digital footprint(s). Some might say that’s a futile gesture at a time where major social media and marketing players know absolutely everything about you and are cheerfully selling all that data to anyone who’ll buy it; when Microsoft is performing every trick in the book to get Windows users to put all their data in the cloud where it’s available for government agencies to snoop upon without letting you know; when a personal computer crisis means many people will be moved on to dumb-client computing landscape where everything from data storage to major processing tasks will be taking place in the cloud; and when people think that clicking ‘Accept’ on website pop-ups does something that meaningfully protects them. But, what do the experts say?
Security brief: AI heightens data privacy risks & reshapes digital trust
Technology and data specialists have warned that artificial intelligence and weak data governance are sharpening privacy risks for organisations, as businesses mark World Data Privacy Day.
ITWire: Data Privacy Week 2026
“Data Privacy Week" presents a great reminder for organisations to reassess their customer privacy policies and prioritise transparent data collection in their marketing strategies.

Dynamic Business: Data Protection Day 2026: Five experts on the privacy risks threatening your business
Five leading cybersecurity experts warn AI is being integrated faster than security policies can manage the risk, creating urgent privacy gaps for SMEs ahead of Data Protection Day on 28 January.
Information Security Buzz: OWASP Top 10 2025: New Enemies, Old Foes, and an Approach to Vulnerability Remediation That Must Evolve
The OWASP Foundation has been a guiding light for security professionals and enthusiasts alike, providing critical, practical advice on the most insidious software vulnerabilities across a plethora of categories and platforms. It has been the first major update since 2021 to the flagship OWASP Top 10 Web Vulnerabilities, and in that time, the industry has been rocked by a stampede of AI technology, tools, and code, each creating a dichotomy of security efficiency and risk for both cybersecurity and software engineering professionals.
DEVOPSdigest: What Software Developers Need to Know About Secure Coding and AI Red Flags
The bottom line: AI tools are not safe for enterprise use unless the code output is reviewed and implemented by a security-proficient human. 30% of security experts admit that they don't trust(link is external) the accuracy of code generated by AI itself. That's why security leaders must prioritize the education and upskilling of developer teams, to ensure they have the necessary skills and capabilities to mitigate AI-assisted code vulnerabilities as early as possible. This will lead to the cultivation of a "security first" team culture and safer AI use.
Stack Overflow: If you're a Zoomer, this one's for you: Everything Gen Z needs to know about the 2025 tech landscape
Here's the lowdown on all the tech from 2025 that you, dear Zoomer, should know about.

SC Media: CISOs can’t wait for the EU AI Act to take shape
CISOs hoping for the EU Artificial Intelligence Act to offer a solid framework for AI governance may be a little confused or disappointed by recent updates surrounding the implementation of AI restrictions.
SecurityBrief: Agentic AI double agents expose dangerous security gaps
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the more than thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention.
DEVOPSdigest: 2026 DevSecOps Predictions
DEVOPSdigest's Prediction Series continues with 2026 DevSecOps Predictions — Industry experts offer predictions on how DevSecOps will evolve and impact the industry in 2026.
ITWire: OWASP Names Latest Top 10 Application Vulnerabilities
The Open Worldwide Application Security Project (OWASP) has unveiled its latest top 10 vulnerabilities list, and it contains some surprising insights into important vulnerability classes.

Channel Insider: Cybersecurity Experts Predict AI, Nation-State Threats in 2026
Cybersecurity experts outline 2026 predictions, from AI-driven attacks and quantum risk to nation-state threats, OT security gaps, and automation pressures.

Security Journal UK: The rise of AI coding tools and the skills gap they expose
Pieter Danhieux, Co-founder and CEO of Secure Code Warrior warns that while AI coding tools promise speed and efficiency, they also introduce new risks.
ITWire: Predictions on State of AI in 2026
2026 is shaping up to be the year AI evolves from instrument to partner, transforming how we work, create and solve problems.

Fortune: AI coding tools exploded in 2025. The first security exploits show what could go wrong
While a breach of the tools hasn’t so far caused a wide-scale attack, there have been a few exploits and near-misses, and cyberthreat researchers have discovered critical vulnerabilities in several popular tools that make clear what could go horribly wrong.
SMBtech: Australian Tech Industry Leaders Make Their Predictions for 2026
It’s that time of year where the technology industry predictions start rolling-in. Here’s what you can (apparently) expect in 2026.

Technology Decisions: The importance of effective security when deploying AI tools
The concern is straightforward: development teams may place undue confidence in AI tools that are not equipped to interpret the nuanced context in which many security vulnerabilities arise. Large language models, for instance, can struggle to understand an application’s authentication or authorisation architecture, increasing the likelihood of missing critical safeguards.
ITWire: Five Steps to Improve the Security of AI Developed Code
Industry guidance on managing the risks of AI-generated code increasingly points to the same conclusion: effective safeguards rely on close collaboration between humans and machines, with developers remaining firmly in the loop.

SecurityBrief Australia: Agentic AI to transform APJ businesses & security by 2026
Agentic artificial intelligence (AI) is set to reshape the enterprise landscape in the Asia-Pacific and Japan (APJ) region in 2026, according to industry executives. Organisations are expected to embrace increasingly autonomous software agents, raising both productivity and new categories of risk across business domains.
SC Magazine UK: Why Firms Can’t Ignore Agentic AI
How big a threat does agentic AI pose to businesses currently? And what should security leaders be doing to address the risk?

VMBlog: Cybersecurity Predictions: What AI will (and won't) do for us in 2026
My co-founder and CTO, Matias Madou, Ph.D., and I consulted our crystal ball (or should that be our NVIDIA GPUs?), and this is what we believe 2026 has in store for us from an AI security perspective.
SD Times: Pumping the Brakes on Agentic AI Adoption in Software Development
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem, namely Model Context Protocol (MCP) systems, to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the over thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention. Maybe it’s time we went a little slower, stopped to reflect on what is at stake here, and how best to defend ourselves.

AIthority: Building Secure and Ethical AI Practices in Software Development
AI is now a key piece of modern software development. More than four out of five developers use AI coding tools daily or weekly – with many relying on multiple tools in parallel. Teams must understand where automation ends, and where accountability begins.
SC Media: Secure Coding as Critical Thinking Instead of Vulnspotting – Matias Madou – ASW #357
Secure code should be grounded more in concepts like secure by default and secure by design than by “spot the vuln” thinking. Matias Madou shares his experience in secure coding training and the importance of teaching critical thinking. He also discusses why critical thinking is so closely related to threat modeling and how LLMs can be a tool for helping developers get beyond the superficial advice of, “Think like an attacker.”

Forbes: How CISOs Can Increase Their Influence In AI-Obsessed Boardrooms
Organizations are at an inflection point driven by the explosive adoption of AI, which promises significant changes in how businesses operate. That leaves CISOs on unsteady ground. As the gatekeepers of their organization’s data and access, they must ensure the security of the enterprise. However, the prospects of a headlong charge into wide-ranging, and possibly unchecked, use of AI could create a flood of security issues that many CISOs, under their current organizational structures, aren’t equipped to handle.
Security Boulevard: Security Degradation in AI-Generated Code: A Threat Vector CISOs Can’t Ignore
Security leaders and developers alike are already acutely aware that AI coding assistants and agentic agents can introduce vulnerabilities into the code they generate. A recent study unveiled another critical concern to keep them up at night — LLMs used for making iterative code improvements may introduce new vulnerabilities over time, even when explicitly asked to make code more secure.

Information Week: Make your own mandate: How CISOs can implement GenAI governance
Government bodies are trying to develop rules and regulations for safe AI use, but enterprises can't afford to wait. They need to address the risks now.

CFOtech Australia: How women can continue to foster fulfilling high-tech careers in the AI age
In the sphere of cybersecurity in general and application security in particular, human oversight remains an absolute 'must' to harness the benefits of AI productivity.

Tanium: Vibe coding may be unstoppable—but here’s how to rein in the risks
Like the meteoric rise of ChatGPT, vibe coding is all anybody can talk about this year. In fact, it just became a word in the dictionary. But beware the boom: These new AI coding tools offer speed, savings—and astounding vulnerabilities.
[PODCAST] Stack Overflow: AI code means more critical thinking, not less
Ryan is joined by Secure Code Warrior’s co-founder and CTO Matias Madou to discuss the implications of LLMs’ variability on code security, the future of developer training as AI coding assistants become more popular, and the importance of critical thinking—especially for junior developers—in the age of AI.

Cybersecurity Insiders: Use It or Lose It: Overreliance on AI Diminishes Critical Cybersecurity Thinking Skills
Software developers reap a host of benefits from making use of artificial intelligence assistants, whether in the form of Large Language Model (LLM) code creators or agentic AI agents. But recent reports, highlighted by a new study at MIT, warn that heavy use of AI can result in a loss of critical thinking skills among users.
Security Week: How Software Development Teams Can Securely and Ethically Deploy AI Tools
To deploy AI tools securely and ethically, teams must balance innovation with accountability—establishing strong governance, upskilling developers, and enforcing rigorous code reviews.

Dark Reading: AI Developed Code: 5 Critical Security Checkpoints for Human Oversight
To write secure code with LLMs developers must have the skills to use AI as a collaborative assistant rather than an autonomous tool, Madou argues.

Techstrong.tv: Secure Code Warrior in the Age of AI with Pieter Danhieux
Secure Code Warrior’s Chief Executive Officer, Chairman, and Co-Founder Pieter Danhieux explains his transition from offensive cybersecurity to promoting secure software development. Founded in 2015, Secure Code Warrior aims to help developers build secure code from the start, a practice Danhieux and host Alan Shimel agree is more effective than fixing vulnerabilities later. The two also discuss the impact of AI on software development, noting that while AI increases coding speed and accessibility for more people, the security of AI-generated code still lags. They emphasize the growing need for developers to master secure coding practices amidst these technological advancements.
SMBtech: Cybersecurity Awareness Month 2025: Australian Industry Reactions and Commentary
October is Australia’s Cybersecurity Awareness Month, the annual reminder for Aussies to stay vigilant online. This year’s theme, ‘Building our cyber safe culture’ once again highlights the importance of taking personal responsibility for staying secure in an increasingly digital world.
SecurityBrief: SMEs urged to cut data & boost cyber defences as attacks rise
Cybersecurity Awareness Month has brought renewed attention to the increasing risks faced by organisations of all sizes, with a particular focus on the growing threat to small and medium-sized enterprises (SMEs) in Australia and the UK.

ITBrief: Our biggest security risk isn’t our software - it’s our thinking
In the world of cybersecurity, we face creative and unconventional threats every day. But our greatest vulnerability isn't a flaw in our software, but a flaw in our collective thinking.
KBI Media: Overcoming the Security Risks of Using AI In Software Development
Development teams face relentless pressure to deliver, yet they must continue to prioritise building secure, high-quality software. Leaders play a crucial role in reinforcing how a Secure by Design approach, supported by observability, benchmarking, and ongoing education, directly enhances code quality. By embedding these practices, organisations can close governance gaps and fully capture the benefits of AI-driven productivity and efficiency, while reducing the risk of security flaws or costly rework during the SDLC.
In AI Today: The looming security challenges posed by Agentic AI
While agentic AI holds the promise of delivering significant business benefits, it also comes with significant caveats. The technology’s capabilities and autonomy present a potent enterprise threat vector beyond the realm of existing security concerns.
Help Net Security: Secure Code Warrior gives CISOs visibility into developer AI tool usage
Secure Code Warrior has launched a beta program to expand the AI capabilities of its Trust Agent product. The new offering provides CISOs with security traceability, visibility, and governance over developers’ use of AI coding tools.

Cyber Risk Leaders: Secure Code Warrior Launches AI Traceability
Secure Code Warrior have released a beta program for a major expansion of AI capabilities within its Trust Agent product. The upgrade, collectively referred to as Trust Agent: AI, leverages a combination of key signals, including AI coding tool usage, vulnerability data, code commit data and developer secure coding skills, to provide visibility into how AI development tools are impacting risk within the software development lifecycle (SDLC).
CSO Online: AI coding assistants amplify deeper cybersecurity risks
Although capable of reducing trivial mistakes, AI coding copilots leave enterprises at risk of increased insecure coding patterns, exposed secrets, and cloud misconfigurations, research reveals.

Secure Code Warrior Launches Industry-First AI Traceability to Enable Secure Developers and Supercharge Safe Productivity
New capabilities in SCW Trust Agent provide visibility and control over LLM usage for security leaders and CISOs.

ITOps Times: Secure Code Warrior announces new solution that provides visibility and governance for AI coding tools
Secure Code Warrior is trying to provide organizations with greater visibility and control over developers’ use of AI coding tools with the launch of its new solution, Trust Agent: AI.
DevOps Digest: Secure Code Warrior Introduces AI Traceability
Secure Code Warrior announced the launch of a beta program for a major expansion of AI capabilities within its Trust Agent product.

CyberWire: Business Briefing for 09.24.25
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

Betanews: AI is an even playing field -- how secure by design can tip the scale [Q&A]
Vibe coding is currently all the rage, with more than 97 percent of respondents to a survey earlier this year reporting having used AI coding tools at work. The adoption of these tools only continues to grow but it comes with a catch, attackers are also employing the same techniques. We spoke to Pieter Danhieux, co-founder and CEO of Secure Code Warrior, to discuss how vibe coding is redefining the software development landscape, how malicious actors are also leveraging this technology and the need for organizations to implement secure by design strategies from the outset.