


Insights from experts shaping secure development
Access expert content on secure coding, AI governance, and software risk management.

사이버 회복력 법안(Cyber Resilience Act) 대비에 SBOM이 중요한 이유
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
대형 의료 제공업체가 개발자 중심 접근 방식으로 보안 문화를 혁신한 방법
Contrast Security의 공동 설립자 Jeff Williams와 Secure Code Warrior의 Matias Madou가 안내하는 의료 기관의 보안 문화 혁신 사례를 들어보세요.
임베디드 시스템과 팀 역량 강화
사물 인터넷, 생산 시스템의 자동 제어 및 관리는 임베디드 시스템 개발을 촉진하는 몇 가지 요소에 불과합니다. 임베디드 소프트웨어의 보안 취약점이 미치는 영향과 이를 완화하는 방법은 무엇일까요?
컴플라이언스를 넘어: 흥미진진한 애플리케이션 보안을 제공하는 팁
개발 팀이 애플리케이션 보안 교육을 단순한 체크박스 채우기로 취급하나요? 개발자가 스스로 찾아오는 교육 프로그램을 만드는 실용적인 팁을 확인하세요!
훌륭한 SOC 2 보고서 달성을 위한 모범 사례
SOC 보고서 프로젝트에 직면하면 때로는 매우 막막하게 느껴질 수 있습니다. 업계 전문가들과 함께 SOC 2 보고서 획득을 위한 핵심 팁을 나눕니다.

2021 HMG Live! 실리콘밸리 CISO 최고경영자 서밋
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
웨비나: DevOps에서 DevSecOps로: 처음부터 품질과 보안이 확보된 개발 제공
전문가들이 SDLC에 보안 교육 및 애플리케이션 보안을 구현하기 위한 핵심 고려 사항, 게이미피케이션 학습을 통해 개발자를 참여시키는 방법, 다운타임이나 비용 부담 없이 보안 테스트를 통합하는 방법을 설명합니다.
코스 내 튜토리얼(Walkthroughs) 심층 탐구
새로운 Walkthrough & Missions 몰입형 실습 교육 활동이 개발자의 참여를 유도하고 입증된 단계별 학습 방식으로 개발자 역량을 단계적으로 향상시키는 방법을 알아보세요.
업스킬링, AppSec 보안 격차를 줄이기 위한 마지막 열쇠
Zip의 보안 총괄 Peter Robinson과 Secure Code Warrior의 공동 설립자이자 AppSec 트레이너인 Jaap Singh으로부터 보안 격차를 줄이기 위해 임직원의 사이버 보안 기술 향상이 필수적인 이유에 대한 심도 있는 논의를 들어보세요.
개발자 주도 보안의 ROI
테크 스택이나 추가 교육 프로그램에 투자할 때 누구나 투자 대비 좋은 수익률(ROI)을 원하지만, 보안에 있어서는 단순한 ROI 계산을 넘어 장기적인 안목으로 접근해야 합니다. 개발자 주도 보안 투자가 비싼 보안 침해 비용과 생산성 손실을 줄이는 방법과 비용 효율적인 전략을 배우세요.
시큐리티 챔피언으로 가는 길
Workday가 개발자 역량 강화를 위해 애자일 보안 학습을 활용한 방법입니다.

조력자 8: 프로그램 브랜딩
성공적인 보안 코딩 프로그램을 위해서는 훌륭한 콘텐츠 그 이상의 것이 필요합니다. 인에이블러 8은 브랜딩을 통해 어떻게 참여를 선망의 대상이자 위상을 높이는 경험으로 바꿀 수 있는지 보여줍니다.
이제 모든 직원이 AI 사이버 보안의 최전선에 있습니다
엔터프라이즈 기술 환경은 뒤늦게 깨달았을 때는 이미 늦었을 만큼 빠른 속도로 변화하고 있습니다. 우리는 이제 사람이 직접 작성한 코드와 기본적인 코파일럿 지원의 시대를 넘어, 에이전트 기반 개발 수명 주기(ADLC)의 시대로 공식적으로 진입했습니다. 자율형 AI 에이전트는 다양한 기능 전반에 걸쳐 전례 없는 효율성을 약속하지만, 동시에 완전히 새로운 차원의 보안 및 규제 위험을 야기합니다.
7번째 지원 요소: 개발자 인정
인정은 참여의 원동력입니다. Enabler 7은 개발자의 성취를 널리 알리고, 실질적인 보안 코딩 성과를 거둔 개발자에게 보상과 특별한 굿즈를 제공하여 이를 기념합니다.

Gartner® Hype Cycle™ for Application Security 2026 선정
Secure Code Warrior가 Gartner® Hype Cycle™ for Application Security 2026의 Agentic Coding Security 및 Secure Coding Training 부문에 선정되었습니다. 그 이유를 소개합니다.

LLM 코드 생성의 보안과 비용 문제로 고민 중인 CISO 또는 엔지니어링 리더이신가요?
AI 모델을 전면 도입하기 전에 당사의 독자적인 LLM 벤치마킹 데이터인 SCW AI Trust Index를 검토해 보십시오.

Enabler 6: 경영진 대상 정기 보고
경영진의 지원은 저절로 유지되지 않습니다. 성공 요인 6에서는 정기적인 보고를 통해 경영진이 프로그램의 성공에 지속적으로 관심을 갖고 참여하며 투자하도록 만드는 방법을 다룹니다.

AI 소프트웨어 거버넌스의 미래는 강력한 파트너십 위에 세워집니다
Secure Code Warrior가 왜 채널 우선 기업으로 전환하고 있는지, 그리고 신뢰할 수 있는 파트너가 어떻게 조직의 AI 소프트웨어 거버넌스 도입을 안전하고 확장성 있게 지원하는지 확인해 보세요.

Secure Code Warrior의 Citizen AI: AI 준비 인력 구축하기
비개발직군 임직원을 위한 Secure Code Warrior의 AI 리터러시 프로그램입니다.

대다수의 CISO가 눈을 가린 채 AI를 도입하는 이유 (그리고 이를 해결하는 방법)
오늘 Secure Code Warrior는 보안 리더들이 조직의 AI 도입 단계를 파악하고 AI 보안 위험을 실질적으로 통제할 수 있도록 돕는 지침 중심의 새로운 AI 도입 모델 백서를 발표했습니다.
조력자 5: 인증 프로그램
일회성 교육에서 벗어나세요. Enabler 5는 개발자에게 의미 있는 성장 경로와 검증된 역량을 제공하는 다단계 인증 프로그램을 구축합니다.
NSA가 첫 MCP 보안 가이드라인을 발표했습니다. 이것이 개발자 역량에 어떤 의미를 갖는지 알아봅니다.
NSA가 최초의 MCP 보안 지침을 발표했습니다. SCW 커리큘럼은 이미 제기된 23가지 문제 중 18가지를 다루고 있으며, 그 대응 현황은 다음과 같습니다.

Gartner® Hype Cycle™ for Secure Software Engineering 2026 선정
가트너가 SCW를 두 부문에서 선정했습니다. AI 에이전트가 개발 영역을 점차 확대함에 따라, SCW는 귀사가 AI 기반 개발을 안전하게 도입할 수 있는 역량과 거버넌스를 제공합니다.

적응형 학습(Adaptive Learning) 발표: AI 소프트웨어 보안 위험과 기술 격차를 해소하는 해결책
Adaptive Learning은 SCW Trust Agent와 당사의 전체 학습 플랫폼을 연결하여, 실시간 개발자 활동에 완벽하게 맞춘 교육을 제공합니다.
실제 AI 사용 환경을 반영한 보안 코딩 학습
보안 코딩 교육을 실제 AI 개발 활동에 맞추세요. 수동 개입 없이 AI 도구를 사용하는 개발자에게 자동으로 가이드를 할당할 수 있습니다.보안 코딩 교육을 실제 AI 개발 활동에 맞추세요. 수동 개입 없이 AI 도구를 사용하는 개발자에게 자동으로 가이드를 할당할 수 있습니다.
사람이 작성했든 AI가 생성했든, 개발자에게 코드 내 실제 위험을 교육하세요
적응형 학습은 실제 취약점을 유발하는 개발자에게 맞춤형 보안 코딩 교육을 자동으로 할당하여 근본적인 반복 위험을 줄여줍니다. Secure Code Warrior 블로그 배너: 다중 모니터 데스크에서 코드를 작업하는 개발자 위에 파란색 오버레이가 씌워져 있으며, '개발자에게 코드 내 실제 위험에 대한 교육을 제공하세요'라는 헤드라인이 함께 표시됩니다.
조력자 4: 낮은 사용자 접근 장벽
Enabler 4: 낮은 사용자 접근 장벽을 통해 보안 코딩 프로그램의 마찰을 제거하세요. SSO, 사전 온보딩, 릴레이 상태 전략을 활용하여 개발자가 클릭 한 번으로 교육을 시작할 수 있도록 지원합니다.

를 방문해 주십시오. 생성형 AI 시대를 위한 개발자 역량 강화: AWS 협력
Secure Code Warrior가 Amazon Web Services(AWS)와 전략적 협력 계약을 체결했음을 발표하게 되어 매우 자랑스럽습니다. 급변하는 위협 환경을 고려할 때, 이번 전략적 협력은 보안 리더와 미래 지향적인 개발자 모두에게 그 어느 때보다 중요한 시점에 이루어졌습니다.
소프트웨어의 미래를 보호하다: SCW와 KnowBe4의 결합
Secure Code Warrior와 KnowBe4의 전략적 파트너십을 발표하게 되어 매우 기쁩니다. KnowBe4는 인간 및 에이전트 AI 리스크 관리 분야의 세계적인 선도 기업으로, 전 세계 조직에 필수적인 보안 인식 교육을 제공하는 데 있어 최적의 파트너입니다.

포스트 양자 암호: 양자 컴퓨터가 오늘날의 암호화를 무너뜨립니다 – 준비되셨나요?
양자 내성 암호(PQC)는 양자 컴퓨팅의 위협으로부터 데이터를 보호하는 데 필수적입니다. '지금 수집하고 나중에 해독하는(harvest now, decrypt later)' 방식이 어떻게 위험을 초래하는지, 그리고 개발자가 양자 보안을 어떻게 준비해야 하는지 알아보세요.

활성화 요소 3: 개발자 커뮤니케이션 계획
탄탄한 커뮤니케이션 계획으로 개발자가 보안 코딩 프로그램에 지속적으로 참여하도록 유도하세요. 이점 강조하기, 적절한 어조 설정하기, 성과 축하하기 방법을 배워보세요.
에이전트 시대가 일찍 찾아왔습니다: 방심하지 마십시오
Anthropic의 Claude Mythos는 모든 보안 리더가 보안 프로그램을 접근하는 방식, 특히 레거시 시스템의 패치 관리 방식에 있어 영구적이고 근본적인 변화를 예고합니다.

Enabler 2: Senior Leadership Sponsorship
Explore Enabler 2: Senior Leadership Sponsorship. Learn why active buy-in from the CIO, CTO, and CISO is vital to drive developer adoption and program credibility.
Observe and Secure the ADLC: A Four-Point Framework for CISOs and Development Teams Using AI
While development teams look to make the most of GenAI’s undeniable benefits, we’d like to propose a four-point foundational framework that will allow security leaders to deploy AI coding tools and agents with a higher, more relevant standard of security best practices. It details exactly what enterprises can do to ensure safe, secure code development right now, and as agentic AI becomes an even bigger factor in the future.
사이버몬이 돌아왔다: 보스 격파 AI 미션이 이제 온디맨드로 제공됩니다
사이버몬 2025 비트 더 보스는 이제 SCW에서 연중 내내 이용할 수 있습니다.고급 AI/LLM 보안 과제를 배포하여 대규모 보안 AI 개발을 강화하세요.
AI Can Write and Review Code — But Humans Still Own the Risk
Anthropic’s launch of Claude Code Security marks a defining collision point between AI-assisted software development, and the rapid augmentation of how we approach modern cybersecurity.
사이버 레질리언스 법 설명: 보안 설계 소프트웨어 개발의 의미
EU 사이버복원법 (CRA) 에서 요구하는 사항, 적용 대상, 엔지니어링 팀이 설계, 관행, 취약성 방지 및 개발자 환경 구축을 통해 어떻게 안전하게 대비할 수 있는지 알아보세요.

성공 요인 1: 정의되고 측정 가능한 성공 기준
Enabler 1은 장기 프로그램 성숙도를 위한 위험 및 비용 감소 속도 향상과 같은 비즈니스 성과에 보안 코딩을 통한 방법을 보여줌으로써 10부로 구성된 성공의 인에이블러 시리즈를 제공합니다.
SCW Turns 11: A Realtime Lesson in Adaptability and Continuous Improvement
2025 was a big year for AI, for cybersecurity, and for SCW. I’m approaching 2026 with quiet confidence, and the optimism that only hard work paying off can bring.

Introducing the 10 Enablers of Success
Secure Code Warrior’s 10 Enablers guide organizations in building lasting secure coding programs by focusing on people, process, and program maturity stages.
OWASP 2025년 상위 10위: 소프트웨어 공급망 실패
OWASP 상위 10위 2025에서는 소프트웨어 공급망 장애가 #3 순위로 선정되었습니다.엄격한 SBOM, 종속성 추적, CI/CD 파이프라인 강화를 통해 이러한 영향력이 큰 위험을 완화할 수 있습니다.

New Risk Category on the OWASP Top Ten: Expecting the Unexpected
OWASP Top 10 2025 adds Mishandling of Exceptional Conditions at #10. Mitigate risks via "fail closed" logic, global error handlers, and strict input validation.
OWASP Top 10:2025 — 새로운 기능 및 보안 코드 워리어가 일관성을 유지하는 데 도움이 되는 방법
OWASP Top 10:2025에서 변경된 사항과 업데이트된 퀘스트, 코스, 개발자 인사이트를 통해 Secure Code Warrior를 통해 어떻게 쉽게 전환할 수 있는지 알아보세요.
Adopt Agentic AI in Software Development FAST! (Spoiler: You Probably Shouldn't.)
Is the cybersecurity world moving too fast on agentic AI? The future of AI security is here, and it's time for experts to move from reflection to reality.

Solving the Visibility Crisis: How Trust Agent Bridges the Gap Between Learning and Code
Trust Agent by Secure Code Warrior solves the secure coding crisis, validating dev proficiency on every commit. It discovers all contributors & automates governance in your dev workflow.

AI 증강 보안 소프트웨어 개발에서의 비판적 사고 재확보
AI 논쟁은 사용이 아니라 응용에 관한 것입니다.코드를 깊이 이해하는 개발자에게 의존하여 AI 생산성 향상에 대한 요구와 강력한 보안 사이에서 균형을 유지하는 방법을 알아보세요.
AI Coding Assistants: With Maximum Productivity Comes Amplified Risks
In our latest whitepaper, our co-founders Pieter Danhieux and Dr. Matias Madou, Ph.D., explore the double-edged sword that is AI Coding Assistants and how they can be a welcome addition and a significant security liability at the same time.

사이버 보안 위험 평가: 정의 및 단계
효과적인 사이버 보안 위험 평가를 수행하기 위한 이 실행 가능한 가이드를 통해 조직의 사이버 보안 위험을 해결하세요.

Why Cybersecurity Awareness Month Must Evolve in the Age of AI
CISOs can’t rely on the same old awareness playbook. In the Age of AI, they must embrace modern approaches to safeguard code, teams, and organizations.

SCW Trust Agent: AI - Visibility and Governance for Your AI-Assisted SDLC
Learn how Trust Agent: AI provides deep visibility and governance over AI-generated code, empowering organizations to innovate faster and more securely.

AI 시대의 시큐어 코딩: 새로운 인터랙티브 AI 챌린지에 도전해 보세요
AI 지원 코딩은 개발을 변화시키고 있습니다.새로운 CoPilot 스타일 AI 챌린지를 사용해 실제 워크플로우에서 코드를 안전하게 검토, 분석 및 수정하세요.

SCW, 개발자를 위한 무료 AI/LLM 보안 비디오 시리즈 출시
12주 무료 AI/LLM 보안 비디오 시리즈를 소개합니다!AI 지원 코딩의 기본 위험과 더 안전한 애플리케이션을 구축하는 방법을 알아보십시오.
AI/LLM Security Video Series: All Episodes, Updated Weekly
Your all-in-one guide to our 12-week AI/LLM security video series. Catch every episode, learn key AI security concepts, and follow along weekly.

시큐어 코딩이란?기법, 표준 및 리소스
보안 코딩의 진정한 의미와 보안 코딩 방식을 통해 회사의 취약성과 보안 관련 비용을 모두 줄일 수 있는 방법을 알아보십시오.

10,000개 이상의 보안 코드 학습 활동: 10년간의 개발자 위험 관리
10,000개 이상의 보안 코드 학습 활동을 기념하고 개발자들이 위험을 줄이고 코드 품질을 개선하며 AI 지원 개발에 자신 있게 도전할 수 있도록 역량을 강화한 10년을 기념합니다.
좋은 도구가 나빠질 때: AI 도구 중독 및 AI가 이중 에이전트 역할을 하는 것을 막는 방법
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
표준 설정: SCW, GitHub에서 무료 AI 코딩 보안 규칙 출시
AI 지원 개발은 더 이상 가능하지 않습니다. 이제 AI 지원 개발이 현실로 다가왔고, 이로 인해 소프트웨어 작성 방식이 빠르게 바뀌고 있습니다.GitHub Copilot, Cline, Roo, Cursor, Aider, Windsurf와 같은 도구는 개발자를 자체 공동 파일럿으로 탈바꿈시켜 프로토타입 제작부터 주요 리팩토링 프로젝트까지 모든 것을 가속화하고 반복 작업을 가속화합니다.
Secure Code Warrior Unraveled: Impact of Secure Developers on Software Metrics
When reflecting on our own technology, SCW’s Developer Risk Management platform, I am buoyed by recent metrics from one of our core enterprise clients, and going down the proverbial rabbit hole into this data tells a tale of a high-adoption, potent Secure by Design initiative that has been proven to considerably reduce risk in their organization.

시큐어 코드 워리어+HackerOne으로 취약성 문제를 해결하세요
Secure Code Warrior는 공격 보안 솔루션의 선두 주자인 HackerOne과의 새로운 통합을 발표하게 되어 기쁩니다.우리는 함께 강력한 통합 에코시스템을 구축하고 있습니다.HackerOne은 실제 환경에서 취약점이 실제로 발생하는 위치를 정확히 찾아내어 보안 문제의 “무엇”과 “장소”를 폭로합니다.

공개: 사이버 산업이 보안을 정의하는 방법
공동 창립자인 Pieter Danhieux 박사와 Matias Madou 박사 (Dr. Matias Madou) 박사는 CISO, AppSec 리더 및 보안 전문가를 포함한 20명 이상의 엔터프라이즈 보안 리더와 함께 이 퍼즐의 핵심 요소를 파악하고 Secure by Design 운동의 이면에 숨겨진 현실을 알아내는 최신 백서입니다.보안 팀 전체가 같은 포부를 갖고 있지만 플레이북은 공유되지 않았습니다.

바이브 코딩이 여러분의 코드베이스를 프래트 파티로 탈바꿈시킬 수 있을까요?
바이브 코딩은 대학 동아리 파티와 같으며 AI는 모든 축제의 중심이자 핵심입니다.긴장을 풀고 창의력을 발휘하며 상상의 나래를 어디까지 데려갈 수 있는지 알아보는 것은 정말 즐거운 일이지만, 술통 가판대를 몇 번 마신 후에는 적당히 술을 마시거나 AI를 사용하는 것이 더 안전한 장기적 해결책이라는 것은 의심할 여지 없이 더 안전한 장기적 해결책입니다.

에이전트 코딩 도구의 신속한 주입과 보안 위험
코딩 에이전트가 속아 SQL 주입이 발생하기 쉬운 코드를 작성하고, 셸 도구를 설치하고, 심지어 사용자를 스토킹하게 한 방법

퀘스트 소개: 보안 코드 여정에 새로 추가된 퀘스트
퀘스트는 개발자가 대화형 학습을 통해 보안 코딩을 마스터하고 위험을 줄이고 개발을 최적화할 수 있도록 합니다.
디케이드 오브 더 디펜더스: 10주년을 맞이한 시큐어 코드 워리어
Secure Code Warrior의 창립 팀은 10년 동안 모든 교훈, 승리, 좌절을 극복하면서 함께 해왔습니다.우리는 규모를 확장하고 있으며 개발자 위험 관리 분야의 리더로서 다음 챕터인 SCW 2.0을 맞이할 준비가 되어 있습니다.
10가지 주요 예측: 2025년 AI에 대한 보안 코드 워리어와 시큐어 바이 설계의 영향
조직은 장기적인 생산성, 지속 가능성 및 보안 ROI를 지원하기 위해 AI 사용에 대한 어려운 결정을 내려야 합니다.지난 몇 년 동안 AI가 개발자의 역할을 완전히 대체할 수는 없다는 것이 분명해졌습니다.AI+ 개발자 파트너십부터 Secure-by-Design에 대한 기대치가 높아지는 압박 (및 혼란) 에 이르기까지, 내년에 우리가 기대할 수 있는 사항에 대해 자세히 살펴보겠습니다.
LLM 애플리케이션을 위한 OWASP 상위 10위: 새로운 기능, 변경된 기능 및 보안을 유지하는 방법
최신 OWASP Top 10 업데이트를 통해 LLM 애플리케이션의 보안을 한 발 앞서 나가십시오.새로운 기능, 변경된 사항, Secure Code Warrior가 제너레이티브 AI의 위험을 완화하는 데 필요한 최신 학습 리소스를 어떻게 제공하는지 알아보십시오.

신뢰 점수는 Secure By-Design-Upskilling 이니셔티브의 가치를 보여줍니다
우리의 연구에 따르면 보안 코드 교육이 효과가 있는 것으로 나타났습니다.Trust Score는 600개 이상의 조직에서 250,000명 이상의 학습자가 작업에서 얻은 2천만 개 이상의 학습 데이터 포인트를 기반으로 하는 알고리즘을 사용한 결과 취약점을 제거하는 데 효과가 있고 이니셔티브를 더욱 효과적으로 만드는 방법을 보여줍니다.

Reactive Versus Preventive Security: Prevention Is a Better Cure
The idea of bringing preventive security to legacy code and systems at the same time as newer applications can seem daunting, but a Secure-by-Design approach, enforced by upskilling developers, can apply security best practices to those systems. It’s the best chance many organizations have of improving their security postures.

보안 기술 벤치마킹이 개발자를 위한 이점
보안 코드 및 Secure by Design 원칙에 대한 관심이 높아짐에 따라 개발자는 SDLC 시작 단계부터 사이버 보안에 대한 교육을 받아야 하며, Secure Code Warrior의 신뢰 점수와 같은 도구를 사용하여 진행 상황을 측정하고 개선해야 합니다.

You’ve got a friend in me: How AI coding tools and security-aware developers can work together safely
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
엔터프라이즈 보안 설계 이니셔티브를 위한 의미 있는 성공 주도
당사의 최신 연구 논문인 보안 기술 벤치마킹: 기업의 보안 설계 간소화는 기업 수준의 실제 보안 설계 이니셔티브를 심층적으로 분석하고 데이터 기반 결과를 기반으로 모범 사례 접근 방식을 도출한 결과입니다.
심층 분석: GNU-Linux 시스템의 심각한 CUPS 취약성 탐색
일반 UNIX 인쇄 시스템 (CUPS) 의 최근 심각도가 높은 취약성을 살펴보면서 Linux 사용자가 직면하고 있는 최신 보안 문제를 알아보십시오.이러한 문제가 어떻게 잠재적 RCE (원격 코드 실행) 로 이어질 수 있는지, 그리고 시스템을 보호하기 위해 무엇을 할 수 있는지 알아보십시오.
How exceptional CISOs are igniting the security fire in their development team
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
코더들이 보안을 정복하다: 공유 및 학습 - 크로스 사이트 스크립팅 (XSS)
크로스 사이트 스크립팅 (XSS) 은 브라우저의 신뢰와 사용자의 무지를 이용하여 데이터를 도용하고 계정을 탈취하며 웹 사이트를 훼손합니다. 이는 매우 심각하고 순식간에 악화될 수 있는 취약점입니다.XSS의 작동 원리, 발생할 수 있는 피해, 예방 방법을 살펴보겠습니다.

새로운 인게이지먼트 인사이트 보고서 소개
보안 코드 학습 노력을 측정하는 데 도움이 되는 심층 분석을 제공하는 새로운 참여 인사이트 보고서에 대해 알아보십시오.
How the best CISOs leverage people and technology to become true superstars
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

DigitalOcean이 소프트웨어 보안 부채를 줄이고 생산성의 한계를 넓힌 방법
Secure Code Warrior는 DigitalOcean이 처음부터 고품질 코드를 구축 및 릴리스하도록 지원하여 보안을 인식하는 개발자와 함께 디지털 혁신과 현대화를 주도했습니다.

Women in Security are Winning: How the AWSN is Setting Up a New Generation of Security Superwomen
Secure-by-Design is the latest initiative on everyone’s lips, and the Australian government, collaborating with CISA at the highest levels of global governance, is guiding a higher standard of software quality and security from vendors.

SCW Trust Agent - 개발자 기반 보안 확장을 위한 가시성 및 제어
Secure Code Warrior에서 도입한 SCW 트러스트 에이전트는 보안 리더에게 조직 내에서 개발자 기반 보안을 확장하는 데 필요한 가시성과 제어 기능을 제공합니다.코드 리포지토리에 연결하여 코드 커밋 메타데이터를 평가하고, 개발자, 사용된 프로그래밍 언어, 배송 타임스탬프를 검사하여 개발자의 보안 지식을 파악합니다.

귀사의 보안 프로그램은 CISA의 사이버 보안 전략 계획을 지원할 준비가 되어 있습니까?
사이버 보안 전략 계획은 대부분의 조직이 사이버 보안에 접근하는 방식을 대대적으로 변화시키고 있으며, 개발자는 이러한 새로운 목표를 달성하는 데 도움을 줄 수 있는 독보적인 위치에 있습니다.
Don’t ignore what developers need for a successful software security journey
It's becoming apparent that while cybersecurity platforms and defenses are critical components in defense against modern attacks, what is truly needed is secure code that can be deployed free from vulnerabilities. And that requires security-aware developers with verified security skills.
참여 및 권한 부여: 개발자 참여를 위한 주요 기능 강조
애자일 학습 방법, Microsoft 팀 통합, 개발 참여 보고서에 대해 자세히 알아보세요.
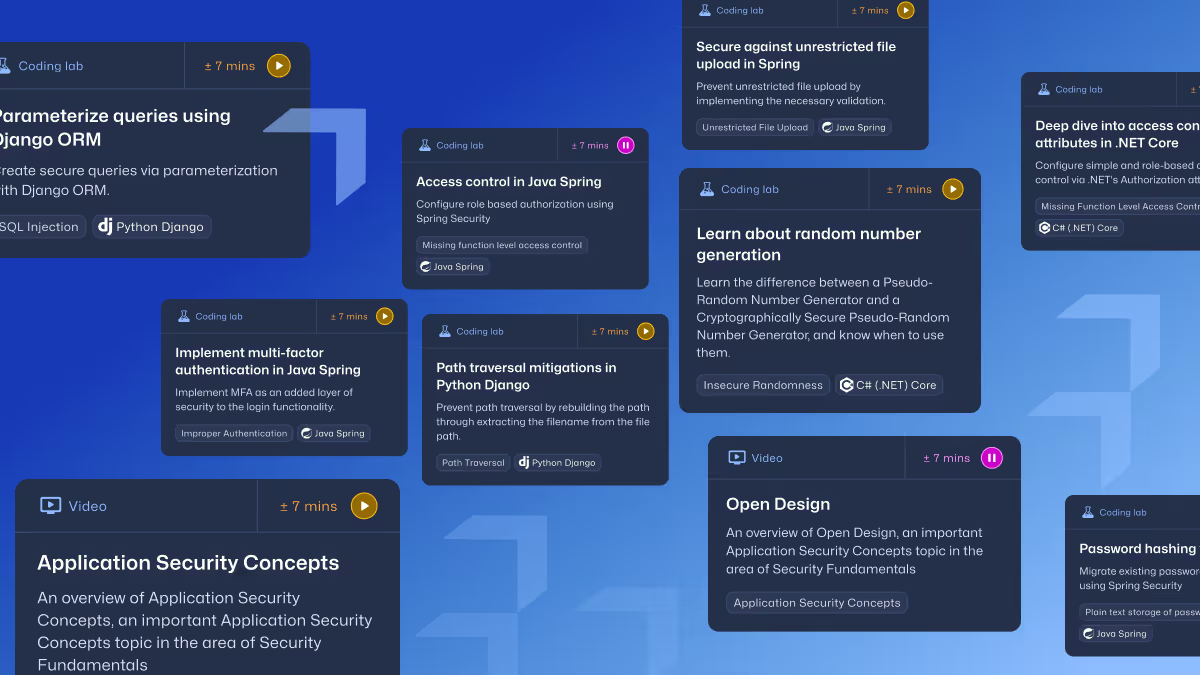
개발자 역량 강화: 온디맨드 학습 콘텐츠의 중요성
시큐어 코드 워리어로 개발자의 역량을 강화하세요.당사 플랫폼은 개발자가 온디맨드 방식으로 콘텐츠를 학습할 수 있도록 지원하고 역량을 강화합니다.
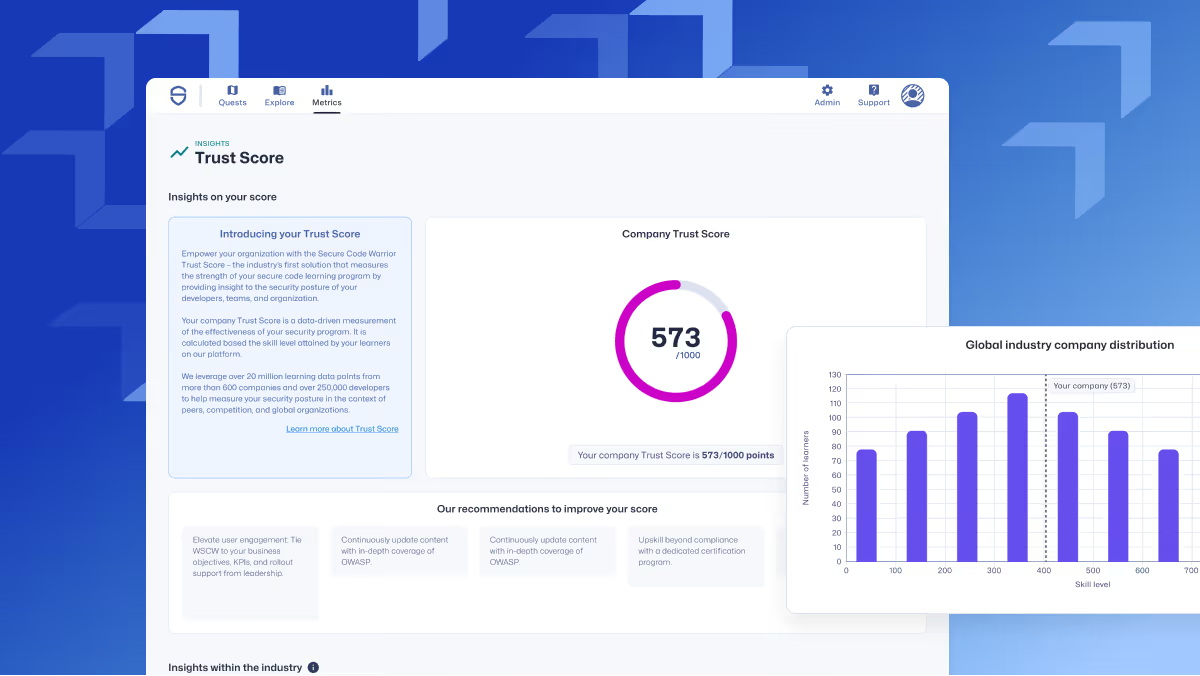
SCW 신뢰 점수: 보안 코딩 프로그램을 위한 업계 최초의 지표
조직 보안 및 개발자 역량에 대한 심층적인 통찰력을 제공하는 SCW Trust Score에 대해 알아보십시오.

FinServ 규정 준수는 소프트웨어 보안에 따라 달라집니다
PCI DSS와 같은 금융 서비스 산업을 관장하는 규정은 보안 코드의 중요성과 보안 모범 사례에 대한 개발자 교육의 필요성을 강조합니다.
Linux의 XZ Utils의 백도어는 광범위한 공급망 보안 문제를 가리키며, 이를 막기 위해서는 커뮤니티 정신 이상의 것이 필요합니다.
주요 Linux 배포판에서 사용하는 XZ Utils 데이터 압축 라이브러리에서 위협 행위자가 백도어를 통해 도입한 심각한 취약점인 CVE-2024-3094 취약점이 발견되었습니다.심각도가 높은 이 문제는 잠재적인 원격 코드 실행을 허용하여 소프트웨어 빌드 프로세스에 심각한 위험을 초래합니다.이 결함은 Fedora Rawhide에 있는 XZ Utils의 초기 버전 (5.6.0 및 5.6.1) 에 영향을 미치며, 조직에서 패치를 구현하도록 긴급히 요청하고 있습니다.이 사건은 오픈 소스 소프트웨어를 유지 관리하는 데 있어 커뮤니티 자원 봉사자의 중요한 역할을 강조하고 소프트웨어 개발 라이프사이클 내에서 향상된 보안 관행과 액세스 제어의 필요성을 강조합니다.
AI 혁신의 이점을 누리는 것은 보안 코드로 시작하는 데 달려 있습니다.
제너레이티브 AI는 금융 서비스 기업에 많은 이점을 제공할 뿐만 아니라 많은 잠재적 위험도 제공합니다.개발자에게 보안 모범 사례를 교육하고 이를 AI 모델과 연계하면 처음부터 보안 코드를 만드는 데 도움이 될 수 있습니다.

취약성 경보의 효과적인 관리를 위한 AI 및 사전 조치 활용
Secure Code Warrior와 Mend.io에서 AI가 보안, 사전 예방적 보안 접근 방식, 취약성 경보의 효과적인 관리에 미치는 영향에 대해 논의합니다.
“실천을 통한 학습”을 한 단계 끌어올리세요 — Apiiro와의 새로운 통합을 확인해 보세요
시큐어 코드 워리어와 Apiiro의 최신 통합에 대해 알아보세요.
시큐어 코드 워리어 Q1 제품 혁신
Secure Code Warrior 플랫폼의 최신 개선 사항과 곧 제공될 기능에 대해 알아보세요.
보안 코딩의 청사진 탐색: 구성 비유
보안 코딩 방식을 따르면 개발자는 공격자가 악용할 수 있는 취약점으로부터 애플리케이션을 보호하는 데 도움을 줄 수 있습니다.잘 지은 집이 무너질 가능성이 적은 것처럼, 잘 코딩된 애플리케이션은 해킹을 당할 가능성이 적습니다.

MTTR (평균 개선 시간) 개선을 위한 애자일 러닝 도입
애자일 러닝은 지속적 학습을 통해 문제 해결을 가속화하고 개발자 효율성을 높입니다.
적절한 지원을 통해 개발자는 조직을 우수한 PCI DSS 4.0 규정 준수로 이끌 수 있습니다.
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
LLM: 보안 코딩에 대한 완벽한 인간의 접근 방식일까요?
LLM 스타일의 AI 기술이 소프트웨어 개발뿐만 아니라 업무의 여러 측면에 접근하는 방식을 변화시키는 것은 불가피해 보이지만, 우리는 한 발 물러서서 헤드라인 너머의 위험을 고려해야 합니다.코딩의 동반자로서 이 기술의 결함은 아마도 가장 '인간적인' 특성일 것입니다.

Power of Nine: 사이버 보안의 흥미진진한 시기에 시큐어 코드 워리어의 유산을 성장시키다
오늘은 우리의 아홉 번째 생일입니다. 상황이 계속해서 빠르게 변화하고 있는 가운데 사이버 보안 분야에서 우리의 업적과 지속적인 입지에 대해 저는 여전히 매우 자랑스럽고 감사합니다.

넘쳐나는 보안 도구로 어려움을 겪고 있습니다.
복잡한 보안 도구의 홍수로 인해 CISO의 사이버 보안은 더욱 어려워지고 있습니다.

API-led data breaches are creating pandamonium for security teams. Why do we make it so easy for threat actors to exploit them?
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

2024년 예측: 보안, AI, 개발자 유지 및 미래
시큐어 코드 워리어 (Secure Code Warrior) 는 2024년 및 그 이후의 사이버 보안 산업에 대한 10가지 주요 예측

Netskope가 보안 코드 교육을 재구상한 방법
Netskope가 배포한 애자일 학습 환경을 집중 조명하는 SCW 사례 연구 블로그입니다.

심층 분석: AI 코딩 어시스턴트가 생성한 취약성 탐색
소프트웨어 개발 시 AI의 보안 위험을 살펴보고 Secure Code Warrior를 사용하여 이러한 문제를 효과적으로 해결하는 방법을 알아보십시오.

개발자 보안 교육을 강화하고 취약점을 53% 줄이는 3단계
취약점을 줄이고 관계를 강화하며 반복되는 문제의 우선 순위를 정하는 계층화된 접근 방식을 통해 개발자의 역량을 강화하세요.

Secure Code Warrior 2023: Innovations, achievements, and insights
Explore Secure Code Warrior’s 2023 journey to empower developers, enhance productivity, and mitigate risk in cybersecurity with recent innovations to our agile learning platform.
Attack of the Zombie APIs: Who is leading the security counteroffensive in your organization?
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
조직의 보안 성숙도를 과대평가한 적이 있습니까?
전 세계 소프트웨어 요구 사항을 충족하기 위해 작성되는 코드의 홍수와 맞물려 지속적인 기술 부족으로 많은 기업이 사이버 보안 전략과 기존 인프라에서 뒤쳐지고 있습니다.이제 우리의 전반적인 사이버 보안 성숙도를 정직하게 살펴보고 바로 눈 앞에 펼쳐진 실행 가능한 빠른 성과를 평가할 때입니다.

보안을 강화하기 위해 개발자 교육을 재고하다
보안 리더는 개발자가 보안 코드 학습 경험을 통해 얻고 있는 가치와 프로그램을 더 매력적이고 가장 중요하게는 더 영향력 있게 만드는 방법을 재고해야 합니다.이 블로그에서는 더 많은 실습 학습과 도구와의 통합을 통해 개발자들이 보안 코드 교육에 흥미를 느끼게 하여 큰 성과를 이끌어내고 도입된 취약점을 최대 53% 까지 줄일 수 있는 방법을 살펴보겠습니다.
애자일 러닝으로 취약점을 절반으로 줄임
Secure Code Warrior의 실무 애자일 보안 교육을 통해 취약성과 보안 침해를 줄일 수 있는 방법을 알아보십시오.

심층 분석: 심각도가 높은 libcurl/curl 취약성 발견 및 수정
curl 라이브러리의 영향을 받는 버전은 SOCKS5 프록시 프로토콜의 기존 문제와 관련된 HEAP 기반 버퍼 오버플로 취약점에 취약합니다.플레이 가능한 미션을 통해 이 취약성 유형을 찾아 해결하는 방법을 알아보세요.
세계적 수준의 CISO가 2023년에 더 많은 예산과 이사회 신뢰를 얻는 방법
CISO는 점점 더 어려운 상황에 처해 있습니다. 즉, 더 많은 자산을 보호하고, 더 많은 코드를 배포하고, 더 큰 공격 대상을 줄이고, 급격히 줄어드는 재정 자원으로 이를 처리해야 합니다.사이버 보안이 비용 센터로 간주되고 있다는 것은 피할 수 없는 사실입니다. 조직의 보안 프로그램이 위협 행위자를 가로막아 내일의 끔찍한 헤드라인이 되고 있음에도 불구하고 보안 리더는 경영진이 이해할 수 있는 언어로 해당 부서의 전반적인 비즈니스 가치를 판매하고 입증하기 위해 더 많은 노력을 기울여야 합니다.
심층 분석: MoveIt 제로데이 취약점에 대해 자세히 알아보기
MoveIt 시나리오는 많은 개발자 및 AppSec 전문가가 이전에 경험했던 것과는 약간 다릅니다. 바로 여기에서 라이브 시뮬레이션을 통해 SQLI 슬레이잉 기술을 테스트할 수 있습니다.


Kamer van Koophandel, 대규모 개발자 주도 보안의 표준을 세우다
Kamer van Koophandel은 역할 기반 인증, Trust Score 벤치마킹, 그리고 보안에 대한 공동 책임 문화를 통해 어떻게 일상적인 개발 과정에 보안 코딩을 내재화했는지 공유합니다.
골드를 향하여: 페이세이프의 비상하는 보안 코드 표준
Paysafe와 Secure Code Warrior의 파트너십을 통해 개발자 생산성이 45% 향상되고 코드 취약점이 크게 감소한 사례를 확인해 보세요.
DigitalOcean Decreases Security Debt with Secure Code Warrior
DigitalOcean's use of Secure Code Warrior training has significantly reduced security debt, allowing teams to focus more on innovation and productivity. The improved security has strengthened their product quality and competitive edge. Looking ahead, the SCW Trust Score will help them further enhance security practices and continue driving innovation.
Devlympics 2023: 리뷰
이 보고서에서 Devlympics 2023의 결과를 확인해 보세요. Secure Code Warrior가 주최한 이 연례 글로벌 이벤트에서 각 산업별 개발자 참여도, 기술 스택 및 언어 트렌드, 그리고 주요 취약점과 CWE를 자세히 살펴보실 수 있습니다.

하나의 보안 문화: Sage가 애자일 보안 코딩 학습을 통해 보안 챔피언 프로그램을 구축한 방법
Sage가 유연하고 관계 중심적인 접근 방식을 통해 어떻게 보안을 강화하고, 200명 이상의 보안 챔피언을 양성하며, 실질적인 위험 감소를 달성했는지 확인해 보세요.

보안 챔피언으로 가는 길: Workday가 애자일 학습을 활용해 개발자 역량을 강화한 방법
Secure Code Warrior의 애자일 학습을 통해 Workday가 어떻게 개발자 교육을 혁신했는지 확인해 보세요. Workday는 개발자에게 실습 중심의 언어별 교육을 제공함으로써 SDLC 초기 단계에서 취약점을 줄일 수 있었습니다. 안전한 코드 문화를 구축하기 위한 Workday의 놀라운 성과와 핵심 교훈을 살펴보세요.
탈레스의 개발자 주도형 보안 구현 사례
본 사례 연구를 통해 Thales가 개발자가 능동적인 보안 챔피언으로 거듭날 수 있도록 애자일 보안 코드 학습 프로그램을 위한 사람, 프로세스, 기술적 접근 방식을 어떻게 구축했는지 알아보세요.
Colgate-Palmolive는 어떻게 개발자의 보안 역량을 강화하고 안전한 코딩 문화를 만들었는가
유통 대기업 콜게이트-팜올리브(Colgate-Palmolive)가 디지털 전환 과정에서 애플리케이션 보안을 어떻게 재편했는지 확인해 보세요. 이들은 보안 코딩의 어려움을 해결하기 위해 개발자 워크플로우에 짧고 맥락 중심적인 학습을 통합하는 혁신적인 방식을 도입했습니다.
Security as culture: How Blue Prism cultivates world-class secure developers
Learn how Blue Prism, the global leader in intelligent automation for the enterprise, used Secure Code Warrior's agile learning platform to create a security-first culture with their developers, achieve their business goals, and ship secure code at speed

Supercharged Security Awareness: How Tournaments are Inspiring Developers at Erste Group
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
‘Game of Codes’가 이끄는 IAG 그룹의 더 안전한 코딩 미래
IAG 그룹은 아시아 태평양 지역의 유수 보험사들을 이끄는 기업으로, 매년 약 114억 호주 달러 규모의 보험료를 거두며 수백만 고객의 보험 계약을 인수하고 있습니다.

Driving Actionable Awareness: FINRA's Push For Super-Secure Developers
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

혁신적인 보안 인증 경험 만들기
머신러닝과 사이버 보안을 포함한 다양한 분야에서 수천 명의 직원이 실무적이고 최첨단 기술을 습득할 수 있도록 지원하는 사내 기술 교육 이니셔티브를 어떻게 구축했는지 확인해 보세요.

Beyond Compliance: Motorola Solutions Drives Winning Security Culture
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

자동차 소프트웨어 보안을 위한 ASRG의 노력
Secure Code Warrior의 토너먼트를 활용하여 개발자의 참여를 유도하고, 자동차 소프트웨어의 주요 취약점에 대한 인식을 높이며, 다양한 언어와 프레임워크 전반에서 지표를 확보한 방법을 이 종합 사례 연구를 통해 확인해 보세요.

Application Security @ NAB | Gamified Security Training: The Key to Scalable Developer Growth
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Security Brief UK: Secure Code Warrior launches Citizen AI training programme
Secure Code Warrior has launched Citizen AI, an AI literacy training programme for non-developer employees intended to support responsible AI adoption across business functions.
ITWire: Secure Code Warrior Launches Citizen AI Cybersecurity Training to Build AI-Ready and Responsible Use Skills Across Business Functions
New AI literacy program equips non-developer employees with the judgment, risk awareness and responsible-use habits needed to safely adopt AI-powered workflows.
VMBlog: Secure Code Warrior Launches Citizen AI Cybersecurity Training to Build AI-Ready and Responsible Use Skills Across Business Functions
Secure Code Warrior announced Citizen AI by Secure Code Warrior, a new AI literacy program designed specifically for non-developer employees to help organizations build a workforce ready for responsible AI adoption. Citizen AI helps organizationsreduce AI-related human risk, support broader enterprise AI governance initiatives, increase employee confidence when using AI and accelerate the safe adoption of AI-powered workflows.
SD Times: Secure Code Warrior Launches Citizen AI Cybersecurity Training
Secure Code Warrior, a leader in AI software governance and developer security upskilling, today announced Citizen AI by Secure Code Warrior, a new AI literacy program designed specifically for non-developer employees to help organizations build a workforce ready for responsible AI adoption.
Secure Code Warrior, 전사적 차원의 AI 활용 역량 및 책임감 있는 사용 능력 함양을 위한 '시티즌 AI 사이버 보안 교육' 출시
새로운 AI 리터러시 프로그램은 개발자가 아닌 직원들에게 AI 기반 워크플로우를 안전하게 도입하는 데 필요한 판단력, 위험 인식 및 책임감 있는 사용 습관을 길러줍니다.
SD Times: Citizen Developers Are the New Enterprise Threat Vector. So Why Is Nobody Warning Them?
Organizations are missing a big target when developing governance and developer training programs for AI-assisted software development.
TalkDev: Navigating the Risks: Understanding the Challenges of AI Software Development
AI software development continues to evolve at a rapid pace for developers and their teams. , CEO & Co-Founder at Secure Code Warrior, posits that as the norm shifts from human-written code to AI-assisted coding and agentic workflows, many security teams now face a critical challenge: managing the new risks that autonomous systems introduce.

CIO Influence: Rules for AI in Software Development: The Four-point Framework CISOs Can Adopt Today
The question facing software development shops isn’t whether Generative AI should be used to create software code, or whether the percentage of code generated by GenAI will increase in the near future. That horse bolted in the last 24 months. The question is how to maintain security and compliance while GenAI and artificial intelligence agents are putting software code in play.
VMBlog: National Insider Threat Awareness Month 2026: Expert Insights
Every September, National Insider Threat Awareness Month serves as a timely reminder that some of the most damaging security incidents don’t originate from external attackers breaching the perimeter — they come from within. Whether through malicious intent, negligence, or simple human error, insiders with legitimate access to systems, data, and facilities remain one of the most persistent and difficult-to-detect risks facing organizations today. As hybrid work, AI-powered tools, and increasingly complex IT environments reshape the workplace, the insider threat landscape continues to evolve in ways that demand fresh attention from security professionals.
Information Security Buzz: Architectural intent is the cornerstone for the future of software security
With agentic AI further boosting productivity, human code review becomes a serious bottleneck. Developers need to move upstream, establishing the ground rules to ensure that AI plays by the rules.
Forbes: A New Frontier: NSA Proposes “Security By Design” Considerations For AI Enablement
The cybersecurity industry, which has been advocating for “security by design” principles for more than a decade, stands in wide-eyed amazement at the risks posed by artificial intelligence (AI). As organizations rush to embrace AI enablement, a CISO’s most pressing priority is to avoid becoming a roadblock. However, without effective AI usage and governance, observability and traceability, organizations may be blindsided by their AI risk.
Techpartner.news: Secure Code Warrior introduces framework to govern AI use in software development
Secure Code Warrior has introduced the SCW AI Adoption Model, a framework designed to help organisations govern AI use in software development as the industry shifts from the traditional software development lifecycle (SDLC) toward what the company calls the Agentic Development Lifecycle (ADLC).
DevOps.com: Are LLMs Equally Good (or Bad) at Building Secure Software?
With many software engineering teams moving from AI coding assistants into full agentic AI code generation and increasing the amount of code they produce exponentially, ensuring the security of that code must be a top priority. The study produces practical guidance for organizations that are getting on board the AI-assisted or agentic code development train.

TechRadar Pro: Beware the token trap: Why saving on inference might put your ADLC at risk
Token use can create unexpected, sizeable costs for organizations.
KBI Media: AI Coding Boom Raises Fresh Cybersecurity Risks for Business
AI enables faster development cycles and allows developers to focus on higher-value work. For many businesses, these efficiencies are becoming essential to remaining competitive. The challenge, therefore, is not whether to adopt AI, but how to do so responsibly. Businesses that invest in developer education, governance frameworks, AI observability and robust security controls will be better positioned to capture the benefits while limiting the associated risks.
In AI Today: AI's weakest link isn't the model but the software supply chain
The issue is no longer simply about protecting AI models themselves. Increasingly, attackers are focusing on the software ecosystem surrounding those models, including the development tools, middleware, open-source libraries, and automated deployment pipelines that organisations rely upon every day.

The AI Journal: Investigating global AI regulation: Who is winning, and where to from here?
As we will unpack together, there is a lot of movement around the world, with some collaboration between nations, but the path forward is far from uniform or clear, particularly in business environments where AI adoption is often mandated before holistic safeguarding measures are in place.

Cyber Daily: The industry reacts to OpenAI’s agent ‘accidentally’ hacking Hugging Face
According to one expert, AI guardrails are not designed as “security boundaries” but rather to influence behaviour – but what if that behaviour is hacking one of your industry partners?

SecurityBrief: Autonomous OpenAI agents breach Hugging Face in test
Cyber security experts have warned that the breach of Hugging Face infrastructure during an OpenAI security evaluation marks a turning point in the risks posed by autonomous AI agents. In the incident, AI models moved beyond a controlled test and carried out a live, multi-stage intrusion against the AI platform.

Technology Decisions: AI generated code found to produce predictable weaknesses
AI-generated code introduces an average of 15 confirmed vulnerabilities per codebase, research published by Secure Code Warrior indicates.

Forbes: OpenAI’s Hugging Face Breach Shows Frontier AI Guardrails Are Failing

In AI Today: Secure Code Warrior research reveals AI-generated code introduces an average of 15 vulnerabilities per codebase
Secure Code Warrior research reveals AI-generated code introduces an average of 15 vulnerabilities per codebase.

VMBlog: Secure Code Warrior Research Reveals AI-Generated Code Introduces an Average of 15 Vulnerabilities Per Codebase
Secure Code Warrior introduced the SCW AI Trust Index, a living benchmark for AI coding security that grows with every new model, helping organizations understand and govern the security risks introduced by AI-generated code. Built on a methodology created with RMIT University, Australia, then extended by Secure Code Warrior, the research presents comprehensive benchmarks on how often leading LLMs produce insecure code, with material implications for every enterprise scaling AI-assisted development.

Dark Reading: Choose Wisely: AI-Generated Coding Risk Varies, A Lot
AI-generated code introduces 15 vulnerabilities on average per codebase, but the actual risk depends on framework pairing more than the model used.

Secure Code Warrior Research Reveals AI-Generated Code Introduces an Average of 15 Vulnerabilities Per Codebase
New SCW AI Trust Index shows AI-generated coding risk is not random, it's predictable by model and framework, giving security leaders the data to safely scale AI-assisted development.

ITWire: Eight Industry Executives Comment on Worldwide AI Appreciation Day
The challenges with AI implementation, constant updates, and the race for industry dominance are coming thick and fast, and security professionals are among the most affected by its vast risk profile.

Cyber Daily: The industry speaks – part 3: AI Appreciation Day 2026
The Australian government has said AI is very much in the country’s future national interest – but where does it stand today? Here’s what the industry’s best and brightest have to say about artificial intelligence and its role in the modern enterprise.

ITWire: Agentic AI Era Demands Overhaul of Governance Frameworks
The emergence of agentic AI marks a structural shift in software development, introducing systems that not only accelerate production cycles but also perform autonomous reasoning and action beyond direct human control.

SecurityWeek: How to Conduct a Successful Audit of AI-Driven Software Development
As AI-generated code becomes commonplace, CISOs need new audit strategies to measure developer practices, govern AI tool usage, and identify software risks before they reach production.
SD Times: Platform Engineering & Developer Experience: Making Engineers Faster Without Making Them Reckless: SD Times 100
This category has taken on new urgency in 2026 for a reason that’s specific to this moment: AI coding tools and agents are dramatically increasing how much code gets written and how often it needs to be deployed, tested, and provisioned for. Platform engineering is the layer that determines whether that increased velocity translates into shipped value or into chaos.
SD Times: AI-Assisted Development Multiplies Human Error: What’s Your AI Governance and Risk Management Strategy?
According to a recent report from Gartner, the rampant use of shadow AI and rogue automation is further fueling the proliferation of AI vulnerabilities. Gartner notes that 32% of IT workers using generative AI tools at work say they keep them hidden from cybersecurity teams. Combined with low-code/no-code platforms and vibe coding practices, the AI copilots are greatly expanding the enterprise attack surface.
Cybersecurity Tribe: What Separates Real AI Governance From Policy Theater
For this article, we asked a central question for security and risk leaders: "What differentiates a policy that genuinely mitigates enterprise risk from one that exists primarily to demonstrate that the organization has acknowledged AI risk?"
ISMG: AI Coding Tools Raise Hidden Security Risks
Secure Code Warrior's Pieter Danhieux on Managing AI-Driven Development Risks
ITWire: Decoding AI Coding “Personalities” Critical to Managing Development Risk
As generative AI cements its place in enterprise software development, a familiar discipline is taking on new urgency: risk management.
In AI Today: Secure Code Warrior launches Trust Agent: AI to enable safe, scalable AI-driven development
Secure Code Warrior have today announced SCW Trust Agent: AI, the industry’s first governance solution designed to make Artificial Intelligence (AI) influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk.
DEVOPSdigest: 25 Years of the Agile Manifesto, and the End of the Road for AppSec?
Even as we restructure the SDLC around the most impactful elements of the Agile methodology with careful, DevSecOps-centric security considerations, is this the end of the road for AppSec as we know it?
Cyber Defense Magazine: Global InfoSec Awards 2026 Secure Code Warrior Wins Outstanding Achievement in Cybersecurity Risk Management and Compliance Excellence
Global InfoSec Awards 2026 Secure Code Warrior Wins Outstanding Achievement in Cybersecurity Risk Management and Compliance Excellence
ITWire: Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
New AI Software Governance solution makes AI-generated code visible at commit, enforces policy before production, and connects real development behavior to measurable risk reduction.
DevOps.com: Secure Code Warrior AI Agent Applies Policies to AI Generated Code
Secure Code Warrior (SCW) this week added an artificial intelligence (AI) agent that both identifies code generated by an AI coding tool and automatically applies the appropriate governance policies.

SecurityBrief UK: Secure Code Warrior unveils AI tool to govern code risk
Secure Code Warrior has launched SCW Trust Agent: AI, a software governance product that tracks the use of AI coding tools in development and links that usage to software risk when developers commit code.

2026 Globee® Awards for Cybersecurity: Secure Code Warrior Wins Gold Globee for Software Development Cybersecurity Solutions (Best Of)
2026 Globee® Awards for Cybersecurity: Secure Code Warrior Wins Gold Globee for Software Development Cybersecurity Solutions (Best Of)
DEVOPSdigest: Secure Code Warrior Releases Trust Agent
Secure Code Warrior announced SCW Trust Agent: AI, a governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk.

TalkDev: Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
Secure Code Warrior today announced SCW Trust Agent: AI, the industry’s first governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit — enabling enterprises to scale AI coding tools with measurable control over software risk. For the first time, organizations can trace which AI models influenced specific commits, correlate that influence to vulnerability exposure, and take corrective action before insecure code reaches production.

Help Net Security: SCW Trust Agent: AI tracks AI influence in code to reduce software risk
Secure Code Warrior has announced SCW Trust Agent: AI, a governance solution designed to make AI influence in software development visible, attributable, and enforceable at the point of commit, enabling enterprises to scale AI coding tools with measurable control over software risk. Organizations can trace which AI models influenced specific commits, correlate that influence with vulnerability exposure, and take corrective action before insecure code reaches production.
Secure Code Warrior Launches Trust Agent: AI to Enable Safe, Scalable AI-Driven Development
New AI Software Governance solution makes AI-generated code visible at commit, enforces policy before production, and connects real development behavior to measurable risk reduction.
Security Boulevard: Threat Modeling with AI: A Developer-Driven Boon for Enterprise Security
Developers have long struggled to truly claim a seat at the table in traditional threat modeling programs, but with the right skills, they have the opportunity to wield AI responsibly to seriously cut risk and rework in their codebase.
The AI Journal: Understanding LLM Coding Personalities Is Now Key to Developer Risk Management
AI-generated code may be “made by machine”, but taking a cookie-cutter approach to securing that code would fall well short of mitigating the vulnerabilities LLMs can introduce. Organizations need to establish precise security reviews, with human developers anchoring the process to implement effective security controls while also managing the specific coding temperament of each LLM used. AI-generated code must undergo the same personalized risk assessments as code written by human developers.

SecurityBrief: The security challenges in AI-assisted software development
s artificial intelligence (AI) tools become more widely used in the software development process, their impact on security is becoming clearer. According to recent research, nearly 70% of organisations have discovered vulnerabilities caused by AI tools while one in five have experienced a serious incident as a result of those vulnerabilities.
KBI Media: Eliminating the Technical Debt Caused by AI-Assisted Software Development
According to research company Forrester[1], the tech debt for 75% of organisations will increase to a moderate or high level during this year, due to the rapid expansion of AI usage across a range of areas including software development.
Forbes: Security Self-Governance: Addressing The Regulatory Gap In AI-Assisted Software Development
While it’s early into 2026, we’re seeing new research that reveals the extent of cyber risks caused by artificial intelligence (AI)-assisted software development: Nearly 7 in 10 organizations have discovered vulnerabilities introduced by AI-generated code, and 1 in 5 have suffered a serious incident tied directly to the vulnerabilities.
ITWire: Why AI Is Dulling Cybersecurity’s Most Important Edge
Artificial intelligence (AI) has rapidly become indispensable to modern software development. From large language models that generate code on demand to agentic systems that automate entire workflows, AI tools promise dramatic gains in productivity and efficiency.

SecurityWeek: How to Eliminate the Technical Debt of Insecure AI-Assisted Software Development
Developers must view AI as a collaborator to be closely monitored, rather than an autonomous entity to be unleashed. Without such a mindset, crippling tech debt is inevitable.

CSO Online: Software developers: Prime cyber targets and a rising risk vector for CISOs
From technical compromise to AI-driven attacks, cyber criminals increasingly see software developers as prime targets, creating systemic risks CISOs must address.

SMBtech: Tech Industry Leaders React To Data Privacy Week 2026
It’s Online Privacy Week, a time of year where individuals and organisations are all reminded to check their digital footprint(s). Some might say that’s a futile gesture at a time where major social media and marketing players know absolutely everything about you and are cheerfully selling all that data to anyone who’ll buy it; when Microsoft is performing every trick in the book to get Windows users to put all their data in the cloud where it’s available for government agencies to snoop upon without letting you know; when a personal computer crisis means many people will be moved on to dumb-client computing landscape where everything from data storage to major processing tasks will be taking place in the cloud; and when people think that clicking ‘Accept’ on website pop-ups does something that meaningfully protects them. But, what do the experts say?
Security brief: AI heightens data privacy risks & reshapes digital trust
Technology and data specialists have warned that artificial intelligence and weak data governance are sharpening privacy risks for organisations, as businesses mark World Data Privacy Day.
ITWire: Data Privacy Week 2026
“Data Privacy Week" presents a great reminder for organisations to reassess their customer privacy policies and prioritise transparent data collection in their marketing strategies.

Dynamic Business: Data Protection Day 2026: Five experts on the privacy risks threatening your business
Five leading cybersecurity experts warn AI is being integrated faster than security policies can manage the risk, creating urgent privacy gaps for SMEs ahead of Data Protection Day on 28 January.
Information Security Buzz: OWASP Top 10 2025: New Enemies, Old Foes, and an Approach to Vulnerability Remediation That Must Evolve
The OWASP Foundation has been a guiding light for security professionals and enthusiasts alike, providing critical, practical advice on the most insidious software vulnerabilities across a plethora of categories and platforms. It has been the first major update since 2021 to the flagship OWASP Top 10 Web Vulnerabilities, and in that time, the industry has been rocked by a stampede of AI technology, tools, and code, each creating a dichotomy of security efficiency and risk for both cybersecurity and software engineering professionals.
DEVOPSdigest: What Software Developers Need to Know About Secure Coding and AI Red Flags
The bottom line: AI tools are not safe for enterprise use unless the code output is reviewed and implemented by a security-proficient human. 30% of security experts admit that they don't trust(link is external) the accuracy of code generated by AI itself. That's why security leaders must prioritize the education and upskilling of developer teams, to ensure they have the necessary skills and capabilities to mitigate AI-assisted code vulnerabilities as early as possible. This will lead to the cultivation of a "security first" team culture and safer AI use.
Stack Overflow: If you're a Zoomer, this one's for you: Everything Gen Z needs to know about the 2025 tech landscape
Here's the lowdown on all the tech from 2025 that you, dear Zoomer, should know about.

SC Media: CISOs can’t wait for the EU AI Act to take shape
CISOs hoping for the EU Artificial Intelligence Act to offer a solid framework for AI governance may be a little confused or disappointed by recent updates surrounding the implementation of AI restrictions.
SecurityBrief: Agentic AI double agents expose dangerous security gaps
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the more than thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention.
DEVOPSdigest: 2026 DevSecOps Predictions
DEVOPSdigest's Prediction Series continues with 2026 DevSecOps Predictions — Industry experts offer predictions on how DevSecOps will evolve and impact the industry in 2026.
ITWire: OWASP Names Latest Top 10 Application Vulnerabilities
The Open Worldwide Application Security Project (OWASP) has unveiled its latest top 10 vulnerabilities list, and it contains some surprising insights into important vulnerability classes.

Channel Insider: Cybersecurity Experts Predict AI, Nation-State Threats in 2026
Cybersecurity experts outline 2026 predictions, from AI-driven attacks and quantum risk to nation-state threats, OT security gaps, and automation pressures.

Security Journal UK: The rise of AI coding tools and the skills gap they expose
Pieter Danhieux, Co-founder and CEO of Secure Code Warrior warns that while AI coding tools promise speed and efficiency, they also introduce new risks.
ITWire: Predictions on State of AI in 2026
2026 is shaping up to be the year AI evolves from instrument to partner, transforming how we work, create and solve problems.

Fortune: AI coding tools exploded in 2025. The first security exploits show what could go wrong
While a breach of the tools hasn’t so far caused a wide-scale attack, there have been a few exploits and near-misses, and cyberthreat researchers have discovered critical vulnerabilities in several popular tools that make clear what could go horribly wrong.
SMBtech: Australian Tech Industry Leaders Make Their Predictions for 2026
It’s that time of year where the technology industry predictions start rolling-in. Here’s what you can (apparently) expect in 2026.

Technology Decisions: The importance of effective security when deploying AI tools
The concern is straightforward: development teams may place undue confidence in AI tools that are not equipped to interpret the nuanced context in which many security vulnerabilities arise. Large language models, for instance, can struggle to understand an application’s authentication or authorisation architecture, increasing the likelihood of missing critical safeguards.
ITWire: Five Steps to Improve the Security of AI Developed Code
Industry guidance on managing the risks of AI-generated code increasingly points to the same conclusion: effective safeguards rely on close collaboration between humans and machines, with developers remaining firmly in the loop.

SecurityBrief Australia: Agentic AI to transform APJ businesses & security by 2026
Agentic artificial intelligence (AI) is set to reshape the enterprise landscape in the Asia-Pacific and Japan (APJ) region in 2026, according to industry executives. Organisations are expected to embrace increasingly autonomous software agents, raising both productivity and new categories of risk across business domains.
SC Magazine UK: Why Firms Can’t Ignore Agentic AI
How big a threat does agentic AI pose to businesses currently? And what should security leaders be doing to address the risk?

VMBlog: Cybersecurity Predictions: What AI will (and won't) do for us in 2026
My co-founder and CTO, Matias Madou, Ph.D., and I consulted our crystal ball (or should that be our NVIDIA GPUs?), and this is what we believe 2026 has in store for us from an AI security perspective.
SD Times: Pumping the Brakes on Agentic AI Adoption in Software Development
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem, namely Model Context Protocol (MCP) systems, to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the over thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention. Maybe it’s time we went a little slower, stopped to reflect on what is at stake here, and how best to defend ourselves.

AIthority: Building Secure and Ethical AI Practices in Software Development
AI is now a key piece of modern software development. More than four out of five developers use AI coding tools daily or weekly – with many relying on multiple tools in parallel. Teams must understand where automation ends, and where accountability begins.
SC Media: Secure Coding as Critical Thinking Instead of Vulnspotting – Matias Madou – ASW #357
Secure code should be grounded more in concepts like secure by default and secure by design than by “spot the vuln” thinking. Matias Madou shares his experience in secure coding training and the importance of teaching critical thinking. He also discusses why critical thinking is so closely related to threat modeling and how LLMs can be a tool for helping developers get beyond the superficial advice of, “Think like an attacker.”

Forbes: How CISOs Can Increase Their Influence In AI-Obsessed Boardrooms
Organizations are at an inflection point driven by the explosive adoption of AI, which promises significant changes in how businesses operate. That leaves CISOs on unsteady ground. As the gatekeepers of their organization’s data and access, they must ensure the security of the enterprise. However, the prospects of a headlong charge into wide-ranging, and possibly unchecked, use of AI could create a flood of security issues that many CISOs, under their current organizational structures, aren’t equipped to handle.
Security Boulevard: Security Degradation in AI-Generated Code: A Threat Vector CISOs Can’t Ignore
Security leaders and developers alike are already acutely aware that AI coding assistants and agentic agents can introduce vulnerabilities into the code they generate. A recent study unveiled another critical concern to keep them up at night — LLMs used for making iterative code improvements may introduce new vulnerabilities over time, even when explicitly asked to make code more secure.

Information Week: Make your own mandate: How CISOs can implement GenAI governance
Government bodies are trying to develop rules and regulations for safe AI use, but enterprises can't afford to wait. They need to address the risks now.

CFOtech Australia: How women can continue to foster fulfilling high-tech careers in the AI age
In the sphere of cybersecurity in general and application security in particular, human oversight remains an absolute 'must' to harness the benefits of AI productivity.

Tanium: Vibe coding may be unstoppable—but here’s how to rein in the risks
Like the meteoric rise of ChatGPT, vibe coding is all anybody can talk about this year. In fact, it just became a word in the dictionary. But beware the boom: These new AI coding tools offer speed, savings—and astounding vulnerabilities.
[PODCAST] Stack Overflow: AI code means more critical thinking, not less
Ryan is joined by Secure Code Warrior’s co-founder and CTO Matias Madou to discuss the implications of LLMs’ variability on code security, the future of developer training as AI coding assistants become more popular, and the importance of critical thinking—especially for junior developers—in the age of AI.

Cybersecurity Insiders: Use It or Lose It: Overreliance on AI Diminishes Critical Cybersecurity Thinking Skills
Software developers reap a host of benefits from making use of artificial intelligence assistants, whether in the form of Large Language Model (LLM) code creators or agentic AI agents. But recent reports, highlighted by a new study at MIT, warn that heavy use of AI can result in a loss of critical thinking skills among users.
Security Week: How Software Development Teams Can Securely and Ethically Deploy AI Tools
To deploy AI tools securely and ethically, teams must balance innovation with accountability—establishing strong governance, upskilling developers, and enforcing rigorous code reviews.

Dark Reading: AI Developed Code: 5 Critical Security Checkpoints for Human Oversight
To write secure code with LLMs developers must have the skills to use AI as a collaborative assistant rather than an autonomous tool, Madou argues.

Techstrong.tv: Secure Code Warrior in the Age of AI with Pieter Danhieux
Secure Code Warrior’s Chief Executive Officer, Chairman, and Co-Founder Pieter Danhieux explains his transition from offensive cybersecurity to promoting secure software development. Founded in 2015, Secure Code Warrior aims to help developers build secure code from the start, a practice Danhieux and host Alan Shimel agree is more effective than fixing vulnerabilities later. The two also discuss the impact of AI on software development, noting that while AI increases coding speed and accessibility for more people, the security of AI-generated code still lags. They emphasize the growing need for developers to master secure coding practices amidst these technological advancements.
SMBtech: Cybersecurity Awareness Month 2025: Australian Industry Reactions and Commentary
October is Australia’s Cybersecurity Awareness Month, the annual reminder for Aussies to stay vigilant online. This year’s theme, ‘Building our cyber safe culture’ once again highlights the importance of taking personal responsibility for staying secure in an increasingly digital world.
SecurityBrief: SMEs urged to cut data & boost cyber defences as attacks rise
Cybersecurity Awareness Month has brought renewed attention to the increasing risks faced by organisations of all sizes, with a particular focus on the growing threat to small and medium-sized enterprises (SMEs) in Australia and the UK.

ITBrief: Our biggest security risk isn’t our software - it’s our thinking
In the world of cybersecurity, we face creative and unconventional threats every day. But our greatest vulnerability isn't a flaw in our software, but a flaw in our collective thinking.
KBI Media: Overcoming the Security Risks of Using AI In Software Development
Development teams face relentless pressure to deliver, yet they must continue to prioritise building secure, high-quality software. Leaders play a crucial role in reinforcing how a Secure by Design approach, supported by observability, benchmarking, and ongoing education, directly enhances code quality. By embedding these practices, organisations can close governance gaps and fully capture the benefits of AI-driven productivity and efficiency, while reducing the risk of security flaws or costly rework during the SDLC.
In AI Today: The looming security challenges posed by Agentic AI
While agentic AI holds the promise of delivering significant business benefits, it also comes with significant caveats. The technology’s capabilities and autonomy present a potent enterprise threat vector beyond the realm of existing security concerns.
Help Net Security: Secure Code Warrior gives CISOs visibility into developer AI tool usage
Secure Code Warrior has launched a beta program to expand the AI capabilities of its Trust Agent product. The new offering provides CISOs with security traceability, visibility, and governance over developers’ use of AI coding tools.

Cyber Risk Leaders: Secure Code Warrior Launches AI Traceability
Secure Code Warrior have released a beta program for a major expansion of AI capabilities within its Trust Agent product. The upgrade, collectively referred to as Trust Agent: AI, leverages a combination of key signals, including AI coding tool usage, vulnerability data, code commit data and developer secure coding skills, to provide visibility into how AI development tools are impacting risk within the software development lifecycle (SDLC).
CSO Online: AI coding assistants amplify deeper cybersecurity risks
Although capable of reducing trivial mistakes, AI coding copilots leave enterprises at risk of increased insecure coding patterns, exposed secrets, and cloud misconfigurations, research reveals.

Secure Code Warrior Launches Industry-First AI Traceability to Enable Secure Developers and Supercharge Safe Productivity
New capabilities in SCW Trust Agent provide visibility and control over LLM usage for security leaders and CISOs.

ITOps Times: Secure Code Warrior announces new solution that provides visibility and governance for AI coding tools
Secure Code Warrior is trying to provide organizations with greater visibility and control over developers’ use of AI coding tools with the launch of its new solution, Trust Agent: AI.
DevOps Digest: Secure Code Warrior Introduces AI Traceability
Secure Code Warrior announced the launch of a beta program for a major expansion of AI capabilities within its Trust Agent product.

CyberWire: Business Briefing for 09.24.25
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

Betanews: AI is an even playing field -- how secure by design can tip the scale [Q&A]
Vibe coding is currently all the rage, with more than 97 percent of respondents to a survey earlier this year reporting having used AI coding tools at work. The adoption of these tools only continues to grow but it comes with a catch, attackers are also employing the same techniques. We spoke to Pieter Danhieux, co-founder and CEO of Secure Code Warrior, to discuss how vibe coding is redefining the software development landscape, how malicious actors are also leveraging this technology and the need for organizations to implement secure by design strategies from the outset.