

Insights from experts shaping secure development
Access expert content on secure coding, AI governance, and software risk management.


AI in the SDLC: Separating the Hype from the Security Reality
AI in the SDLC, presented in partnership with KnowBe4: Kawin Boonyapredee (CISO Advisor, KnowBe4) and Pieter Danhieux (CEO, SCW) unpack AI code security risks.

German OWASP Day 2026
Secure Code Warrior is sponsoring German OWASP Day 2026, bringing together AppSec practitioners to explore best practices in secure development, operations, and testing. SCW will share how to build security into every stage of the development lifecycle.

AdelaideSEC
Secure Code Warrior is hosting a secure coding tournament at AdelaideSEC. Developers and security professionals compete hands-on to identify and fix real-world vulnerabilities, sharpening skills and connecting with the local tech community.

Black Hat USA 26
Secure Code Warrior is exhibiting at Black Hat USA 2026 in Las Vegas. CEO Pieter Danhieux, Chief Customer Officer Fatemah Beydoun, and Chief Product and Technology Officer Alex Bullen will be on-site — reach out to book a meeting.

FS-ISAC APAC Summit
Can't wait to sponsor the FS-ISAC APAC Summit on July 14–15, 2026, in Singapore! Stop by Booth #8 to connect with our team, and don't miss Pieter Danhieux on July 14 at 1:15 PM in Heliconia 3401, revealing groundbreaking research on how AI coding models stack up against 10,000 human developers and what it means for security in AI-assisted development. See you there!

Gartner Security & Risk Management Summit 2026
Excited to sponsor the Gartner Security & Risk Management Summit in London, September 22–24, 2026! Come connect with our team to see how Secure Code Warrior is helping organizations govern AI-generated code and build lasting security skills across the SDLC. See you there!

OWASP Global AppSec USA
Proud to be a Silver Sponsor of OWASP Global AppSec USA 2026, celebrating its 25th anniversary on November 5–6, 2026, at the Hyatt Regency in San Francisco! Join us and 800+ application security professionals for sessions on AI security, threat modeling, a Capture the Flag competition, the OWASP Projects Demo Room, and exclusive networking receptions. Come find us there and let's connect!

Customer Showcase Webinar: Danske Bank
Danske Bank shares how they built a thriving secure coding culture — key strategies, real results, and lessons you can replicate. Watch on demand.

Gartner Security & Risk Management Summit
Join us at Gartner Security & Risk Management Summit, from June 1-3, 2026, in National Harbor, Maryland. We’re excited to join CISOs and cybersecurity leaders to gain expert insights on AI, risk resilience, and evolving threat landscapes to strengthen their organization's security posture. Don’t forget to connect and stop by our booth!

From Shadow AI to AI Software Governance: Regaining Visibility Across Your Codebase
Join Secure Code Warrior’s Matias Madou, CTO, and Tamim Noorzad, Director of Product, to learn how AI Software Governance provides the visibility and insight needed to manage AI-assisted development at scale.

OWASP Global AppSec EU
Can’t wait to sponsor OWASP Global AppSec EU Conference, marking its 25th anniversary from June 22–26, 2026, at the Austria Center in Vienna. Join us and over 800 other experts to explore the vibrant exhibitor hall, participate in the Meet the Mentor program, and earn CPE credits, all while enjoying exclusive networking receptions. Don’t forget to connect and stop by our booth!

OWASP BASC
We are excited to sponsor OWASP BASC on April 11 in Boston, MA. This is the premier application security conference that brings together security professionals, developers, and researchers to advance the field of application security in Boston.

OT Summit Madrid
Join us at the OpenText Summit Madrid 2026, an in‑person event designed to show how AI, cloud, and secure information management are powering a new generation of intelligent enterprises.

Cyber Security Summit
The Cyber Security Summit takes place on April 28th and 29th and is a premier conference that assembles top-tier experts, innovators, and exhibitors to showcase the latest trends, resilient IT strategies, and industry best practices. Don’t miss this opportunity to stop by our booth and connect with us!

Developer Security Proficiency: Accelerating Vulnerability Remediation with Integrated AST and Secure Developer Upskilling
Stop just finding vulnerabilities and start fixing them for good. Detecting a bug is only half the battle. To achieve true Secure by Design, security insights must translate into fast, effective remediation. Join experts Eric Johnson from Secure Code Warrior and Steven Zimmerman from Black Duck on March 18 to learn how to bridge the gap between detection and developer upskilling.

Tech Council Parliamentary Innovation Showcase
A flagship event of the Tech Council of Australia (TCA), the Parliamentary Innovation Showcase 2026 offers a fantastic opportunity for decision-makers, industry leaders, academics, and tech enthusiasts to explore cutting-edge technologies, exchange ideas, and gain insight into the future of research, investment, and innovation.

Product Security Virtual Summit
Secure Code Warrior is proud to partner with Cycode for this year’s Product Security Virtual Summit on January 28th. We’re diving into the future of secure software in the AI era and showing how to turn security alerts into developer superpowers.

Phishapalooza
SCW is honored to attend the 18th annual Phishapalooza to support the American Cancer Society. We look forward to connecting with the local cybersecurity community for a day of ice fishing and fundraising in the Twin Cities. Join us as we partner with GuidePoint Security to help drive impactful donations for this great cause.

OWASP LASCON
We are proud to be a Gold Sponsor for OWASP LASCON 2026 in Austin, TX! Join us at the Norris Conference Center as we gather with over 400 web developers and security professionals to share cutting-edge ideas in application security.

New York Secure Code Showdown
SCW, OWASP and AWS invite you to improve your skills at the New York Secure Code Showdown on Thursday, February 19, 2026, from 11 am to 4 pm EST. This tournament challenges you to identify and fix vulnerabilities across your choice of major software languages. It’s a great way to master secure coding foundations while competing against your peers!

Gold Coast BSides
We are excited to host a secure coding tournament at BSides Goldie! Join us on the Gold Coast Australia for a hands-on competition where you can test your ability to identify and fix real-world vulnerabilities. Whether you are a seasoned developer or a security newcomer, this is a fantastic opportunity to collaborate, sharpen your skills, and help build a more secure local tech community.

BSides Frankfurt
We are excited to host a secure coding tournament at BSides Frankfurt! Join us on the Goethe-Universität Frankfurt campus for a hands-on competition where you can test your ability to identify and fix real-world vulnerabilities. Whether you are a seasoned developer or a security newcomer, this is a fantastic opportunity to collaborate, sharpen your skills, and help build a more secure local tech community.

RSA Conference
We’re heading San Francisco to the RSA Conference 2026 to discuss. We help organizations empower developers with the skills to write secure code from the start. Join us at booth #250 in the South Expo Hall to see how we can build a community of security-driven developers in your organization.

FS-ISAC FinCyber Today Canada
We are ready to discuss developer risk management at FS-ISAC FinCyber Today Canada. We help financial institutions mitigate application risk by empowering their developers with secure code learning. Join us at our booth in the Solutions Hall to see how we can strengthen your security posture.
Threat Modelling with AI: Turning Every Developer into a Threat Modeler
Threat modeling with AI: how to turn every developer into a threat modeler, straight from their IDE.

Finding Your Developers
Curriculum and Onboarding Manager Katelynd Trinidad walks through different methods for locating code contributors at your organization to help ensure they receive secure code training.

The Power of Brand in AppSec DevSec DevSecOps (What's in an Acronym!?)
In AppSec, lasting program impact demands more than just tech—it needs a strong brand. A powerful identity ensures your initiatives resonate and drive sustained engagement within your developer community.

Vibe Coding: Practical Guide to Updating Your AppSec Strategy for AI
Watch on-demand to learn how to empower AppSec managers to become AI enablers, rather than blockers, through a practical, training-first approach. We'll show you how to leverage Secure Code Warrior (SCW) to strategically update your AppSec strategy for the age of AI coding assistants.

The Future of Cyber Security Virtual Conference
The Future Of Cyber Security Conference series aims to help businesses to stay one step ahead of attackers through a number of insightful sessions not available at any other security conference. Can’t wait to virtually meet with you!

SecTor
Come visit our booth #336 at SecTor 2025 in Toronto at the Metro Toronto Convention Centre! Us along with other security professionals will be sharing our latest research and techniques on underground threats and corporate defenses.

OWASP New Zealand Day
We are excited to attend OWASP New Zealand Day on the University of Auckland's campus! This conference is all about web and application security, with a mission to help Kiwi developers build more secure applications by focusing on robust architecture and development techniques. Be sure to visit our booth and connect with us to discuss our Developer Management Platform!

OWASP Global AppSec 2025 USA
Come visit us at our Expo Space at The Marriott Marquis in downtown Washington, DC! You'll have the chance to connect with us and over 800 security experts who share a passion for all things security.

OWASP BeNeLux Days
Visit our booth at OWASP BeNeLux Days happening in Mechelen, Belgium! This event brings you technical talks from experts in security, DevOps, and cloud, alongside hands-on training in top security areas. You'll also hear from industry leaders through keynote speeches, explore the latest security technology at vendor booths, and dive into activities like Capture The Flag and security tool training.

Melbourne AppSec & DevSecOps Summit
Get ready for an exciting day of insights and networking at the Melbourne AppSec & DevSecOps Summit! We can't wait to connect with security and development leaders like you, share ideas, and explore the latest trends in application security and DevSecOps. While you're there, let's schedule a brief meeting to discuss how our solutions can enhance your developer management strategies.

FS-ISAC Fall Summit
Visit us at FS-ISAC Fall Americas Summit for our Breakfast on Tuesday October 7, 8:00am - at the Catering Sponsor Table to explore how secure by design strategies and developer-focused risk management are transforming cybersecurity.

CISO Inspired Summit US
Join us at the CISO Inspired Summit New York 2025! This is your chance to connect with cybersecurity leaders, dive into proactive defense strategies, and build resilient security frameworks to confidently navigate today's evolving digital landscape.

CISO Inspired Summit UK
This November, join us at the CISO Inspired Summit UK 2025! Connect with fellow cybersecurity leaders to tackle rising threats, strengthen your digital defenses, and build robust strategies for business resilience in today's rapidly evolving cyber landscape.

BSides Bournemouth
BSides Bournemouth is a community-driven cybersecurity conference set to take place on August 16, at the Royal Bath Hotel in Bournemouth, UK. Come join us and other great sponsors like JP Morgan Chase for a day of insightful talks, networking and hands-on activities.

Black Hat USA
Join our executives at Black Hat USA at the Mandalay Bay in Las Vegas, NV! They are very excited to talk about AI/LLM secure code risk & ROI of skilled developers!

OWASP Global AppSec EU 2025
Visit us at Booth #G08 at OWASP Global AppSec EU to discover how secure by design principles and effective developer risk management are shaping the next generation of cybersecurity.

FS-ISAC EMEA Summit
Visit us at FS-ISAC EMEA Summit for our Breakfast on May 21, 8:00am - at the Catering Sponsor Table to explore how secure by design strategies and developer-focused risk management are transforming cybersecurity.

Cybersecurity Summit, Hamburg
We’re excited to connect with decision-makers, and innovators at the Cybersecurity Summit to discuss how proactive secure coding can accelerate software development while improving security posture.

OpenText Summit Madrid
Secure Code Warrior is proud to sponsor OpenText Summit Madrid 2025 on April 10! This exclusive event brings together leaders to explore how cloud, security, and AI are transforming information management. With tailored sessions across Explore, Transform, and Imagine, attendees will gain insights, best practices, and real-world success stories.

Australian Cyber Exchange
On April 3rd, our CEO, Pieter Danhieux, will speak at ACE25, the inaugural Australian Cyber Exchange, uniting government, private sector, and academia to strengthen Australia’s cyber capabilities. With a focus on innovation, sovereignty, and growth, ACE25 will feature panels, showcases, and pitch sessions tackling key cybersecurity challenges.

The Future Of Cyber Security London
Secure Code Warrior will be attending this full-day conference that brings together top cybersecurity experts to tackle the evolving threats in our digital world—from ransomware and botnets to crypto-hacking and cybercrime-as-a-service. Looking forward to insightful discussions and cutting-edge strategies!

OWASP SnowFROC
Join us at SnowFROC '25, Denver’s premier application security conference! This one-day event, drawing around 400 attendees, features hands-on training, top-notch food, and exceptional networking. Happening Friday, March 14, 2025, with expert-led presentations and workshops covering diverse cybersecurity topics.

BSides Limburg
Secure Code Warrior will be hosting a tournament at BSides Limburg this year on March 14! BSides is a community-driven cybersecurity event that goes beyond traditional conferences—fostering deep discussions, hands-on demos, and collaboration in an intimate setting. It’s where the next big ideas in security take shape!

2nd Annual 2025 OWASP Maine Secure Coding Tournament
OWASP Maine partnered with Secure Code Warrior will be hosting the 2nd annual OWASP Maine Secure Coding Tournament! This will be an in-person meetup where we welcome all software developers and appsec professionals from entry-level to principal. Bring your laptop and your secure coding wits and compete against your peers to be crowned the most secure coder in the state of Maine for 2025!

NDC Security 2025
Dive into cutting-edge topics, hands-on workshops, and networking with peers in the heart of Oslo. Don’t miss this chance to elevate your knowledge and shape the future of security. Visit us at spot H to learn how Secure Code Warriors empowers developers to improve productivity and code security!

RSAConference 2025
Visit us at Booth #2353 at RSAC 2025 to explore innovative solutions and join the conversation shaping the future of cybersecurity.

DevSecOps360 London
Join us Wednesday 22nd January 2025 at the IBM Innovation Studio London for an insightful event showcasing our latest integration vision for DevSecOps within the partner ecosystem.

Black Hat Europe
Join us at Black Hat Europe at the ExCeL in London

OWASP Benelux
SCW is proud to sponsor this year’s conference. Stop by our booth and learn about how SCW is helping companies master the OWASP Top 10 and reduce security risk for organizations all over Europe.

German OWASP Day 2024
Join Secure Code Warrior in Liepzig, Germany for great insights from OWASP, insights into the direction of software security in 2025 and fun networking.

DevSecOps 360 Toronto
Join SCW, IBM, Black Duck, Iruis Risk and Contrast to learn how your organization can accelerate development while minimizing vulnerabilities, delivering clear benefits to both business and security teams.

Cloud & Cyber Security Expo, Paris
Secure Code Warrior is thrilled to be a silver sponsor for the premiere Cybersecurity event in France. Looking forward to seeing you there.

OpenText World 2024
Join Secure Code Warrior and OpenText to learn how companies around the world are leveraging SAST findings to create an agile learning experience for secure coding.

DevSecOps 360 London
Join SCW, IBM, BlackDuck and IruisRisk for an insightful event showcasing our latest integrations and learn how companies have realized real business and productivity gains for their organisations.

AppSecDay Stockholm
Join Secure Code Warrior, OpenText and Sonatype for a discussion on navigating Open Source, compliance with NIS2, AI & DevSecOps

DevSecOps 360 Milan
Join us as we showcase how automation can drive faster, more secure development. A long with our partners IBM Cyber Security Services, Synopsys, and IriusRisk, we’ll dive into practical solutions to reduce vulnerabilities and keep your teams competitive.

Charity Pro-Am Scramble
Join Secure Code Warrior and our partner Arctiq for the Charity Pro-Am Scramble at Golf Le Diable in Mont Tremblant. Together, we’ll tee off for a great cause, supporting KidSport Québec to help more kids get involved in team sports and build their future through the power of play.

AppSec Day Utrecht
As application security evolves, organizations are increasingly integrating AI solutions for real-time threat detection and prevention. Join Secure Code Warrior and our partners Opentext and Sonatype!

SF 49er Red Zone Experience
Join SCW and Guidepoint for amazing football, great tailgate food and engaging conversations on software security and how to avoid being “tackled” by security vulnerabilities.

SCW Trust Agent/Q3 Product Roadmap Webinar
Join Patrick Collins, Secure Code Warrior’s Chief Product Officer, as he highlights and demos the brand-new SCW Trust Agent product offering and dives into the product roadmap for the coming months.

OWASP 2024 Global AppSec
The Global AppSec US Conference should be action-packed with new trends and topics discussed. Join us at our booth in San Francisco for a demo on our latest product offerings.

Transformation DevSecOps
DevSecOps enables the identification of security issues earlier in the development life cycle—surfaced directly to developers who can have the greatest impact.

Cybersecurity Summit
The leading experts from mid-sized to large corporations, will meet with innovative providers of digital solutions for Cybersecurity in business. Learn from experts on our stages and meet the leading providers in the trade show area.

Blackhat USA
Now in its 27th year, Black Hat USA returns to the Mandalay Bay Convention Center in Las Vegas with a 6-day program. The event will open with four days of specialized cybersecurity Trainings (August 3-8), with courses for all skill levels. The two-day main conference (August 7-8) will feature more than 100 selected Briefings, dozens of open-source tool demos in Arsenal, a robust Business Hall, networking and social events, and much more.

AppSec & DevSecOps Summit
Unravel, unite, and uplift your security strategies at the Melbourne AppSec and DevSecOps Summit 2024. Boost your security prowess and be at the forefront of the application and cloud security revolution.

Benchmark the Current State of your Security Program with SCW Trust Score
In today's rapidly evolving security landscape, understanding where your security program stands is paramount. Join, Secure Code Warrior Chief Technology Officer & Co-founder, Matias Madou, to discuss an industry leading innovation in our security program benchmarking: SCW Trust Score.

Nordic IT Security
The most reputable cyber security summit in Scandinavia, Nordic IT Security, has been around for 17 years acting as a steering wheel for navigation through the Nordic’s “cybersecurity watch-out” scheme.

Belgian Coffee Hour
For those RSAC attendees from Belgium, we are hosting a special "Last Coffee of the Day" on Tuesday, March 7 at 3:00 p.m. Join our resident Belgians, CEO Pieter Danhieux and CTO Matias Madou, and other executives from Secure Code Warrior as we wind down another successful day of RSAC with great coffee and delicious bites.

Taking charge of vulnerability alerts
Today’s threat landscape is increasingly unmanageable for many companies as they struggle with an application security approach built to react rather than take charge.

SCW Coffee Shop @ RSAC 2024
The SCW Coffee Shop is back for its 4th year! Join us for coffee and learn how to brew good security into your applications!

RSAConference 2024
The art of possibility is here! Stop by Booth 5179 to see how you can reduce your vulnerabilities by 53%

Meet with SCW Leadership @ RSAC24
Our co-founders and executives will be at Bluestone Lane Union Square Coffee Shop from May 6th through May 7th sipping on one of San Francisco’s best coffee and taking meetings.

In developers and AI, we trust
SCW Coffee Shop @RSAC24 presents: Join Matias Madou, our cofounder & CTO, and industry experts as they talk about the challenges and strategies for measuring security skills within the development cohort

How to quantify the effectiveness of your secure coding program with SCW Trust Score
SCW Coffee Shop @RSAC24 presents: Join Patrick Collins, CTPO, and Junie Dinda, CMO, as they dive into an in-depth session of the new SCW Trust Score, an industry-first benchmark reshaping the landscape of secure coding programs.

Carolina Hurricanes with GuidePoint
Join us and our partners from GuidePoint at the hockey rink for an exciting game and some AppSec talks!

Bay Area Vendor Happy Hour
More information soon.

Women Leaders in Security
SCW Coffee Shop @RSAC24 presents: Join Fatemah Beydoun, cofounder & CCO, along a panel of women leaders in the industry as they discuss how to shift left to course correct the gender gap in security. Moderated by our own, Holly Whalen, VP Channel Partners.

From Compliance Checkboxes to Risk Management: Unleashing the True Potential of SAST
Explore innovative strategies for maximizing the effectiveness of your SAST tools and implement a developer-driven security program.

secIT - Hannover 2024
Schedule time to meet or stop by Booth 14 during secIT!

Hands on Application Security Workshop
In partnership with AWS, Contrast Security, and Artiq, we bring you a interactive hands-on AppSec workshop

Virtual Wine Tasting - Ohio
Join us, GuidePoint, and other partners for a Virtual Wine Tasting with Silver Oaks Winery.

DevSecOps 360 - Riyadh
In partnership with IBM, Synopsys, and IriusRisk, we’ll share our latest integration vision for DevSecOps within the partner ecosystem

DevSecOps 360 - Munich
In partnership with IBM, Synopsys, and IriusRisk, we’ll share our latest integration vision for DevSecOps within the partner ecosystem

DevSecOps 360 - Dubai
In partnership with IBM, Synopsys, and IriusRisk, we’ll share our latest integration vision for DevSecOps within the partner ecosystem

The evolving role of the AppSec developer
Changes, causes, and considerations for one of the most important roles on your company's security team.

Strengthen left: Develop your security muscle
How to help your developers build and release secure software faster.
Shifting left for secure by design
Reduce the risks and costs associated with application security by empowering developers to be the first line of defense of your organization.
Shift left security training and vulnerability detection for embedded systems
In this webinar, we consider the challenges organizations face when adopting a security-first approach to development especially within embedded software and how to harness best practices in learning technology and benefit from shifting left to optimize developer secure code training.
Secure Coding Virtual Summit
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Saltworks and Secure Code Warrior: Better together
Preaching the gospel of when developer learning and skill-sets go up, code vulnerabilities go down.
Join us at the DEVOPS Conference
Come join us at the DEVOPS Conference this March 8-9 for some insightful talks and a chance to participate at the secure coding tournament. Get your free tickets now!
Is security a developer's problem?
Technology has exploded. And it ALL needs to be secured. Yet, security teams don’t have the manpower to cover all bases in times of rapid technological growth and evolving cybersecurity threats.
Increase software release velocity with holistic, developer-driven security
AWS + Secure Code Warrior on the importance of increasing the quantity and quality of developer code output.

Increase software release velocity with holistic, developer-driven security
We know these times may not suit everyone, so if you'd like to listen to the webinar at a more sociable hour please register and we'll send you a recording. With the rise of security breaches stemming from exploitable software vulnerabilities, organizations must look to minimize th
How to close the avoidance and remediation gap in open source compliance.
Closing this gap is important to help engineering teams and their leaders better understand the impact of open source software on an organization’s ability to create and deliver risk-free solutions. Hear how our experts tackle software audits.

How to build an AppSec program with a strong foundation
The importance and key approaches to setting a baseline when it comes to strategy development for your AppSec program.
Enabler 8: Branding Your Program
A secure coding program needs more than great content to succeed. Enabler 8 shows how branding turns participation into a coveted, status-driven experience.
Every Employee is Now on the Frontline of AI Cybersecurity
The enterprise technology landscape is shifting with a velocity few predicted until it was too late. We have officially crossed the threshold from human-written code and basic copilot assistance, into the era of the Agentic Development Lifecycle (ADLC). While autonomous AI agents promise unprecedented efficiency across multiple functions, they also bring an entirely new class of security and regulatory risks.
Enabler 7: Developer Recognition
Recognition fuels participation. Enabler 7 celebrates developer achievement loudly, with rewards and exclusive swag that mark real, earned secure coding wins.

Named in the Gartner® Hype Cycle™ for Application Security 2026
Secure Code Warrior is named in the Gartner® Hype Cycle™ for Application Security, 2026 for Agentic Coding Security and Secure Coding Training. Here's why.

Are you a CISO or Engineering Leader worried about the Security and Cost of LLM code generation?
Review the SCW AI Trust Index, our proprietary LLM benchmarking data, before going all-in on an AI model.

Enabler 6: Regular Reporting to Leadership
Executive buy-in doesn't sustain itself. Enabler 6 shows how regular reporting keeps leadership engaged, informed, and invested in program success.

The Future of AI Software Governance Is Built on Strong Partnerships
Discover why Secure Code Warrior is becoming a channel-first company and how trusted partners help organizations adopt AI Software Governance securely and at scale.

Citizen AI by Secure Code Warrior: Build an AI-Ready Workforce
Secure Code Warrior's AI literacy program for non-developer employees.

Why most CISOs are navigating AI adoption blindfolded (and how they can remove it)
Today, Secure Code Warrior issued an all-new white paper covering a prescriptive, directional AI adoption model that security leaders can use to identify their adoption stage and make real progress in bringing the AI security risks within their organization under control.
Enabler 5: Certification Programs
Move beyond one-and-done training. Enabler 5 builds multi-level certification programs that give developers meaningful progression and validated skills.
The NSA just issued its first MCP security guidance. Here's what it means for developer capability.
NSA published its first MCP security guidance. SCW's curriculum already covers 18 of 23 issues raised — here's how it maps.

Named in the Gartner® Hype Cycle™ for Secure Software Engineering 2026
Gartner names SCW twice. As AI agents take over more development, SCW gives you the capability and governance to adopt AI-driven development securely.

Announcing Adaptive Learning: The Antidote to AI Software Security Risk and Skill Gaps
Adaptive Learning bridges SCW Trust Agent with our entire learning platform, ensuring training stays perfectly aligned with real-time developer activity.
Secure coding learning that reflects real AI usage
Align secure coding training to real AI development activity — automatically assigning guidance to developers using AI tools, without manual intervention.Align secure coding training to real AI development activity — automatically assigning guidance to developers using AI tools, without manual intervention.
Train developers on the real risks in their code, whether human-written or AI-generated
Adaptive Learning auto-assigns targeted secure coding training to the developers introducing real vulnerabilities, reducing recurring risks at the source.Secure Code Warrior blog banner with a blue overlay over a developer working at a multi-monitor desk displaying code, alongside the headline 'Train developers on the real risks in their code.'l
Enabler 4: Low Barrier to User Access
Remove friction from your secure coding program with Enabler 4: Low Barrier to User Access. Explore SSO, front-loaded onboarding, and relay state strategies to get developers training with a single click.

Equipping Developers for the Generative AI Era: AWS Collaboration
I am proud to announce that Secure Code Warrior has signed a strategic collaboration agreement with Amazon Web Services (AWS). Given the rapid evolution of the threat landscape, this strategic collaboration could not come at a more mission-critical moment for both security leaders and future-focused developers.
Securing the Future of Software: SCW and KnowBe4 Join Forces
I am thrilled to announce today an upcoming strategic partnership between Secure Code Warrior and KnowBe4. KnowBe4 is a world-renowned leader in comprehensively managing human and agentic AI risk, making them the perfect partner to help us distribute foundational security awareness to organizations across the globe.

Post-Quantum Cryptography: Quantum Computers Will Break Today’s Encryption – Are You Ready?
Post-quantum cryptography (PQC) is critical for protecting data from quantum computing threats. Learn how “harvest now, decrypt later” exposes risk and how developers can prepare for quantum-safe security.

Enabler 3: Developer Communications Plan
Keep developers engaged in your secure coding program with a strong communications plan. Learn to highlight benefits, set the right tone, and celebrate wins.
The Agentic Era Arrived Early: Don’t Be Caught Off Guard
Anthropic's Claude Mythos represents a permanent, fundamental shift in how every security leader must approach their security program, especially with patch management of legacy systems.

Enabler 2: Senior Leadership Sponsorship
Explore Enabler 2: Senior Leadership Sponsorship. Learn why active buy-in from the CIO, CTO, and CISO is vital to drive developer adoption and program credibility.
Observe and Secure the ADLC: A Four-Point Framework for CISOs and Development Teams Using AI
While development teams look to make the most of GenAI’s undeniable benefits, we’d like to propose a four-point foundational framework that will allow security leaders to deploy AI coding tools and agents with a higher, more relevant standard of security best practices. It details exactly what enterprises can do to ensure safe, secure code development right now, and as agentic AI becomes an even bigger factor in the future.
Cybermon Is Back: Beat the Boss AI Missions Now Available On Demand
Cybermon 2025 Beat the Boss is now available year-round in SCW. Deploy advanced AI/LLM security challenges to strengthen secure AI development at scale.
AI Can Write and Review Code — But Humans Still Own the Risk
Anthropic’s launch of Claude Code Security marks a defining collision point between AI-assisted software development, and the rapid augmentation of how we approach modern cybersecurity.
Cyber Resilience Act Explained: What It Means for Secure by Design Software Development
Learn what the EU Cyber Resilience Act (CRA) requires, who it applies to, and how engineering teams can prepare with secure by design practices, vulnerability prevention, and developer capability building.

Enabler 1: Defined & Measurable Success Criteria
Enabler 1 kicks off our 10-part Enablers of Success series by showing how to link secure coding to business outcomes like risk reduction and velocity for long-term program maturity.
SCW Turns 11: Adaptability and Continuous Improvement
2025 was a big year for AI, for cybersecurity, and for SCW. I’m approaching 2026 with quiet confidence, and the optimism that only hard work paying off can bring.

Introducing the 10 Enablers of Success
Secure Code Warrior’s 10 Enablers guide organizations in building lasting secure coding programs by focusing on people, process, and program maturity stages.
OWASP Top 10 2025: Software Supply Chain Failures
OWASP Top 10 2025 lists Software Supply Chain Failures at #3. Mitigate this high-impact risk via strict SBOMs, dependency tracking, and CI/CD pipeline hardening.

New Risk Category on the OWASP Top Ten: Expecting the Unexpected
OWASP Top 10 2025 adds Mishandling of Exceptional Conditions at #10. Mitigate risks via "fail closed" logic, global error handlers, and strict input validation.
OWASP Top 10: 2025 – What’s New and How SCW Keeps You Aligned
Discover what changed in the OWASP Top 10: 2025 and how Secure Code Warrior makes the transition easy with updated Quests, Courses, and developer insights.
Adopt Agentic AI in Software Development FAST! (Spoiler: You Probably Shouldn't.)
Is the cybersecurity world moving too fast on agentic AI? The future of AI security is here, and it's time for experts to move from reflection to reality.

Solving the Visibility Crisis: How Trust Agent Bridges the Gap Between Learning and Code
Trust Agent by Secure Code Warrior solves the secure coding crisis, validating dev proficiency on every commit. It discovers all contributors & automates governance in your dev workflow.

Reclaiming Critical Thinking in AI-Augmented Secure Software Development
The AI debate isn't about use, but application. Discover how to balance the need for AI productivity gains with robust security by relying on developers who deeply understand their code.

Cybersecurity Risk Assessment: Definition and Steps
Address cybersecurity risks at your organization with this actionable guide to carrying out effective cybersecurity risk assessments.

Why Cybersecurity Awareness Month Must Evolve in the Age of AI
CISOs can’t rely on the same old awareness playbook. In the Age of AI, they must embrace modern approaches to safeguard code, teams, and organizations.

SCW Trust Agent: AI - Visibility and Governance for Your AI-Assisted SDLC
Learn how Trust Agent: AI provides deep visibility and governance over AI-generated code, empowering organizations to innovate faster and more securely.

Secure Coding in the Age of AI: Try Our New Interactive AI Challenges
AI-assisted coding is changing development. Try our new Copilot-style AI Challenges to review, analyze, and fix code securely in realistic workflows.

SCW Launches Free AI/LLM Security Video Series for Developers
Introducing our free 12-week AI/LLM security video series! Learn the foundational risks of AI-assisted coding and how to build safer applications.
AI/LLM Security Video Series: All Episodes, Updated Weekly
Your all-in-one guide to our 12-week AI/LLM security video series. Catch every episode, learn key AI security concepts, and follow along weekly.

What is Secure Coding? Techniques, Standards, and Resources
Learn what secure coding really means and how secure coding practices can reduce both vulnerabilities and security-related costs at your company.

10,000+ Secure Code Learning Activities: A Decade of Developer Risk Management
Celebrating 10,000+ secure code learning activities and a decade of empowering developers to reduce risk, improve code quality, and confidently tackle AI-assisted development.
When Good Tools Go Bad: AI Tool Poisoning, and How to Stop Your AI From Acting as a Double Agent
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Setting the Standard: SCW Releases Free AI Coding Security Rules on GitHub
AI-assisted development is no longer on the horizon — it’s here, and it’s rapidly reshaping how software is written. Tools like GitHub Copilot, Cline, Roo, Cursor, Aider, and Windsurf are transforming developers into co-pilots of their own, enabling faster iteration and accelerating everything from prototyping to major refactoring projects.

Close the Loop on Vulnerabilities with Secure Code Warrior + HackerOne
Secure Code Warrior is excited to announce our new integration with HackerOne, a leader in offensive security solutions. Together, we're building a powerful, integrated ecosystem. HackerOne pinpoints where vulnerabilities are actually happening in real-world environments, exposing the "what" and "where" of security issues.

Revealed: How the Cyber Industry Defines Secure by Design
In our latest white paper, our Co-Founders, Pieter Danhieux and Dr. Matias Madou, Ph.D., sat down with over twenty enterprise security leaders, including CISOs, AppSec leaders and security professionals, to figure out the key pieces of this puzzle and uncover the reality behind the Secure by Design movement. It’s a shared ambition across the security teams, but no shared playbook.

Is Vibe Coding Going to Turn Your Codebase Into a Frat Party?
Vibe coding is like a college frat party, and AI is the centerpiece of all the festivities, the keg. It’s a lot of fun to let loose, get creative, and see where your imagination can take you, but after a few keg stands, drinking (or, using AI) in moderation is undoubtedly the safer long-term solution.

Prompt Injection and the Security Risks of Agentic Coding Tools
How a coding agent was tricked into writing SQL injection-prone code, installing shell tools, and maybe even stalking its user

Introducing Quests: The Newest Addition to Your Secure Code Journey
Quests empower developers to master secure coding through interactive learning, reducing risk and optimizing development
The Decade of the Defenders: Secure Code Warrior Turns Ten
Secure Code Warrior's founding team has stayed together, steering the ship through every lesson, triumph, and setback for an entire decade. We’re scaling up and ready to face our next chapter, SCW 2.0, as the leaders in developer risk management.

10 Key Predictions: Secure Code Warrior on AI & Secure-by-Design’s Influence in 2025
Organizations are facing tough decisions on AI usage to support long-term productivity, sustainability, and security ROI. It’s become clear to us over the last few years that AI will never fully replace the role of the developer. From AI + developer partnerships to the increasing pressures (and confusion) around Secure-by-Design expectations, let’s take a closer look at what we can expect over the next year.
OWASP Top 10 For LLM Applications: What’s New, Changed, and How to Stay Secure
Stay ahead in securing LLM applications with the latest OWASP Top 10 updates. Discover what's new, what’s changed, and how Secure Code Warrior equips you with up-to-date learning resources to mitigate risks in Generative AI.

Trust Score Reveals the Value of Secure-by-Design Upskilling Initiatives
Our research has shown that secure code training works. Trust Score, using an algorithm drawing on more than 20 million learning data points from work by more than 250,000 learners at over 600 organizations, reveals its effectiveness in driving down vulnerabilities and how to make the initiative even more effective.

The Benefits of Benchmarking Security Skills for Developers
The growing focus on secure code and Secure-by-Design principles requires developers to be trained in cybersecurity from the start of the SDLC, with tools like Secure Code Warrior’s Trust Score helping measure and improve their progress.

You’ve got a friend in me: How AI coding tools and security-aware developers can work together safely
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Driving Meaningful Success for Enterprise Secure-by-Design Initiatives
Our latest research paper, Benchmarking Security Skills: Streamlining Secure-by-Design in the Enterprise is the result of deep analysis of real Secure-by-Design initiatives at the enterprise level, and deriving best practice approaches based on data-driven findings.
Deep Dive: Navigating the Critical CUPS Vulnerability in GNU-Linux Systems
Discover the latest security challenges facing Linux users as we explore recent high-severity vulnerabilities in the Common UNIX Printing System (CUPS). Learn how these issues may lead to potential Remote Code Execution (RCE) and what you can do to protect your systems.
Coders Conquer Security: Share & Learn - Cross-Site Scripting (XSS)
Cross-site scripting (XSS) uses the trust of browsers and ignorance of users to steal data, take over accounts, and deface websites; it's a vulnerability that can get very ugly, very quickly. Let's take a look at how XSS works, what damage can be done, and how to prevent it.

Introducing Our New Engagement Insights Report
Learn about our new Engagement Insight Report that provides in-depth analysis to help you measure your secure code learning efforts.

How DigitalOcean Reduced Software Security Debt and Pushed the Boundaries of Productivity
Secure Code Warrior helped DigitalOcean build and release quality code from the start, driving digital innovation and modernization with security-aware developers.

Women in Security are Winning: How the AWSN is Setting Up a New Generation of Security Superwomen
Secure-by-Design is the latest initiative on everyone’s lips, and the Australian government, collaborating with CISA at the highest levels of global governance, is guiding a higher standard of software quality and security from vendors.

SCW Trust Agent - Visibility and Control to Scale Developer Driven Security
SCW Trust Agent, introduced by Secure Code Warrior, offers security leaders the visibility and control needed to scale developer-driven security within organizations. By connecting to code repositories, it assesses code commit metadata, inspects developers, programming languages used, and shipment timestamps to determine developers' security knowledge.

Is Your Security Program Ready for CISA's Cybersecurity Strategic Plan?
The Cybersecurity Strategic Plan pushes major changes to the way most organizations approach cybersecurity, and developers are in a unique position to help achieve those new goals.
Engage & Empower: Highlighting Key Features for Developer Engagement
Learn all about our agile learning methods, Microsoft teams integration, and our reports for development engagement.
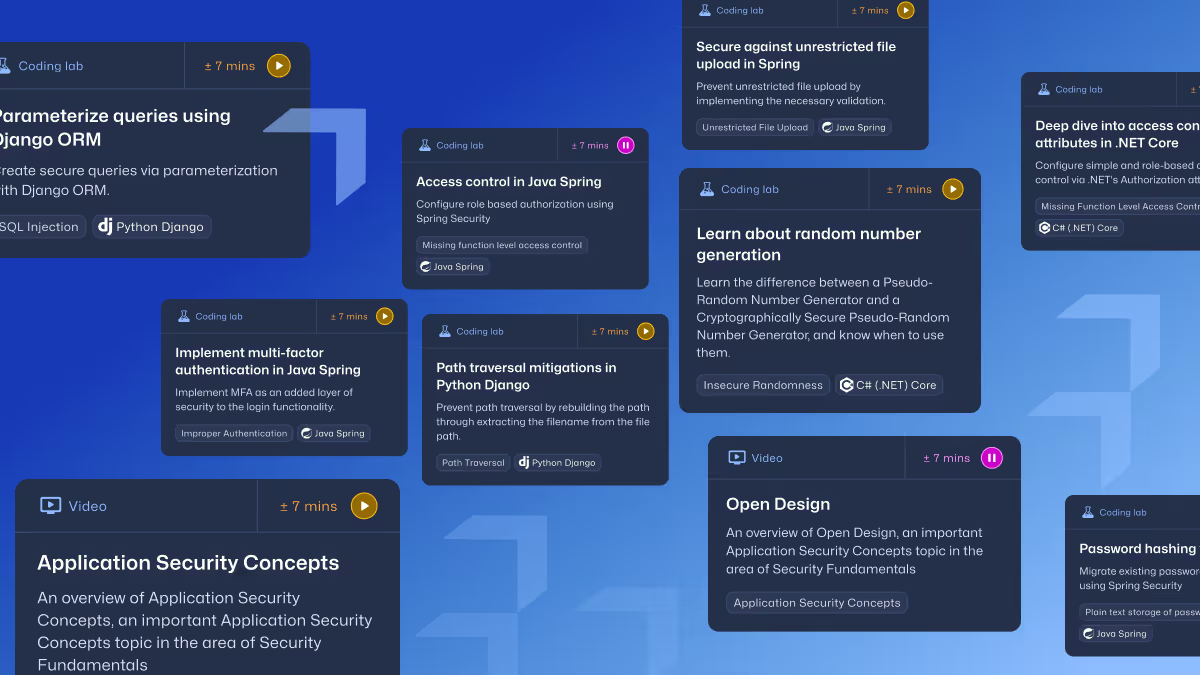
Empowering Developers: The Importance of Learning Content On Demand
Empower your developers with Secure Code Warrior. Our platform enables and empowers developers with learning content on demand.
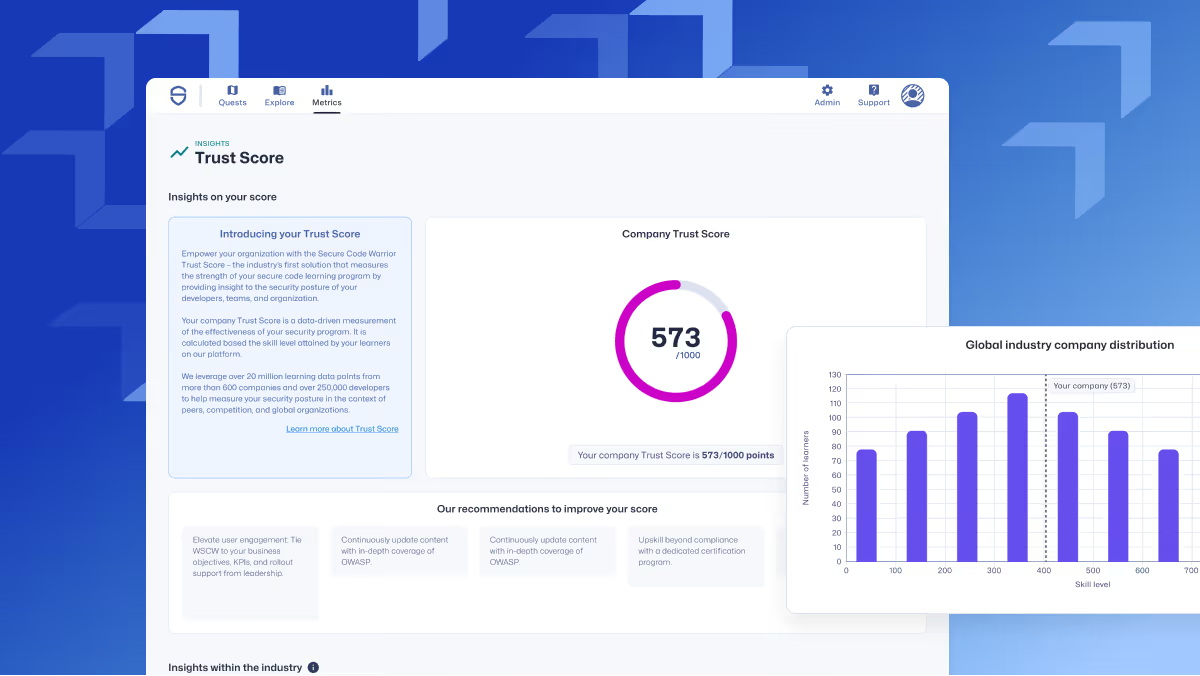
SCW Trust Score: An Industry-First Metric for Secure Coding Programs
Discover SCW Trust Score, providing deep insights into organizational security and developer competency.

FinServ compliance depends on software security
Regulations governing the financial services industry, such as PCI DSS, emphasize the importance of secure code and the need for training developers in security best practices.
The XZ Utils backdoor in Linux points to a wider supply chain security issue, and we need more than community spirit to keep it at bay
A critical vulnerability, CVE-2024-3094, was discovered in the XZ Utils data compression library used by major Linux distributions, introduced through a backdoor by a threat actor. This high-severity issue allows for potential remote code execution, posing significant risks to software build processes. The flaw affects early versions (5.6.0 and 5.6.1) of XZ Utils in Fedora Rawhide, with an urgent call for organizations to implement patches. The incident underscores the critical role of community volunteers in maintaining open-source software and highlights the need for enhanced security practices and access control within the software development lifecycle.
Reaping the benefits of AI innovation depends on starting with secure code
Generative AI offers financial services companies a lot of advantages, but also a lot of potential risk. Training developers in security best practices and pairing them with AI models can help create secure code from the start.

Harnessing AI and proactive measures for effective management of vulnerability alerts
Secure Code Warrior and Mend.io discuss impacts of AI on security, proactive security approaches, and effective management of vulnerability alerts.
Take “Learning by Doing” to the Next Level – Check out our new integration with Apiiro
Learn about Secure Code Warrior's latest integration with Apiiro.
Secure Code Warrior Q1 Product Innovations
Learn about the most recent improvements to the Secure Code Warrior platform and what will be coming soon.
Navigating the blueprints of secure coding: A construction analogy
By following secure coding practices, developers can help to protect their applications from vulnerabilities that can be exploited by attackers. Just as a well-built house is less likely to collapse, a well-coded application is less likely to be hacked.

Embracing agile learning for mean time to remediation (MTTR) improvement
Agile learning accelerates issue resolution and boost developer efficiency with continuous learning.
With the right support, developers can lead your organization to superior PCI DSS 4.0 compliance
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
LLMs: An (im)perfectly human approach to secure coding?
While it is looking inevitable that LLM-style AI technology will change the way we approach many aspects of work - not just software development - we must take a step back and consider the risks beyond the headlines. And as a coding companion, its flaws are perhaps its most “human” attribute.

The Power of Nine: Growing Secure Code Warrior’s legacy in an exciting time for cybersecurity
Today is our ninth birthday, and I remain immensely proud and grateful for our achievements and enduring place in cybersecurity land as the scene continues to change rapidly.

Suffering from a surfeit of security tools
A deluge of complex security tools is making cybersecurity even more challenging for CISOs.

2024 predictions: Security, AI, developer retention and the road ahead
Secure Code Warrior top 10 predictions for the cybersecurity industry in 2024 and beyond.

How Netskope Reimagined Secure Code Education
SCW case study blog that highlights the agile learning environment that Netskope has deployed.

Deep-dive: Navigating vulnerabilities generated by AI coding assistants
Explore the security risks of AI in software development and learn how to navigate these challenges effectively with Secure Code Warrior.

3 steps to boost developer security education and cut vulnerabilities by 53%
Empower developers with a tiered approach to cut vulnerabilities, fostering relationships and prioritizing recurring issues.
Have you overestimated your organization’s security maturity?
With a persistent skills shortage at odds with the deluge of code being written to satisfy the world’s software needs, many businesses are falling behind in their cybersecurity strategy and existing infrastructure. It’s time we took an honest look at our overall cybersecurity maturity, and assessed the viable quick wins that are right in front of us.

Rethinking developer education to supercharge security
Security leaders need to rethink the value developers are getting from the secure code learning experience, and how to make the program more engaging and, most importantly, more impactful. In this blog, we’ll explore how to get developers excited about the secure code education through more hands-on learning and integrations with their tools to drive a big results and reduce vulnerabilities introduced up to 53%.
Reduce vulnerabilities by half with agile learning
Learn how you can reduce vulnerabilities and security breaches with Secure Code Warrior’s hands-on agile security training.

Deep-Dive: Finding and fixing high-severity libcurl/curl vulnerabilities
Affected versions of the curl library are susceptible to a Heap-based buffer overflow vulnerability, related to a legacy issue with the SOCKS5 proxy protocol. Learn how to find and fix this vulnerability type with a playable mission.
How world-class CISOs are winning more budget and board trust in 2023
CISOs are finding themselves in an increasingly fraught position: Protect more assets, ship more code, reduce a bigger attack surface, and do it with rapidly diminishing financial resources. It’s an inescapable fact that cybersecurity is viewed as a cost center, and despite an organization’s security program being what stands in the way of a threat actor making them tomorrow’s disastrous headline, security leaders must do more to sell in and prove the overall business value of the department, in language that makes sense to the executive body.

Deep-Dive: Up close and personal with the MOVEit zero-day vulnerability
The MOVEit scenario is a little different from what many developers and AppSec professionals may have previously experienced, and you can test your SQLi-slaying skills in a live simulation right here.

What’s new at Secure Code Warrior: multi-company tournaments, SCIM, program workflows, and more!
New at Secure Code Warrior: set up tournaments for multiple companies, new coding guidelines, SCIM provisioning for users, and more!

Do software vendors care as much about security as you do?
It’s safe to say that the past couple of years have been transformational for cybersecurity standards, and while not mandatory, it should be a goal for all organizations to follow suit, and scrutinize vendor security practices as though they are part of their own internal security program.

Revealed: An exciting partnership to elevate agile learning and developer-driven security in the enterprise
Fresh off the back of our Series C funding announcement, I am thrilled to announce another step in our company’s journey. Security industry leader, Synopsys, has welcomed an exciting new addition to its product suite: Synopsys Developer Security Training, powered by Secure Code Warrior.

Code out of the cage: Why secure developers can ship without limits
It seems baffling that most developers who work on code that powers critical infrastructure, automobiles, medical tech, and everything in between, do so without first verifying their security prowess. On the other hand, why do security-skilled developers, who have repeatedly proven that they understand how to build things securely, need to queue with everyone else in the ever-slowing development pipelines because of all the security gates?

The ROI of an Agile Learning Platform
The cost of addressing code vulnerabilities and technical debt is high and continues to suppress software development teams’ productivity. Learn how implementing an agile learning platform for secure code can more effectively train developers on secure coding techniques to fix vulnerabilities faster as well as earlier in the SDLC and prevent them in the first place to drive significant cost avoidance. This blog outlines how to think about the financial impact and ROI of an agile learning platform.

Raising the bar for secure coding: Infusing agile learning into future-ready enterprises
We announced the closing of our Series-C funding round, having raised USD $50 million towards the next phase of our mission: helping more pioneering organizations harness the power of their development cohort in thwarting common vulnerabilities.

How to win over developers with agile learning for secure code
Learn how an agile learning platform for secure code can be embedded into developer workflows and tools, and start to build a culture of secure code learning.

PCI-DSS 4.0 will be here sooner than you think, and it’s an opportunity to elevate your organization’s cyber resilience
Earlier this year, the PCI Security Standards Council revealed version 4.0 of their Payment Card Industry Data Security Standard (PCI DSS). While organizations won’t need to be fully compliant with 4.0 until March 2025, this update is their most transformative to date, and will require most businesses to assess (and likely upgrade) complex security processes, and elements of their tech stack. This is in addition to implementing role-based security awareness training and regular secure coding education for developers.

From training to agile learning: How an agile learning platform for secure code revolutionizes your approach to secure software
Learn how an agile learning platform for secure code upskills developers, reduces risk, and lowers technical debt over time by starting left in the SDLC.

Rethinking Software in the Organizational Hierarchy
By helping define the responsibilities of our apps and software within a tight hierarchy, and enforcing those policies with least privilege, we can make sure that our apps and software also survive and thrive despite the threat landscape arrayed against them.

Proactive protection: Leveraging the National Cybersecurity Strategy for advanced threat prevention
CISA's National Cybersecurity Strategy represents the best chance we have at raising software standards across the board and, finally, ushering in a new era of security-skilled developers.
Kamer van Koophandel: Developer-Driven Security at Scale
Kamer van Koophandel shares how it embedded secure coding into everyday development through role-based certifications, Trust Score benchmarking, and a culture of shared security ownership.
Going for Gold: Soaring Secure Code Standards at Paysafe
See how Paysafe's partnership with Secure Code Warrior led to a 45% boost in developer productivity and a major reduction in code vulnerabilities.
Devlympics 2023: In Review
Explore the Devlympics 2023 results in this report. Dive into developer engagement, tech stack and languages trends in each industry that participated, and key vulnerabilities and CWEs covered in the annual global event hosted by Secure Code Warrior.

One Culture of Security: How Sage Built Their Champions Program
Discover how Sage enhanced security with a flexible, relationship-focused approach, creating 200+ security champions and achieving measurable risk reduction.

The path to security champions: How Workday utilized agile learning to upskill developers
Discover how Workday transformed developer training with agile learning through Secure Code Warrior. By empowering developer with hands-on, language-specific education, Workday reduced vulnerabilities early in the SDLC. See their impressive results and key takeaways to build a secure code culture.
How Thales implemented developer-driven security
In this case study, learn how Thales has developed people, process, and technology approaches for an agile secure code learning program in order to engage developers to become active security champions.
How Colgate-Palmolive boosted developer security skills and created a secure coding culture
Discover how retail giant Colgate-Palmolive reshaped its application security during its digital transformation journey. Facing challenges in secure coding, they innovated their approach by integrating bite-sized, in-context learning into the developer workflow.
How a ‘Game of Codes’ is leading IAG Group to a more secure coding future
IAG Group is the name behind many of the leading insurancecompanies in the Asia-Pacific region, underwriting policies formillions of customers to the tune of approximately AUD $11.4 Billionin premiums per annum.

Creating a revolutionary security certification experience
Learn how they created an in-house technology education initiative, aimed at supporting thousands of employees to learn practical, cutting-edge skills in a number of disciplines, including machine learning and cybersecurity.

ASRG's push for automotive software security
Explore this comprehensive case study to learn more about how they utilized Secure Code Warrior's tournaments to engage developers, increase awareness of key vulnerabilities affecting automotive software, and gain metrics across multiple languages and frameworks.

SC Media: CISOs can’t wait for the EU AI Act to take shape
CISOs hoping for the EU Artificial Intelligence Act to offer a solid framework for AI governance may be a little confused or disappointed by recent updates surrounding the implementation of AI restrictions.

SecurityBrief: Agentic AI double agents expose dangerous security gaps
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the more than thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention.
DEVOPSdigest: 2026 DevSecOps Predictions
DEVOPSdigest's Prediction Series continues with 2026 DevSecOps Predictions — Industry experts offer predictions on how DevSecOps will evolve and impact the industry in 2026.
ITWire: OWASP Names Latest Top 10 Application Vulnerabilities
The Open Worldwide Application Security Project (OWASP) has unveiled its latest top 10 vulnerabilities list, and it contains some surprising insights into important vulnerability classes.

Channel Insider: Cybersecurity Experts Predict AI, Nation-State Threats in 2026
Cybersecurity experts outline 2026 predictions, from AI-driven attacks and quantum risk to nation-state threats, OT security gaps, and automation pressures.

Security Journal UK: The rise of AI coding tools and the skills gap they expose
Pieter Danhieux, Co-founder and CEO of Secure Code Warrior warns that while AI coding tools promise speed and efficiency, they also introduce new risks.
ITWire: Predictions on State of AI in 2026
2026 is shaping up to be the year AI evolves from instrument to partner, transforming how we work, create and solve problems.

Fortune: AI coding tools exploded in 2025. The first security exploits show what could go wrong
While a breach of the tools hasn’t so far caused a wide-scale attack, there have been a few exploits and near-misses, and cyberthreat researchers have discovered critical vulnerabilities in several popular tools that make clear what could go horribly wrong.

SMBtech: Australian Tech Industry Leaders Make Their Predictions for 2026
It’s that time of year where the technology industry predictions start rolling-in. Here’s what you can (apparently) expect in 2026.

Technology Decisions: The importance of effective security when deploying AI tools
The concern is straightforward: development teams may place undue confidence in AI tools that are not equipped to interpret the nuanced context in which many security vulnerabilities arise. Large language models, for instance, can struggle to understand an application’s authentication or authorisation architecture, increasing the likelihood of missing critical safeguards.
ITWire: Five Steps to Improve the Security of AI Developed Code
Industry guidance on managing the risks of AI-generated code increasingly points to the same conclusion: effective safeguards rely on close collaboration between humans and machines, with developers remaining firmly in the loop.

SecurityBrief Australia: Agentic AI to transform APJ businesses & security by 2026
Agentic artificial intelligence (AI) is set to reshape the enterprise landscape in the Asia-Pacific and Japan (APJ) region in 2026, according to industry executives. Organisations are expected to embrace increasingly autonomous software agents, raising both productivity and new categories of risk across business domains.
SC Magazine UK: Why Firms Can’t Ignore Agentic AI
How big a threat does agentic AI pose to businesses currently? And what should security leaders be doing to address the risk?

VMBlog: Cybersecurity Predictions: What AI will (and won't) do for us in 2026
My co-founder and CTO, Matias Madou, Ph.D., and I consulted our crystal ball (or should that be our NVIDIA GPUs?), and this is what we believe 2026 has in store for us from an AI security perspective.
SD Times: Pumping the Brakes on Agentic AI Adoption in Software Development
An alleged nation-state attacker used Claude Code and a range of tools in the developer ecosystem, namely Model Context Protocol (MCP) systems, to almost autonomously target specific companies with benign open-source hacking tools at scale. Of the over thirty attacks, several were successful, and proved that AI agents could indeed execute large-scale, malicious tasks with little to no human intervention. Maybe it’s time we went a little slower, stopped to reflect on what is at stake here, and how best to defend ourselves.

AIthority: Building Secure and Ethical AI Practices in Software Development
AI is now a key piece of modern software development. More than four out of five developers use AI coding tools daily or weekly – with many relying on multiple tools in parallel. Teams must understand where automation ends, and where accountability begins.
SC Media: Secure Coding as Critical Thinking Instead of Vulnspotting – Matias Madou – ASW #357
Secure code should be grounded more in concepts like secure by default and secure by design than by “spot the vuln” thinking. Matias Madou shares his experience in secure coding training and the importance of teaching critical thinking. He also discusses why critical thinking is so closely related to threat modeling and how LLMs can be a tool for helping developers get beyond the superficial advice of, “Think like an attacker.”
Forbes: How CISOs Can Increase Their Influence In AI-Obsessed Boardrooms
Organizations are at an inflection point driven by the explosive adoption of AI, which promises significant changes in how businesses operate. That leaves CISOs on unsteady ground. As the gatekeepers of their organization’s data and access, they must ensure the security of the enterprise. However, the prospects of a headlong charge into wide-ranging, and possibly unchecked, use of AI could create a flood of security issues that many CISOs, under their current organizational structures, aren’t equipped to handle.
Security Boulevard: Security Degradation in AI-Generated Code: A Threat Vector CISOs Can’t Ignore
Security leaders and developers alike are already acutely aware that AI coding assistants and agentic agents can introduce vulnerabilities into the code they generate. A recent study unveiled another critical concern to keep them up at night — LLMs used for making iterative code improvements may introduce new vulnerabilities over time, even when explicitly asked to make code more secure.

Information Week: Make your own mandate: How CISOs can implement GenAI governance
Government bodies are trying to develop rules and regulations for safe AI use, but enterprises can't afford to wait. They need to address the risks now.

CFOtech Australia: How women can continue to foster fulfilling high-tech careers in the AI age
In the sphere of cybersecurity in general and application security in particular, human oversight remains an absolute 'must' to harness the benefits of AI productivity.

Tanium: Vibe coding may be unstoppable—but here’s how to rein in the risks
Like the meteoric rise of ChatGPT, vibe coding is all anybody can talk about this year. In fact, it just became a word in the dictionary. But beware the boom: These new AI coding tools offer speed, savings—and astounding vulnerabilities.
[PODCAST] Stack Overflow: AI code means more critical thinking, not less
Ryan is joined by Secure Code Warrior’s co-founder and CTO Matias Madou to discuss the implications of LLMs’ variability on code security, the future of developer training as AI coding assistants become more popular, and the importance of critical thinking—especially for junior developers—in the age of AI.

Cybersecurity Insiders: Use It or Lose It: Overreliance on AI Diminishes Critical Cybersecurity Thinking Skills
Software developers reap a host of benefits from making use of artificial intelligence assistants, whether in the form of Large Language Model (LLM) code creators or agentic AI agents. But recent reports, highlighted by a new study at MIT, warn that heavy use of AI can result in a loss of critical thinking skills among users.

Security Week: How Software Development Teams Can Securely and Ethically Deploy AI Tools
To deploy AI tools securely and ethically, teams must balance innovation with accountability—establishing strong governance, upskilling developers, and enforcing rigorous code reviews.

Dark Reading: AI Developed Code: 5 Critical Security Checkpoints for Human Oversight
To write secure code with LLMs developers must have the skills to use AI as a collaborative assistant rather than an autonomous tool, Madou argues.

Techstrong.tv: Secure Code Warrior in the Age of AI with Pieter Danhieux
Secure Code Warrior’s Chief Executive Officer, Chairman, and Co-Founder Pieter Danhieux explains his transition from offensive cybersecurity to promoting secure software development. Founded in 2015, Secure Code Warrior aims to help developers build secure code from the start, a practice Danhieux and host Alan Shimel agree is more effective than fixing vulnerabilities later. The two also discuss the impact of AI on software development, noting that while AI increases coding speed and accessibility for more people, the security of AI-generated code still lags. They emphasize the growing need for developers to master secure coding practices amidst these technological advancements.
SMBtech: Cybersecurity Awareness Month 2025: Australian Industry Reactions and Commentary
October is Australia’s Cybersecurity Awareness Month, the annual reminder for Aussies to stay vigilant online. This year’s theme, ‘Building our cyber safe culture’ once again highlights the importance of taking personal responsibility for staying secure in an increasingly digital world.
SecurityBrief: SMEs urged to cut data & boost cyber defences as attacks rise
Cybersecurity Awareness Month has brought renewed attention to the increasing risks faced by organisations of all sizes, with a particular focus on the growing threat to small and medium-sized enterprises (SMEs) in Australia and the UK.

ITBrief: Our biggest security risk isn’t our software - it’s our thinking
In the world of cybersecurity, we face creative and unconventional threats every day. But our greatest vulnerability isn't a flaw in our software, but a flaw in our collective thinking.
KBI Media: Overcoming the Security Risks of Using AI In Software Development
Development teams face relentless pressure to deliver, yet they must continue to prioritise building secure, high-quality software. Leaders play a crucial role in reinforcing how a Secure by Design approach, supported by observability, benchmarking, and ongoing education, directly enhances code quality. By embedding these practices, organisations can close governance gaps and fully capture the benefits of AI-driven productivity and efficiency, while reducing the risk of security flaws or costly rework during the SDLC.
In AI Today: The looming security challenges posed by Agentic AI
While agentic AI holds the promise of delivering significant business benefits, it also comes with significant caveats. The technology’s capabilities and autonomy present a potent enterprise threat vector beyond the realm of existing security concerns.

Help Net Security: Secure Code Warrior gives CISOs visibility into developer AI tool usage
Secure Code Warrior has launched a beta program to expand the AI capabilities of its Trust Agent product. The new offering provides CISOs with security traceability, visibility, and governance over developers’ use of AI coding tools.

Cyber Risk Leaders: Secure Code Warrior Launches AI Traceability
Secure Code Warrior have released a beta program for a major expansion of AI capabilities within its Trust Agent product. The upgrade, collectively referred to as Trust Agent: AI, leverages a combination of key signals, including AI coding tool usage, vulnerability data, code commit data and developer secure coding skills, to provide visibility into how AI development tools are impacting risk within the software development lifecycle (SDLC).

CSO Online: AI coding assistants amplify deeper cybersecurity risks
Although capable of reducing trivial mistakes, AI coding copilots leave enterprises at risk of increased insecure coding patterns, exposed secrets, and cloud misconfigurations, research reveals.

Secure Code Warrior Launches Industry-First AI Traceability to Enable Secure Developers and Supercharge Safe Productivity
New capabilities in SCW Trust Agent provide visibility and control over LLM usage for security leaders and CISOs.

ITOps Times: Secure Code Warrior announces new solution that provides visibility and governance for AI coding tools
Secure Code Warrior is trying to provide organizations with greater visibility and control over developers’ use of AI coding tools with the launch of its new solution, Trust Agent: AI.
DevOps Digest: Secure Code Warrior Introduces AI Traceability
Secure Code Warrior announced the launch of a beta program for a major expansion of AI capabilities within its Trust Agent product.

CyberWire: Business Briefing for 09.24.25
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.

Betanews: AI is an even playing field -- how secure by design can tip the scale [Q&A]
Vibe coding is currently all the rage, with more than 97 percent of respondents to a survey earlier this year reporting having used AI coding tools at work. The adoption of these tools only continues to grow but it comes with a catch, attackers are also employing the same techniques. We spoke to Pieter Danhieux, co-founder and CEO of Secure Code Warrior, to discuss how vibe coding is redefining the software development landscape, how malicious actors are also leveraging this technology and the need for organizations to implement secure by design strategies from the outset.
SD Times: Benchmarking AI-assisted developers (and their tools) for superior AI governance
If the tech stack lacks tools that oversee not only developer security proficiency, but also the trustworthiness of approved AI coding companions each developer uses, then it is likely that efforts to uplift the overall security program and the developers working within it will be short of the appropriate data insights to effect change.
ITWire: The Benefits and Risks of Using AI Tools in Software Development
The process of software development is undergoing a period of expedited change. Thanks to massive advances in artificial intelligence (AI) technology, projects can be completed more rapidly and by people with little or no prior experience.

LeadDev: Ethics are being forgotten as the AI race heats up
Is the tech industry capable of the change needed to curb ethical and environmental concerns?
Secure Code Warrior Expands Commitment to Secure by Design Best Practices with Free Secure Code Video Series for Developers
Launch of new 12-week video series on AI/LLM security empowers developers to safely adopt AI coding and mitigate emerging security risks.
CSO Online: When AI nukes your database: The dark side of vibe coding
As developers lean on Copilot and GhostWriter, experts warn of insecure defaults, hallucinated dependencies, and attacks that slip past traditional defenses.
The AI Journal: Resilience and Developer Risk Management: Two Pillars of Success in the Era of Secure by Design and AI Coding
Change is afoot in cybersecurity governance, and it couldn’t come at a more transformative time for security leaders worldwide. The White House issued a recent Executive Order (EO) designed to “reprioritize cybersecurity efforts to protect America”, and with it, reduce friction related to overzealous government oversight to focus on protecting critical digital assets and enhanced secure technology practices. Coupled with significant cuts to CISA, one could be forgiven for being apprehensive of the right approach going forward, especially in the wake of rapid AI technology progression and Secure by Design initiatives.

SecurityWeek: How to Close the AI Governance Gap in Software Development
Widespread adoption of AI coding tools accelerates development—but also introduces critical vulnerabilities that demand stronger governance and oversight.

teiss: When regulations aren’t enough
Pieter Danhieux at Secure Code Warrior explains why “Secure by Design” has emerged as mission critical for software development

Information Age: Vibe coding is a hot skill – and security experts are worried
GenAI tools are building insecure apps faster than ever.

CXFocus Magazine: Going above and beyond in 2026
Today’s customers are an exacting lot with little tolerance for suppliers that fail to meet their ever-increasing expectations. Almost 94 per cent of Australian consumers stopped purchasing from at least one company after a negative experience, according to CPM’s 2025 The State of Customer Experience in Australia Report.

SafetyDetectives: Interview With Matias Madou - CTO and Co-Founder at Secure Code Warrior
SafetyDetectives recently sat down with Matias Madou, CTO and Co-Founder of Secure Code Warrior, to discuss his journey from software developer to cybersecurity leader and entrepreneur. With a background in security research, obfuscation techniques, and nearly a decade at Fortify, Matias has seen firsthand how critical it is to upskill developers if organizations hope to defend against modern threats. In this interview, he shares how Secure Code Warrior is helping organizations foster a security-first development culture, the risks and opportunities of AI-driven coding tools, and why the path to safer software must always begin with better-trained developers.

Dark Reading: Do Claude Code Security Reviews Pass the Vibe Check?
AI-assisted security reviews from Anthropic and others could help level up enterprise application security in the era of vibe coding.

GovTech Review: The global challenge of achieving cyber resilience
Concerningly, 2030 is only five years away, and cybersecurity efforts — whether national, international or specific to organisations — still face many of the same barriers that have always hampered comprehensive security. For this reason there remains a question mark over whether countries will be able to meet their 2030 goals.

KBI Media: AI Coding Assistants Boost Productivity … But At What Cost to Security?
As the pressure mounts to ship faster and innovate more aggressively, development teams must remember that code security is no longer optional but a business-critical necessity.
Forbes: Beware Of Agentic AI’s Heel Turn As Corporate Security Villain
Enterprises need to assert AI governance and ensure that developers are equipped to maintain oversight, with the security skills to safely prompt and review AI-assisted code and commits.
Techradar Pro: Why continuous security improvement for developers is the key to renewed resilience
While change can be challenging to navigate, the current security climate feels like the perfect time to embrace measures that will improve software quality and reduce risk for years to come.
DevOps Digest: From Helper to Hacker: How AI Tools Can Be Turned Against You
A recent finding by InvariantLabs uncovered a critical vulnerability in the Model Context Protocol (MCP), an API-like framework allowing powerful AI tools to autonomously interact with other software and databases, that allows for what has been dubbed "Tool Poisoning Attacks," a new vulnerability category that could prove especially damaging in the enterprise.
Technology Decisions: Secure by Design: Vital in an evolving threat landscape
In the evolving world of software development, a familiar term is gaining renewed urgency: Secure by Design.
Information Week: Will Any Countries Meet the Cyber Resilience Challenge?
One of the key hurdles facing nations and enterprises in achieving cyber resilience goals is the lack of security personnel and advanced security skills.
SecurityBrief Australia: The risks of using AI in the software development pipeline
AI coding assistants are not going away, and the upgrade in code velocity cannot be ignored. However, security leaders must act now to manage their use safely.

ITWire: AI Appreciation Day
Artificial Intelligence Appreciation Day celebrates the way AI has changed our lives for the better. This year, we speak to AI leaders to analyse what the next wave of innovations has in store for us and their transformative impact on various industries worldwide.

Dynamic Business: AI Appreciation Day: What business leaders really think about AI right now
On AI Appreciation Day, industry experts reveal how smart, responsible AI use is transforming business, empowering people, and driving meaningful innovation.
In AI Today: How to keep AI-assisted software development under control
Faced with large workloads and relentless deadlines, developers are understandably inclined to turn to third-party AI tools, sometimes without vetting them or getting approval from supervisors. It’s creating a trend dubbed ‘Shadow AI’. This should be of concern for all senior executives as unmanaged AI decreases overall enterprise visibility of development processes while increasing the potential for new vulnerabilities that are not adequately captured or managed.

Help Net Security: Cybersecurity essentials for the future: From hype to what works
Cybersecurity never stands still. One week it’s AI-powered attacks, the next it’s a new data breach, regulation, or budget cut. With all that noise, it’s easy to get distracted. But at the end of the day, the goal stays the same: protect the business.

Cyber Daily: Bad practices are increasing security risks within software development projects
A recent CISA discussion paper details some exceptionally risky software development activities that are in all-too-common use.

Techstrong.tv: [VIDEO] Secure Code Warrior CTO Matias Madou on Empowering Developers with AI-Driven Security Tools
Matias Madou, CTO and Co-Founder of Secure Code Warrior, shares his journey in app security and how AI is helping developers write secure code. He introduces new AI security rules, available free on GitHub, and discusses the future of development tools and AI solutions.
DevOps.com: Secure Code Warrior Defines Security Rules for AI Coding
Secure Code Warrior has made available a set of security rules for application developers using artificial intelligence (AI) tools to generate code.
SecurityBrief Australia: Secure Code Warrior unveils free AI security rules for developers
Secure Code Warrior has released AI Security Rules on GitHub, offering developers a free resource aimed at improving code security when working with AI coding tools.
KBI Media: Overcoming The Complexity And Security Issues Posed By AI Coding Tools
The current software environment has grown out of control security-wise and this trend shows no signs of slowing. However there is hope for slaying the twin challenges of complexity and insecurity.
Secure Code Warrior Unveils Industry-First AI Coding Rulesets to Guide Safer AI Code Deployment
Secure Code Warrior, the leading developer risk management company, today announced the availability of AI Security Rules on GitHub – a first-of-its-kind, free resource to help developers generate more secure code when working with AI coding tools like GitHub Copilot, Cline, Roo, Cursor, Aider and Windsurf.
Help Net Security: Free AI coding security rules now available on GitHub
Developers are turning to AI coding assistants to save time and speed up their work. But these tools can also introduce security risks if they suggest flawed or unsafe code. To help address that, Secure Code Warrior has released a new set of free AI Security Rules on GitHub.

DevPro Journal: Secure Code Warrior unveils AI coding rulesets to guide safer AI code deployment
Community-driven resource empowers developer teams of all sizes to integrate AI safely into critical workflows.

SD Times: Managing the growing risk profile of agentic AI and MCP in the enterprise
Security leaders need to take a hard look at how these risks affect their business, being sure they understand the potential vulnerabilities that result from using agentic AI and MCP, and take the necessary steps to minimize those risks.

HackerOne Launches Technology Alliance Program to Advance AI-Powered Security Ecosystem and Customer Innovation
HackerOne, a global leader in offensive security solutions, today announced the launch of its PartnerOne Technology Alliance Program. The initiative is designed to accelerate secure innovation by connecting leading technology providers with HackerOne’s AI-powered platform that seamlessly scales human security expertise through AI agents to not just find but remediate vulnerabilities.
Dark Reading: Next-Gen Developers Are a Cybersecurity Powder Keg
AI coding tools promise productivity but deliver security problems, too. As developers embrace "vibe coding," enterprises face mounting risks from insecure code generation that security teams can't keep pace with.

Conversational AI News: Training Developers to Build Defensively with AI
Today we're meeting Pieter Danhieux, CEO & Co-Founder at Secure Code Warrior. They specialise in secure coding practices and developer risk management.
ITWire: The Importance Of Security Benchmarking When Using AI Development Tools
If it was possible to have an experienced chef in the kitchen to help prepare a sophisticated dish, most people would happily accept the assistance. The same holds true for a qualified contractor to work on a home-improvement project, or an office aide to handle tedious, repetitive tasks.
DevOps Digest: Fix It or Face the Consequences: CISA's Memory-Safe Muster
While CISA's efforts can help companies navigate the "need for speed" in a fast-moving DevOps environment, IT and security leaders across the private sector must do their part to prepare their companies for the necessary changes.

SC Magazine UK: Secure-by-Design Is Hard, but Our Online Future Depends on It
Secure software hinges on introducing security at the beginning of the SDLC.
ITWire: Experts Confirm DeepSeek Too Insecure for Enterprise Deployment
While DeepSeek’s capabilities seem to be extensive, experts have identified significant failings – particularly from a security perspective.
Cyber Daily: Secure-by-design principles struggle to find unified enterprise adoption
While awareness of the concept of ‘Secure by Design’ is growing within many organisations, its usage remains fragmented and inconsistent.

Built In: How to Tame ‘Unleashed’ AI-Assisted Software Development
The rise of AI coding assistants in software development has introduced new vulnerabilities. Our expert, Dr Matias Madou, offers advice for stemming the tide.

Cybersecurity Tribe: Experts Reveal How Agentic AI Is Shaping Cybersecurity in 2025
We were lucky enough at RSAC 2025 to interview a series of industry experts to explore this issue, "Where exactly are we with Agentic AI in cybersecurity in 2025?"

DevOps.com: How Benchmarking Can Help Software Development Teams Achieve CISA’s “Secure by Design”
Organizations can more readily achieve CISA’s Secure by Design through benchmarking by implementing the following developer-centric best practices.

Bank Info Security: Secure by Design: Moving Beyond Checkbox Compliance
Secure Code Warrior CEO Danhieux Urges Clarity Around Secure-by-Design Practices.

SecurityWeek: Developers Must Slay the Complexity and Security Issues of AI Coding Tools
The advantages AI tools deliver in speed and efficiency are impossible for developers to resist. But the complexity and risk created by AI-generated code can’t be ignored.

The AI Journal: Why Security Benchmarking Has Emerged as Critical for AI in Software Development Tools
In the last five years, nearly two-thirds of IT executives and administrators say their organisation has incorporated AI tools into the software development lifecycle (SDLC), according to research from KPMG and OutSystems, which makes available a low-code, AI-supported platform to build applications.
KBI Media: How Adopting Maturity Models Can Improve Enterprise IT Security
With risk assessments becoming a higher priority, organisations need to take an approach with developer-driven security that actively targets developer risk management, skills enhancement and strategic repository “gatekeeping”. Initiatives that can help them stay on course while assessing their current security levels and creating an action plan that aligns with BSIMM or OWASP SAMM.
Forbes: How Companies Can Chart The Way Along The Secure-By-Design Path
From our own observations, we've found that organizations generally need three to five years to fully integrate SBD into their software development practices as part of a developer risk management commitment. But we've also seen that it’s well worth the time and effort: Within the context of the software development life cycle (SDLC), SBD promotes a “security first” enterprise culture and mindset in eliminating vulnerabilities as early as possible in the process.

TechRadar Pro: Secure by design: what we can learn from the financial services sector
Secure by design in software development, inspired by financial services.

Dynamic Business: 26 Aussie startups to unleash cyber fixes at ACE 25
The Australian Cyber Exchange 2025 (ACE 25), in collaboration with the Tech Council of Australia (TCA), rolled out in Sydney and is aimed at building up Australia’s own cyber capabilities.
iTWire: The Tech Council of Australia Bolsters Collaboration To Building Sovereign Capability To Keep Australians Safe
The Tech Council of Australia (TCA) is collaborating with industry and government leaders to advocate for the national approach across the cyber ecosystem and is reinforcing its position on building sovereign cyber security capability.

Intelligent CIO: The Tech Council of Australia bolsters collaboration to building sovereign capability
Collaboration pitched as a critical step to ensure industry and government are taking a coordinated approach to building Australia’s cyber security and resilience.
KBI Media: How Organisations Can Achieve Secure-By-Design By 2030
Governments worldwide, from the UK to Australia, have set ambitious goals to enhance software security by 2030, particularly within critical infrastructure. However, achieving a secure-by-design (SBD) approach is not merely a matter of deploying advanced security tools or implementing stringent policies. Rather, it necessitates a fundamental shift in organisational culture, prioritising security at every level of software development.
Cyber Daily: Paving a pathway to better Australian cyber security preparedness
Australia’s goal of seeding a zero-trust culture across all organisations can be significantly achieved by focusing on the first line of defence against threat actors: software developers.
SecurityWeek: Security Maturity Models: Leveraging Executive Risk Appetite for Your Secure Development Evolution
Organizations can align their processes with one of two global industry standards for self-assessment and security maturity—BSIMM and OWASP SAMM.

SD Times: DeepSeek is unsafe for enterprise use, tests reveal
The birth of China’s DeepSeek AI technology clearly sent shockwaves throughout the industry, with many lauding it as a faster, smarter and cheaper alternative to well-established LLMs. However, similar to the hype train we saw (and continue to see) for the likes of OpenAI and ChatGPT’s current and future capabilities, the reality of its prowess lies somewhere between the dazzling controlled demonstrations and significant dysfunction, especially from a security perspective.

Energy Source & Distribution: How to boost security of Australia’s critical infrastructure
Increasing technical complexity and a widening attack surface are making life tough for IT security professionals. Faced with an evolving threat landscape, the pressure is on to deploy and maintain effective protection for critical infrastructure.
KBI Media: A Supercharged Security Culture is Needed to Navigate Australia’s Cybersecurity Rules
A success marker in cybersecurity has traditionally been for an organisation to have an uneventful year – but this has become much harder to pull off. Even if an organisation manages to navigate the threat landscape without incident, it must still meet an ever-growing list of requirements just to maintain its license to operate. Australian CISOs have never had to deal with a greater number of legislative and regulatory requirements being imposed to drive secure behaviours and uplift collective cybersecurity postures.

Intelligent CISO: Q&A: How organizations can achieve Secure-by-Design by 2030
Matias Madou, Co-founder and CTO, Secure Code Warrior, says Secure-by-Design (SBD) requires a cultural shift in how developers approach security.