What security practices do 300,000 developers really do?
BSIMM 8 is out! Fantastic. The one and only large-scale study on what security practices large organizations put in place to produce secure software.
The study is carried out by application security professionals under the supervision of Gary McGraw, making sure the gathered data is consistent, accurate and gives an insight into what 300,000 developers do on a day-to-day basis.In my latest presentation, I reference BSIMM numbers where I mention that on average, there are 2 application security professional per 100 developers.
However, that hasn't been the case since BSIMM4. BSIMM8 reports that this number is even less, now at 1.6 per 100 developers. Hiring more application security professionals will simply not work as there is a shortage of talent. More than ever, we need to give the developers the tools and the training to write secure code that is hands-on, readily available and scalable for organisations.
The report also shows that the most common activity in the Training practice is providing an awareness training to all employees at 67%. I started mapping what we do at Secure Code Warrior (SCW) in the Training practice and realized that our solution can tick off all the 12 activities in the Training practice ranging from level 1 (most companies do it) to level 3 (very few companies do it).
One single solution that can be used to cover an entire practice!Out of the 12 training practices, the most interesting practices for the Secure Code Warrior solution are:
- Level 1: Provide awareness training
- Level 1: Deliver on-demand individual training
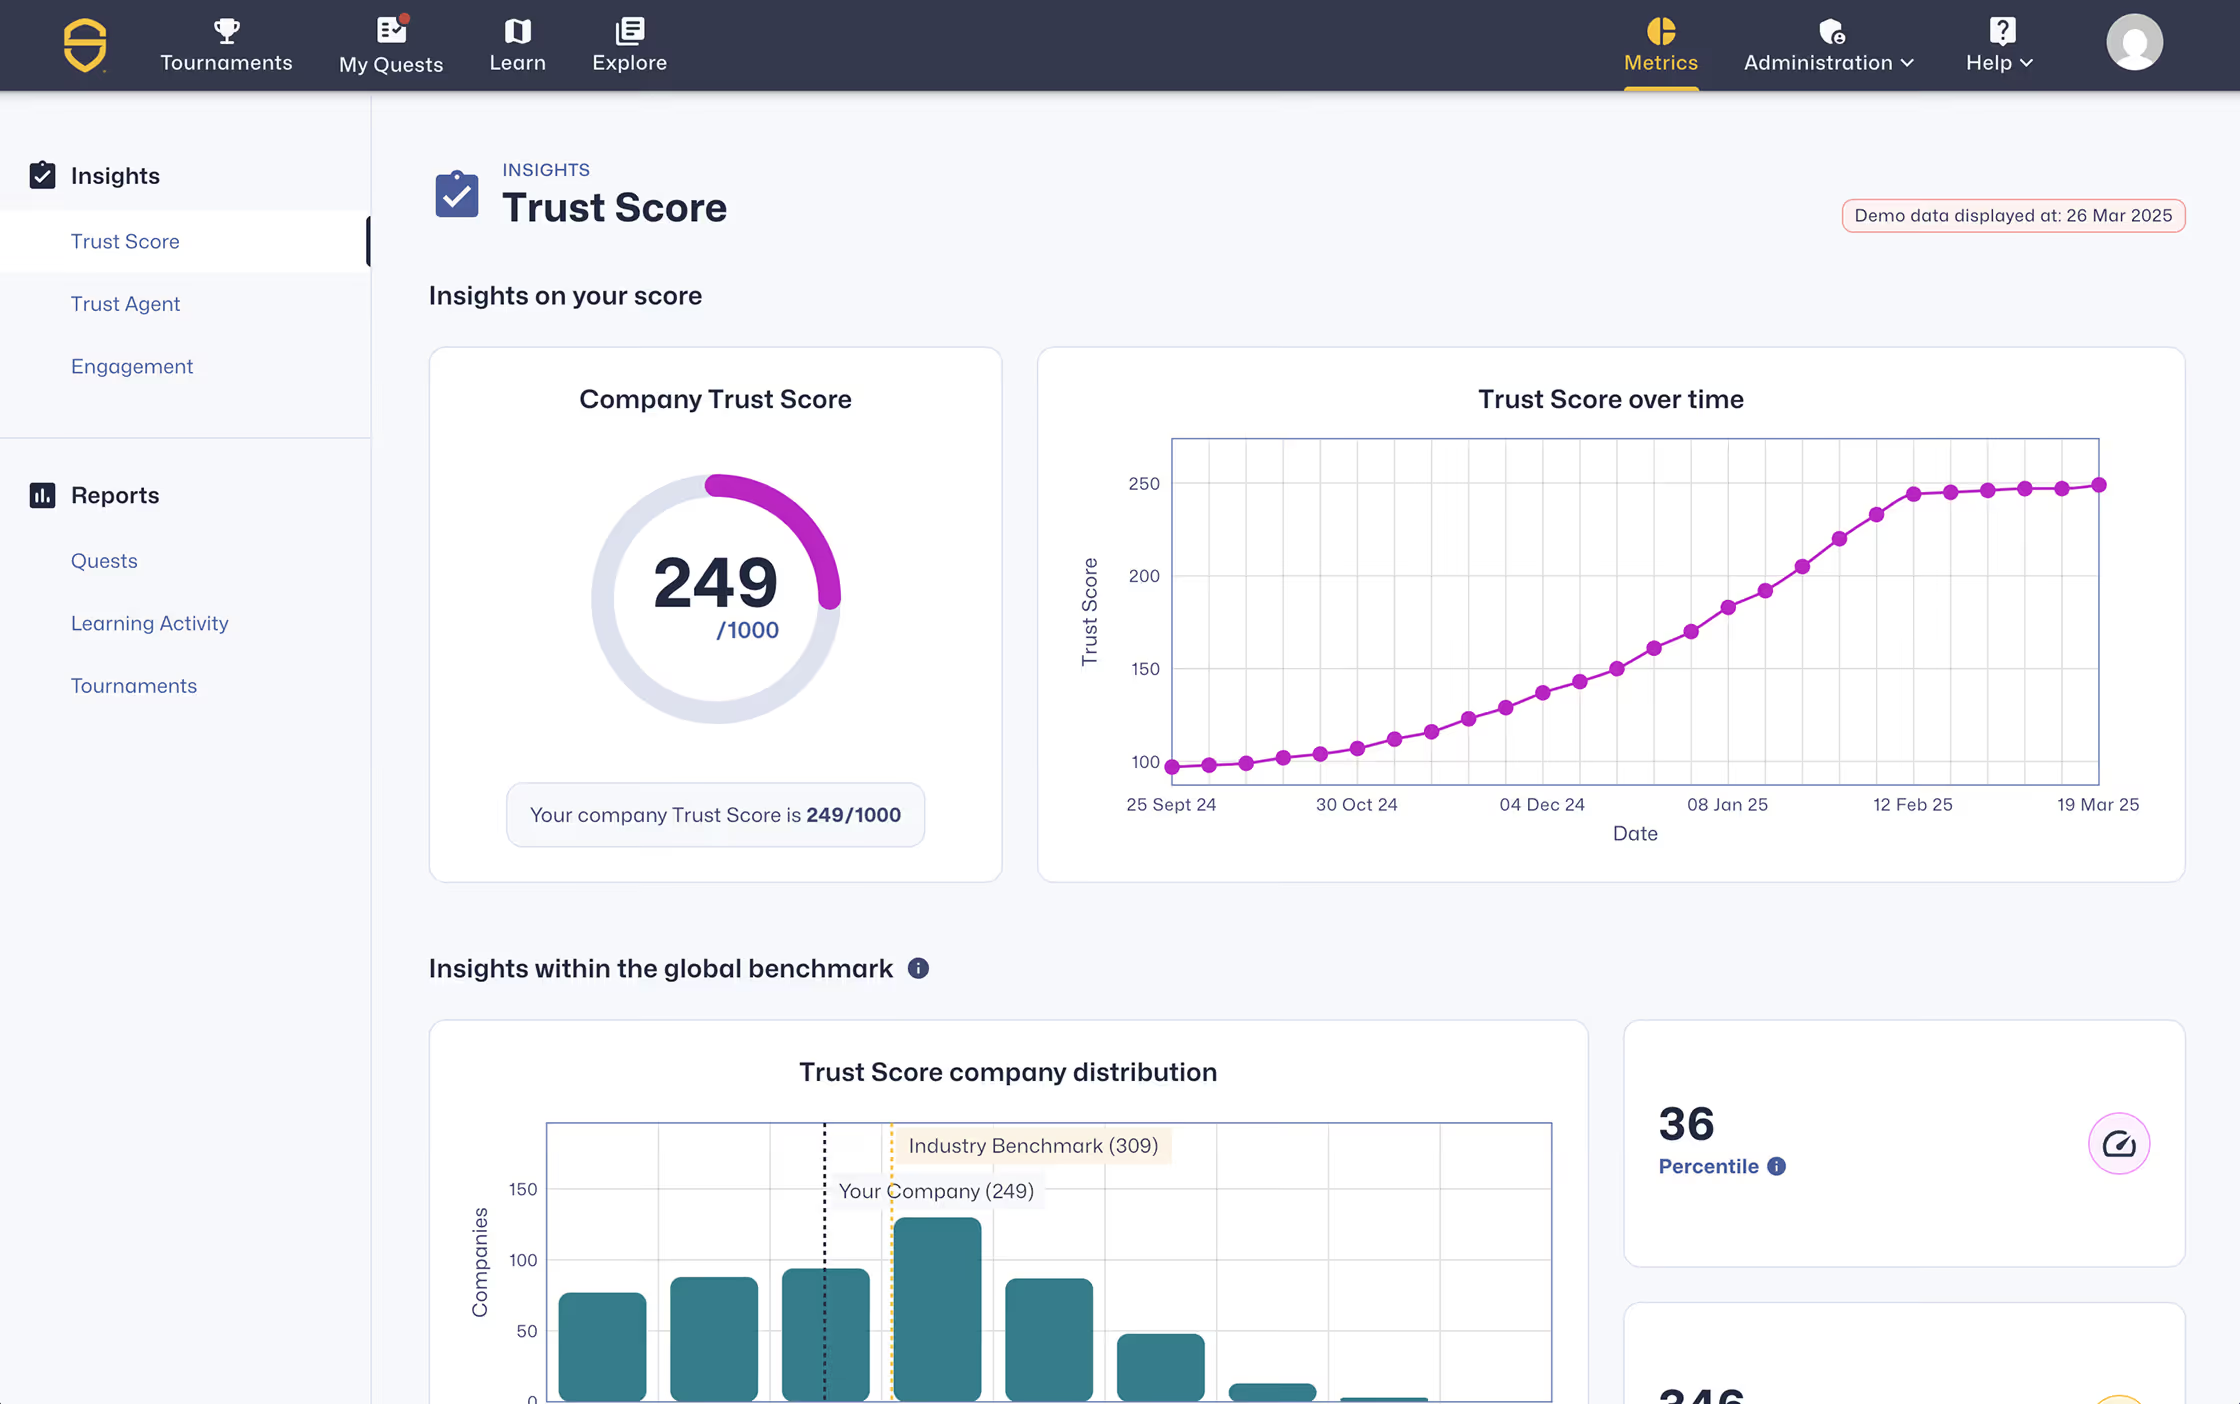
- Level 2: Enhance satellite through training (SCW metrics)
- Level 3: Reward progression through curriculum (SCW badges)
- Level 3: Provide training for vendors or outsourced workers (SCW Assessments)
- Level 3: Host external software security events (SCW Tournament mode)
- Level 3: Identify satellite through training (SCW metrics)
Are you confident that your current solution addresses these practices?
Govern AI-driven development before it ships
Measure AI-assisted risk, enforce secure coding policy at commit, and accelerate secure delivery across your SDLC.
Explore more blogs
Access expert content on secure coding, AI governance, and software risk management.
Every Employee is Now on the Frontline of AI Cybersecurity
The enterprise technology landscape is shifting with a velocity few predicted until it was too late. We have officially crossed the threshold from human-written code and basic copilot assistance, into the era of the Agentic Development Lifecycle (ADLC). While autonomous AI agents promise unprecedented efficiency across multiple functions, they also bring an entirely new class of security and regulatory risks.
Secure AI-driven development before it ships
See developer risk, enforce policy, and prevent vulnerabilities across your software development lifecycle.