Shift left security training and vulnerability detection for embedded systems
In this webinar, we consider the challenges organizations face when adopting a security-first approach to development especially within embedded software and how to harness best practices in learning technology and benefit from shifting left to optimize developer secure code training.

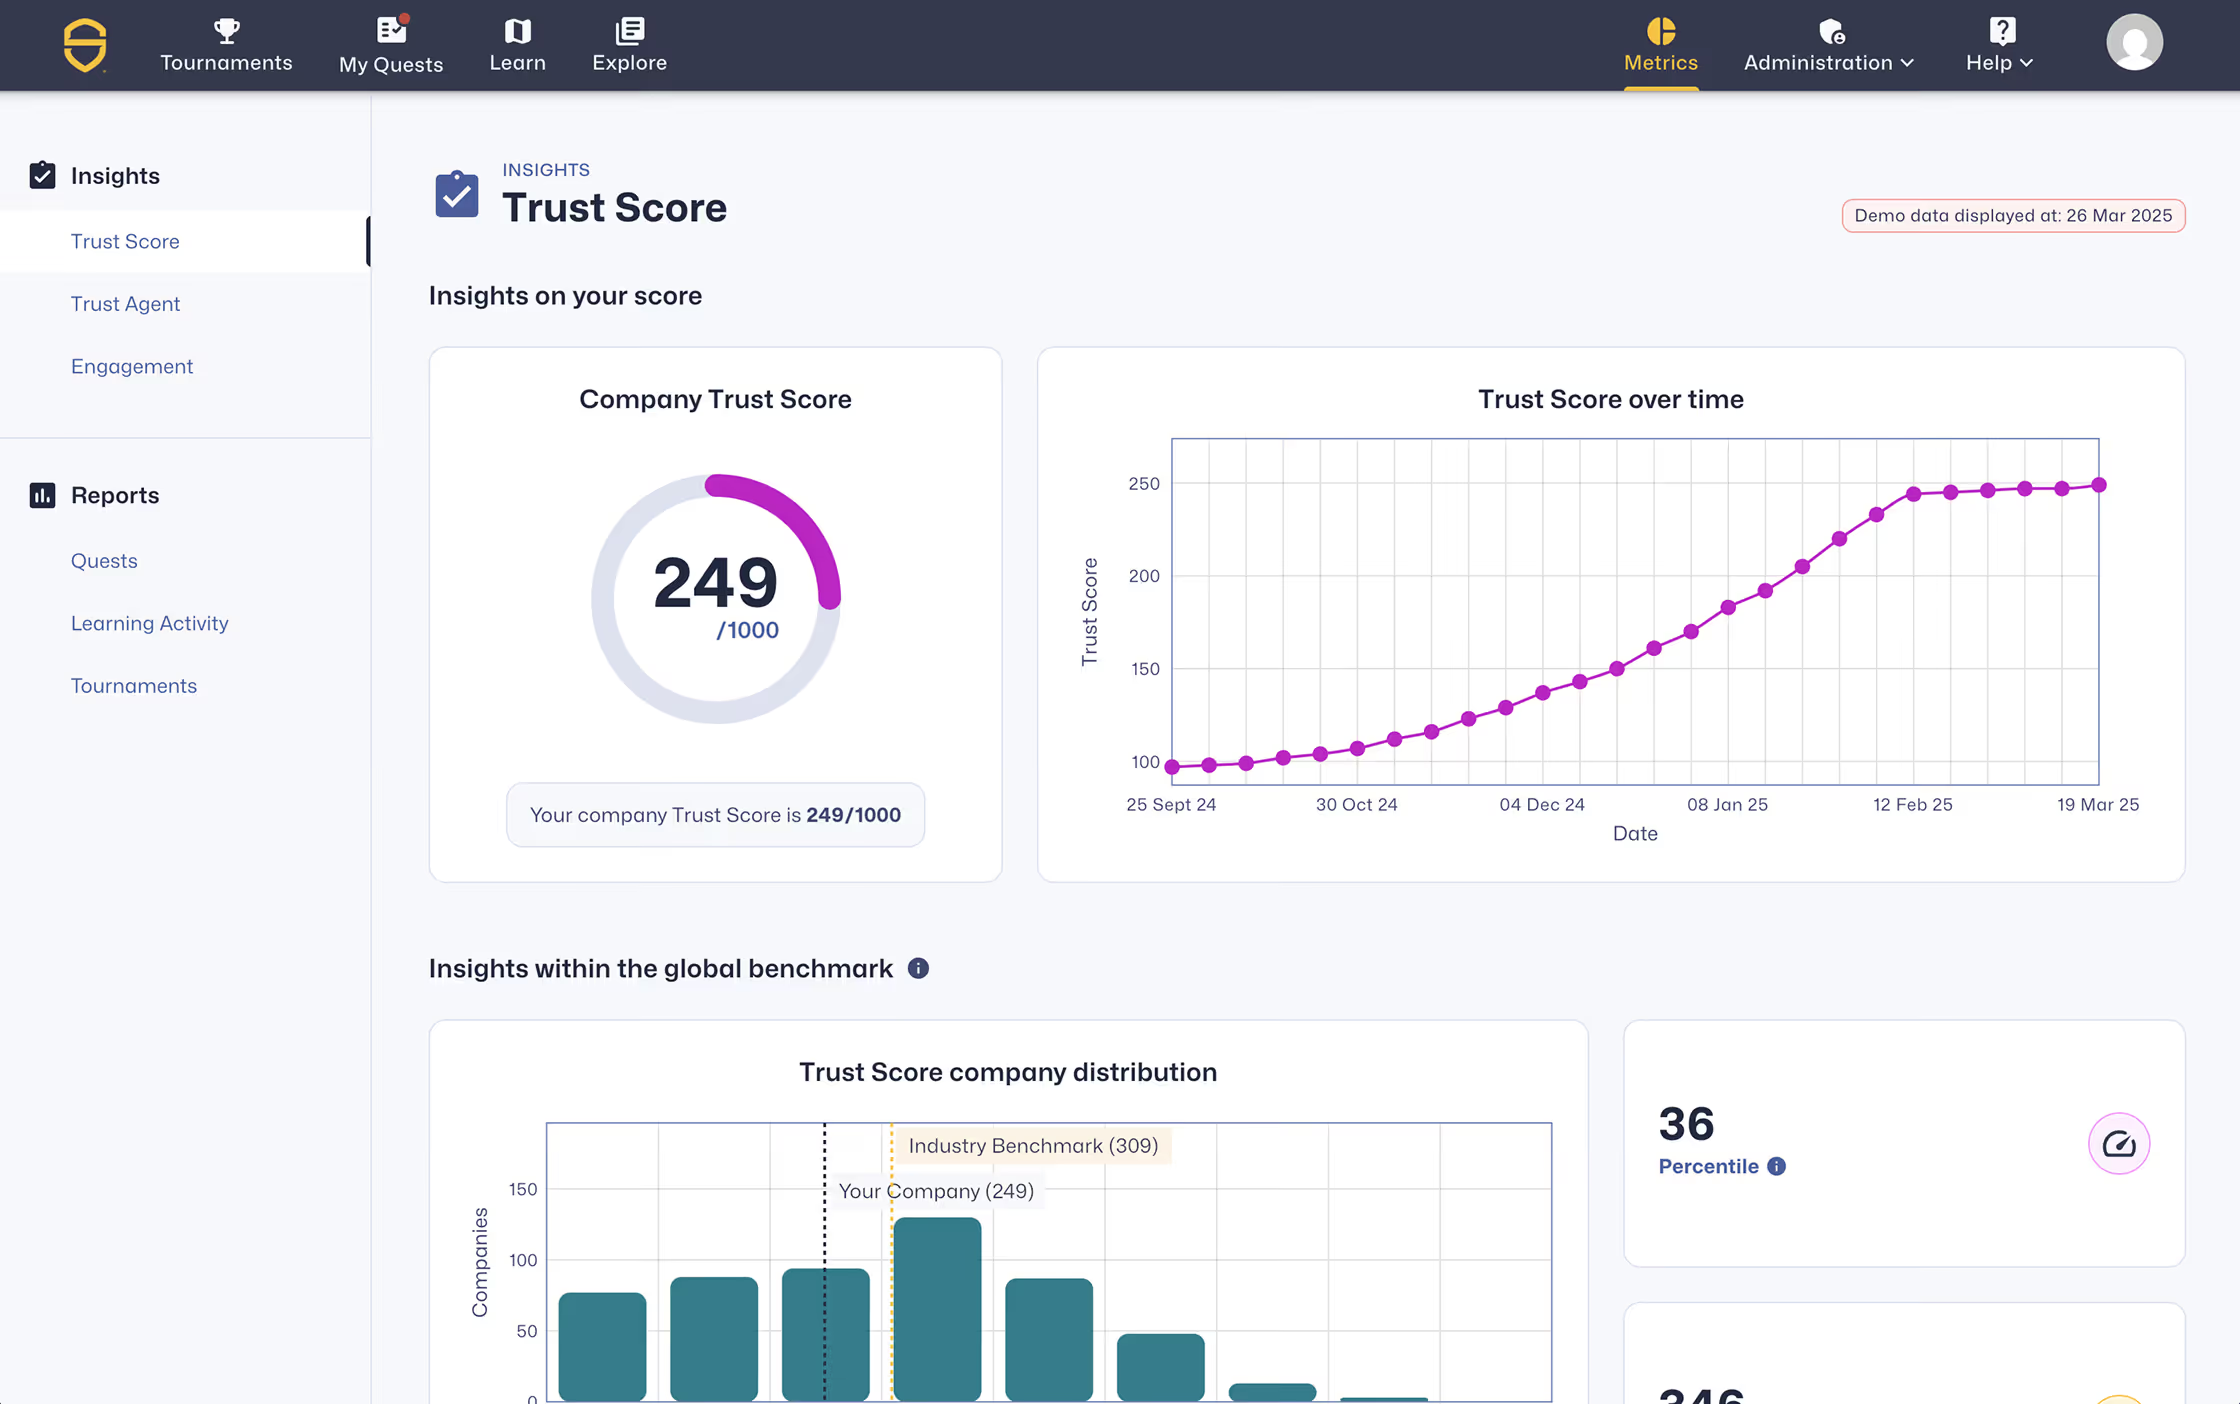
This on-demand session walks through what a typical embedded C++ coding challenge looks like inside the Secure Code Warrior learning platform, using memory corruption as the working example.
Watch to see:
- How developers locate and analyze a vulnerability directly in the code viewer
- Tiered hints that build understanding without giving away the answer
- How to identify and validate the correct fix once the vulnerability is found
- The other play modes available across the platform, including guided learning pathways, benchmarking assessments, and team coding competitions
Contact our sales team to set up a tailored demo for your developers.

Explore more events and webinars
Access expert content on secure coding, AI governance, and software risk management.

OWASP Global AppSec USA
Proud to be a Silver Sponsor of OWASP Global AppSec USA 2026, celebrating its 25th anniversary on November 5–6, 2026, at the Hyatt Regency in San Francisco! Join us and 800+ application security professionals for sessions on AI security, threat modeling, a Capture the Flag competition, the OWASP Projects Demo Room, and exclusive networking receptions. Come find us there and let's connect!

OWASP LASCON
We are proud to be a Gold Sponsor for OWASP LASCON 2026 in Austin, TX! Join us at the Norris Conference Center as we gather with over 400 web developers and security professionals to share cutting-edge ideas in application security.
Secure AI-driven development before it ships
See developer risk, enforce policy, and prevent vulnerabilities across your software development lifecycle.