Define how software is built securely in the age of AI
Build secure, resilient AI-driven software. Secure Code Warrior makes it possible at every commit.



Setting the direction for secure software in an AI-driven world
Software development has changed. Code is no longer written only by developers — it’s generated, suggested, and accelerated by AI tools and agents as part of a new, powerful and too often hidden tech stack. This shift increases speed, but also introduces unacceptable new risks that traditional approaches weren’t built to handle. Secure Code Warrior works with enterprises globally to ensure software remains secure and aligned to organizational standards, no matter how it is created.
Software development has been transformed by AI. Security must evolve with it.
AI-assisted development increases speed, scale, and complexity. Traditional security programs can’t keep up. A new approach is required. Security leaders must act now to bring AI visibility, accountability, and developer capability into how software is built.
Secure, high-quality code — every time, no matter the source
Secure Code Warrior reduces risk where it matters most: at the point of code creation. Security becomes part of how software is built, rather than an expensive, time-consuming afterthought.
Secure Code Warrior is trusted by global organizations to improve software security outcomes

Nuestro contenido más reciente
Vamos a tratar uno de los problemas más comunes a los que se enfrentan las organizaciones que administran sitios web o que permiten a los empleados acceder de forma remota a los recursos informáticos, que es prácticamente todo el mundo. Y sí, probablemente hayas adivinado que vamos a hablar de la autenticación.
Si una aplicación no cuenta con suficientes controles antiautomatización, los atacantes pueden seguir adivinando las contraseñas hasta que encuentren una que coincida. A continuación, te explicamos cómo detenerlos.
Si bien los problemas de codificación pueden ser parte del problema, los errores de lógica empresarial suelen ser el resultado de defectos de diseño o suposiciones lógicas incorrectas cuando se crea una aplicación por primera vez.

En ciberseguridad, a menudo somos como cazadores. Nuestros ojos están fijos en el horizonte, buscando la próxima vulnerabilidad emergente. Sin embargo, este enfoque orientado hacia el futuro puede tener el sorprendente efecto de reducir nuestra conciencia general sobre la seguridad.
Es común que los sitios web y las aplicaciones permitan a los usuarios enviar comentarios y otros datos a través de una aplicación mediante el correo electrónico. Y la mayoría de las personas ni siquiera piensan en ello en términos de un posible riesgo de seguridad.
Una referencia directa a un objeto se produce cuando se hace referencia a un registro específico (el «objeto») dentro de una aplicación. Por lo general, adopta la forma de un identificador único y puede aparecer en una URL.

La seguridad del software siempre es una prioridad para mí, al igual que el peligro muy real que representa nuestro estilo de vida cada vez más digital y de intercambio de información personal. Después de todo, nos encontramos en un territorio en gran medida desregulado, sin supervisión y felizmente ignorado. Estamos en el Lejano Oeste.
La gran mayoría de los sitios web utilizan bases de datos XML para realizar funciones críticas, como almacenar las credenciales de inicio de sesión de los usuarios, la información de los clientes, la información de identidad personal y los datos confidenciales o sensibles, lo que deja a los ataques de XQuery con una huella de ataque bastante grande.
From secure coding to governing AI-driven software
The key moments across product, growth, and market shifts that shaped how modern software is secured.
Rethinking software security at the source
Secure Code Warrior is founded in Australia by Pieter Danhieux, Fatemah Beydoun, Colin Wong, and Jaap Karan Singh on a simple belief:
- Fixing vulnerabilities after code is written doesn’t scale.
From day one, the focus was clear: Improve how developers write code to reduce risk at the source.
Embedding security into developer workflows
After securing four major Australian banks, Secure Code Warrior expands into the US and Europe. The acquisition of Sensei Security, and the addition of founders Matias Madou and Nathan Desmet, mark a turning point. Security moves beyond training into hands-on, in-workflow learning embedded directly in how code is written.
Enterprise adoption validates the model
With Series A and B funding, Secure Code Warrior scales globally across industries.
- Developer-driven security can scale, delivering measurable impact.
From training to Benchmark your security program
Secure Code Warrior raises Series C, acquires Adversary, and grows to 450+ global customers.Partnerships with GitHub, GitLab, Contrast Security, and Synopsys embed the platform across the development ecosystem. Customers achieve consistent reductions in vulnerabilities introduced during development — shifting security from detection to prevention.
AI reshapes software development
The rise of ChatGPT and GitHub Copilot transforms how code is created.Software is no longer written solely by developers, it’s generated, assisted, and accelerated by AI. As adoption grows, organizations face reduced visibility, increased velocity, and new classes of risk, driving the need for greater insight into how code is created.
The governance gap becomes unavoidable
At scale, organizations can no longer answer critical questions:
- Who - or what - is writing code?
- Does it meet security standards?
- Are developers equipped to evaluate it?
Traditional approaches can’t keep up. A new challenge emerges: governing software development in an AI-driven world.
Defining the next standard for secure software
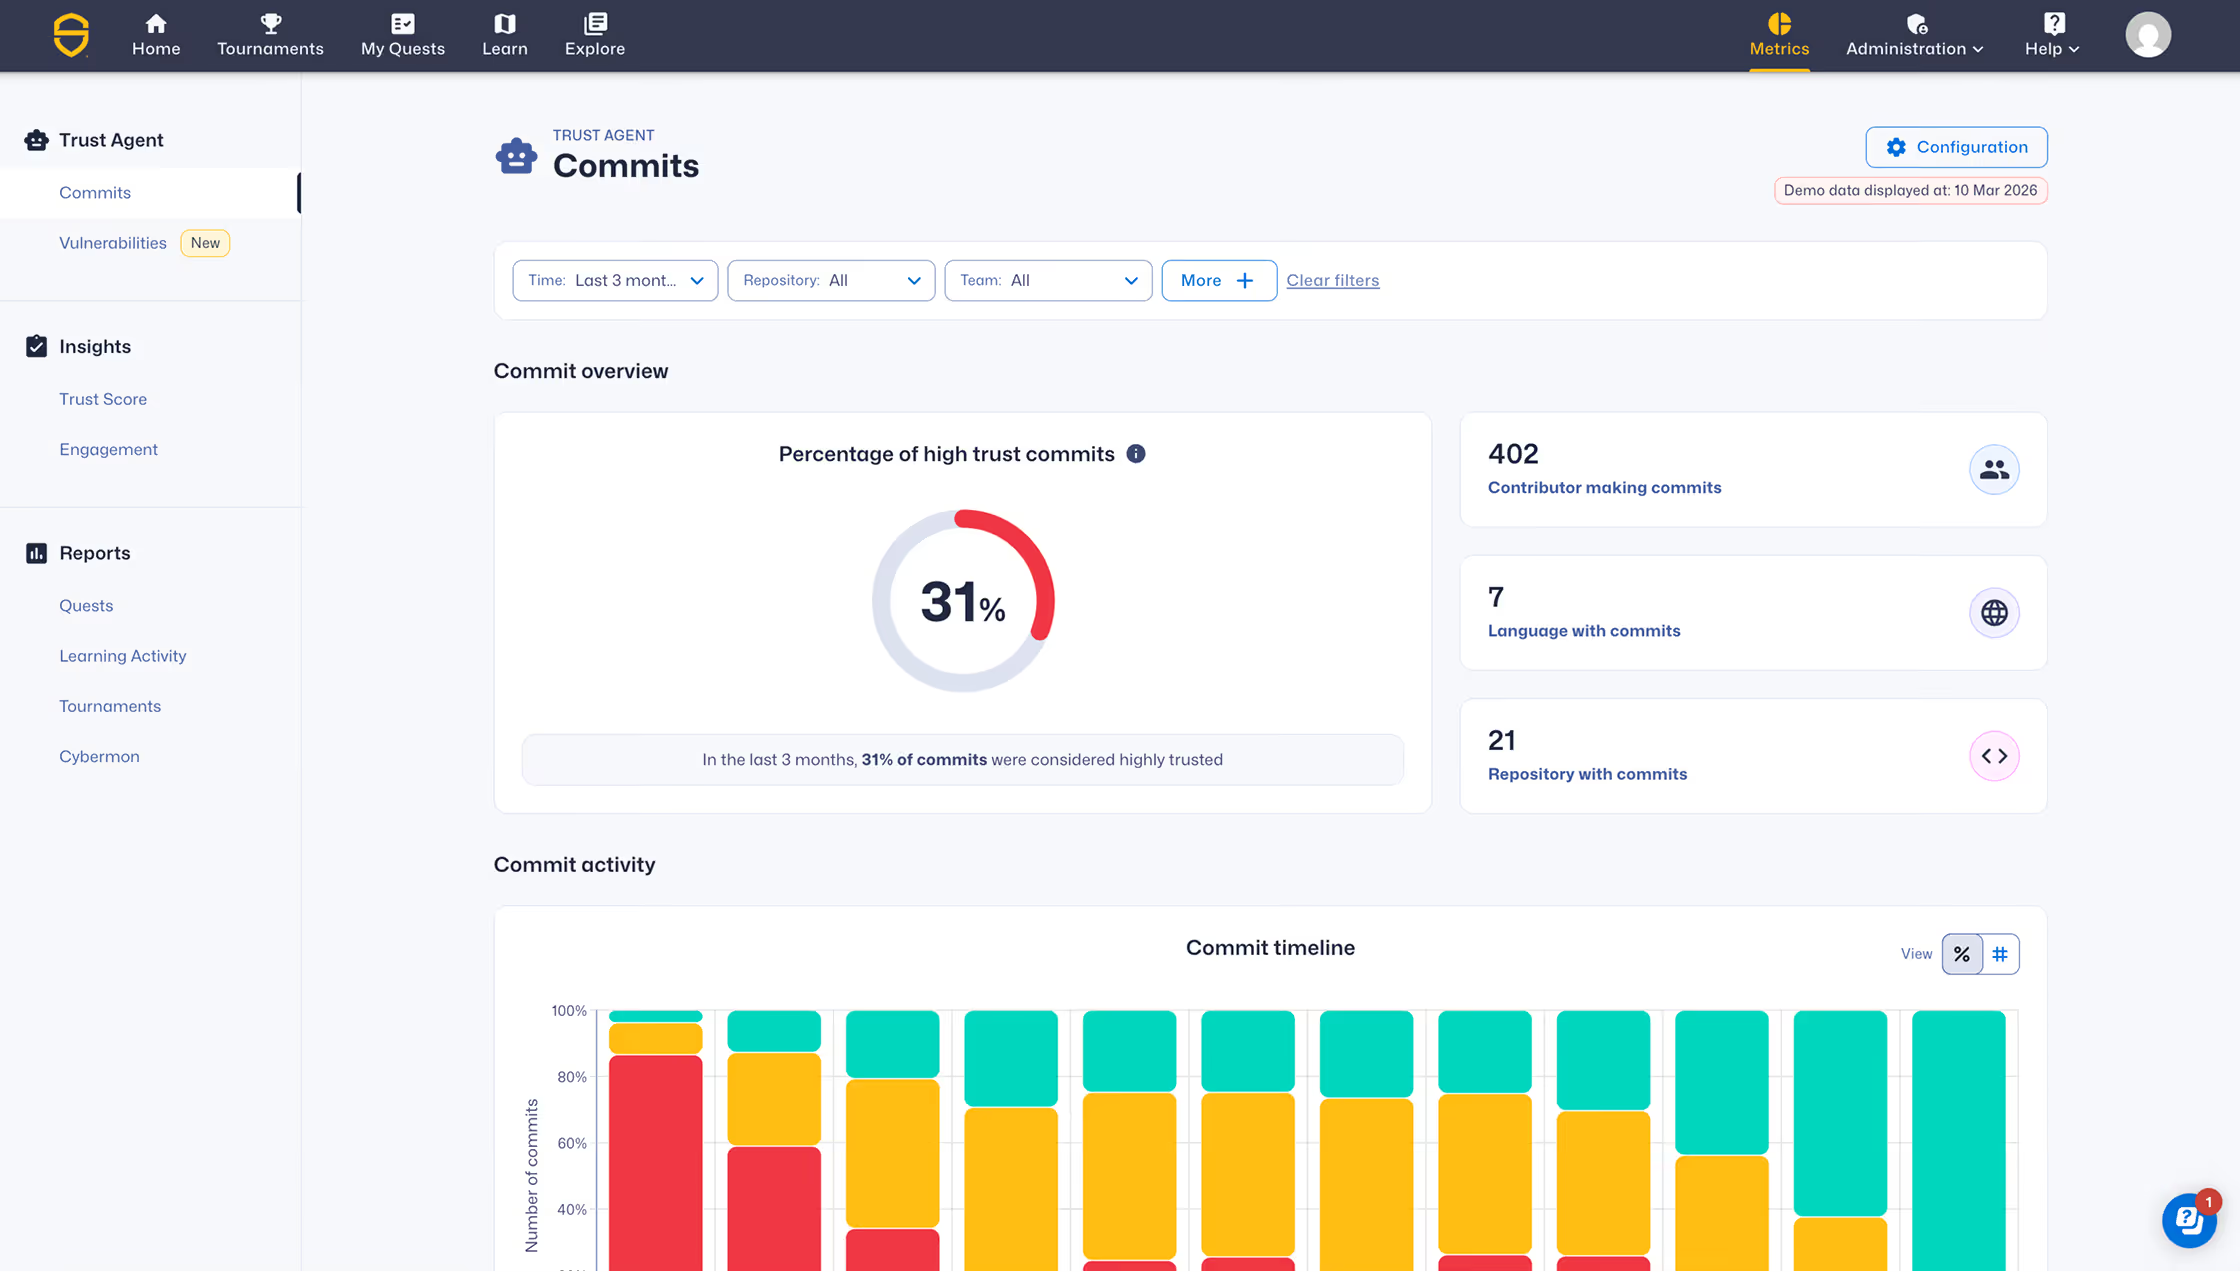
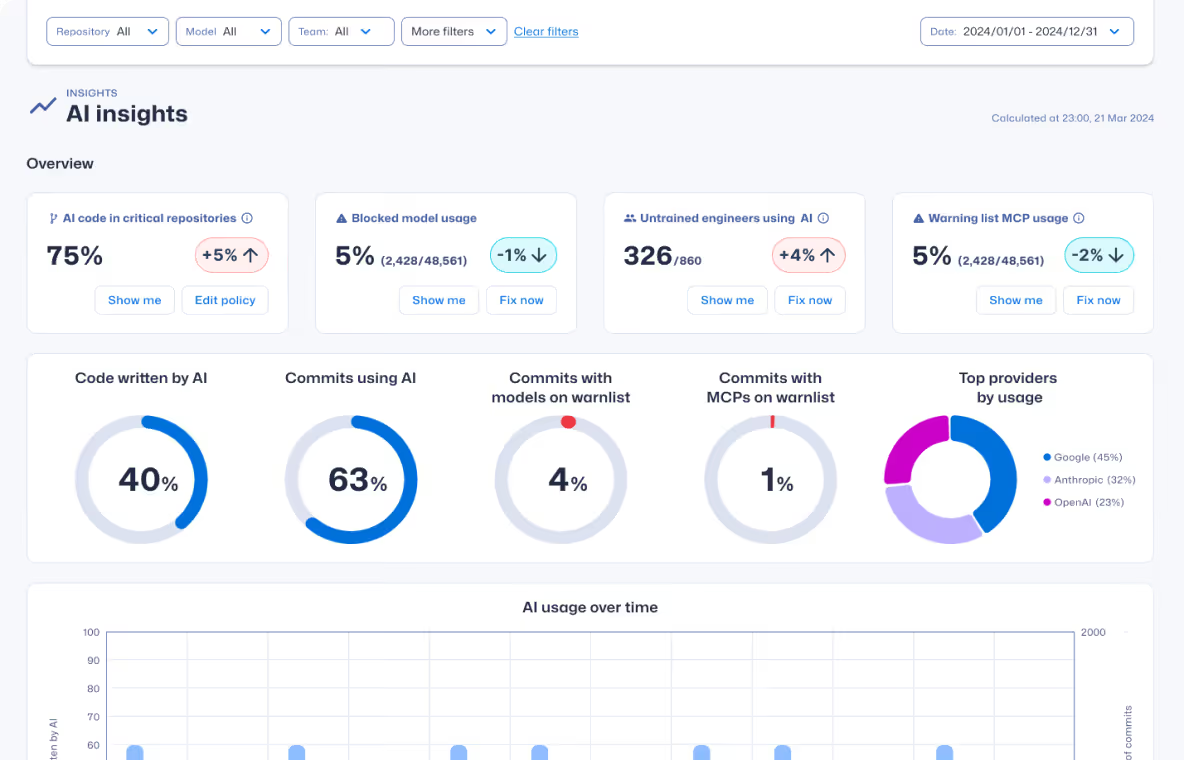
Secure Code Warrior introduces Trust Agent:AI, extending the platform to bring visibility and accountability into AI-driven development. Organizations can now understand how code is created, align development to risk thresholds, and strengthen developer capability in real time.
Our leadership team brings deep experience across software development, cybersecurity, and enterprise technology
We believe the future of software security depends on empowering developers — not slowing them down.




AI didn’t just accelerate software development — it changed how it must be secured.
Do the best work of your career
We're at one of the most important intersections in tech right now — where AI, software development, and security collide. The problems are real. The impact is measurable. And the team is one you'll actually want to work with.
Govern AI-driven development
before it ships
See where AI tools generate code, correlate commits with risk signals, and maintain visibility across your AI software supply chain.